
#binancesafufundtransfercompleted7499btc
The 90% figure is Binance's own claim. "Replaced" is not "recovered," and the independent proof is still pending.
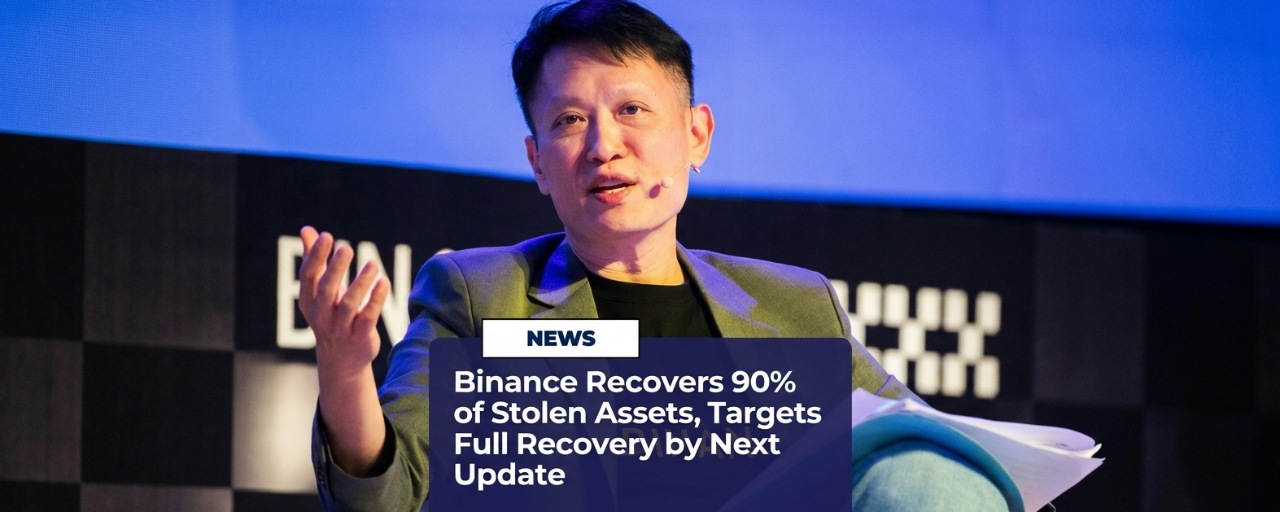
Binance says it has replenished 90% of the assets stolen in Thursday's $6.3B hack, up from about 80% in its previous update, using its own resources (CoinDesk, Oct 31). For anyone watching $BNB , $BTC and $ETH around the exchange's restart, the question has shifted from whether Binance says it can pay to whether the numbers survive independent checking.
WHAT BINANCE SAYS (OCT 31 UPDATE)
▪️ 90% of stolen assets replenished, up from roughly 80%
▪️ Fully backed per Binance: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD and ZEC ▪️ The remaining ~10% is less liquid tokens, being bought on public markets and over the counter
▪️ Funding: corporate treasury, part of the futures insurance fund, and a partial SAFU deployment expected within 24 hours. Binance says it is using only the portion above SAFU's required size and has committed to restoring the fund to about $1B
▪️ Withdrawals: on track to reopen Sunday, Nov 1. An earlier update said the restart would be phased, with not every service returning at once
▪️ A full technical post-mortem will be published once the investigation finishes
"REPLENISHED" IS NOT "RECOVERED"
Binance is buying replacement assets with its own money. That restores user balances. It does not claw back what the attacker took. The separate recovery effort is the roughly $3B that partners froze on-chain (per Binance; Tether says it froze over $1.56B and Circle over $800M). Tallies of what remains with the attacker differ by analyst, so treat any single figure with care.
WHAT IS STILL OPEN
▪️ Independent verification: Binance's proof-of-reserves snapshot (midnight UTC, Oct 31) shows 100%+ coverage for the named tokens. The full cryptographic proof, which lets users verify their balances are included, is expected by Nov 3 (CoinDesk)
▪️ Root cause: Binance first pointed to a compromised engineer's laptop, then to additional breach points. Co-CEO Richard Teng said an EIP-7702 delegation "did not pass through our normal approval controls"
▪️ Attribution: analytics firms TRM Labs and Chainalysis assess the attack matches North Korea's TraderTraitor group. These are third-party assessments. Binance has not attributed the attack, and President Trump said "we don't know"
▪️ Scale: the loss is roughly 4% of the ~$144B Binance held before the hack (DefiLlama, via CoinDesk)
WHAT WOULD CONFIRM A CLEAN RECOVERY
The full cryptographic proof published on time and checked by independent analysts. Withdrawals reopening on schedule without new outages. A post-mortem that explains how the approval controls were bypassed.
WHAT WOULD SIGNAL TROUBLE
The restart slipping, outside analysts unable to reconcile the reserve data, the last 10% taking far longer than described, or more breach points surfacing.
MY TAKE (ANALYSIS, NOT FACT)
Replacing 90% of a loss in about two days is a genuine strength, and it is the strongest argument for Binance's balance sheet. But whether SAFU "worked" is too early to say. It was one of three funding sources, and only its above-requirement portion is being used. What would settle the trust question is independent proof and a full root-cause report, and neither has been published yet.
Also expect phishing waves. Use official Binance channels only.
Is the 90% replacement enough to restore your trust, or are you waiting for the full proof of reserves?
Not financial advice. Always DYOR.
Follow for Daily Hot Analytics Like This. @MistralAK
#Binance #SAFU #CryptoSecurity #BinanceRecovery90% of stolen assets