


Security teams that join Anthropic’s expanded Cyber Verification Program must agree to let the company retain their data so it can watch for cyber misuse.
Anthropic rebuilt the program Tuesday into three tiers of access with fewer cyber blocks at each level.
Anthropic will offer zero data retention later this fall
Enterprise Frontier Safeguards, coming later this fall, will combine the same safeguards with zero data retention. Eligible organizations will then be able to hold data in cloud infrastructure they control.
Until then, organizations with zero-data-retention access to Claude Fable 5.1 or Claude Mythos 5.1 can join without retention.
The program is available on the Claude Platform, Google Cloud’s Vertex AI, and Microsoft Foundry. On Amazon Bedrock, access is limited to customers eligible for Enterprise Frontier Safeguards.
Defense Access is the first level and was made for responding to incidents, breaking down malware, and making sure that discovered bugs are real.
Security teams, open-source maintainers, researchers who have reported bugs in the past, and critical infrastructure operators as small as a regional hospital can all apply to join the Defense Access tier. Anthropic says it will reply to applicants in a few days.
Red Team Access focuses on authorized penetration testing and is exclusively available to organizations. Anthropic indicates that the application vetting process may take several weeks.
Red Team users get cut off mid-task if they try to deploy ransomware, damage physical systems, or pen test high-risk safety systems.
The most relaxed rules belong to Specialized Access. Only a small group gets in, such as organizations cleared to test flight systems, power grids, telecom networks, or the systems banks use to move money between each other.
Anthropic checks every Specialized Access applicant with the US government. Existing Project Glasswing members move into this tier without having to reapply.
All 3 tiers have Claude Opus 5.5, Claude Sonnet 5.5, and Claude Mythos 5.1 available.
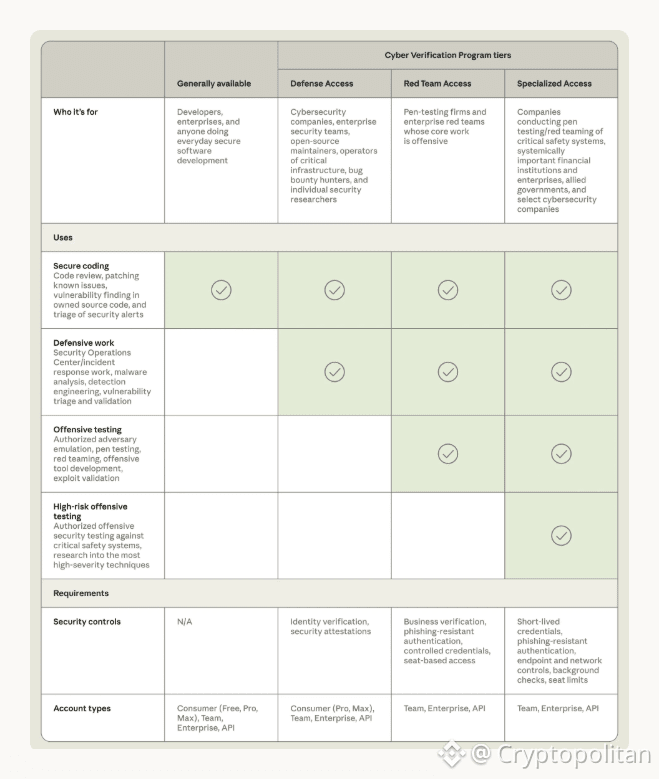 Anthropic’s overview of the Cyber Verification Program tiers, published October 6, 2026.
Opus 5.5 completed 34 of 50 attack tasks at the Red Team tier
Anthropic tested the tiers on CyScenarioBench, running Opus 5.5 five times on each of 10 multi-stage cyber challenges. Every task was blocked on the first prompt without the program.
Defense Access blocked 46 of 50 trials at some point. Red Team Access blocked none, and the model completed 34 of 50 tasks, in line with its unprotected 67.6% success rate.
Opus 5.5 was released on September 22, but most of the security tasks sent to it were diverted to the older Opus 4.8 instead.
Between April and July, Glasswing partners pinpointed 129,000+ verified vulnerabilities, and Anthropic’s own open-source scanning added another 5,500 through October. Over 33,000 have been rated as either critical or high severity.
The figures are based on 33 partner reports, and Anthropic expects the actual impact to be at least five times larger. In June, Glasswing added 150 more organizations.
In August, Kraken parent Payward joined Glasswing to scan its systems and open-source dependencies, Cryptopolitan said. Mythos was dark worldwide between June 12 and July 1, after a Commerce Department export ruling barred foreign access.
The smartest crypto minds already read our newsletter. Want in? Join them.