
#714723
714723
1,730 නැරඹීම්
7 සාකච්ඡා කරමින්
උණුසුම්
නවතම


Lighter Pauses Withdrawals After Suspected $15.5 Million API Key Exploit• Lighter suspended withdrawals and pool creation on Nov. 16 after a suspected $15.5 million exploit.
• Researchers estimate losses of $10.39 million and $5.09 million across market maker accounts #714710 and #714723.
• The attacker's wallet withdrew $10.39 million in USDC at 10:11:47 UTC, per the Ethereum record.
Withdrawals and Pool Creation Halted
Decentralized perpetual futures venue Lighter has halted all withdrawals and the creation of new liquidity pools after on-chain observers flagged roughly $15.5 million leaving its Ethereum Layer 1 contract on Monday. In a Nov. 16 statement, the team said it was investigating a security incident that appeared to involve a single compromised external party, without naming the affected entity or putting a dollar figure on the loss. The halt covers every withdrawal and every new pool on the platform, and the team framed it as a precaution while it assessed the full impact. The suspected scale comes from researchers rather than the exchange. Early on-chain analysis pointed to an attacker withdrawing about $10.39 million in USDC, and follow-up work identified a second affected account, lifting the estimated total to roughly $15.48 million. Researcher 0xTria, citing observations from Korean blockchain analysts, traced the method to leaked API keys belonging to two large market maker accounts rather than a flaw in Lighter's protocol. The attacker first closed the victims' open trading positions and converted their holdings into USDC. Using one compromised account, the attacker then created a public zero-fee pool and deposited about $10,000 to acquire roughly 99.99% of its shares. The victims' USDC moved into that pool in batches of roughly $1 million and was redeemed back out, a route that appears to exploit how Lighter treats transfers between accounts sharing one Layer 1 address, which need no extra signature. Account #714710 reportedly lost $10.39 million, and account #714723 another $5.09 million.
Lighter Pins the Breach on a Leaked API Key
Lighter's follow-up update on Monday, posted at 12:49 UTC, narrowed the cause: the exchange said the incident stemmed from a leaked API key, the credential that lets trading software execute on an account's behalf, tied to one trader's account. It also stated that Lighter's protocol and smart contracts were not affected, and named the wallet address the team believes belongs to the attacker, an address community observers had already flagged. Chain timing frames how fast events moved: the first major withdrawal landed at 10:11:47 UTC, nearly an hour before Lighter's first public disclosure at 11:02 UTC, which paused withdrawals and pool creation. The venue, which settles trades on Ethereum using zero-knowledge proofs, placed the fault outside that settlement stack entirely. The team has switched on Guardian mode on its smart contract as a precaution and said its priority is recovering funds tied to what it described as an additional withdrawal attempt by the attacker. A contract upgrade carried out by Lighter's Security Council is meant to complete, with withdrawals reopening, before Monday ends. The update stops at a single compromised account and gives no dollar figure of its own. The $15.5 million total remains a researcher estimate the team has not confirmed, and Lighter has not said how the key leaked or whose account it belonged to.
Attacker Splits Funds Into 160 ETH Transfers
Ethereum's public record anchors the money trail. The attacker's wallet, 0xb3fffca23d4444eE73349825ACD84f7b5020e387, made the $10.39 million USDC withdrawal from the contract after receiving about $10,000 through a relay transfer roughly half an hour earlier. On-chain data shows the wallet swapped the USDC for about 5,760 ETH through CoW Swap and then split the holdings into 15 transfers of 160 ETH each, two of which were sent back. As of 12:51 UTC the address still held about 3,565 ETH. Analytics account Lookonchain reported the attacker was depositing funds on Hyperliquid, a larger perps rival, to buy the privacy coin Monero (XMR); neither Lighter nor the chain has confirmed that yet. A separate projection even models Lighter flipping Hyperliquid as the top perps platform by January 2027, a measure of how closely watched the venue had become. The incident reached the token directly. Upbit and Bithumb suspended LIT deposits and withdrawals in response to the security reports. LIT fell more than 17% at one point on Monday before recovering part of the loss to trade around $2.50 to $2.66, unwinding part of an October run built on the Robinhood Wallet integration and expanding token buybacks. Lighter itself had been expanding its infrastructure, launching an EVM development network in October that lets smart contracts manage trading orders and move assets between its Ethereum-compatible environment and Lighter Core. Our live monitoring shows the token down about 13.4% over the past 24 hours, and the full drawdown is charted in LIT technical analysis.
Still Paused, and Still Unconfirmed
The chain and the team's own words now bound the story tightly. The Ethereum record fixes the first theft at $10.39 million in USDC at 10:11:47 UTC, and Lighter's own post-mortem places the root cause in a leaked API key tied to one trader's account, with the protocol and smart contracts untouched. Remediation runs on the two tracks the team named: Guardian mode on the contract and a Security Council upgrade, with withdrawals targeted to reopen before Monday ends. What stays open sits in the gaps: the $15.5 million total is still a researcher estimate Lighter has not confirmed, the team has not explained how the key leaked, and no recovery figure exists for the attacker's additional withdrawal attempt. Until that upgrade lands, withdrawals and new pool creation stay paused.
Lighter Pauses Withdrawals After Suspected $15.5 Million API Key Exploit
• Lighter suspended withdrawals and pool creation on Nov. 16 after a suspected $15.5 million exploit.
• Researchers estimate losses of $10.39 million and $5.09 million across market maker accounts #714710 and #714723.
• The attacker's wallet withdrew $10.39 million in USDC at 10:11:47 UTC, per the Ethereum record.
Withdrawals and Pool Creation Halted
Decentralized perpetual futures venue Lighter has halted all withdrawals and the creation of new liquidity pools after on-chain observers flagged roughly $15.5 million leaving its Ethereum Layer 1 contract on Monday. In a Nov. 16 statement, the team said it was investigating a security incident that appeared to involve a single compromised external party, without naming the affected entity or putting a dollar figure on the loss. The halt covers every withdrawal and every new pool on the platform, and the team framed it as a precaution while it assessed the full impact. The suspected scale comes from researchers rather than the exchange. Early on-chain analysis pointed to an attacker withdrawing about $10.39 million in USDC, and follow-up work identified a second affected account, lifting the estimated total to roughly $15.48 million. Researcher 0xTria, citing observations from Korean blockchain analysts, traced the method to leaked API keys belonging to two large market maker accounts rather than a flaw in Lighter's protocol. The attacker first closed the victims' open trading positions and converted their holdings into USDC. Using one compromised account, the attacker then created a public zero-fee pool and deposited about $10,000 to acquire roughly 99.99% of its shares. The victims' USDC moved into that pool in batches of roughly $1 million and was redeemed back out, a route that appears to exploit how Lighter treats transfers between accounts sharing one Layer 1 address, which need no extra signature. Account #714710 reportedly lost $10.39 million, and account #714723 another $5.09 million.
Lighter Pins the Breach on a Leaked API Key
Lighter's follow-up update on Monday, posted at 12:49 UTC, narrowed the cause: the exchange said the incident stemmed from a leaked API key, the credential that lets trading software execute on an account's behalf, tied to one trader's account. It also stated that Lighter's protocol and smart contracts were not affected, and named the wallet address the team believes belongs to the attacker, an address community observers had already flagged. Chain timing frames how fast events moved: the first major withdrawal landed at 10:11:47 UTC, nearly an hour before Lighter's first public disclosure at 11:02 UTC, which paused withdrawals and pool creation. The venue, which settles trades on Ethereum using zero-knowledge proofs, placed the fault outside that settlement stack entirely. The team has switched on Guardian mode on its smart contract as a precaution and said its priority is recovering funds tied to what it described as an additional withdrawal attempt by the attacker. A contract upgrade carried out by Lighter's Security Council is meant to complete, with withdrawals reopening, before Monday ends. The update stops at a single compromised account and gives no dollar figure of its own. The $15.5 million total remains a researcher estimate the team has not confirmed, and Lighter has not said how the key leaked or whose account it belonged to.
Attacker Splits Funds Into 160 ETH Transfers
Ethereum's public record anchors the money trail. The attacker's wallet, 0xb3fffca23d4444eE73349825ACD84f7b5020e387, made the $10.39 million USDC withdrawal from the contract after receiving about $10,000 through a relay transfer roughly half an hour earlier. On-chain data shows the wallet swapped the USDC for about 5,760 ETH through CoW Swap and then split the holdings into 15 transfers of 160 ETH each, two of which were sent back. As of 12:51 UTC the address still held about 3,565 ETH. Analytics account Lookonchain reported the attacker was depositing funds on Hyperliquid, a larger perps rival, to buy the privacy coin Monero (XMR); neither Lighter nor the chain has confirmed that yet. A separate projection even models Lighter flipping Hyperliquid as the top perps platform by January 2027, a measure of how closely watched the venue had become. The incident reached the token directly. Upbit and Bithumb suspended LIT deposits and withdrawals in response to the security reports. LIT fell more than 17% at one point on Monday before recovering part of the loss to trade around $2.50 to $2.66, unwinding part of an October run built on the Robinhood Wallet integration and expanding token buybacks. Lighter itself had been expanding its infrastructure, launching an EVM development network in October that lets smart contracts manage trading orders and move assets between its Ethereum-compatible environment and Lighter Core. Our live monitoring shows the token down about 13.4% over the past 24 hours, and the full drawdown is charted in LIT technical analysis.
Still Paused, and Still Unconfirmed
The chain and the team's own words now bound the story tightly. The Ethereum record fixes the first theft at $10.39 million in USDC at 10:11:47 UTC, and Lighter's own post-mortem places the root cause in a leaked API key tied to one trader's account, with the protocol and smart contracts untouched. Remediation runs on the two tracks the team named: Guardian mode on the contract and a Security Council upgrade, with withdrawals targeted to reopen before Monday ends. What stays open sits in the gaps: the $15.5 million total is still a researcher estimate Lighter has not confirmed, the team has not explained how the key leaked, and no recovery figure exists for the attacker's additional withdrawal attempt. Until that upgrade lands, withdrawals and new pool creation stay paused.
• Researchers estimate losses of $10.39 million and $5.09 million across market maker accounts #714710 and #714723.
• The attacker's wallet withdrew $10.39 million in USDC at 10:11:47 UTC, per the Ethereum record.
Withdrawals and Pool Creation Halted
Decentralized perpetual futures venue Lighter has halted all withdrawals and the creation of new liquidity pools after on-chain observers flagged roughly $15.5 million leaving its Ethereum Layer 1 contract on Monday. In a Nov. 16 statement, the team said it was investigating a security incident that appeared to involve a single compromised external party, without naming the affected entity or putting a dollar figure on the loss. The halt covers every withdrawal and every new pool on the platform, and the team framed it as a precaution while it assessed the full impact. The suspected scale comes from researchers rather than the exchange. Early on-chain analysis pointed to an attacker withdrawing about $10.39 million in USDC, and follow-up work identified a second affected account, lifting the estimated total to roughly $15.48 million. Researcher 0xTria, citing observations from Korean blockchain analysts, traced the method to leaked API keys belonging to two large market maker accounts rather than a flaw in Lighter's protocol. The attacker first closed the victims' open trading positions and converted their holdings into USDC. Using one compromised account, the attacker then created a public zero-fee pool and deposited about $10,000 to acquire roughly 99.99% of its shares. The victims' USDC moved into that pool in batches of roughly $1 million and was redeemed back out, a route that appears to exploit how Lighter treats transfers between accounts sharing one Layer 1 address, which need no extra signature. Account #714710 reportedly lost $10.39 million, and account #714723 another $5.09 million.
Lighter Pins the Breach on a Leaked API Key
Lighter's follow-up update on Monday, posted at 12:49 UTC, narrowed the cause: the exchange said the incident stemmed from a leaked API key, the credential that lets trading software execute on an account's behalf, tied to one trader's account. It also stated that Lighter's protocol and smart contracts were not affected, and named the wallet address the team believes belongs to the attacker, an address community observers had already flagged. Chain timing frames how fast events moved: the first major withdrawal landed at 10:11:47 UTC, nearly an hour before Lighter's first public disclosure at 11:02 UTC, which paused withdrawals and pool creation. The venue, which settles trades on Ethereum using zero-knowledge proofs, placed the fault outside that settlement stack entirely. The team has switched on Guardian mode on its smart contract as a precaution and said its priority is recovering funds tied to what it described as an additional withdrawal attempt by the attacker. A contract upgrade carried out by Lighter's Security Council is meant to complete, with withdrawals reopening, before Monday ends. The update stops at a single compromised account and gives no dollar figure of its own. The $15.5 million total remains a researcher estimate the team has not confirmed, and Lighter has not said how the key leaked or whose account it belonged to.
Attacker Splits Funds Into 160 ETH Transfers
Ethereum's public record anchors the money trail. The attacker's wallet, 0xb3fffca23d4444eE73349825ACD84f7b5020e387, made the $10.39 million USDC withdrawal from the contract after receiving about $10,000 through a relay transfer roughly half an hour earlier. On-chain data shows the wallet swapped the USDC for about 5,760 ETH through CoW Swap and then split the holdings into 15 transfers of 160 ETH each, two of which were sent back. As of 12:51 UTC the address still held about 3,565 ETH. Analytics account Lookonchain reported the attacker was depositing funds on Hyperliquid, a larger perps rival, to buy the privacy coin Monero (XMR); neither Lighter nor the chain has confirmed that yet. A separate projection even models Lighter flipping Hyperliquid as the top perps platform by January 2027, a measure of how closely watched the venue had become. The incident reached the token directly. Upbit and Bithumb suspended LIT deposits and withdrawals in response to the security reports. LIT fell more than 17% at one point on Monday before recovering part of the loss to trade around $2.50 to $2.66, unwinding part of an October run built on the Robinhood Wallet integration and expanding token buybacks. Lighter itself had been expanding its infrastructure, launching an EVM development network in October that lets smart contracts manage trading orders and move assets between its Ethereum-compatible environment and Lighter Core. Our live monitoring shows the token down about 13.4% over the past 24 hours, and the full drawdown is charted in LIT technical analysis.
Still Paused, and Still Unconfirmed
The chain and the team's own words now bound the story tightly. The Ethereum record fixes the first theft at $10.39 million in USDC at 10:11:47 UTC, and Lighter's own post-mortem places the root cause in a leaked API key tied to one trader's account, with the protocol and smart contracts untouched. Remediation runs on the two tracks the team named: Guardian mode on the contract and a Security Council upgrade, with withdrawals targeted to reopen before Monday ends. What stays open sits in the gaps: the $15.5 million total is still a researcher estimate Lighter has not confirmed, the team has not explained how the key leaked, and no recovery figure exists for the attacker's additional withdrawal attempt. Until that upgrade lands, withdrawals and new pool creation stay paused.
9

·
--
🚨 $LIT ¡TRAICIÓN EN LIGHTER!
Lighter, el exchange de perpetuos, amaneció con $15.48 millones en USDC drenados de dos cuentas de market makers. Para mí, lo más grave no es el monto: es que unas llaves API filtradas bastaron para vaciar las cuentas sin que el protocolo se rompiera.
Miren el detalle que nadie está viendo:
→ La cuenta #714710 perdió $10.39M y la #714723 otros $5.09M, en la mañana de hoy 16 de noviembre.
→ El atacante creó un pool público con 0% de comisión, compró el 99.99% con apenas ~$10,000 y sacó los fondos en lotes de ~$1M.
→ Lo robado ya se cambió a ETH en CoW Swap y 640 ETH (~$1.12M) se pasaron a Hyperliquid para comprar 2,240 XMR, casi imposible de rastrear.
Lighter pausó los retiros y la creación de pools sin fecha de regreso, y su token $LIT cayó 9%, de $2.75 a $2.50.
¿Crees que los exchanges descentralizados son más seguros que los centralizados? 👇
$LIT $ETH $XMR
#HackCrypto #Lighter #SeguridadDeFi
🚨 $LIT ¡TRAICIÓN EN LIGHTER!
Lighter, el exchange de perpetuos, amaneció con $15.48 millones en USDC drenados de dos cuentas de market makers. Para mí, lo más grave no es el monto: es que unas llaves API filtradas bastaron para vaciar las cuentas sin que el protocolo se rompiera.
Miren el detalle que nadie está viendo:
→ La cuenta #714710 perdió $10.39M y la #714723 otros $5.09M, en la mañana de hoy 16 de noviembre.
→ El atacante creó un pool público con 0% de comisión, compró el 99.99% con apenas ~$10,000 y sacó los fondos en lotes de ~$1M.
→ Lo robado ya se cambió a ETH en CoW Swap y 640 ETH (~$1.12M) se pasaron a Hyperliquid para comprar 2,240 XMR, casi imposible de rastrear.
Lighter pausó los retiros y la creación de pools sin fecha de regreso, y su token $LIT cayó 9%, de $2.75 a $2.50.
¿Crees que los exchanges descentralizados son más seguros que los centralizados? 👇
$LIT $ETH $XMR
#HackCrypto #Lighter #SeguridadDeFi
Lighter, el exchange de perpetuos, amaneció con $15.48 millones en USDC drenados de dos cuentas de market makers. Para mí, lo más grave no es el monto: es que unas llaves API filtradas bastaron para vaciar las cuentas sin que el protocolo se rompiera.
Miren el detalle que nadie está viendo:
→ La cuenta #714710 perdió $10.39M y la #714723 otros $5.09M, en la mañana de hoy 16 de noviembre.
→ El atacante creó un pool público con 0% de comisión, compró el 99.99% con apenas ~$10,000 y sacó los fondos en lotes de ~$1M.
→ Lo robado ya se cambió a ETH en CoW Swap y 640 ETH (~$1.12M) se pasaron a Hyperliquid para comprar 2,240 XMR, casi imposible de rastrear.
Lighter pausó los retiros y la creación de pools sin fecha de regreso, y su token $LIT cayó 9%, de $2.75 a $2.50.
¿Crees que los exchanges descentralizados son más seguros que los centralizados? 👇
$LIT $ETH $XMR
#HackCrypto #Lighter #SeguridadDeFi
3.8k
·
--
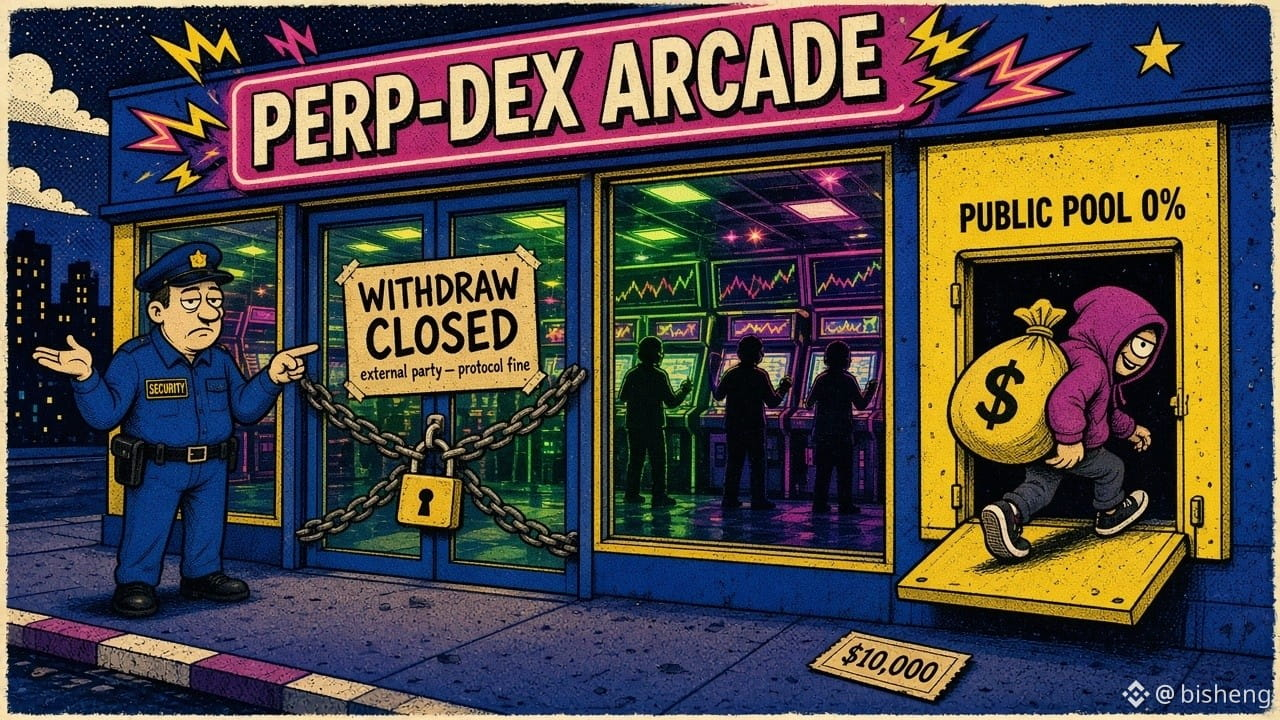
今晚 Lighter 自己发了公告。北京时间大约 19:02,@Lighter_xyz 说正在调查一起安全事件,看起来只涉及一个被攻破的外部主体。作为预防,全部提款先停,建池也停。什么时候重开,一条时间都没给。
钱在里面的人,现在先出不去。
链上这几小时把过程摊得比较清楚。Lookonchain 转发 @0xTria 的复盘:大约 1550 万美元的 USDC,从两个做市商账户被抽走。一个是 #714710,大约 1039 万;另一个 #714723,大约 509 万。官方到现在没认这个数字,也没说就是 API 密钥泄露,但这条路径跟链上对得上。按复盘,大概发生在今天下午 5 点 41 分到 6 点 25 分(北京时间)。
走法并不复杂。先把这两个账户的仓位平掉,把保证金腾出来。再用受害人的账户建一个 0 手续费的公共池,扔进去大约 1 万美元,就把份额拿到接近 99.99%。接着把受害人的 USDC 按大约 100 万一块倒进这个池子,再赎回提走。有链上观察看到,攻击地址先在 CoW Protocol 把钱换成了以太坊,后面拆到别的钱包,还有部分往 Hyperliquid 和门罗那边流。
复盘里有一句很关键。Lighter 的 API 密钥本来不能直接把钱转到别人账户,那一步还要 L1 钱包签名。可同一条 L1 地址下面的账户互转,不用再签一次。受害人自己建的公共池,又算他自己的账户。所以密钥一旦漏了,池子就变成提款通道。一万刀买到出口。这不是什么高深攻击,是权限就留了口。
官方现在把事说成「外部单一主体」,协议没事。这是在给自己摘干净。站不住。他们连建池都停了,等于承认这条路走得通。密钥是入口,池子规则是出口,两个问题都在。还在跟你强调「不是智能合约漏洞」的人,是在玩定义。
交易照样能开仓平仓,钱就是取不出来。这不叫去中心化,这叫平台一句话把闸关上了。
刚才看到 LIT 大约 2.59 美元,比前收大约 2.87 跌了将近 10%。Upbit、Bithumb 已经按官方公告暂停了 LIT 充提。币价和韩国站这边已经先动了,没人在等事后报告。
有分析把两个账户往一家伦敦做市商 Abraxas Capital 上靠,说其中一笔最早是从他们已知的钱包打进来的。官方没点名,这件事先当未确认,别写成定论。
我的判断是:这件事过不了「外部密钥丢了」四个字。提款后面大概率会分批开。LIT 在韩国那两家能不能恢复进出,要看他们什么时候解除。要是池子那条权限不改,同样的走法还能再来一遍。钱还锁在里面的人,先别拿「协议没问题」当安慰。官方到现在没给重开时间表。池子规则改不改,比再发一条「外部主体」有用。
#Lighter #LIT
今晚 Lighter 自己发了公告。北京时间大约 19:02,@Lighter_xyz 说正在调查一起安全事件,看起来只涉及一个被攻破的外部主体。作为预防,全部提款先停,建池也停。什么时候重开,一条时间都没给。
钱在里面的人,现在先出不去。
链上这几小时把过程摊得比较清楚。Lookonchain 转发 @0xTria 的复盘:大约 1550 万美元的 USDC,从两个做市商账户被抽走。一个是 #714710,大约 1039 万;另一个 #714723,大约 509 万。官方到现在没认这个数字,也没说就是 API 密钥泄露,但这条路径跟链上对得上。按复盘,大概发生在今天下午 5 点 41 分到 6 点 25 分(北京时间)。
走法并不复杂。先把这两个账户的仓位平掉,把保证金腾出来。再用受害人的账户建一个 0 手续费的公共池,扔进去大约 1 万美元,就把份额拿到接近 99.99%。接着把受害人的 USDC 按大约 100 万一块倒进这个池子,再赎回提走。有链上观察看到,攻击地址先在 CoW Protocol 把钱换成了以太坊,后面拆到别的钱包,还有部分往 Hyperliquid 和门罗那边流。
复盘里有一句很关键。Lighter 的 API 密钥本来不能直接把钱转到别人账户,那一步还要 L1 钱包签名。可同一条 L1 地址下面的账户互转,不用再签一次。受害人自己建的公共池,又算他自己的账户。所以密钥一旦漏了,池子就变成提款通道。一万刀买到出口。这不是什么高深攻击,是权限就留了口。
官方现在把事说成「外部单一主体」,协议没事。这是在给自己摘干净。站不住。他们连建池都停了,等于承认这条路走得通。密钥是入口,池子规则是出口,两个问题都在。还在跟你强调「不是智能合约漏洞」的人,是在玩定义。
交易照样能开仓平仓,钱就是取不出来。这不叫去中心化,这叫平台一句话把闸关上了。
刚才看到 LIT 大约 2.59 美元,比前收大约 2.87 跌了将近 10%。Upbit、Bithumb 已经按官方公告暂停了 LIT 充提。币价和韩国站这边已经先动了,没人在等事后报告。
有分析把两个账户往一家伦敦做市商 Abraxas Capital 上靠,说其中一笔最早是从他们已知的钱包打进来的。官方没点名,这件事先当未确认,别写成定论。
我的判断是:这件事过不了「外部密钥丢了」四个字。提款后面大概率会分批开。LIT 在韩国那两家能不能恢复进出,要看他们什么时候解除。要是池子那条权限不改,同样的走法还能再来一遍。钱还锁在里面的人,先别拿「协议没问题」当安慰。官方到现在没给重开时间表。池子规则改不改,比再发一条「外部主体」有用。
#Lighter #LIT
钱在里面的人,现在先出不去。
链上这几小时把过程摊得比较清楚。Lookonchain 转发 @0xTria 的复盘:大约 1550 万美元的 USDC,从两个做市商账户被抽走。一个是 #714710,大约 1039 万;另一个 #714723,大约 509 万。官方到现在没认这个数字,也没说就是 API 密钥泄露,但这条路径跟链上对得上。按复盘,大概发生在今天下午 5 点 41 分到 6 点 25 分(北京时间)。
走法并不复杂。先把这两个账户的仓位平掉,把保证金腾出来。再用受害人的账户建一个 0 手续费的公共池,扔进去大约 1 万美元,就把份额拿到接近 99.99%。接着把受害人的 USDC 按大约 100 万一块倒进这个池子,再赎回提走。有链上观察看到,攻击地址先在 CoW Protocol 把钱换成了以太坊,后面拆到别的钱包,还有部分往 Hyperliquid 和门罗那边流。
复盘里有一句很关键。Lighter 的 API 密钥本来不能直接把钱转到别人账户,那一步还要 L1 钱包签名。可同一条 L1 地址下面的账户互转,不用再签一次。受害人自己建的公共池,又算他自己的账户。所以密钥一旦漏了,池子就变成提款通道。一万刀买到出口。这不是什么高深攻击,是权限就留了口。
官方现在把事说成「外部单一主体」,协议没事。这是在给自己摘干净。站不住。他们连建池都停了,等于承认这条路走得通。密钥是入口,池子规则是出口,两个问题都在。还在跟你强调「不是智能合约漏洞」的人,是在玩定义。
交易照样能开仓平仓,钱就是取不出来。这不叫去中心化,这叫平台一句话把闸关上了。
刚才看到 LIT 大约 2.59 美元,比前收大约 2.87 跌了将近 10%。Upbit、Bithumb 已经按官方公告暂停了 LIT 充提。币价和韩国站这边已经先动了,没人在等事后报告。
有分析把两个账户往一家伦敦做市商 Abraxas Capital 上靠,说其中一笔最早是从他们已知的钱包打进来的。官方没点名,这件事先当未确认,别写成定论。
我的判断是:这件事过不了「外部密钥丢了」四个字。提款后面大概率会分批开。LIT 在韩国那两家能不能恢复进出,要看他们什么时候解除。要是池子那条权限不改,同样的走法还能再来一遍。钱还锁在里面的人,先别拿「协议没问题」当安慰。官方到现在没给重开时间表。池子规则改不改,比再发一条「外部主体」有用。
#Lighter #LIT
161

Lighter 这事,现在满屏都在喊“不是协议被黑,只是做市商 API key 泄露”,评论区已经有人顺手喊抄底 LIT 了。我觉得这个说法恰恰是最该警惕的地方。
先说能核实的。社区分析(BlockBeats、@BimbaCrypto 等转述)说被掏的是两个大户账户 #714710 约1039万、#714723 约509万 USDC。我刚去 Lighter 公开 API 查了这两个账户:仓位全清,余额分别只剩1040.39和510.69 USDC。注意这两个数,正好约是原余额的万分之一。
这和社区还原的手法完全对得上:攻击者用受害账户建一个0手续费公共池,自己先放约1万刀拿到99.99%份额,再把受害账户的 USDC 分批挪进池子,然后赎回。受害人那边剩下的,就是那0.01%。
关键在权限设计。按社区分析,API key 本来不能直接往外部地址转钱,但同一个 L1 地址下的账户之间转账不需要额外签名,而受害账户自己建的池子被系统当成“自己的账户”。也就是说,一把只该用来下单的交易 key,绕一圈等于拿到了提款权。在 CEX 上大家开 API 都会关掉提币权限,就是为了防这种事;这里那道墙存在,但有个门没锁。
所以“不是协议漏洞”这句话我不太买账。合约没被打穿是真的,但让交易 key 能把钱搬走的规则就是协议的一部分。key 怎么丢的、是不是真的丢了,Lighter 截至我发帖还没出正式说明,这部分先别下结论。
链上那头:吴说引 Arkham,攻击地址 0xb3fff…e387 把1039万 USDC 通过 CoW 换成约5750枚 ETH;我刚查这个地址还剩约4804.5枚,已经在往外拆。
用 Lighter 跑 API 的兄弟,现在能做的就是把 key 全部作废重建,查一下自己 L1 下面有没有多出来不认识的池子或子账户。
Lighter 这事,现在满屏都在喊“不是协议被黑,只是做市商 API key 泄露”,评论区已经有人顺手喊抄底 LIT 了。我觉得这个说法恰恰是最该警惕的地方。
先说能核实的。社区分析(BlockBeats、@BimbaCrypto 等转述)说被掏的是两个大户账户 #714710 约1039万、#714723 约509万 USDC。我刚去 Lighter 公开 API 查了这两个账户:仓位全清,余额分别只剩1040.39和510.69 USDC。注意这两个数,正好约是原余额的万分之一。
这和社区还原的手法完全对得上:攻击者用受害账户建一个0手续费公共池,自己先放约1万刀拿到99.99%份额,再把受害账户的 USDC 分批挪进池子,然后赎回。受害人那边剩下的,就是那0.01%。
关键在权限设计。按社区分析,API key 本来不能直接往外部地址转钱,但同一个 L1 地址下的账户之间转账不需要额外签名,而受害账户自己建的池子被系统当成“自己的账户”。也就是说,一把只该用来下单的交易 key,绕一圈等于拿到了提款权。在 CEX 上大家开 API 都会关掉提币权限,就是为了防这种事;这里那道墙存在,但有个门没锁。
所以“不是协议漏洞”这句话我不太买账。合约没被打穿是真的,但让交易 key 能把钱搬走的规则就是协议的一部分。key 怎么丢的、是不是真的丢了,Lighter 截至我发帖还没出正式说明,这部分先别下结论。
链上那头:吴说引 Arkham,攻击地址 0xb3fff…e387 把1039万 USDC 通过 CoW 换成约5750枚 ETH;我刚查这个地址还剩约4804.5枚,已经在往外拆。
用 Lighter 跑 API 的兄弟,现在能做的就是把 key 全部作废重建,查一下自己 L1 下面有没有多出来不认识的池子或子账户。
先说能核实的。社区分析(BlockBeats、@BimbaCrypto 等转述)说被掏的是两个大户账户 #714710 约1039万、#714723 约509万 USDC。我刚去 Lighter 公开 API 查了这两个账户:仓位全清,余额分别只剩1040.39和510.69 USDC。注意这两个数,正好约是原余额的万分之一。
这和社区还原的手法完全对得上:攻击者用受害账户建一个0手续费公共池,自己先放约1万刀拿到99.99%份额,再把受害账户的 USDC 分批挪进池子,然后赎回。受害人那边剩下的,就是那0.01%。
关键在权限设计。按社区分析,API key 本来不能直接往外部地址转钱,但同一个 L1 地址下的账户之间转账不需要额外签名,而受害账户自己建的池子被系统当成“自己的账户”。也就是说,一把只该用来下单的交易 key,绕一圈等于拿到了提款权。在 CEX 上大家开 API 都会关掉提币权限,就是为了防这种事;这里那道墙存在,但有个门没锁。
所以“不是协议漏洞”这句话我不太买账。合约没被打穿是真的,但让交易 key 能把钱搬走的规则就是协议的一部分。key 怎么丢的、是不是真的丢了,Lighter 截至我发帖还没出正式说明,这部分先别下结论。
链上那头:吴说引 Arkham,攻击地址 0xb3fff…e387 把1039万 USDC 通过 CoW 换成约5750枚 ETH;我刚查这个地址还剩约4804.5枚,已经在往外拆。
用 Lighter 跑 API 的兄弟,现在能做的就是把 key 全部作废重建,查一下自己 L1 下面有没有多出来不认识的池子或子账户。
7
·
--
观点:Lighter或为做市商账户API密钥泄露,而非黑客攻击事件观点:Lighter或为做市商账户API密钥泄露,而非黑客攻击事件
11 月 16 日,Predicts.guru 创始人 @0xTria 转发韩国交易员研究结论称,Lighter 正在经历的不是协议级别黑客攻击,而是 2 个大做市商账户的 API 密钥泄露。
攻击者关闭了受害者的仓位,从受害者账户创建了一个 0% 费用的公共池,投入约 1 万美元以拥有 99.99% 的份额,然后将受害者的 USDC 以 100 万美元的块分批转入池中并赎回。Lighter 上的 API 密钥无法向他人发送资金,但同一 L1 地址上的账户之间转账无需签名,而由受害者创建的池被视为他们自己的账户。
受影响资金总计约 1550 万美元:来自 #714710 的 1039 万美元,来自 #714723 的 509 万美元。
查看原文:https://x.com/0xtria/status/2122280548047671629?s=46
观点:Lighter或为做市商账户API密钥泄露,而非黑客攻击事件
观点:Lighter或为做市商账户API密钥泄露,而非黑客攻击事件
11 月 16 日,Predicts.guru 创始人 @0xTria 转发韩国交易员研究结论称,Lighter 正在经历的不是协议级别黑客攻击,而是 2 个大做市商账户的 API 密钥泄露。
攻击者关闭了受害者的仓位,从受害者账户创建了一个 0% 费用的公共池,投入约 1 万美元以拥有 99.99% 的份额,然后将受害者的 USDC 以 100 万美元的块分批转入池中并赎回。Lighter 上的 API 密钥无法向他人发送资金,但同一 L1 地址上的账户之间转账无需签名,而由受害者创建的池被视为他们自己的账户。
受影响资金总计约 1550 万美元:来自 #714710 的 1039 万美元,来自 #714723 的 509 万美元。
查看原文:https://x.com/0xtria/status/2122280548047671629?s=46
11 月 16 日,Predicts.guru 创始人 @0xTria 转发韩国交易员研究结论称,Lighter 正在经历的不是协议级别黑客攻击,而是 2 个大做市商账户的 API 密钥泄露。
攻击者关闭了受害者的仓位,从受害者账户创建了一个 0% 费用的公共池,投入约 1 万美元以拥有 99.99% 的份额,然后将受害者的 USDC 以 100 万美元的块分批转入池中并赎回。Lighter 上的 API 密钥无法向他人发送资金,但同一 L1 地址上的账户之间转账无需签名,而由受害者创建的池被视为他们自己的账户。
受影响资金总计约 1550 万美元:来自 #714710 的 1039 万美元,来自 #714723 的 509 万美元。
查看原文:https://x.com/0xtria/status/2122280548047671629?s=46
8
තවත් අන්තර්ගතයන් ගවේෂණය කිරීමට ඇතුල් වන්න
Binance චතුරශ්රය හි ගෝලීය ක්රිප්ටෝ පරිශීලකයින් හා එක්වන්න
⚡️ ක්රිප්ටෝ පිළිබඳ නවතම සහ ප්රයෝජනවත් තොරතුරු ලබා ගන්න.
💬 ලොව විශාලතම ක්රිප්ටෝ හුවමාරුව මගින් විශ්වාස කෙරේ.
👍 සත්යායනය කරන ලද නිර්මාණකරුවන්ගෙන් සැබෑ විදසුන් සොයා ගන්න.
විද්යුත් තැපෑල / දුරකථන අංකය
නැගී එන මාතෘකා
1
#A Packed Week of Earnings and Data Tests Markets
82,717 නැරඹීම්
490 සාකච්ඡා කරමින්
2
#AnthropicIPOTestsInvestorAppetiteForAI
163,546 නැරඹීම්
1,754 සාකච්ඡා කරමින්
3
#NvidiaBoardNotConsideringHuang’sReturnasCEO
16,607 නැරඹීම්
244 සාකච්ඡා කරමින්
4
#WhatInvestmentSignalsDo13FFilingsReveal?
10,481 නැරඹීම්
177 සාකච්ඡා කරමින්
5
#GoldmanSachsAndMillenniumEachHeldOver$1.2BInBitcoinETFs
0 නැරඹීම්
1 සාකච්ඡා කරමින්
6
#InvescoStablecoinReservesFundLaunchesOnEthereum
4,230 නැරඹීම්
97 සාකච්ඡා කරමින්
7
#CypherpunkReports$306MQ3NetProfit
808 නැරඹීම්
16 සාකච්ඡා කරමින්
8
#OPTIMJACKAttackInfectsAtLeast186Websites
7,567 නැරඹීම්
124 සාකච්ඡා කරමින්
9
#StrategySells2.09MMSTRSharesFor$244.7M
2,255 නැරඹීම්
19 සාකච්ඡා කරමින්
10
#StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
8,884 නැරඹීම්
87 සාකච්ඡා කරමින්