When the hacker already has the keys, what is left to negotiate?
Chainflip just found out. The cross-chain swap protocol confirmed about $12M was drained from its vaults on Nov 21: 122.86 BTC, 520.22 ETH, 3.25M USDC and 758,141 USDT (Chainflip Labs, via Cointelegraph).
The number nearly tripled in a day. First reports only saw the Ethereum vault, $4.86M. The Bitcoin haul surfaced hours later.
And here is the twist: this was not a smart contract bug. Security firm Decurity says the attacker appears to have used a copy of the validator network's shared signing key. The prep work goes back to Tornado Cash funding on Nov 11 and a validator account registered on Nov 20. Chainflip has put the protocol in Safe Mode, with deposits, withdrawals, swaps and quotes all switched off.
So Chainflip made the attacker an offer: return 90% by 18:38 UTC on Nov 23, keep 10% (about $1.2M) as a bounty, and walk away as a white hat with law enforcement complaints withdrawn.
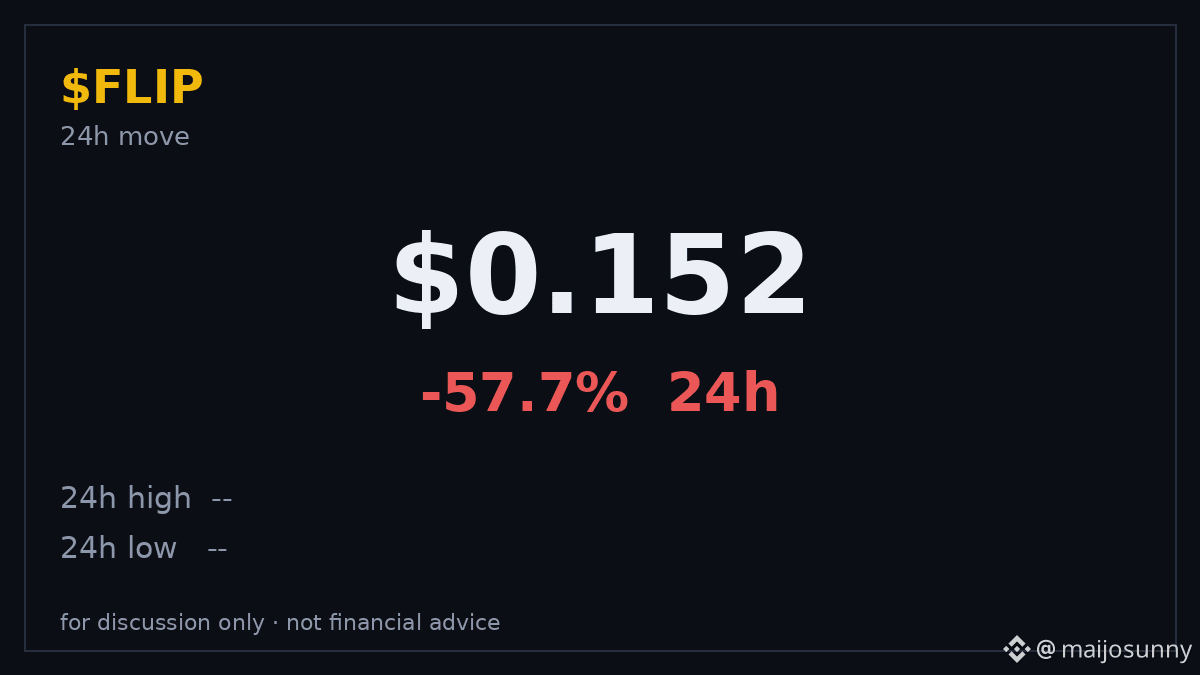
📉 $FLIP is down about 58% in 24h to $0.152 (CoinGecko).
Why it matters: cross-chain vaults hold native assets, so key management is the whole security model. A code audit does not help when the signing key itself is copied. Every bridge holding $BTC and $ETH in vaults is watching how this one ends.
My take: this is not really about the $12M anymore. It is about whether a 10% bounty can buy back a signing key compromise, or whether the attacker would rather sit on flagged coins that no exchange will touch.
Action Required:
- Do not click any "recovery" links or fake support accounts, scammers are already circling
- If you have funds in Chainflip, wait for the official reopening notice
- Verify return addresses only from Chainflip's official channels
Does the attacker take the $1.2M deal, or does this end in a manhunt? 👇
Not financial advice. DYOR.
#crypto #Chainflip #DeFi
Chainflip just found out. The cross-chain swap protocol confirmed about $12M was drained from its vaults on Nov 21: 122.86 BTC, 520.22 ETH, 3.25M USDC and 758,141 USDT (Chainflip Labs, via Cointelegraph).
The number nearly tripled in a day. First reports only saw the Ethereum vault, $4.86M. The Bitcoin haul surfaced hours later.
And here is the twist: this was not a smart contract bug. Security firm Decurity says the attacker appears to have used a copy of the validator network's shared signing key. The prep work goes back to Tornado Cash funding on Nov 11 and a validator account registered on Nov 20. Chainflip has put the protocol in Safe Mode, with deposits, withdrawals, swaps and quotes all switched off.
So Chainflip made the attacker an offer: return 90% by 18:38 UTC on Nov 23, keep 10% (about $1.2M) as a bounty, and walk away as a white hat with law enforcement complaints withdrawn.
📉 $FLIP is down about 58% in 24h to $0.152 (CoinGecko).
Why it matters: cross-chain vaults hold native assets, so key management is the whole security model. A code audit does not help when the signing key itself is copied. Every bridge holding $BTC and $ETH in vaults is watching how this one ends.
My take: this is not really about the $12M anymore. It is about whether a 10% bounty can buy back a signing key compromise, or whether the attacker would rather sit on flagged coins that no exchange will touch.
Action Required:
- Do not click any "recovery" links or fake support accounts, scammers are already circling
- If you have funds in Chainflip, wait for the official reopening notice
- Verify return addresses only from Chainflip's official channels
Does the attacker take the $1.2M deal, or does this end in a manhunt? 👇
Not financial advice. DYOR.
#crypto #Chainflip #DeFi