#sxt $SXT @SpaceandTime A small worry about agents showing each other proofs
Picture two trading bots meeting for the first time. Before they do any business, one hands the other a proof of its own track record.
That is roughly what the AI agents page in the Space and Time (@SpaceandTimeDB) docs describes. Agents swap zero-knowledge proofs of their internal state, such as performance numbers, past behavior and risk assessments, so each side can check the other meets some conditions first.
I like the idea. I also got stuck on one detail.
The insert docs list three ways data gets into a table. Chain data comes through indexers that must agree with each other. Web data arrives with a zkTLS check. And there are signed inserts, where someone signs a payload with their own key, which leaves a record of who submitted what.
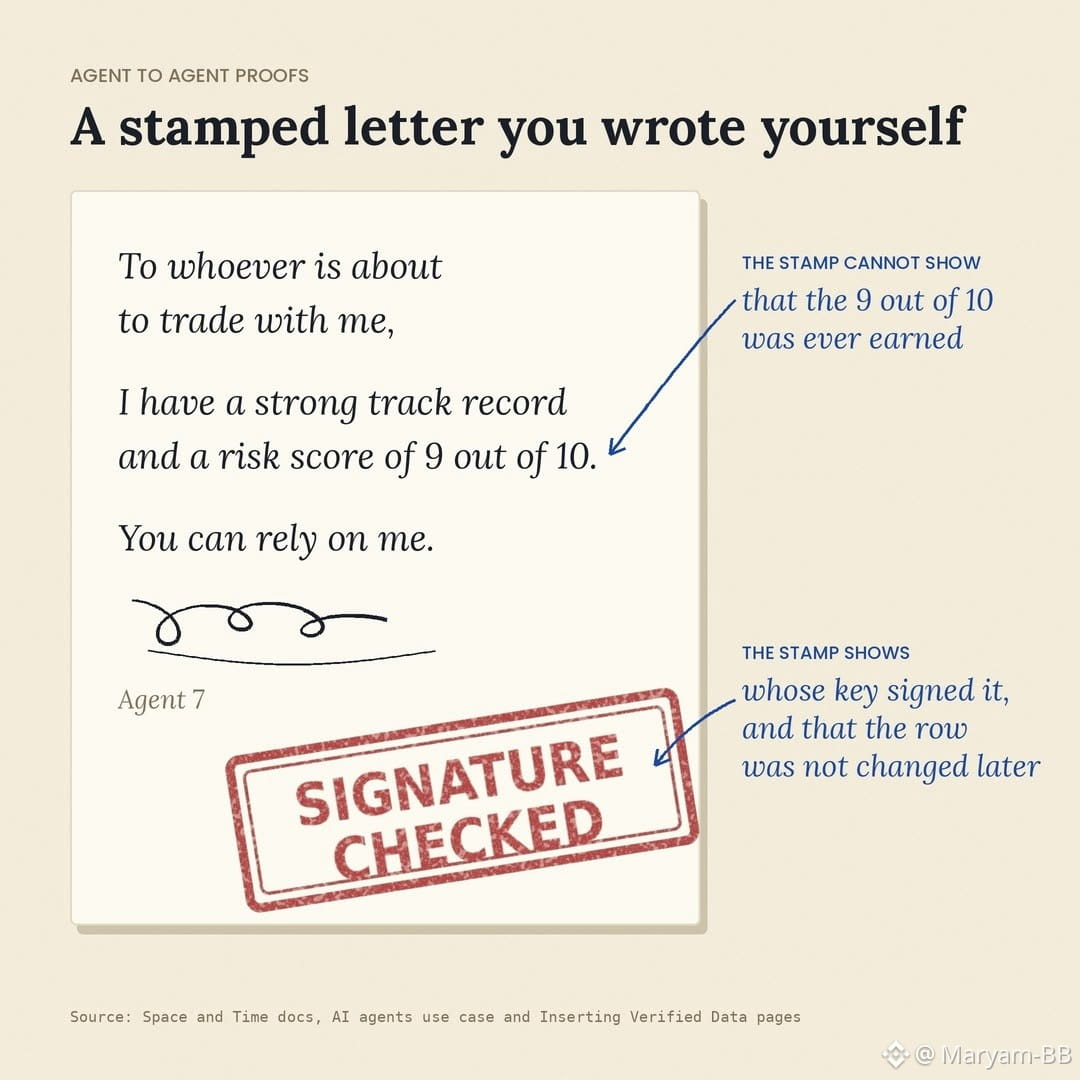
An agent's own risk assessment doesn't come from a chain or a website. My guess is it would be a signed insert. The proof could then show that the row exists, that nobody changed it, and that the query over it ran correctly.
It would not show the assessment was any good.
It reminds me of a reference letter you wrote about yourself and then had notarized. The notary only vouches for the signature, never for what the letter says.
Maybe I'm missing a step, because the page doesn't say how those rows get written. So I'm left with a plain question. How is one agent supposed to judge a score that only the other agent has ever vouched for?
Paid promotion: written for the Space and Time campaign on Binance Square CreatorPad.
Purchasing SXT is risky. You are encouraged to DYOR and to consult professional advice before buying SXT or any other cryptocurrency.
Picture two trading bots meeting for the first time. Before they do any business, one hands the other a proof of its own track record.
That is roughly what the AI agents page in the Space and Time (@SpaceandTimeDB) docs describes. Agents swap zero-knowledge proofs of their internal state, such as performance numbers, past behavior and risk assessments, so each side can check the other meets some conditions first.
I like the idea. I also got stuck on one detail.
The insert docs list three ways data gets into a table. Chain data comes through indexers that must agree with each other. Web data arrives with a zkTLS check. And there are signed inserts, where someone signs a payload with their own key, which leaves a record of who submitted what.
An agent's own risk assessment doesn't come from a chain or a website. My guess is it would be a signed insert. The proof could then show that the row exists, that nobody changed it, and that the query over it ran correctly.
It would not show the assessment was any good.
It reminds me of a reference letter you wrote about yourself and then had notarized. The notary only vouches for the signature, never for what the letter says.
Maybe I'm missing a step, because the page doesn't say how those rows get written. So I'm left with a plain question. How is one agent supposed to judge a score that only the other agent has ever vouched for?
Paid promotion: written for the Space and Time campaign on Binance Square CreatorPad.
Purchasing SXT is risky. You are encouraged to DYOR and to consult professional advice before buying SXT or any other cryptocurrency.