


The refrigeration controllers hijacked overnight in hundreds of French supermarkets were running out-of-date firmware, Danfoss said. Attackers turned fridges up to 50 degrees Celsius, leaving stores to toss out fresh and frozen stock.
A source close to Prime Minister Sebastien Lecornu said that France’s cybersecurity agency, ANSSI, had discovered a vulnerability in software from Danfoss. The person said the agency had already reached out to the vendor.
Danfoss names AK-SM800 and AK-SC355 legacy controllers
Danish maker Danfoss said it was “aware of incidents in France affecting a limited number of refrigeration management systems.” It identified two product lines, the AK-SM800 and the AK-SC355.
Most of the affected hardware is legacy kit that “no longer receive software or security updates,” the company said. The affected units reportedly ran regulation software that predated version 4.
The affected systems “were running outdated firmware,” Danfoss said. It also said it had “long advised customers to keep supported systems updated with the latest firmware and to migrate legacy systems to current-generation solutions.”
A supermarket’s cold rooms and cold cabinets are controlled from one linked panel. The panel controls temperature and defrost cycles, short periods when equipment heats up to melt ice.
It looks like the attackers commandeered the defrost function and ran it nonstop at 50 degrees.
In August 2026, Team82 from Claroty published research on the Danfoss AK-SM 800A, the system manager that orchestrates a facility’s refrigeration controllers. The team disclosed three vulnerabilities: CVE-2025-41450, authentication bypass using a hidden password based on the current date; CVE-2025-41451, command injection in email-alert configuration leading to remote code execution after login; and CVE-2025-41452, Nginx configuration injection able to cause denial of service.
Danfoss patched the flaws in firmware R4.3.1. Researchers also uncovered thousands of such management interfaces exposed to the public internet.
There’s no confirmed connection between that research and this week’s attack.
Intermarché owner counts 150 stores hit for six hours
Les Mousquetaires, the owner of Intermarché, said refrigerators at about 150 of its stores were at 50 degrees for six hours overnight. All the food concerned was binned to forestall any health risk, the group said.
At an Intermarché in central Paris, staff tipped cartloads of thawed food into a skip. Melted ice cream spilled onto the pavement.
Carrefour said 80 of its supermarkets were hit and that the vast majority of its 6,000 outlets were untouched. Monoprix, which has some 490 stores in France, said 5% had been hit.
Going after equipment indispensable to preserving fresh products and feeding French shoppers “is of extreme gravity and is unprecedented,” Coopérative U CEO Dominique Schelcher wrote on X.
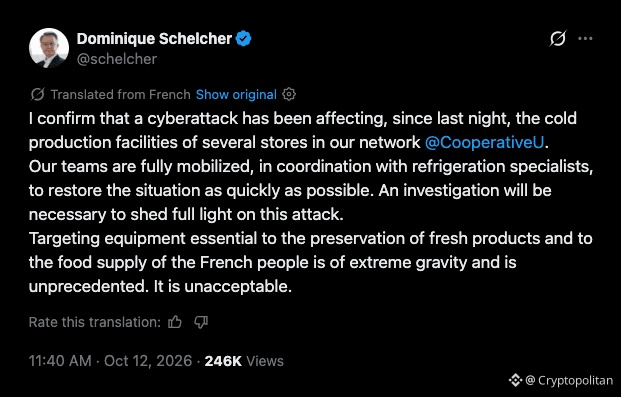 Coopérative U CEO Dominique Schelcher confirms the attack in a post on [X](https://x.com/schelcher/status/2109564928881308012) on October 12, 2026, shown in X’s English translation.
Thierry Cotillard, CEO of Intermarché, estimated the potential losses at tens of millions of euros across the country in a single day. Paris prosecutors opened an investigation into what they described as a large-scale attack.
Attacks also hit Spain, Portugal, Poland, Germany and Belgium, Sekoia threat analyst Felix Aime said.
Earlier this year, Cryptopolitan reported that France’s tax authority had suffered a breach leading to a loss of some 700,000 taxpayers’ data. Then the government announced it would hire sovereign AI firms like Mistral, and not OpenAI, to probe public systems for weaknesses.
If you're reading this, you’re already ahead. Stay there with our newsletter.