
BITGET $387.5M HACK: WITHDRAWALS REOPEN TODAY AS THORCHAIN WAR HEATS UP
The biggest crypto hack of 2026 👇
🔰 WHAT HAPPENED: On September 24, attackers drained $387.5M from Bitget's hot and warm wallets. They didn't steal private keys. They spoofed backend transfer data and tricked Bitget's own approval system.
✅ Cold wallets untouched
✅ User balances unchanged
✅ Deposits and trading never stopped
❌ Withdrawals frozen since September 24
Bitget's CEO points to a suspected North Korea link. There is no official government attribution yet.
🔰 ARE FUNDS SAFE? Bitget says its $464M+ User Protection Fund covers the full loss.
Still with the Attacker:
➡️ 63,000 ETH ($183M)
➡️ 102M XRP ($157M)
➡️ Only ~$318K frozen So Far
Nothing meaningful has been recovered yet.
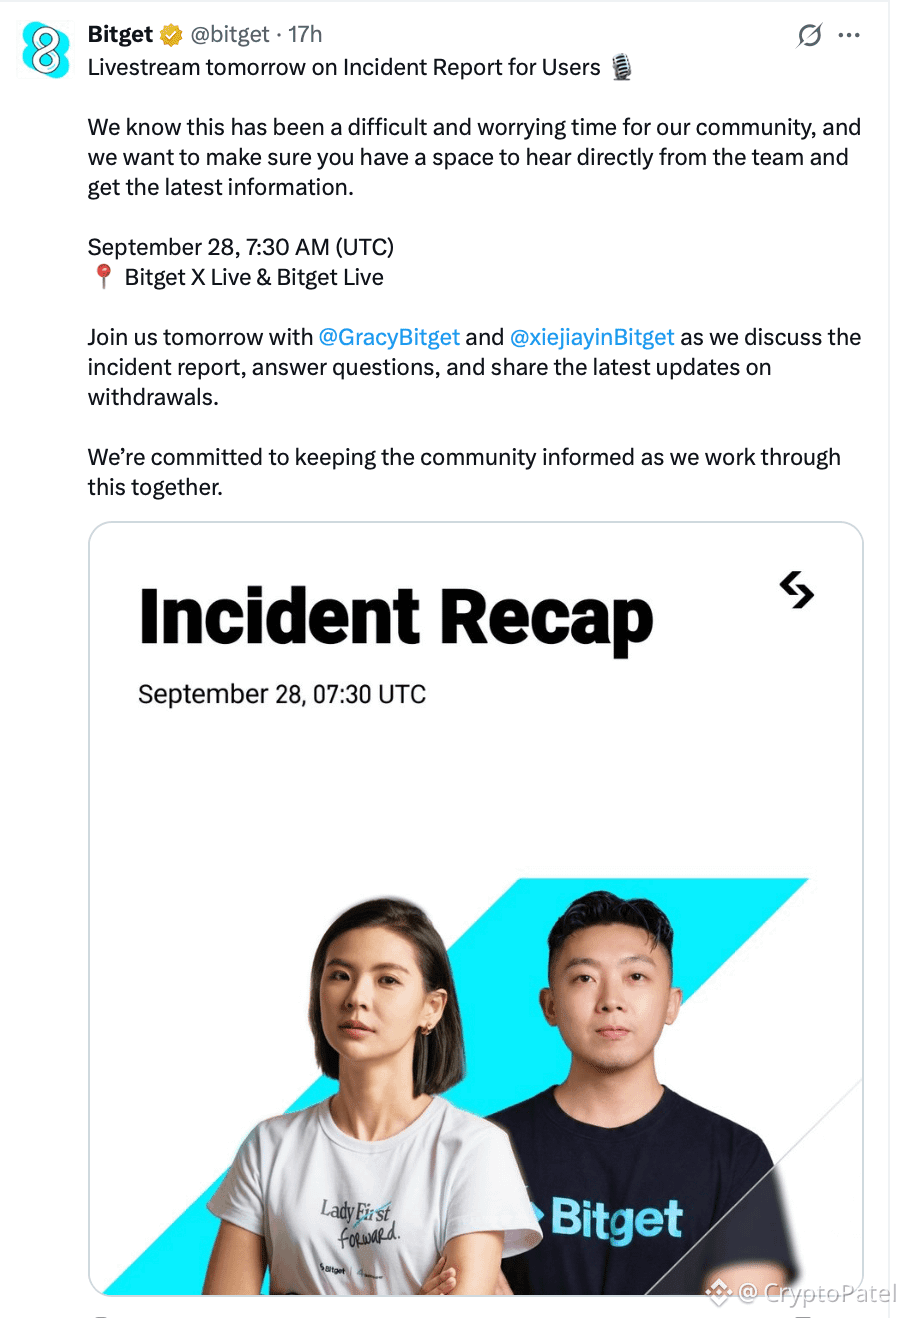
🔰 WITHDRAWAL SCHEDULE (08:00 UTC / 1:30 PM IST)
🟠 Sept 28: $BTC
🔵 Sept 29: $ETH
🟢 Sept 30: $USDT
⚪ Oct 2: Other tokens, fiat, P2P
Bounty: 5% for frozen funds and 5% for recovered funds. It's not a "10% bounty."
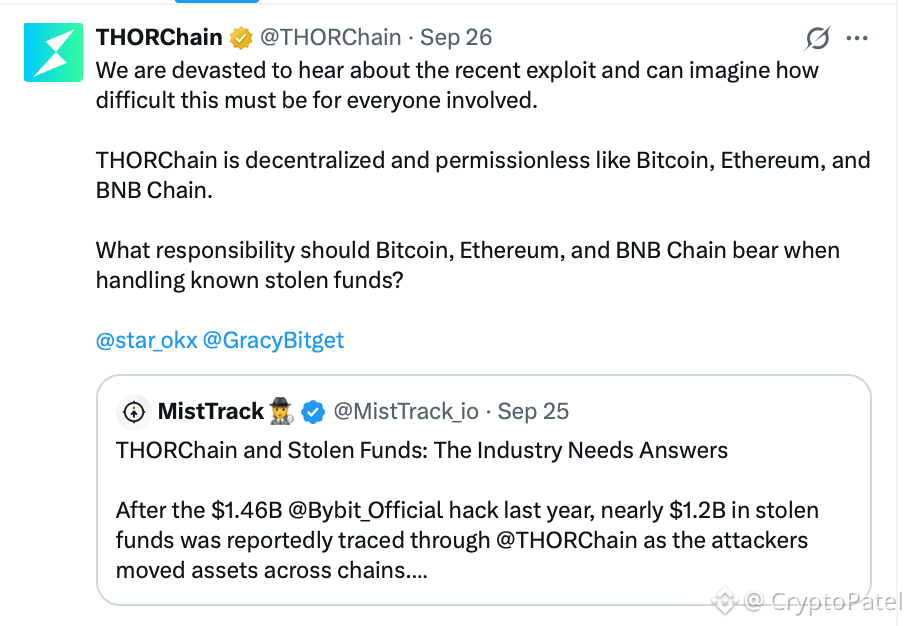
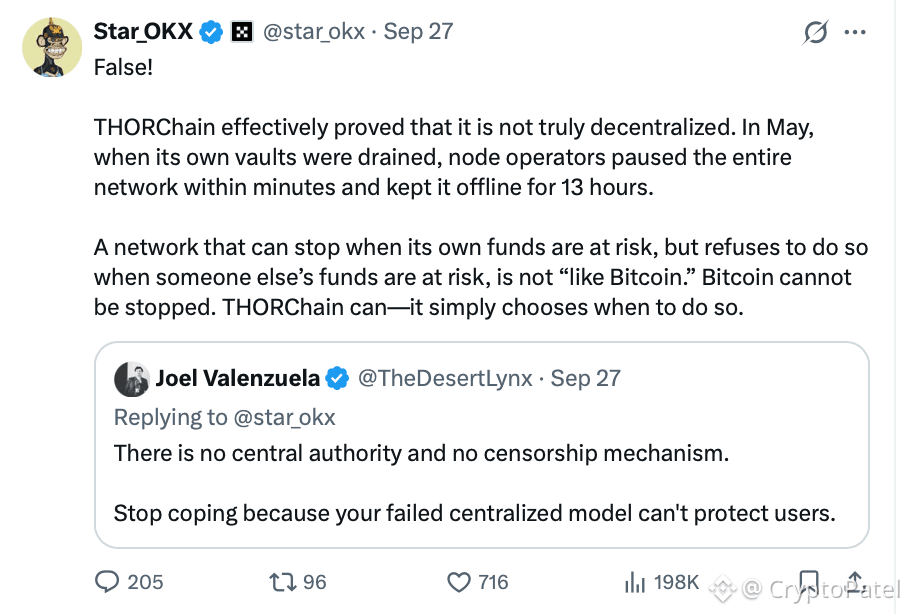
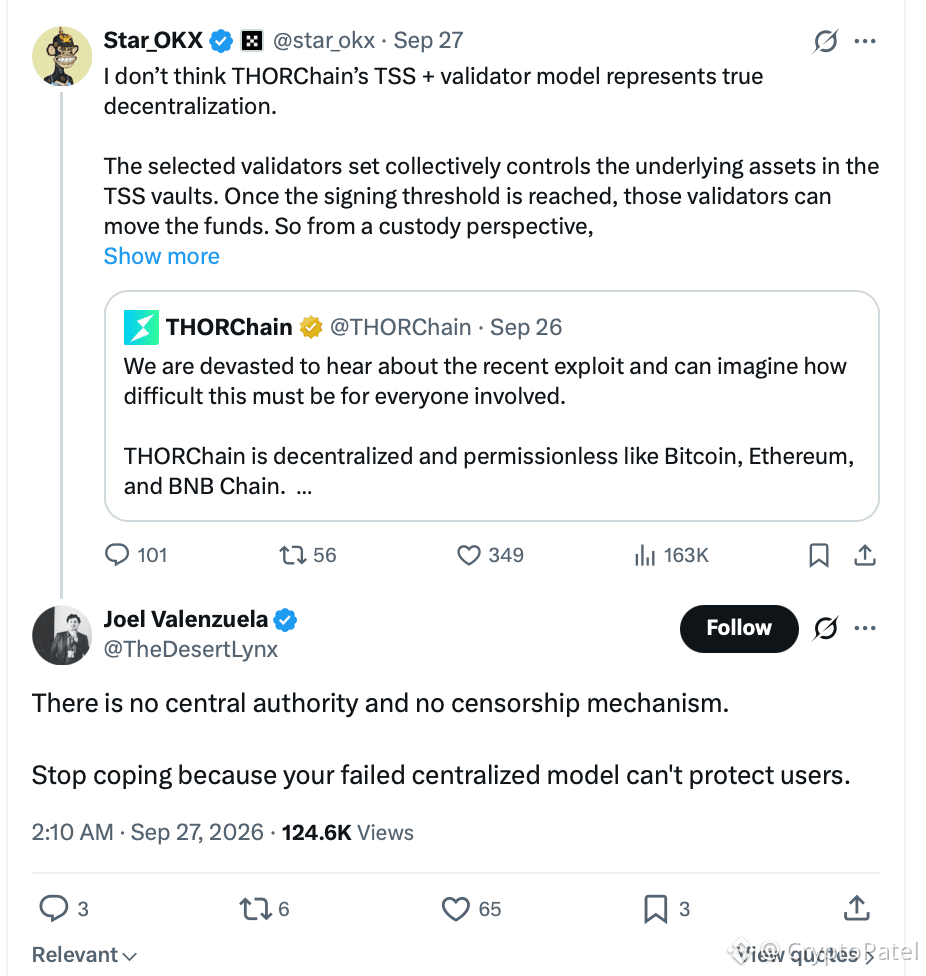
🔰 THORCHAIN WAR: The stolen funds are being swapped into BTC through THORChain, the same route used after the Bybit hack. Bitget asked THORChain to block the attacker addresses, and THORChain refused, saying it is "permissionless like Bitcoin."
But in May 2026, THORChain halted its entire network within hours after losing $10.7M of its own funds, and stayed offline for over five weeks.
So the brake exists. The question is who it's used for.
🔰 DOG DELISTING: Hours after the hack, with withdrawals frozen, Bitget announced the DOG/USDT delisting for September 30. Holders were trapped and the price decoupled. Bitget calls it a routine review, but the timing hurt users.
🔰 CRYPTOPATEL TAKEAWAYS:
✅ Never keep more on an exchange than you actively trade
✅ Judge Bitget by today's withdrawals, not by statements
✅ Watch RUNE, since pressure on THORChain is rising
Should THORChain block hacker addresses? Comment 👇
#BitgetHack #THORChain #CryptoHack