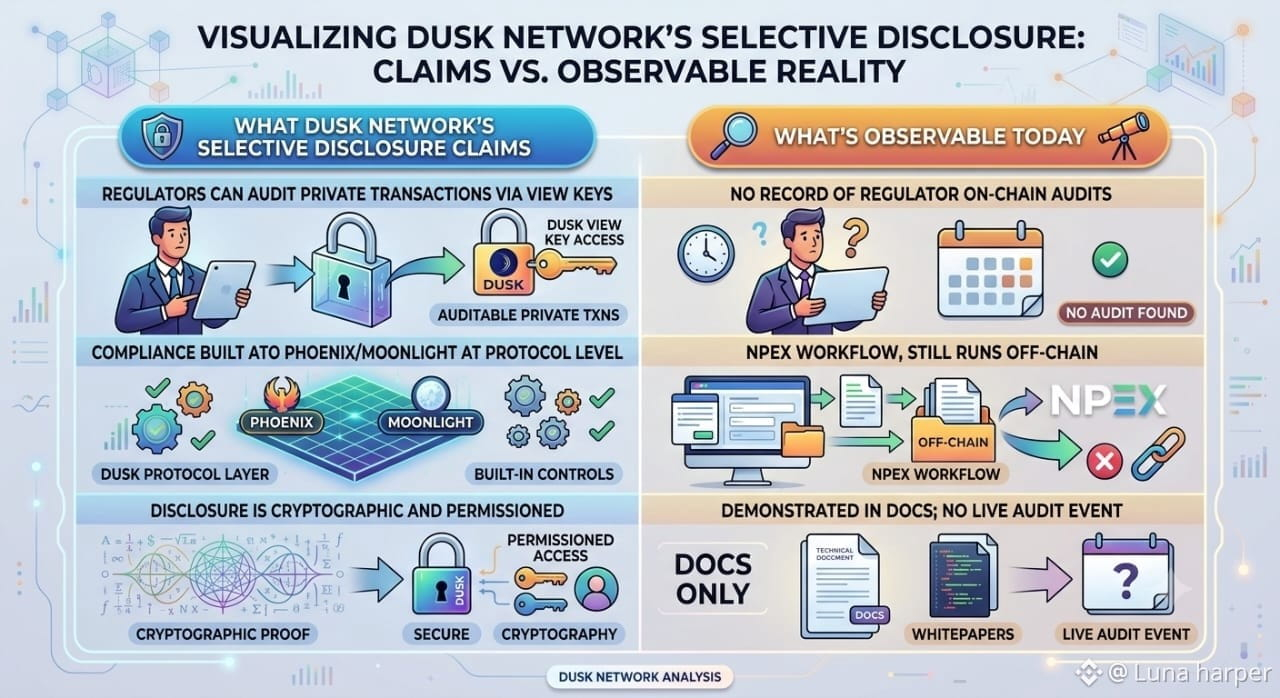
I kept staring at the phrase "selective disclosure" every time it showed up in Dusk Network's docs, because it gets used like a settled feature rather than something anyone has actually exercised. $DUSK #Dusk @Dusk frames Phoenix and Moonlight as giving regulators the ability to audit a private transaction without exposing it publicly, which is the actual answer to the securities-privacy tension the project claims to solve. What I couldn't find was a documented instance of that disclosure path being triggered by an external party in production, as opposed to being demonstrated in a technical writeup. The NPEX integration is the closest real testbed, since it's the licensed venue where disclosure requirements aren't hypothetical, but even there the compliance workflow still leans on off-chain reporting rather than an auditor pulling a view key on-chain. So the primitive exists at the protocol level, and the regulatory need for it is real, but the two haven't visibly met yet in a transaction anyone outside the team can point to. I keep coming back to whether the first real test of this will be an on-chain view-key grant tied to an actual NPEX disclosure event, or whether it quietly stays a filing that never touches the chain it was built for.


Publicar
Aviso legal: inclui opiniões de terceiros. Não constitui aconselhamento. A Binance AI pode ser utilizada sem garantia. Consulta os Termos e Condições.