
North Korea's nuclear weapons are not funded by traditional revenue sources like coal or taxes, but are supported by stolen cryptocurrency. On July 18, 2024, North Korea's top government hacker group, Lazarus Group, launched a bold attack on WazirX, India's largest cryptocurrency exchange.
In just over an hour, this group stole more than $200 million and vanished before any response could catch up. The attack was organized like a professional military campaign. The heist at WazirX was just one of many activities directly linked to Lazarus.
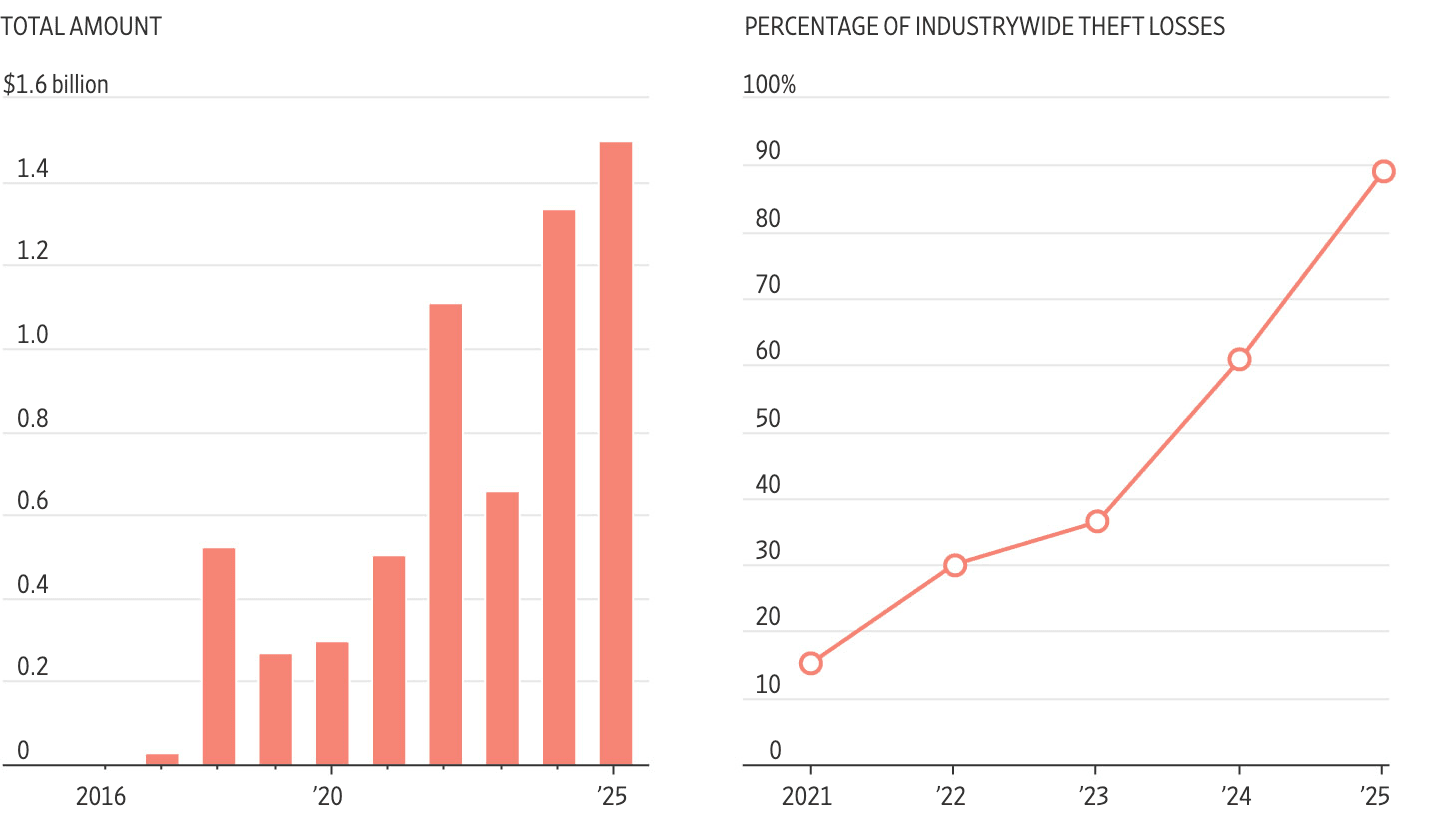
Over the past 10 years, Lazarus has stolen more than $6 billion, making this group the most dangerous cryptocurrency thief in the world. According to a report from the Wall Street Journal, Lazarus's activities play a crucial role in maintaining Kim Jong Un's regime while funding the nuclear program despite strict international sanctions.
Lazarus: Assembling the best minds of North Korea
Benedict Hamilton, CEO at Kroll – the company assisting WazirX in tracing the theft, stated that the speed and level of automation of this group suggest that the stolen money may have been converted to cash immediately after the attack occurred.
With nearly half of its assets lost, WazirX was forced to suspend operations. A spokesperson for the exchange said they are working to recover users' funds and expect to be back in operation soon.
Lazarus is formed from the brightest minds of North Korea, and this group is not in a hurry with their campaigns. They spend months, even years, researching targets, creating fake profiles, and seeking a single weakness to exploit.
To infiltrate company systems, Lazarus uses personal information from employees' Instagram, LinkedIn, and Facebook, then builds personalized phishing tricks to lure them into clicking on links containing malware.
Some Lazarus members even applied for remote jobs at U.S. tech companies using fake identities, passing interviews and working within the system to access data. These campaigns are organized and operated like professional military operations, backed by the state.
North Korea and the cryptocurrency theft strategy
In February 2024, Lazarus executed the largest theft in the group's history – stealing $1.5 billion from Bybit, one of the largest cryptocurrency exchanges in the world. According to a report from Chainalysis, in just 2024, North Korea was responsible for over 60% of the stolen funds in the entire cryptocurrency sector.
This country has built a formidable cyber army with over 8,000 hackers working full-time, organized into military-style groups and supported by many smaller units, according to the Wall Street Journal.
Children with talents in mathematics or science are selected early and trained intensively to become hackers. They do not have side jobs but dedicate all their time to cyber attack activities.
Even though they live better than most North Korean citizens, these hackers face immense pressure and severe forms of punishment if they fail. Elma Duval, co-author of a report from the Seoul-based advocacy group PScore, interviewed former IT staff and revealed that hackers are often physically punished if they do not complete their tasks.
Kim Jong Il, the late leader of North Korea, once stated that future wars would be conducted by computers. This vision became a national strategy under Kim Jong Un.
With traditional revenue sources such as arms trading, coal smuggling, and foreign labor choked by international sanctions, North Korea has been forced to seek new income sources. The country's intelligence agency estimates that North Korea needs about $6 billion a year, including hundreds of millions to maintain its nuclear weapons program.
Cryptocurrency becomes an ideal choice: fast, low cost, and hard to trace. Although Pyongyang has never publicly claimed responsibility for any attacks, U.S. officials say Lazarus often leaves traces, including malware and wallets reused from previous hacks.
This group has been accused of involvement in major attacks such as the 2014 Sony hack, the 2016 Bangladesh central bank heist, and the 2017 WannaCry ransomware attack.
Lazarus: New targets are cryptocurrency ETF funds and job seekers
In September 2024, the FBI issued a warning that Lazarus was targeting companies related to ETF funds. This is an attractive market segment with $37 billion in investment inflows last year, including funds from BlackRock, Fidelity, and many other large companies. Lazarus used emails containing custom-designed malware targeting each victim.
In December 2024, a U.S. court charged 14 North Koreans for stealing the identities of Americans and applying for jobs at U.S. tech companies and non-profit organizations. These Lazarus members referred to themselves as 'IT warriors,' earning $88 million in salaries, all of which were sent directly back to North Korea.
These jobs provide them direct access to company systems and data. Some cryptocurrency companies have confirmed being attacked by fake applicants.
Ben Turner, head of engineering at Cloudburst Technologies – a cryptocurrency intelligence firm, said: 'We are increasingly noticing the presence of North Korean hackers around us.' His team also reported a significant increase in suspicious job applications, indicating that Lazarus is expanding its operations.
Disclaimer: This article is for informational purposes only and not investment advice. Investors should conduct thorough research before making decisions. We are not responsible for your investment decisions.


