

#circletetherfreezebitgethackerwallet
circletetherfreezebitgethackerwallet
113,834 views
1,554 Discussing
ရေပန်းစားသော
နောက်ဆုံး
#CircleTetherFreezeBitgetHackerWallet Circle and Tether blacklisted a wallet linked to the Bitget exploit, freezing roughly $318,000 in USDC and USDT. The action came after the Bitget breach in which approximately $351.6 million in assets were affected.
However, most of the stolen funds remained outside the reach of stablecoin issuers, with more than 63,000 ETH reportedly still held across exploiter-linked wallets.
#Circle #Tether #USDC #USDT $USDC
{spot}(USDCUSDT)
$USDT $ETH
{spot}(ETHUSDT)
#CircleTetherFreezeBitgetHackerWallet Circle and Tether blacklisted a wallet linked to the Bitget exploit, freezing roughly $318,000 in USDC and USDT. The action came after the Bitget breach in which approximately $351.6 million in assets were affected.
However, most of the stolen funds remained outside the reach of stablecoin issuers, with more than 63,000 ETH reportedly still held across exploiter-linked wallets.
#Circle #Tether #USDC #USDT $USDC
$USDT $ETH
However, most of the stolen funds remained outside the reach of stablecoin issuers, with more than 63,000 ETH reportedly still held across exploiter-linked wallets.
#Circle #Tether #USDC #USDT $USDC
$USDT $ETH
1
38
·
--
Circle has frozen a Tether wallet linked to a Bitget hacker, marking a significant move in the ongoing battle against illicit activities in the crypto space. This action highlights the increasing collaboration between major players to enhance security and compliance. The market is watching closely to see how this impacts trust and regulatory scrutiny on stablecoins and exchanges. Such proactive measures, while potentially disruptive in the short term, are crucial for the long-term health and adoption of digital assets. The incident underscores the importance of robust security protocols for all participants in the ecosystem.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#CircleTetherFreezeBitgetHackerWallet
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#CircleTetherFreezeBitgetHackerWallet
79
·
--
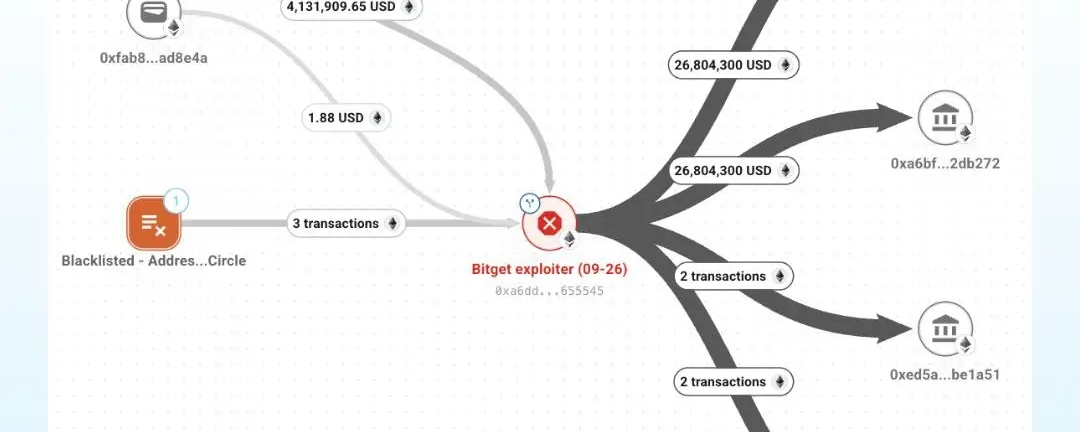
Article
📽️🍿 And the Media Circus 🎪 around the Bitget hack continues !What happened & timeline of events
🦹The Hacker has entered Bitget exchange draining it for $385M 💰 in various crypto currencies.
⏳The first "suspicious" transfer was noticed 3 HOURS BEFORE Bitget actualy reacted
They have been alerted more times during this 3 hours ,one time by Bubblemaps who saw huge amounts being drained to a new wallet and split into more places right after - which is well known tackics hackers use.
🤯 There was NO 🙂↔️ private keys exploit, the whole heist happened because Bitget's system itself ALLOWED it to happened.
👉 3hours later.... They finally reacted and stoped the withdrawals.
🔶Big exchanges reacted to the news and offered help, among them was our very own @CZ showing it's full support and offering help to Bitget in this troubled times . Other exchanges offered help also, showing sympathy and crypto communities standing together in the face of unfortunate events 🌪️
💱 Tether and Circle have jumped in to help, promising they I'll freeze the hackers known address stablecoins . Now this guest as noble as it looks opened a whole avalanche of questions
👉 It Tether and Circle can Freeze someone's address, what's stoping them from freezing our assets if some bank or organisation SKS them ? The very nature of crypto is being put under a big question ❓ Decentralisation or Not quite ?
This spiced up even more when Bitget's CEO Gracy Chan reached out to Thor Chain - the chain that stands by decentralisation stronger than many others Also, one of the most attacked and blamed for "not helping " in many cases like this one Thor Chain makes their point - we are truly decentralised, we can't just pause all withdrawals for all users cause it's convenient Also have you asked Bitcoin, Etherium , BNB CHAIN to stop their withdrawals too - cause most of the money is going through those chains?
Making a hard point on decentralisation and the nature of crypto , Thor Chain ⛓️ Takes their stand here. Users are devided - half say great for Thor, decentralisation should always be respected , that's why it exists , while the other half say
Thor Chain uses double standards - when they were hacked they did stoped withdrawals for 13h so it is possible.
Thor Chain ⛓️ sais - ask $BTC , $ETH and other chains to stop withdrawals, why are we always attacked ?
What is your take ?
Decentralisation on demand or always ?
#Hack
#CircleTetherFreezeBitgetHackerWallet
📽️🍿 And the Media Circus 🎪 around the Bitget hack continues !
What happened & timeline of events
🦹The Hacker has entered Bitget exchange draining it for $385M 💰 in various crypto currencies.
⏳The first "suspicious" transfer was noticed 3 HOURS BEFORE Bitget actualy reacted
They have been alerted more times during this 3 hours ,one time by Bubblemaps who saw huge amounts being drained to a new wallet and split into more places right after - which is well known tackics hackers use.
🤯 There was NO 🙂↔️ private keys exploit, the whole heist happened because Bitget's system itself ALLOWED it to happened.
👉 3hours later.... They finally reacted and stoped the withdrawals.
🔶Big exchanges reacted to the news and offered help, among them was our very own @CZ showing it's full support and offering help to Bitget in this troubled times . Other exchanges offered help also, showing sympathy and crypto communities standing together in the face of unfortunate events 🌪️
💱 Tether and Circle have jumped in to help, promising they I'll freeze the hackers known address stablecoins . Now this guest as noble as it looks opened a whole avalanche of questions
👉 It Tether and Circle can Freeze someone's address, what's stoping them from freezing our assets if some bank or organisation SKS them ? The very nature of crypto is being put under a big question ❓ Decentralisation or Not quite ?
This spiced up even more when Bitget's CEO Gracy Chan reached out to Thor Chain - the chain that stands by decentralisation stronger than many others Also, one of the most attacked and blamed for "not helping " in many cases like this one Thor Chain makes their point - we are truly decentralised, we can't just pause all withdrawals for all users cause it's convenient Also have you asked Bitcoin, Etherium , BNB CHAIN to stop their withdrawals too - cause most of the money is going through those chains?
Making a hard point on decentralisation and the nature of crypto , Thor Chain ⛓️ Takes their stand here. Users are devided - half say great for Thor, decentralisation should always be respected , that's why it exists , while the other half say
Thor Chain uses double standards - when they were hacked they did stoped withdrawals for 13h so it is possible.
Thor Chain ⛓️ sais - ask $BTC , $ETH and other chains to stop withdrawals, why are we always attacked ?
What is your take ?
Decentralisation on demand or always ?
#Hack
#CircleTetherFreezeBitgetHackerWallet
3
2.2k
·
--
တက်ရိပ်ရှိသည်
#circletetherfreezebitgethackerwallet
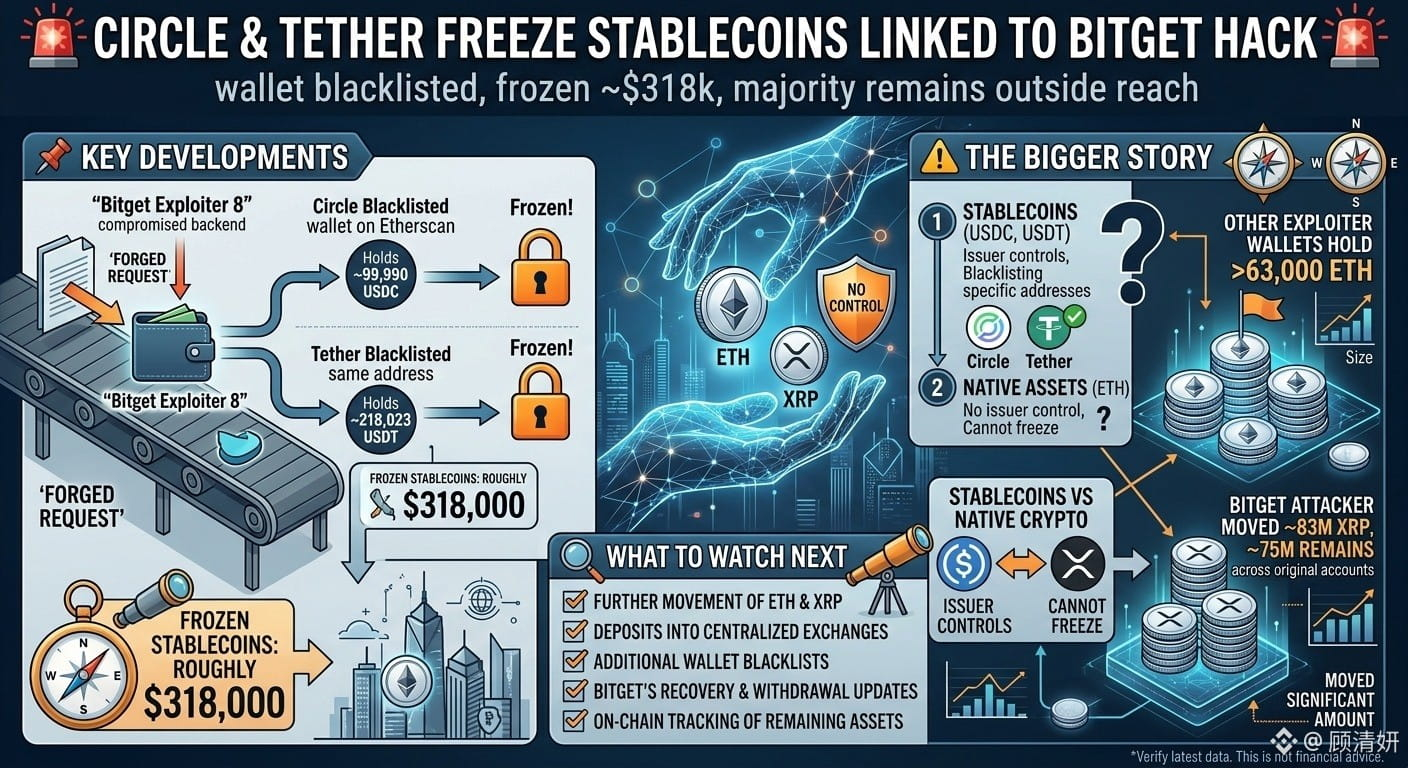
🚨 CIRCLE & TETHER FREEZE STABLECOINS LINKED TO BITGET HACK
Circle and Tether have blacklisted a wallet linked to the recent Bitget security breach, freezing roughly $318,000 worth of USDC and USDT.
But the majority of the stolen assets remain outside the reach of stablecoin issuers.
📌 KEY DEVELOPMENTS
• Circle blacklisted a wallet identified as “Bitget Exploiter 8” on Etherscan.
• The wallet held approximately 99,990 USDC and 218,023 USDT.
• Tether subsequently blacklisted the same address.
• The frozen stablecoins are worth roughly $318,000.
• Other exploiter-linked wallets reportedly still hold more than 63,000 ETH.
• Stablecoin issuers can freeze their own tokens, but they cannot freeze native ETH held by an attacker.
⚠️ THE BIGGER STORY
The incident highlights an important difference between stablecoins and native crypto assets.
USDC and USDT include issuer-level controls that allow Circle and Tether to blacklist specific addresses.
ETH does not have an issuer with the same type of control.
Meanwhile, the Bitget attacker has also moved a significant amount of stolen XRP. CoinDesk reported that roughly $83 million in XRP had been moved from three original holding wallets, with about $75 million remaining across the original accounts at the time of its report.
🔎 WHAT TO WATCH
• Further movement of the stolen ETH and XRP
• Deposits into centralized exchanges
• Additional wallet blacklists
• Bitget's recovery and withdrawal updates
• On-chain tracking of the remaining assets
This is not just another exchange hack story. It shows how the ability to freeze assets can differ dramatically depending on the underlying blockchain and token design.
$SUPER $GRAM $PYTH
{future}(PYTHUSDT)
{future}(GRAMUSDT)
{future}(SUPERUSDT)
#circletetherfreezebitgethackerwallet
🚨 CIRCLE & TETHER FREEZE STABLECOINS LINKED TO BITGET HACK
Circle and Tether have blacklisted a wallet linked to the recent Bitget security breach, freezing roughly $318,000 worth of USDC and USDT.
But the majority of the stolen assets remain outside the reach of stablecoin issuers.
📌 KEY DEVELOPMENTS
• Circle blacklisted a wallet identified as “Bitget Exploiter 8” on Etherscan.
• The wallet held approximately 99,990 USDC and 218,023 USDT.
• Tether subsequently blacklisted the same address.
• The frozen stablecoins are worth roughly $318,000.
• Other exploiter-linked wallets reportedly still hold more than 63,000 ETH.
• Stablecoin issuers can freeze their own tokens, but they cannot freeze native ETH held by an attacker.
⚠️ THE BIGGER STORY
The incident highlights an important difference between stablecoins and native crypto assets.
USDC and USDT include issuer-level controls that allow Circle and Tether to blacklist specific addresses.
ETH does not have an issuer with the same type of control.
Meanwhile, the Bitget attacker has also moved a significant amount of stolen XRP. CoinDesk reported that roughly $83 million in XRP had been moved from three original holding wallets, with about $75 million remaining across the original accounts at the time of its report.
🔎 WHAT TO WATCH
• Further movement of the stolen ETH and XRP
• Deposits into centralized exchanges
• Additional wallet blacklists
• Bitget's recovery and withdrawal updates
• On-chain tracking of the remaining assets
This is not just another exchange hack story. It shows how the ability to freeze assets can differ dramatically depending on the underlying blockchain and token design.
$SUPER $GRAM $PYTH
صقرالكريبتو1:
إذا كنت مهتمًا بمبادرات ومكافآت مجتمع Binance Square، يمكنك الاطلاع على التفاصيل هنا:
https://app.binance.com/uni-qr/cpos/371236206995198?r=BJVUISWL&l=ar&uco=85gobSlX7-HA00IdwCDWsg&uc=app_square_share_link&us=copylink
4
13
13.9k

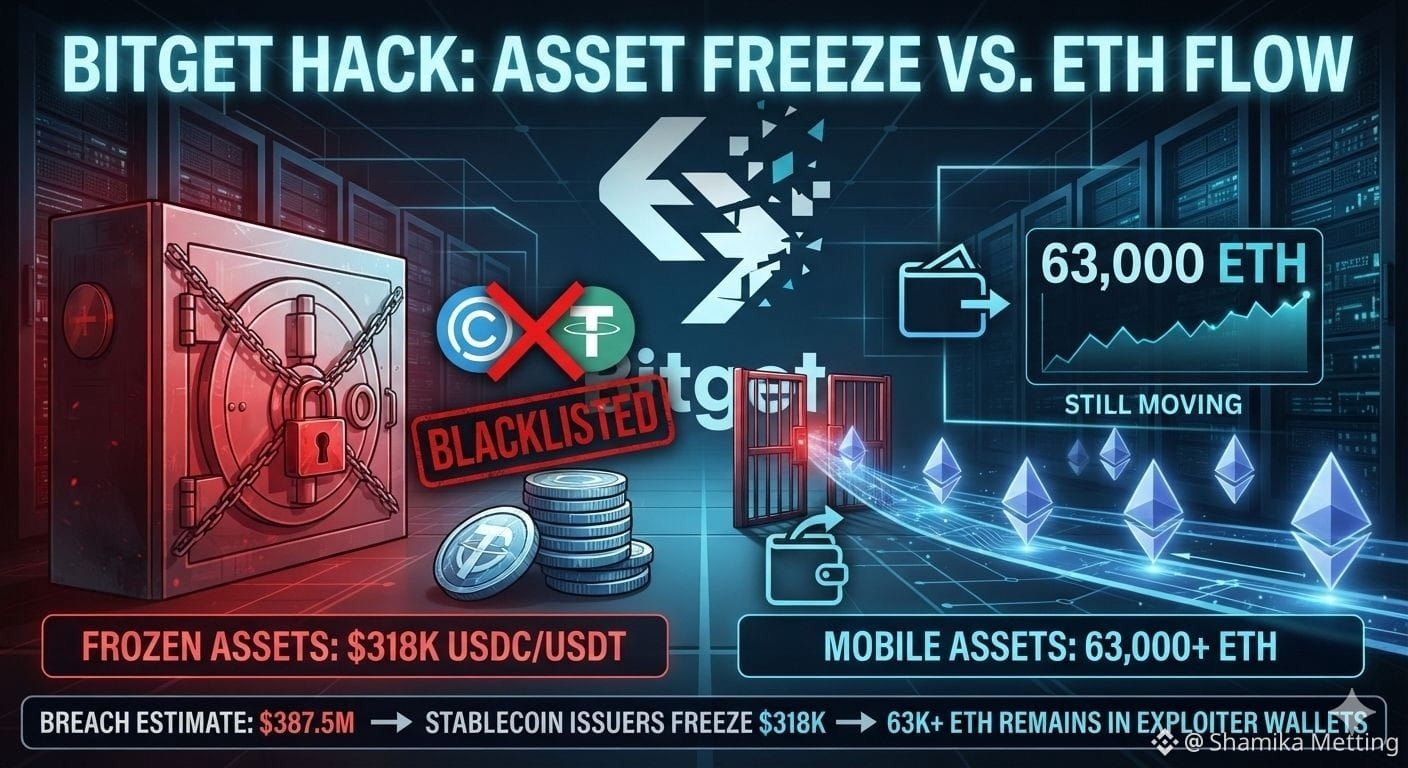
#circletetherfreezebitgethackerwallet 🚨 اختراق BITGET: تم تجميد 318 ألف دولار. لكن 63 ألف+ ETH ما زالت تتحرك
أظهر استغلال Bitget واحدًا من حقائق أمن العملات المشفرة.
قامت Circle وTether بإدراج محفظة أحد المخترقين ضمن القوائم السوداء، ما أدى إلى تجميد حوالي 318 ألف دولار من USDC وUSDT.
لكن هذه هي القصة 👇
🔹 يُقدَّر الآن أن اختراق Bitget وصل إلى حوالي 387.5 مليون دولار
🔹 أكثر من 63,000 ETH لا تزال موجودة في المحافظ المرتبطة بالمستغل
🔹 لا يمكن تجميد ETH من قبل مُصدري العملات المستقرة
🔹 تقول Bitget إن الهجوم شمل اختراق بنية تحتية للواجهة الخلفية وليس تسريبًا
🔹 تقول Bitget إن صندوق الحماية لديها البالغ 464 مليون دولار+ يغطي خسائر المستخدمين
📌 خلاصة المتداول: راقب المحافظ وحركات ETH/XRP عن كثب. التحويلات الكبيرة، إلى البورصات قد تزيد ضغط البيع.
السؤال الحقيقي: هل سيستمر المخترق في الاحتفاظ بـ ETH أم سيبدأ في توزيع ETH عبر المحافظ؟
ما الذي تتابعه؟ تدفقات ETH أم تحديثات تعافي Bitget؟ 👇
متابعة من فضلكم
#Crypto #Ethereum #Bitget
$ETH $BTC $SOL
1
3
6.4k

📊 Bitget Hack: What Crypto Traders Should Watch
Bitget says the breach affected approximately $387.5M in assets, while its protection fund is intended to cover customer losses.
Circle and Tether have already frozen a small portion of the stolen stablecoins.
Now watch $ETH and $XRP wallet movements closely — on-chain data can reveal the next move before headlines do. 🔎
#circletetherfreezebitgethackerwallet
3
2k
·
--
တက်ရိပ်ရှိသည်
#CircleTetherFreezeBitgetHackerWallet Circle and Tether froze about $318,000 in USDC and USDT linked to the Bitget hack. They were able to blacklist those stablecoins because the tokens have issuer-level freeze controls. �$NVDAB
#CircleTetherFreezeBitgetHackerWallet Circle and Tether froze about $318,000 in USDC and USDT linked to the Bitget hack. They were able to blacklist those stablecoins because the tokens have issuer-level freeze controls. �$NVDAB
1
13
Article
#circletetherfreezeBitgethackerwallet#CircleTetherFreezeBitgetHackerWallet
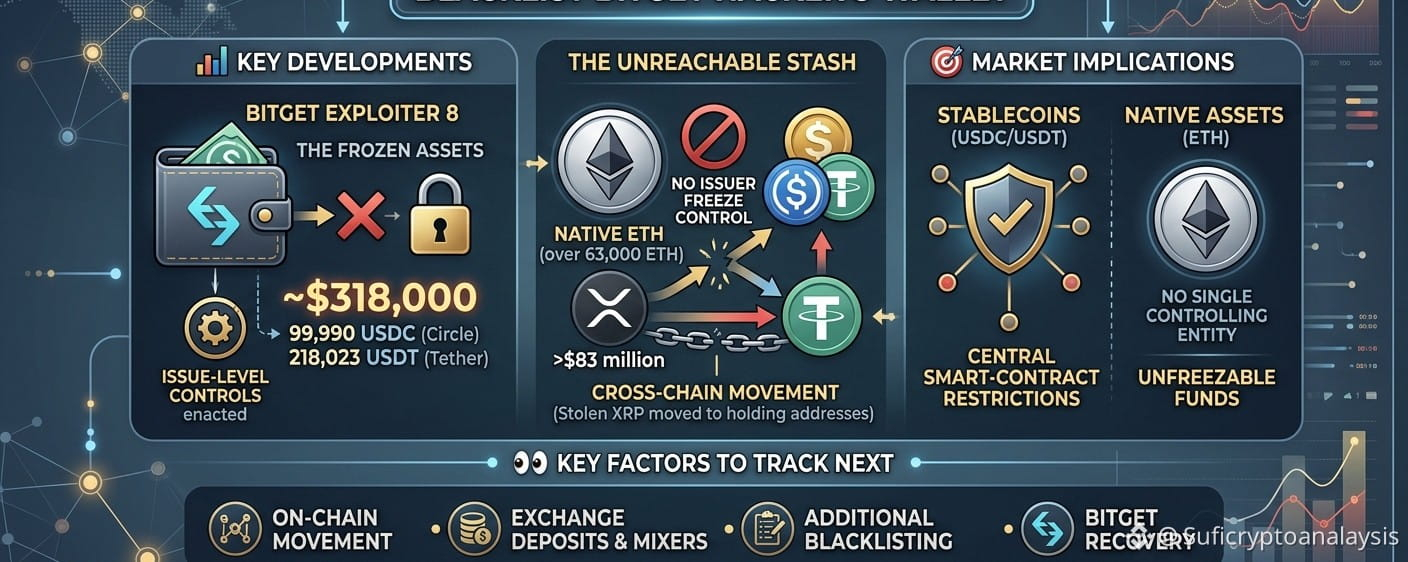
🌐 Asset Freeze: Circle & Tether Blacklist Bitget Hacker’s WalletIn a swift security response, major stablecoin issuers Circle and Tether have blacklisted a digital wallet directly tied to the recent security breach Bitget exchange. Together, the companies have successfully frozen roughly$318,000 worth of liquidity, showcasing the powerful clawback capabilities built into modern stablecoins.📊 Key DevelopmentsThe Frozen Assets: The blacklisted address (labeled "Bitget Exploiter 8" on Etherscan) contained 99,990 USDC and 218,023 USDT.Stablecoin Controls:Both Circle and Tether enacted their issuer-level controls to lock down these specific tokens, rendering them completely unmovable.The Unreachable Stash:Despite the freeze, the attacker still holds massive reserves beyond control, including over 63,000 native Ethereum (ETH).Cross-Chain Movement: Reports indicate the exploiter has also initiated massive movements of stolen XRP, shifting roughly $83 million across various holding addresses.🎯 Market ImplicationsThis incident highlights a fundamental structural difference in decentralized finance: stablecoins (USDC/USDT) possess central smart-contract restrictions allowing issuers to block wallets, whereas native assets like ETH do not have a single entity with the power to freeze funds. While the frozen amount is a small fraction of the total stolen bounty, it limits the attacker’s immediate off-ramp capabilities and underscores why hackers rapidly swap stablecoins into native assets or privacy coins.👀 Key Factors to Track NextOngoing on-chain movement of the stolen ETH and remaining XRP holdings.Potential hacker attempts to deposit funds into centralized exchanges using mixers.Additional blacklisting requests by law enforcement or cybersecurity firms.Official recovery timelines and system upgradeupdatesfromtheBitgetteam.How do you view this balance between centralization and decentralization? Is the ability to freeze assets a necessary security net, or does it go against the true ethos of crypto?
$SUPER $GRAM $PYTH
{spot}(PYTHUSDT)
{spot}(GRAMUSDT)
{spot}(SUPERUSDT)
#circletetherfreezeBitgethackerwallet
#CircleTetherFreezeBitgetHackerWallet
🌐 Asset Freeze: Circle & Tether Blacklist Bitget Hacker’s WalletIn a swift security response, major stablecoin issuers Circle and Tether have blacklisted a digital wallet directly tied to the recent security breach Bitget exchange. Together, the companies have successfully frozen roughly$318,000 worth of liquidity, showcasing the powerful clawback capabilities built into modern stablecoins.📊 Key DevelopmentsThe Frozen Assets: The blacklisted address (labeled "Bitget Exploiter 8" on Etherscan) contained 99,990 USDC and 218,023 USDT.Stablecoin Controls:Both Circle and Tether enacted their issuer-level controls to lock down these specific tokens, rendering them completely unmovable.The Unreachable Stash:Despite the freeze, the attacker still holds massive reserves beyond control, including over 63,000 native Ethereum (ETH).Cross-Chain Movement: Reports indicate the exploiter has also initiated massive movements of stolen XRP, shifting roughly $83 million across various holding addresses.🎯 Market ImplicationsThis incident highlights a fundamental structural difference in decentralized finance: stablecoins (USDC/USDT) possess central smart-contract restrictions allowing issuers to block wallets, whereas native assets like ETH do not have a single entity with the power to freeze funds. While the frozen amount is a small fraction of the total stolen bounty, it limits the attacker’s immediate off-ramp capabilities and underscores why hackers rapidly swap stablecoins into native assets or privacy coins.👀 Key Factors to Track NextOngoing on-chain movement of the stolen ETH and remaining XRP holdings.Potential hacker attempts to deposit funds into centralized exchanges using mixers.Additional blacklisting requests by law enforcement or cybersecurity firms.Official recovery timelines and system upgradeupdatesfromtheBitgetteam.How do you view this balance between centralization and decentralization? Is the ability to freeze assets a necessary security net, or does it go against the true ethos of crypto?
$SUPER $GRAM $PYTH
4
Article
Circle & Tether Freeze Wallet Linked to Bitget ExploitThe recent Bitget security incident has sparked another major discussion about crypto security and stablecoin control.
Circle and Tether reportedly blacklisted a wallet connected to the exploit, freezing approximately $318,000 worth of USDC and USDT.
However, this represents only a small portion of the affected assets. A significant amount was reportedly converted into ETH, which cannot be directly frozen by USDC or USDT issuers.
This creates an interesting contrast.
Stablecoins: issuers can intervene and freeze specific tokens.
Native crypto assets: assets such as ETH operate without a centralized issuer capable of freezing the coins themselves.
The incident therefore raises a broader question for the crypto industry:
Does the ability to freeze stolen stablecoins provide an important security layer, or does it introduce a trade-off with the permissionless nature of cryptocurrency?
The investigation and movement of the affected funds remain an evolving story.
What is your view?
$USDC $USDT
#CircleTetherFreezeBitgetHackerWallet #Bitget
Circle & Tether Freeze Wallet Linked to Bitget Exploit
The recent Bitget security incident has sparked another major discussion about crypto security and stablecoin control.
Circle and Tether reportedly blacklisted a wallet connected to the exploit, freezing approximately $318,000 worth of USDC and USDT.
However, this represents only a small portion of the affected assets. A significant amount was reportedly converted into ETH, which cannot be directly frozen by USDC or USDT issuers.
This creates an interesting contrast.
Stablecoins: issuers can intervene and freeze specific tokens.
Native crypto assets: assets such as ETH operate without a centralized issuer capable of freezing the coins themselves.
The incident therefore raises a broader question for the crypto industry:
Does the ability to freeze stolen stablecoins provide an important security layer, or does it introduce a trade-off with the permissionless nature of cryptocurrency?
The investigation and movement of the affected funds remain an evolving story.
What is your view?
$USDC $USDT
#CircleTetherFreezeBitgetHackerWallet #Bitget
1
65
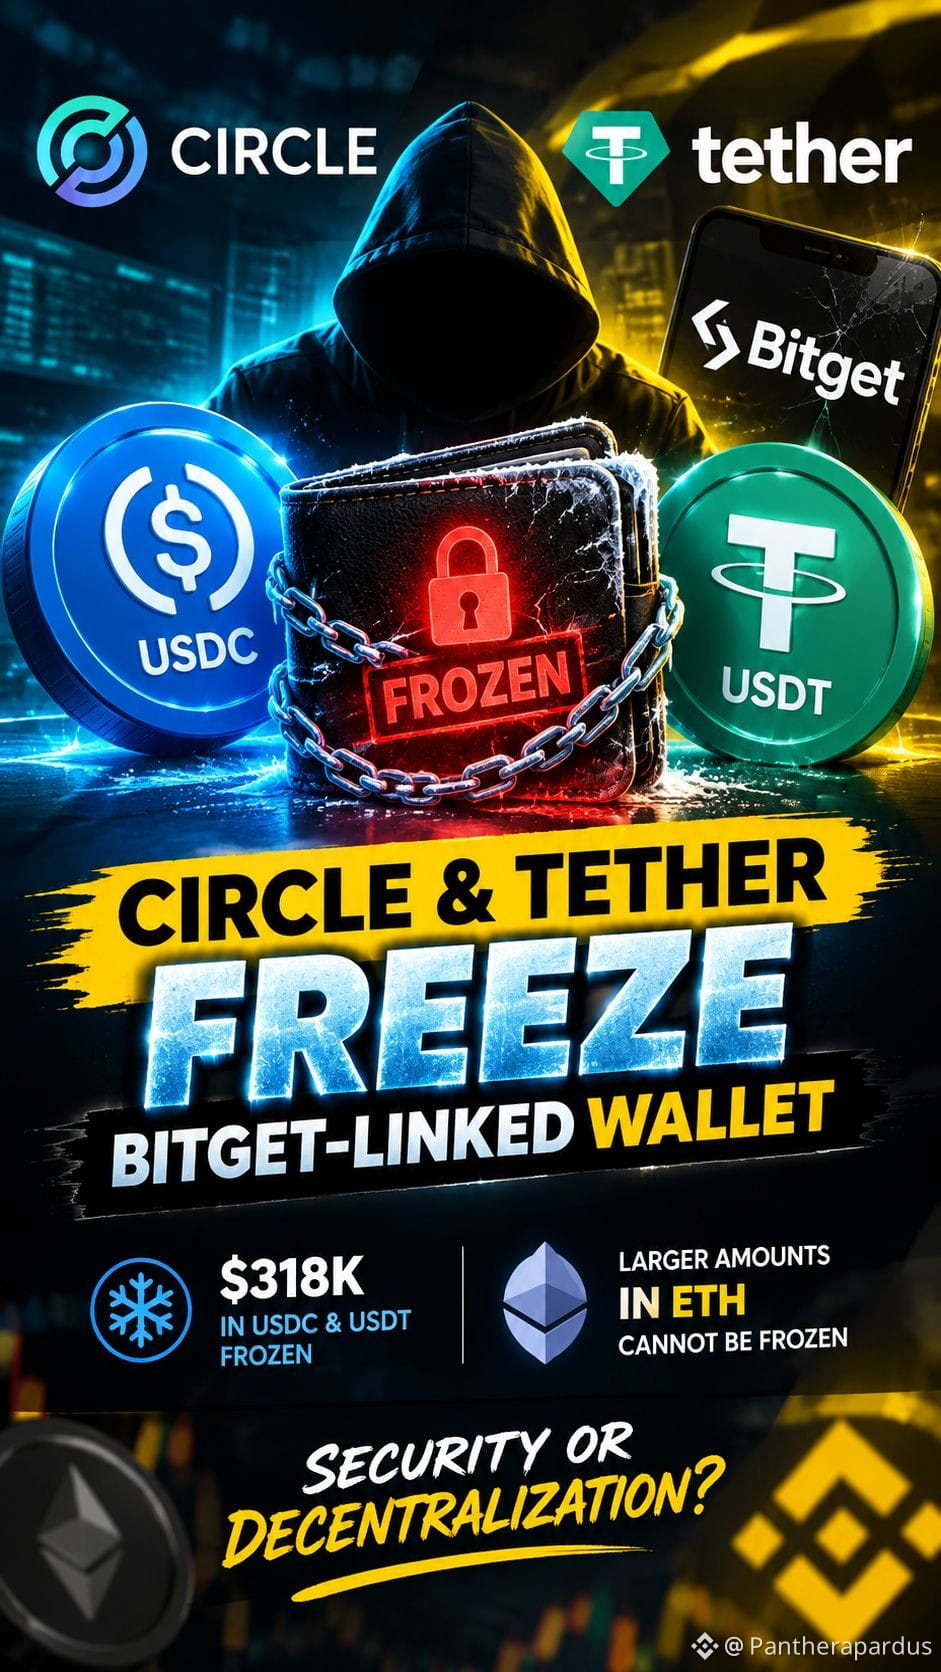
🚨 Circle & Tether Freeze Bitget-Linked Wallet
Circle and Tether have blacklisted a wallet linked to the recent Bitget exploit, freezing roughly $318,000 in USDC and USDT.
But here’s the interesting part: the majority of the stolen assets were reportedly moved into ETH, which cannot simply be frozen by a stablecoin issuer.
This incident highlights an important crypto-security question:
🔐 How should the industry balance asset recovery, security, and decentralization?
What do you think?
$USDC
{spot}(USDCUSDT)
$USDT
#CircleTetherFreezeBitgetHackerWallet #BinanceSquareTalks
🚨 Circle & Tether Freeze Bitget-Linked Wallet
Circle and Tether have blacklisted a wallet linked to the recent Bitget exploit, freezing roughly $318,000 in USDC and USDT.
But here’s the interesting part: the majority of the stolen assets were reportedly moved into ETH, which cannot simply be frozen by a stablecoin issuer.
This incident highlights an important crypto-security question:
🔐 How should the industry balance asset recovery, security, and decentralization?
What do you think?
$USDC
$USDT
#CircleTetherFreezeBitgetHackerWallet #BinanceSquareTalks
92

·
--
တက်ရိပ်ရှိသည်
#circletetherfreezebitgethackerwallet
🚨 Security Alert: Circle & Tether Intercept Exploiter Address Following Bitget Breach 🛡️
Rapid security coordination on-chain! Following a security incident where Bitget's backend wallet infrastructure was compromised, major stablecoin issuers Circle and Tether took swift action to blacklist and freeze an address labeled "Bitget Exploiter 8".
The joint response immobilized approximately $318,000 in stablecoins (99,990 USDC and 218,023 USDT) held in the targeted wallet, cutting off those specific assets from being laundered across secondary platforms.
$ZEC
{future}(ZECUSDT)
💡 Key Highlights:
🛑 Swift Blacklisting: Circle and Tether executed smart contract freezes within hours of security alerts from security firm MistTrack.
⚖️ Limits of On-Chain Freezes: While stablecoin issuers can freeze fiat-backed tokens (USDC/USDT), decentralized assets like Ethereum cannot be frozen. Trackers note that the attacker quickly converted a significant portion of stolen assets into ETH.
🛡️ Full Protection Covered: Bitget CEO Gracy Chen confirmed that private keys were not leaked and user assets are fully protected through Bitget's User Protection Fund (valued at over $400M).
What is your take on centralized stablecoin freezes—a vital safety net during exchange breaches or a reminder of central control in crypto? Share your view below! 👇
#CircleMints500MUSDCOnSolana #Bitget
#circletetherfreezebitgethackerwallet
🚨 Security Alert: Circle & Tether Intercept Exploiter Address Following Bitget Breach 🛡️
Rapid security coordination on-chain! Following a security incident where Bitget's backend wallet infrastructure was compromised, major stablecoin issuers Circle and Tether took swift action to blacklist and freeze an address labeled "Bitget Exploiter 8".
The joint response immobilized approximately $318,000 in stablecoins (99,990 USDC and 218,023 USDT) held in the targeted wallet, cutting off those specific assets from being laundered across secondary platforms.
$ZEC
💡 Key Highlights:
🛑 Swift Blacklisting: Circle and Tether executed smart contract freezes within hours of security alerts from security firm MistTrack.
⚖️ Limits of On-Chain Freezes: While stablecoin issuers can freeze fiat-backed tokens (USDC/USDT), decentralized assets like Ethereum cannot be frozen. Trackers note that the attacker quickly converted a significant portion of stolen assets into ETH.
🛡️ Full Protection Covered: Bitget CEO Gracy Chen confirmed that private keys were not leaked and user assets are fully protected through Bitget's User Protection Fund (valued at over $400M).
What is your take on centralized stablecoin freezes—a vital safety net during exchange breaches or a reminder of central control in crypto? Share your view below! 👇
#CircleMints500MUSDCOnSolana #Bitget
1
2.4k
*Bitget Hack Update — $XRP
{spot}(XRPUSDT)
#StrategyStriveAdd2305BitcoinThisWeek #DogecoinETFsPostBiggestWeekSinceLaunch #CircleTetherFreezeBitgetHackerWallet #SECSaysTokenBuybacksNotAutoSecurities The attacker has moved ∼$83M worth of stolen $XRP from 3 holding wallets.
Around 103M $XRpwas stolen in total — now ∼$75M still sits in wallets that _cannot be frozen_ under XRP Ledger rules. XRP is the native asset, so Ripple has no freeze button for it.
What _can_ be done:
- Exchanges can blacklist accounts that RECEIVE the stolen funds
- But they can't block the attacker's own wallets
For comparison: Circle and Tether already froze ∼$320K in related USDC/USDT — those tokens have blacklist controls.
Bitget says its protection fund will fully cover the $387.5M loss, customer balances are safe, and withdrawals will resume gradually Sept. 28 - Oct. 2.
Now the real question is: how much of this $XRP can be tracked / frozen when it hits CEXs? The on-chain chase is on. 7fa8
*Bitget Hack Update — $XRP
#StrategyStriveAdd2305BitcoinThisWeek #DogecoinETFsPostBiggestWeekSinceLaunch #CircleTetherFreezeBitgetHackerWallet #SECSaysTokenBuybacksNotAutoSecurities The attacker has moved ∼$83M worth of stolen $XRP from 3 holding wallets.
Around 103M $XRpwas stolen in total — now ∼$75M still sits in wallets that _cannot be frozen_ under XRP Ledger rules. XRP is the native asset, so Ripple has no freeze button for it.
What _can_ be done:
- Exchanges can blacklist accounts that RECEIVE the stolen funds
- But they can't block the attacker's own wallets
For comparison: Circle and Tether already froze ∼$320K in related USDC/USDT — those tokens have blacklist controls.
Bitget says its protection fund will fully cover the $387.5M loss, customer balances are safe, and withdrawals will resume gradually Sept. 28 - Oct. 2.
Now the real question is: how much of this $XRP can be tracked / frozen when it hits CEXs? The on-chain chase is on. 7fa8
113
·
--
တက်ရိပ်ရှိသည်
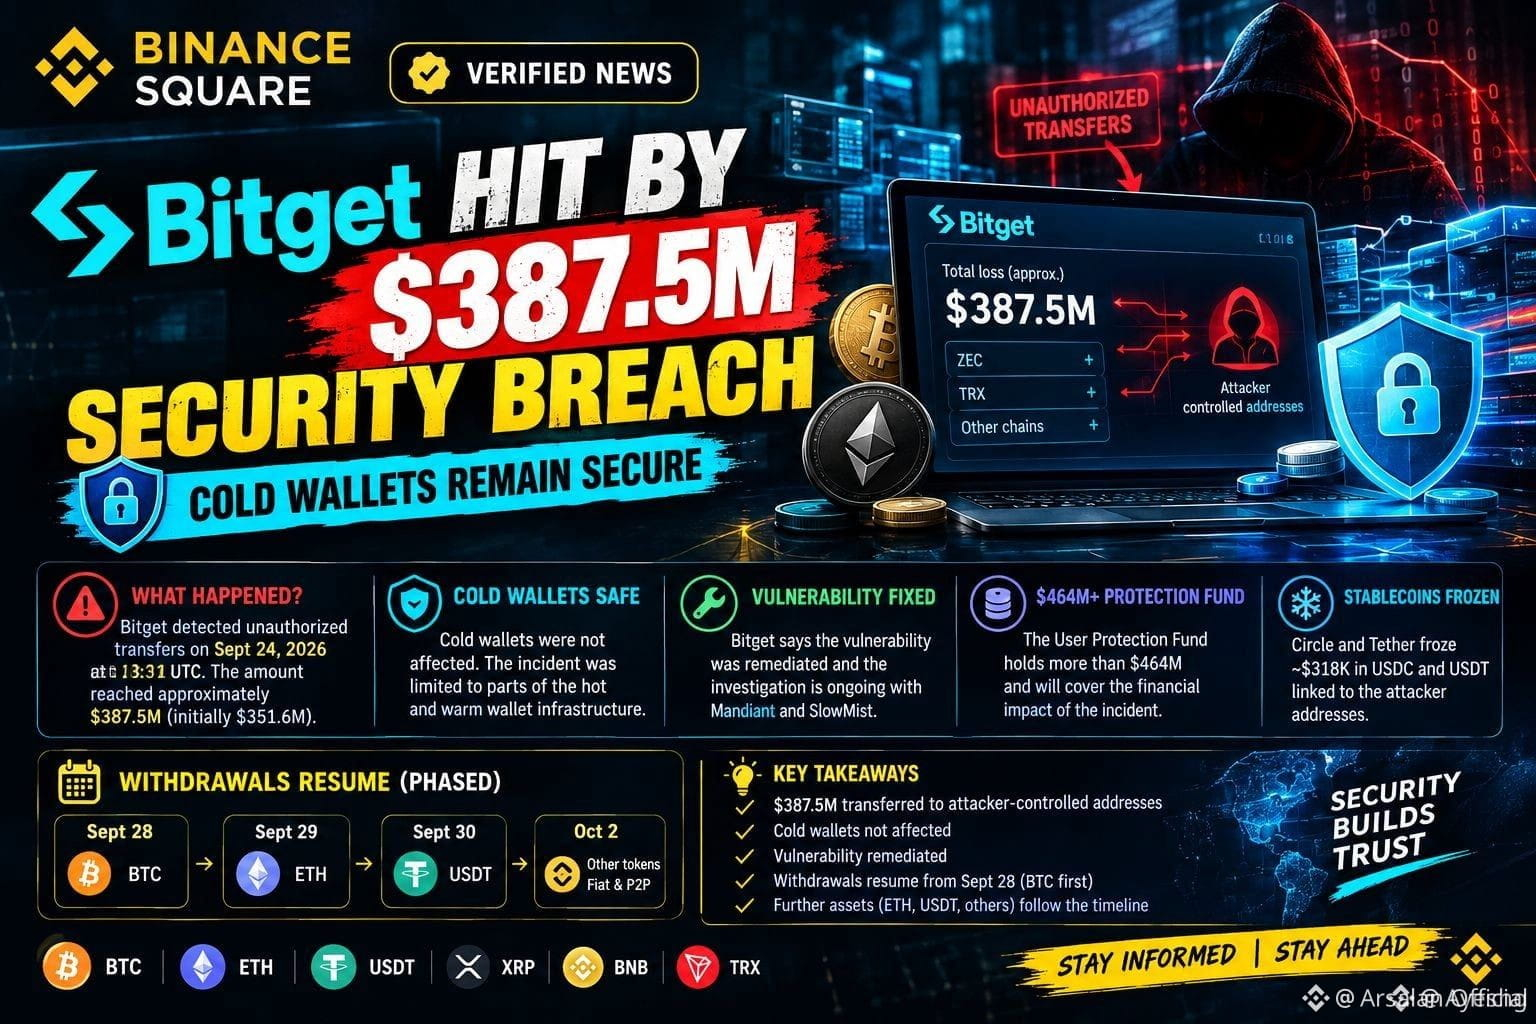
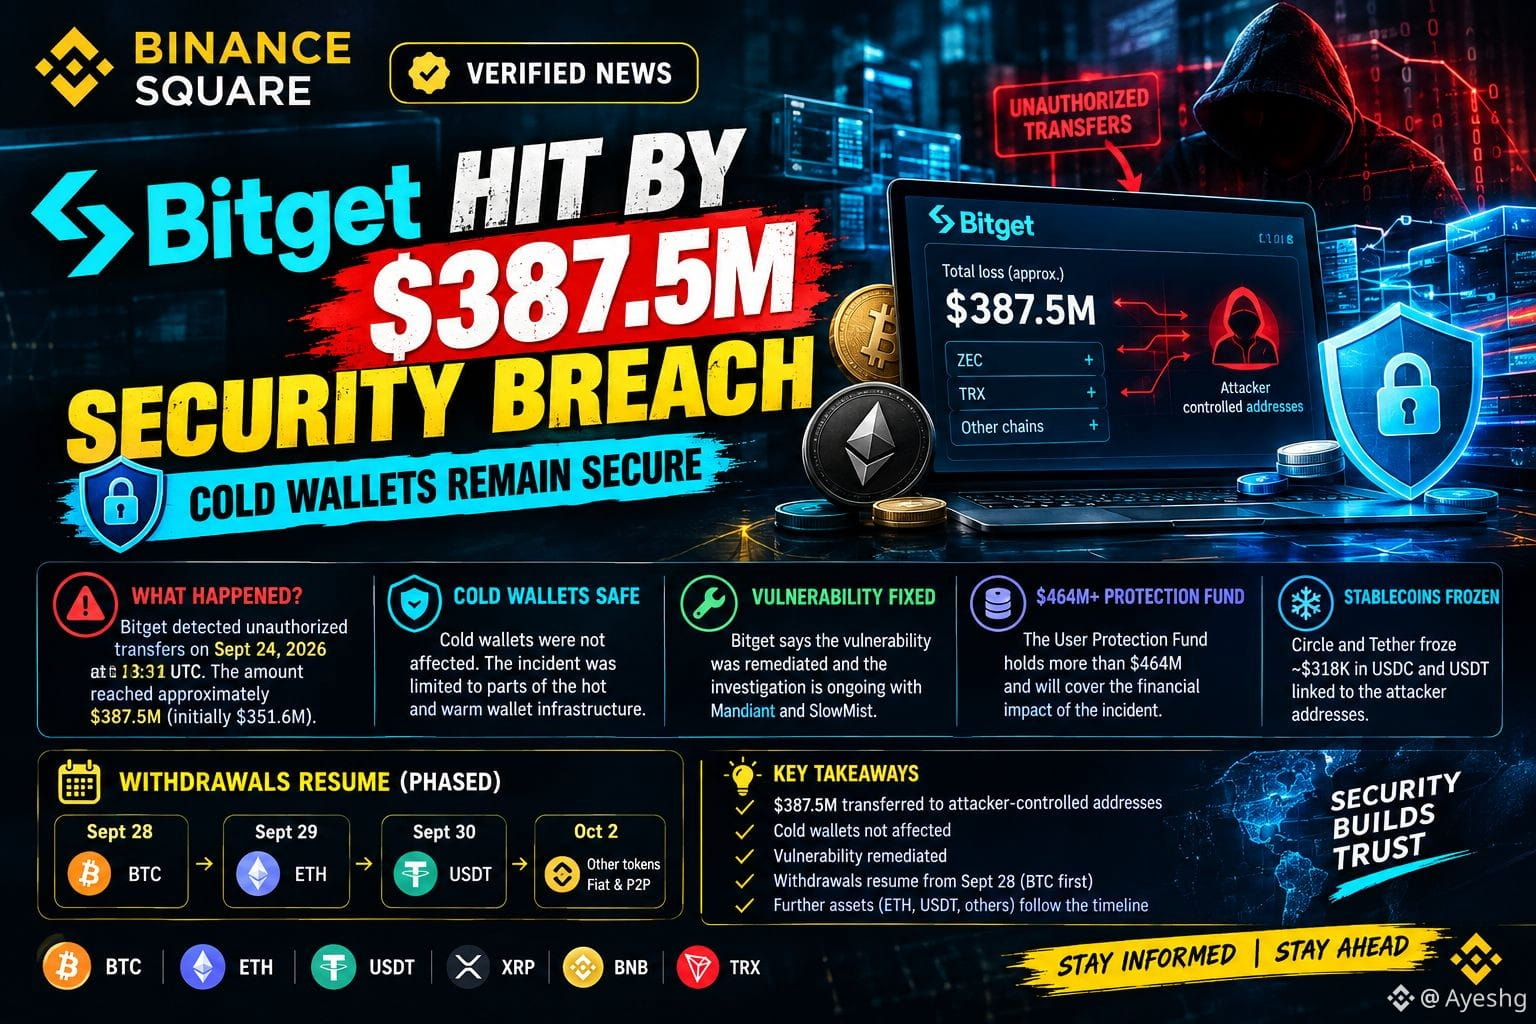
#circletetherfreezebitgethackerwallet 🔴 BITGET'S $387.5M INCIDENT: NO COLD-WALLET COMPROMISE
Crypto exchange Bitget has reported that approximately $387.5 million in assets were affected by unauthorized transfers detected on September 24 at 18:31 UTC.
The initial estimate was $351.6 million, but the figure was later revised after additional on-chain tracing identified assets including ZEC and TRX.
🔐 HOW DID IT HAPPEN?
According to Bitget, the incident was contained to parts of its hot and warm wallet infrastructure.
🛡️ Cold wallets remained secure.
Bitget said the attacker exploited a vulnerability in its backend wallet infrastructure and manipulated transaction data so that unauthorized transfers were processed through the platform's authorization system. The investigation is continuing with Mandiant and SlowMist.
💰 $464M+ PROTECTION FUND
Bitget says its User Protection Fund holds more than $464 million and covers the financial impact of the incident.
The exchange also says customer account balances remain unaffected, while deposits and trading continue.
🧊 STABLECOINS FROZEN
Circle and Tether have reportedly frozen approximately $318,000 in USDC and USDT linked to the attacker addresses.
📅 WITHDRAWALS TO RESUME
Bitget has announced a phased withdrawal schedule:
• September 28: BTC
• September 29: ETH
• September 30: USDT
• October 2: Other tokens, fiat & P2P
⚠️ NORTH KOREA CONNECTION?
Bitget CEO Gracy Chen has said that the attack pattern appears consistent with groups previously associated with North Korea. However, the attacker's identity and attribution remain under investigation, so this should be treated as an allegation rather than a confirmed fact.
📊 MARKET WATCH
The incident highlights the continuing importance of exchange security, wallet architecture and asset protection in the crypto industry.
₿ $BTC | ♦️ $ETH | 💧 $XRP
#Bitget #BitgetHack #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #XRP #BNB #Crypto #Blockchain #BinanceSquare
Specialhyips:
may mà ko có tài sản trên sàn này
1
6
7.9k
Bitget Security Incident Triggers Exchange Audit Focus
Exchange security became a major focus following a reported exploit on Bitget estimated between $351.6M and $387.5M. Bitget clarified that backend infrastructure was compromised while cold wallets and user funds remained safe, backed by their $464M protection fund. Tether and Circle quickly froze hacker-controlled funds, keeping market panic localized.
#StrategyStriveAdd2305BitcoinThisWeek #CircleTetherFreezeBitgetHackerWallet #SECSaysTokenBuybacksNotAutoSecurities
{spot}(BTCUSDT)
{spot}(ETHUSDT)
{spot}(BNBUSDT)
Bitget Security Incident Triggers Exchange Audit Focus
Exchange security became a major focus following a reported exploit on Bitget estimated between $351.6M and $387.5M. Bitget clarified that backend infrastructure was compromised while cold wallets and user funds remained safe, backed by their $464M protection fund. Tether and Circle quickly froze hacker-controlled funds, keeping market panic localized.
#StrategyStriveAdd2305BitcoinThisWeek #CircleTetherFreezeBitgetHackerWallet #SECSaysTokenBuybacksNotAutoSecurities
1
25
🔒 Stablecoins Frozen — But ETH Keeps Moving
Circle and Tether moved against a Bitget-exploiter wallet holding roughly 218K $USDT and 100K $USDC.
The incident highlights an important difference between issuer-controlled stablecoins and native assets like $ETH.
Spot investors should watch on-chain flows before making decisions. 📈
#circletetherfreezebitgethackerwallet
277
·
--
#CircleTetherFreezeBitgetHackerWallet
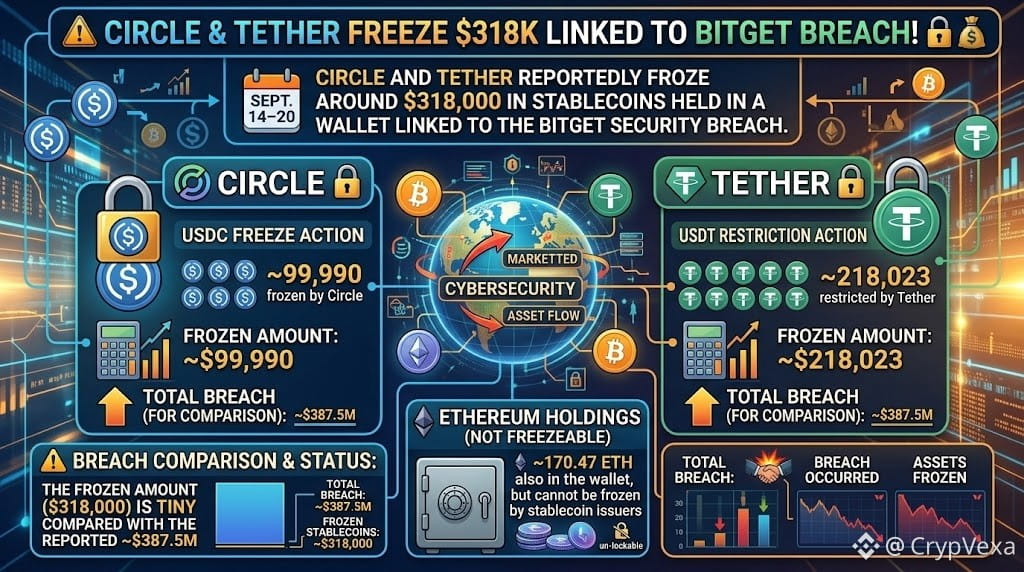
🚨 Circle & Tether Freeze $318K Linked to Bitget Breach! 🔒💰
Circle and Tether reportedly froze around $318,000 in stablecoins held in a wallet linked to the Bitget security breach.
🔵 USDC: ~99,990 frozen by Circle
🟢 USDT: ~218,023 restricted by Tether
⟠ ETH: ~170.47 ETH also in the wallet, but cannot be frozen by stablecoin issuers
📊 The frozen amount is tiny compared with the reported ~$387.5M breach.
⚠️ The key distinction: USDC and USDT issuers can blacklist their tokens, while native assets like ETH and XRP generally cannot be frozen at the token-contract level.
🔐 Bitget reportedly attributed the incident to compromised backend wallet infrastructure and manipulated transaction data, while stating its protection fund covers customer losses.
#Bitget #USDC #USDT #Ethereum
1
8
·
--
တက်ရိပ်ရှိသည်
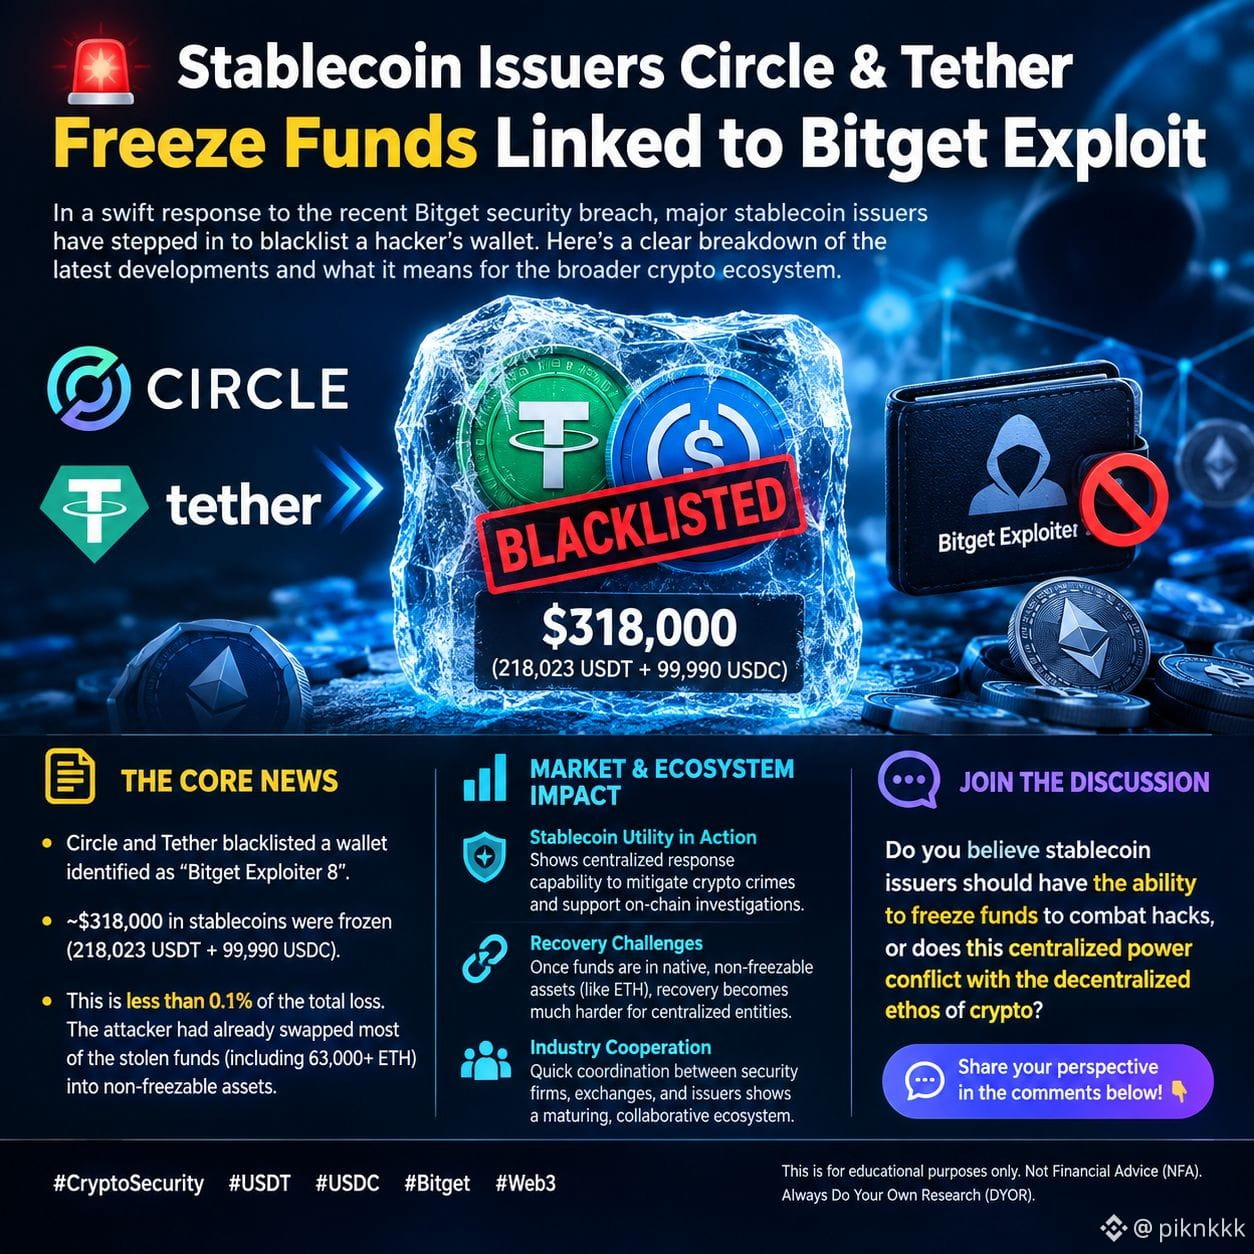
#circletetherfreezebitgethackerwallet 🚨 Stablecoin Issuers Circle & Tether Freeze Funds Linked to Bitget Exploit
In a swift response to the recent Bitget security breach, major stablecoin issuers have stepped in to blacklist a hacker’s wallet. Here is a clear breakdown of the latest developments and what it means for the broader crypto ecosystem.
📌 The Core News
• Circle and Tether have jointly blacklisted a wallet identified by security firms as "Bitget Exploiter 8" [[4]].
• This coordinated action successfully froze approximately $318,000 in stablecoins, consisting of roughly 218,023 USDT and 99,990 USDC [[13]].
• Notably, this frozen amount represents less than 0.1% of the total reported loss. The attacker had already swapped the majority of the stolen funds (including over 63,000 ETH) into decentralized, non-freezable assets before the blacklist was applied [[14]].
📊 Market & Ecosystem Impact
• Stablecoin Utility in Action This event highlights the centralized response capability of fiat-backed stablecoin issuers to actively mitigate crypto-related crimes and assist in on-chain investigations.
• Recovery Challenges It underscores a critical security reality: once funds are converted into native, non-freezable blockchain assets (like ETH), recovery becomes significantly more complex for centralized entities.
• Industry Cooperation The rapid coordination between blockchain security firms, exchanges, and stablecoin issuers demonstrates a maturing, collaborative ecosystem response to large-scale exploits.
💬 Join the Discussion
Do you believe stablecoin issuers should have the ability to freeze funds to combat hacks, or does this centralized power conflict with the decentralized ethos of crypto? Share your perspective in the comments below! 👇
🔖 Hashtags
#CryptoSecurity #USDT #USDC #Bitget #Web3
This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$RAY $SUPER $DASH
{future}(DASHUSDT)
{future}(SUPERUSDT)
{spot}(RAYUSDT)
#circletetherfreezebitgethackerwallet 🚨 Stablecoin Issuers Circle & Tether Freeze Funds Linked to Bitget Exploit
In a swift response to the recent Bitget security breach, major stablecoin issuers have stepped in to blacklist a hacker’s wallet. Here is a clear breakdown of the latest developments and what it means for the broader crypto ecosystem.
📌 The Core News
• Circle and Tether have jointly blacklisted a wallet identified by security firms as "Bitget Exploiter 8" [[4]].
• This coordinated action successfully froze approximately $318,000 in stablecoins, consisting of roughly 218,023 USDT and 99,990 USDC [[13]].
• Notably, this frozen amount represents less than 0.1% of the total reported loss. The attacker had already swapped the majority of the stolen funds (including over 63,000 ETH) into decentralized, non-freezable assets before the blacklist was applied [[14]].
📊 Market & Ecosystem Impact
• Stablecoin Utility in Action This event highlights the centralized response capability of fiat-backed stablecoin issuers to actively mitigate crypto-related crimes and assist in on-chain investigations.
• Recovery Challenges It underscores a critical security reality: once funds are converted into native, non-freezable blockchain assets (like ETH), recovery becomes significantly more complex for centralized entities.
• Industry Cooperation The rapid coordination between blockchain security firms, exchanges, and stablecoin issuers demonstrates a maturing, collaborative ecosystem response to large-scale exploits.
💬 Join the Discussion
Do you believe stablecoin issuers should have the ability to freeze funds to combat hacks, or does this centralized power conflict with the decentralized ethos of crypto? Share your perspective in the comments below! 👇
🔖 Hashtags
#CryptoSecurity #USDT #USDC #Bitget #Web3
This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$RAY $SUPER $DASH
2.1k
·
--
Article
Bitget Hack Explained: How $387.5M Was Stolen Without Private Keys#circletetherfreezebitgethackerwallet
Bitget Hack Explained: How $387.5M Was Stolen Without Private Keys
Bitget is dealing with one of the largest crypto security incidents of 2026 after attackers moved approximately $387.5 million from parts of the exchange’s hot and warm wallet infrastructure.
What makes the incident unusual is that the attackers reportedly did not steal private keys.
Bitget detected unauthorized transfers at 18:31 UTC on September 24, initially estimating the affected assets at about $351.6 million. The figure was later raised to $387.5 million after on-chain investigators identified additional assets involving networks including Zcash and TRON.
The attack reportedly targeted the backend
According to Bitget CEO Gracy Chen, investigators ruled out a direct private-key compromise.
Instead, the attacker reportedly compromised a critical backend system within Bitget's wallet infrastructure and spoofed transaction data. The altered information was then processed by the exchange's normal authorization system, causing transactions to appear legitimate to the signing process.
That distinction is important.
The incident was not simply a case of someone obtaining a private key and draining a wallet. The reported attack targeted the infrastructure that tells the wallet system what transaction it is actually approving.
Bitget said its cold wallets were not affected, while the investigation continued with assistance from cybersecurity firms including Mandiant and SlowMist.
Where did the money go?
On-chain trackers identified large quantities of XRP, ETH, USDT, USDC and other assets among the transferred funds. Bitget's later revision added assets that were not included in its initial estimate.
The attackers also began converting portions of the stolen assets into other cryptocurrencies, making recovery more difficult.
Circle and Tether were able to freeze approximately $318,000 worth of USDC and USDT connected to the attack. However, that amount represents only a small fraction of the total funds involved.
Bitget says its protection fund can cover the loss
Bitget has said its User Protection Fund, valued at more than $464 million, is sufficient to cover the affected customer funds. The exchange has also stated that customer account balances remain accurate.
Withdrawals were temporarily suspended following the incident while Bitget investigated and secured the affected infrastructure.
The exchange has announced a phased restart beginning September 28, with additional assets scheduled to follow through October 2.
North Korea link remains an attribution claim
Bitget CEO Gracy Chen has publicly linked the attack to North Korean-linked actors, citing IP addresses and similarities in laundering patterns.
Blockchain intelligence firm Elliptic has also assessed that the incident was highly likely to be connected to North Korean operators. However, attribution of cyberattacks can evolve as investigators examine additional evidence, so the distinction between reported attribution and independently established identity remains important.
Why this breach matters
The Bitget incident highlights a security problem that goes beyond protecting private keys.
Cold storage can protect assets from direct wallet compromise, but exchanges also depend on backend infrastructure, transaction-generation systems, authorization layers and monitoring tools.
If an attacker can manipulate the information presented to an authorization system, the security model can potentially be challenged without directly stealing the underlying signing keys.
For crypto exchanges, the question after Bitget is therefore not only “Are the private keys secure?”
It is also:
“Can the system accurately verify what those keys are being asked to sign?”
That distinction could become one of the most important security lessons from the Bitget incident.
Bitget Hack Explained: How $387.5M Was Stolen Without Private Keys
#circletetherfreezebitgethackerwallet
Bitget Hack Explained: How $387.5M Was Stolen Without Private Keys
Bitget is dealing with one of the largest crypto security incidents of 2026 after attackers moved approximately $387.5 million from parts of the exchange’s hot and warm wallet infrastructure.
What makes the incident unusual is that the attackers reportedly did not steal private keys.
Bitget detected unauthorized transfers at 18:31 UTC on September 24, initially estimating the affected assets at about $351.6 million. The figure was later raised to $387.5 million after on-chain investigators identified additional assets involving networks including Zcash and TRON.
The attack reportedly targeted the backend
According to Bitget CEO Gracy Chen, investigators ruled out a direct private-key compromise.
Instead, the attacker reportedly compromised a critical backend system within Bitget's wallet infrastructure and spoofed transaction data. The altered information was then processed by the exchange's normal authorization system, causing transactions to appear legitimate to the signing process.
That distinction is important.
The incident was not simply a case of someone obtaining a private key and draining a wallet. The reported attack targeted the infrastructure that tells the wallet system what transaction it is actually approving.
Bitget said its cold wallets were not affected, while the investigation continued with assistance from cybersecurity firms including Mandiant and SlowMist.
Where did the money go?
On-chain trackers identified large quantities of XRP, ETH, USDT, USDC and other assets among the transferred funds. Bitget's later revision added assets that were not included in its initial estimate.
The attackers also began converting portions of the stolen assets into other cryptocurrencies, making recovery more difficult.
Circle and Tether were able to freeze approximately $318,000 worth of USDC and USDT connected to the attack. However, that amount represents only a small fraction of the total funds involved.
Bitget says its protection fund can cover the loss
Bitget has said its User Protection Fund, valued at more than $464 million, is sufficient to cover the affected customer funds. The exchange has also stated that customer account balances remain accurate.
Withdrawals were temporarily suspended following the incident while Bitget investigated and secured the affected infrastructure.
The exchange has announced a phased restart beginning September 28, with additional assets scheduled to follow through October 2.
North Korea link remains an attribution claim
Bitget CEO Gracy Chen has publicly linked the attack to North Korean-linked actors, citing IP addresses and similarities in laundering patterns.
Blockchain intelligence firm Elliptic has also assessed that the incident was highly likely to be connected to North Korean operators. However, attribution of cyberattacks can evolve as investigators examine additional evidence, so the distinction between reported attribution and independently established identity remains important.
Why this breach matters
The Bitget incident highlights a security problem that goes beyond protecting private keys.
Cold storage can protect assets from direct wallet compromise, but exchanges also depend on backend infrastructure, transaction-generation systems, authorization layers and monitoring tools.
If an attacker can manipulate the information presented to an authorization system, the security model can potentially be challenged without directly stealing the underlying signing keys.
For crypto exchanges, the question after Bitget is therefore not only “Are the private keys secure?”
It is also:
“Can the system accurately verify what those keys are being asked to sign?”
That distinction could become one of the most important security lessons from the Bitget incident.
Bitget Hack Explained: How $387.5M Was Stolen Without Private Keys
Bitget is dealing with one of the largest crypto security incidents of 2026 after attackers moved approximately $387.5 million from parts of the exchange’s hot and warm wallet infrastructure.
What makes the incident unusual is that the attackers reportedly did not steal private keys.
Bitget detected unauthorized transfers at 18:31 UTC on September 24, initially estimating the affected assets at about $351.6 million. The figure was later raised to $387.5 million after on-chain investigators identified additional assets involving networks including Zcash and TRON.
The attack reportedly targeted the backend
According to Bitget CEO Gracy Chen, investigators ruled out a direct private-key compromise.
Instead, the attacker reportedly compromised a critical backend system within Bitget's wallet infrastructure and spoofed transaction data. The altered information was then processed by the exchange's normal authorization system, causing transactions to appear legitimate to the signing process.
That distinction is important.
The incident was not simply a case of someone obtaining a private key and draining a wallet. The reported attack targeted the infrastructure that tells the wallet system what transaction it is actually approving.
Bitget said its cold wallets were not affected, while the investigation continued with assistance from cybersecurity firms including Mandiant and SlowMist.
Where did the money go?
On-chain trackers identified large quantities of XRP, ETH, USDT, USDC and other assets among the transferred funds. Bitget's later revision added assets that were not included in its initial estimate.
The attackers also began converting portions of the stolen assets into other cryptocurrencies, making recovery more difficult.
Circle and Tether were able to freeze approximately $318,000 worth of USDC and USDT connected to the attack. However, that amount represents only a small fraction of the total funds involved.
Bitget says its protection fund can cover the loss
Bitget has said its User Protection Fund, valued at more than $464 million, is sufficient to cover the affected customer funds. The exchange has also stated that customer account balances remain accurate.
Withdrawals were temporarily suspended following the incident while Bitget investigated and secured the affected infrastructure.
The exchange has announced a phased restart beginning September 28, with additional assets scheduled to follow through October 2.
North Korea link remains an attribution claim
Bitget CEO Gracy Chen has publicly linked the attack to North Korean-linked actors, citing IP addresses and similarities in laundering patterns.
Blockchain intelligence firm Elliptic has also assessed that the incident was highly likely to be connected to North Korean operators. However, attribution of cyberattacks can evolve as investigators examine additional evidence, so the distinction between reported attribution and independently established identity remains important.
Why this breach matters
The Bitget incident highlights a security problem that goes beyond protecting private keys.
Cold storage can protect assets from direct wallet compromise, but exchanges also depend on backend infrastructure, transaction-generation systems, authorization layers and monitoring tools.
If an attacker can manipulate the information presented to an authorization system, the security model can potentially be challenged without directly stealing the underlying signing keys.
For crypto exchanges, the question after Bitget is therefore not only “Are the private keys secure?”
It is also:
“Can the system accurately verify what those keys are being asked to sign?”
That distinction could become one of the most important security lessons from the Bitget incident.
1
179

·
--
ကျရိပ်ရှိသည်
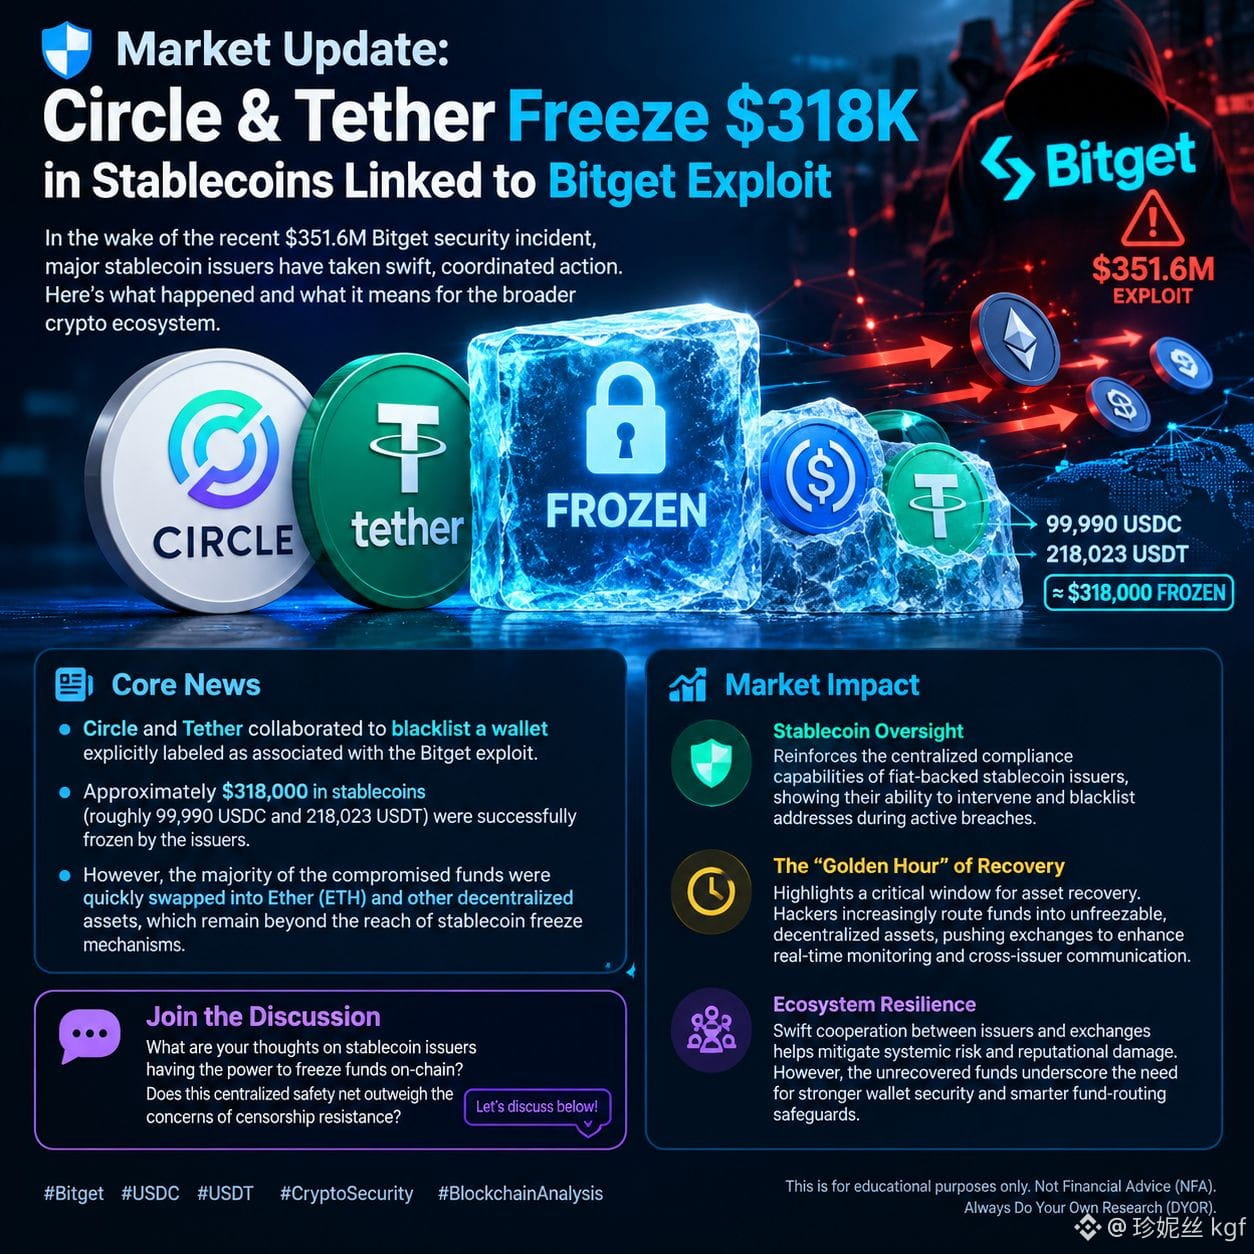
#circletetherfreezebitgethackerwallet 🛡️ Market Update: Circle & Tether Freeze $318K in Stablecoins Linked to Bitget Exploit
In the wake of the recent $351.6M Bitget security incident, major stablecoin issuers have taken swift, coordinated action. Here is a clear breakdown of what happened and what it means for the broader crypto ecosystem.
📰Core News
• Circle and Tether collaborated to blacklist a wallet explicitly labeled as associated with the Bitget exploit [[20]].
• Approximately $318,000 in stablecoins (roughly 99,990 USDC and 218,023 USDT) were successfully frozen by the issuers [[17]].
• However, the majority of the compromised funds were quickly swapped into Ether (ETH) and other decentralized assets, which remain beyond the reach of stablecoin freeze mechanisms [[11]].
📊 Market Impact
• Stablecoin Oversight This event reinforces the centralized compliance capabilities of fiat-backed stablecoin issuers, demonstrating their ability to intervene and blacklist addresses during active security breaches.
•The "Golden Hour" of Recovery It highlights a critical window for asset recovery. Hackers increasingly route stolen funds into unfreezable, decentralized assets to bypass blacklists, pushing exchanges to enhance real-time transaction monitoring and cross-issuer communication.
• Ecosystem Resilience Swift cooperation between major issuers and exchanges helps mitigate systemic risk and reputational damage. However the unrecovered portion of the funds underscores the ongoing industry-wide need for robust wallet security and smarter fund-routing safeguards.
💬 Join the Discussion
What are your thoughts on stablecoin issuers having the power to freeze funds on-chain? Does this centralized safety net outweigh the concerns of censorship resistance? Let’s discuss below! 👇
#Bitget #USDC #USDT #CryptoSecurity #BlockchainAnalysis
This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$ACE $2Z $PHA
{future}(PHAUSDT)
{future}(2ZUSDT)
{future}(ACEUSDT)
#circletetherfreezebitgethackerwallet 🛡️ Market Update: Circle & Tether Freeze $318K in Stablecoins Linked to Bitget Exploit
In the wake of the recent $351.6M Bitget security incident, major stablecoin issuers have taken swift, coordinated action. Here is a clear breakdown of what happened and what it means for the broader crypto ecosystem.
📰Core News
• Circle and Tether collaborated to blacklist a wallet explicitly labeled as associated with the Bitget exploit [[20]].
• Approximately $318,000 in stablecoins (roughly 99,990 USDC and 218,023 USDT) were successfully frozen by the issuers [[17]].
• However, the majority of the compromised funds were quickly swapped into Ether (ETH) and other decentralized assets, which remain beyond the reach of stablecoin freeze mechanisms [[11]].
📊 Market Impact
• Stablecoin Oversight This event reinforces the centralized compliance capabilities of fiat-backed stablecoin issuers, demonstrating their ability to intervene and blacklist addresses during active security breaches.
•The "Golden Hour" of Recovery It highlights a critical window for asset recovery. Hackers increasingly route stolen funds into unfreezable, decentralized assets to bypass blacklists, pushing exchanges to enhance real-time transaction monitoring and cross-issuer communication.
• Ecosystem Resilience Swift cooperation between major issuers and exchanges helps mitigate systemic risk and reputational damage. However the unrecovered portion of the funds underscores the ongoing industry-wide need for robust wallet security and smarter fund-routing safeguards.
💬 Join the Discussion
What are your thoughts on stablecoin issuers having the power to freeze funds on-chain? Does this centralized safety net outweigh the concerns of censorship resistance? Let’s discuss below! 👇
#Bitget #USDC #USDT #CryptoSecurity #BlockchainAnalysis
This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$ACE $2Z $PHA
206 Atlas:
Freezing $318K while hackers swap the bulk into ETH proves stablecoin blacklists are mostly theater for PR, not actual recovery.
2
2
2.1k
·
--
#CircleTetherFreezeBitgetHackerWallet
🚨 THE HACKER GOT FROZEN. 🧊
Circle & Tether have blacklisted a wallet linked to the Bitget hack, freezing roughly $318K in $USDC + $USDT . 💰
But here’s the twist 👀
💵 Stablecoins → Frozen
⟠ $ETH → Cannot be frozen by issuers
The majority of stolen funds had already moved into assets outside stablecoin issuers’ control.
Crypto security just got a serious reality check. ⚠️
What do you think —
🔒 Protection or centralization?
#CircleTetherFreezeBitgetHackerWallet #USDC #USDT #Bitget #CryptoSecurity #Crypto #BinanceSquare
1
71
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
အီးမေးလ် / ဖုန်းနံပါတ်
ရေပန်းစားနေသော ခေါင်းစဉ်များ
1
#ChinaMayLetAlibabaByteDanceBuyNvidiaChips
419 views
53 Discussing
2
#USChinaRelease$30BTariffCutProductLists
5 views
3 Discussing
3
#SKoreaFSCConsidersVirtualAssetMarketMaker
1,251 views
82 Discussing
4
#ChinaIndustrialProfitGrowthSlowsFourthMonth
2,416 views
108 Discussing
5
#BitwiseFilesFinalNEARSpotETFProspectus
106,338 views
1,612 Discussing
6
#BitgetHackerMoves$83MStolenXRP
37,180 views
173 Discussing
7
#SOLSpotETFWeeklyInflow$188M
23,877 views
138 Discussing
8
#DogecoinETFsPostBiggestWeekSinceLaunch
63,943 views
1,072 Discussing
9
#StrategyStriveAdd2305BitcoinThisWeek
159,177 views
2,318 Discussing
10
#TrumpRejectsIranHormuzReopening
137,088 views
1,746 Discussing