🚨 $BTC CLIPBOARD INTERCEPTION VULNERABILITY EXPOSED ACROSS MAJOR ENTERPRISE PLATFORMS! ⚡
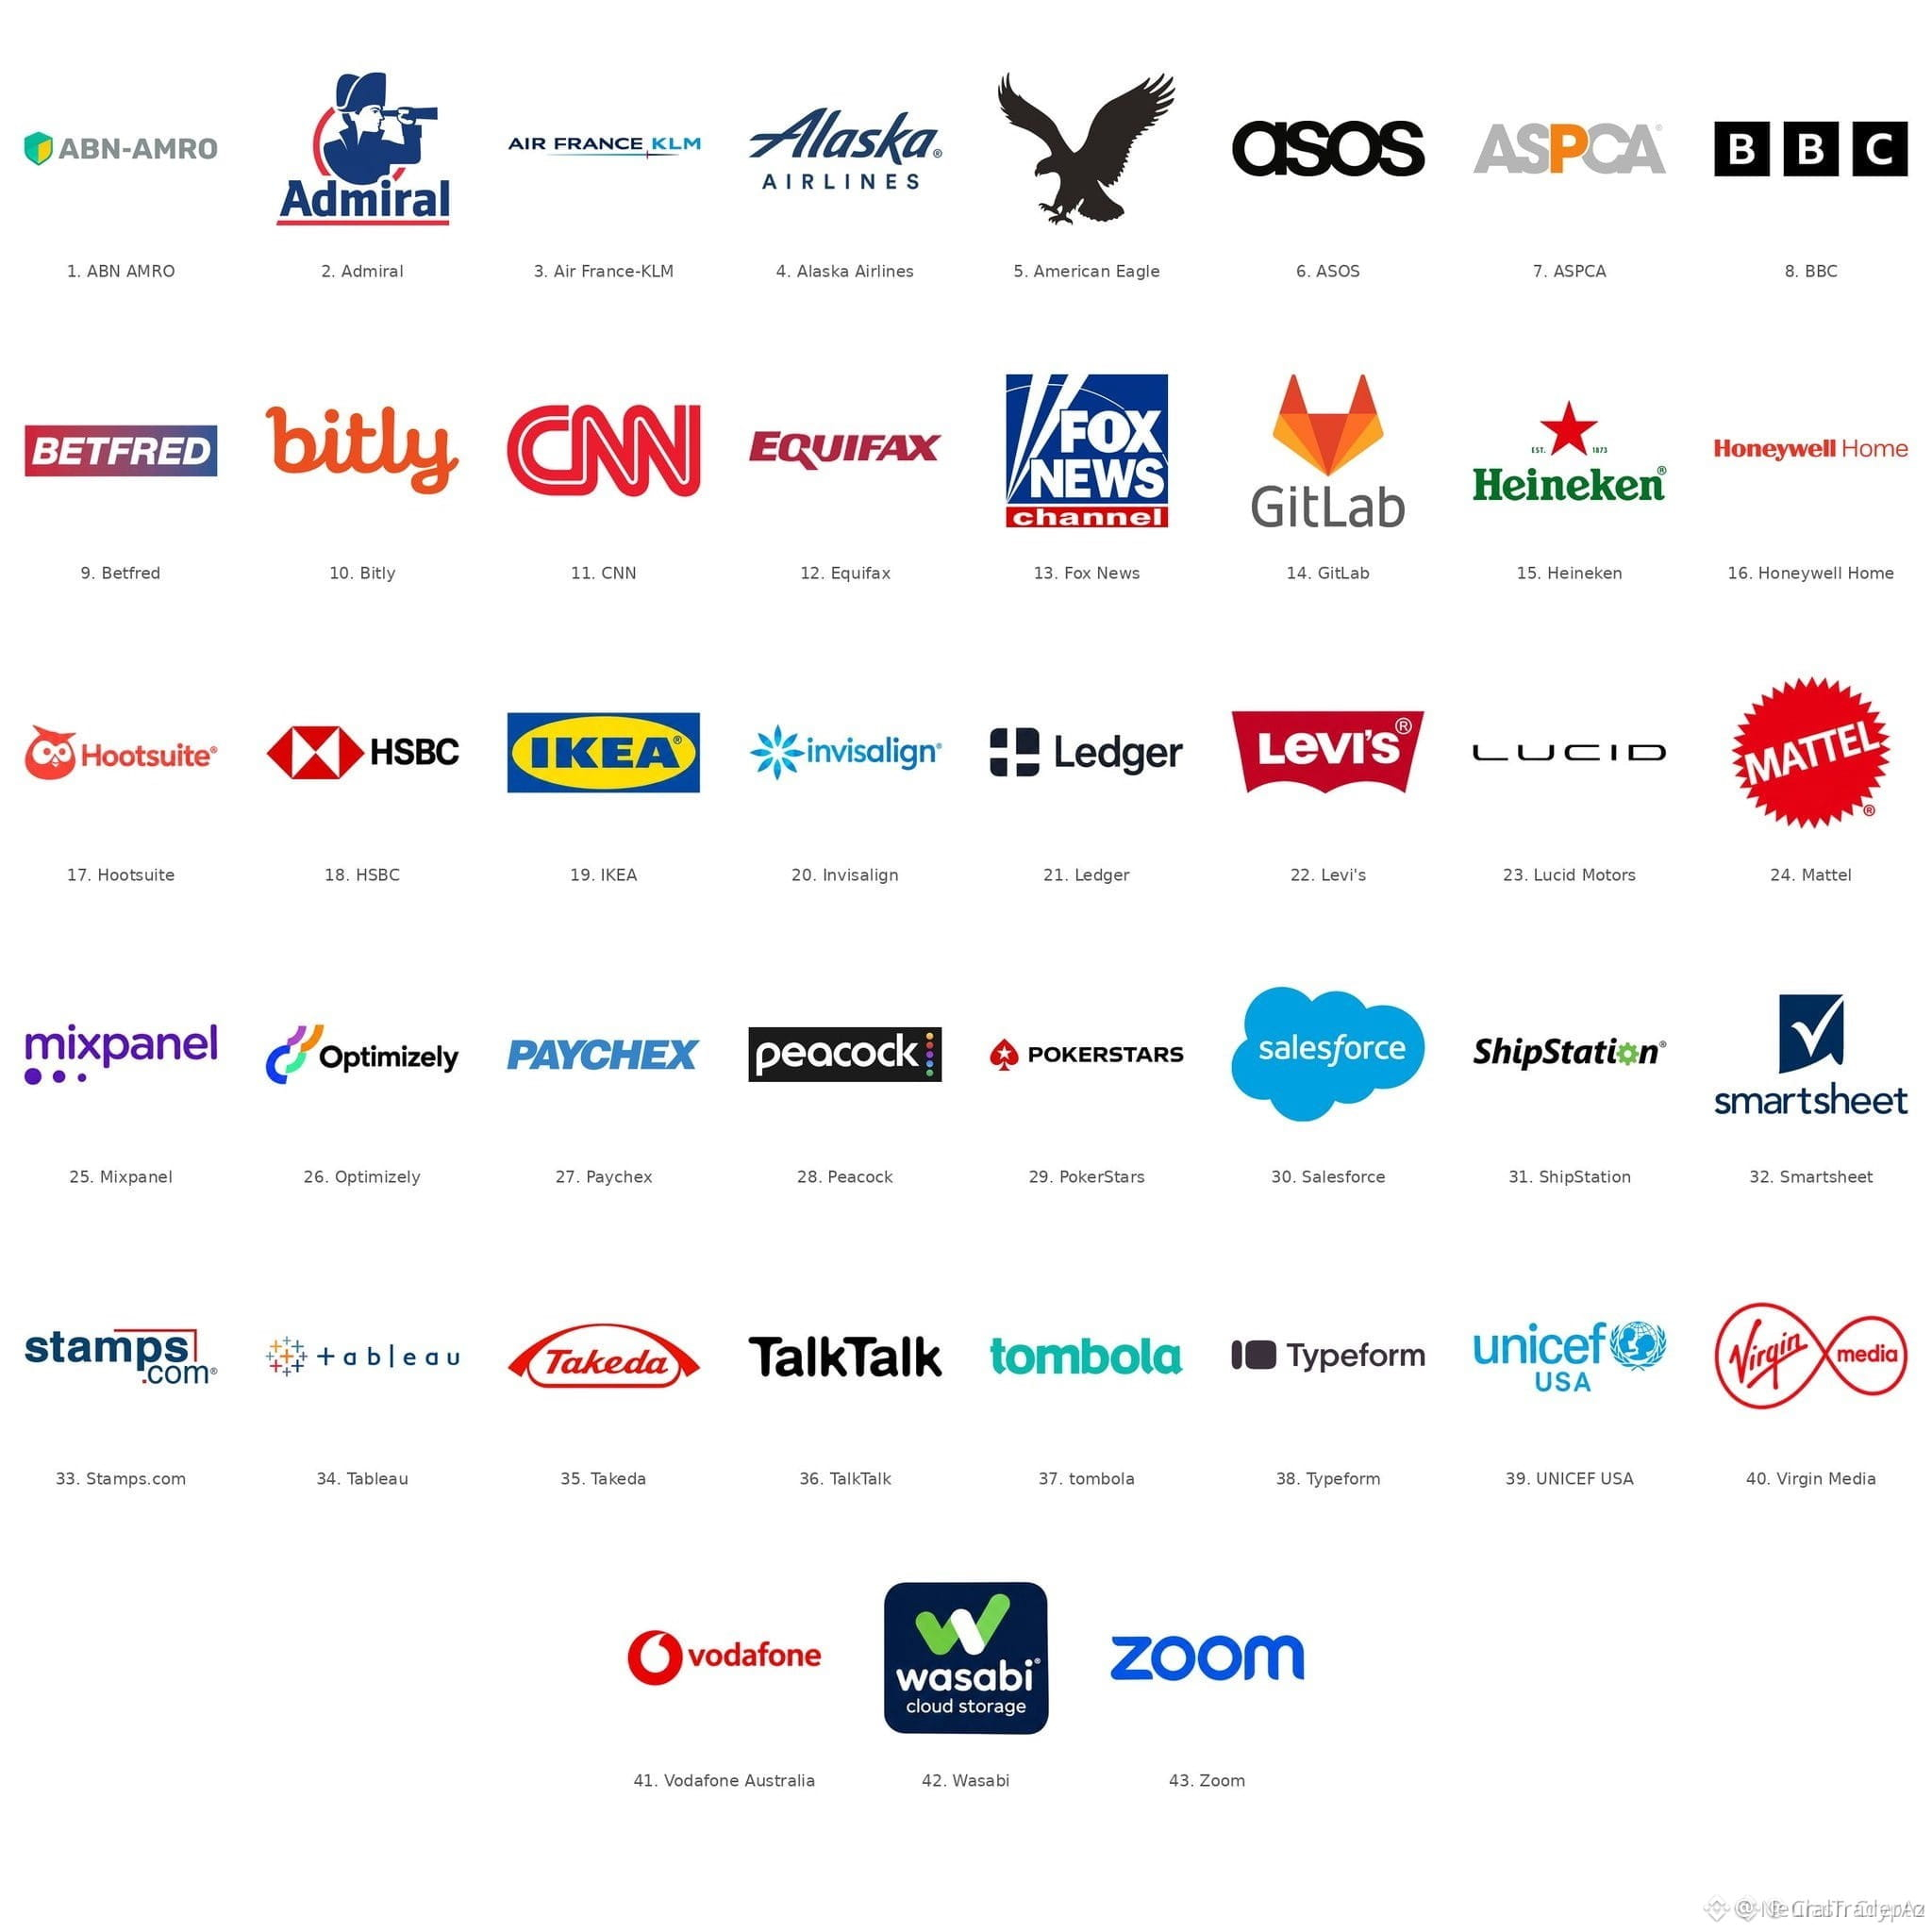
A critical third-party script injection via Optimizely recently compromised 178 enterprise websites, including institutional heavyweights and hardware security providers. 🔍 The malicious payload silently targeted clipboard functions, swapping destination addresses to redirect asset transfers during manual copy-paste operations. ⚡
Even isolated web infrastructure remains vulnerable when integrated testing suites are exploited at the source. 🛡️ Always verify destination hashes character by character before signing any transaction. 💬 Do you rely on manual copy-pasting or hardware-confirmed address whitelisting for your transfers? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #RiskManagement #SmartMoney
🔥 💎
A critical third-party script injection via Optimizely recently compromised 178 enterprise websites, including institutional heavyweights and hardware security providers. 🔍 The malicious payload silently targeted clipboard functions, swapping destination addresses to redirect asset transfers during manual copy-paste operations. ⚡
Even isolated web infrastructure remains vulnerable when integrated testing suites are exploited at the source. 🛡️ Always verify destination hashes character by character before signing any transaction. 💬 Do you rely on manual copy-pasting or hardware-confirmed address whitelisting for your transfers? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #RiskManagement #SmartMoney
🔥 💎