#NEARFallsToAround$4.70Down14%
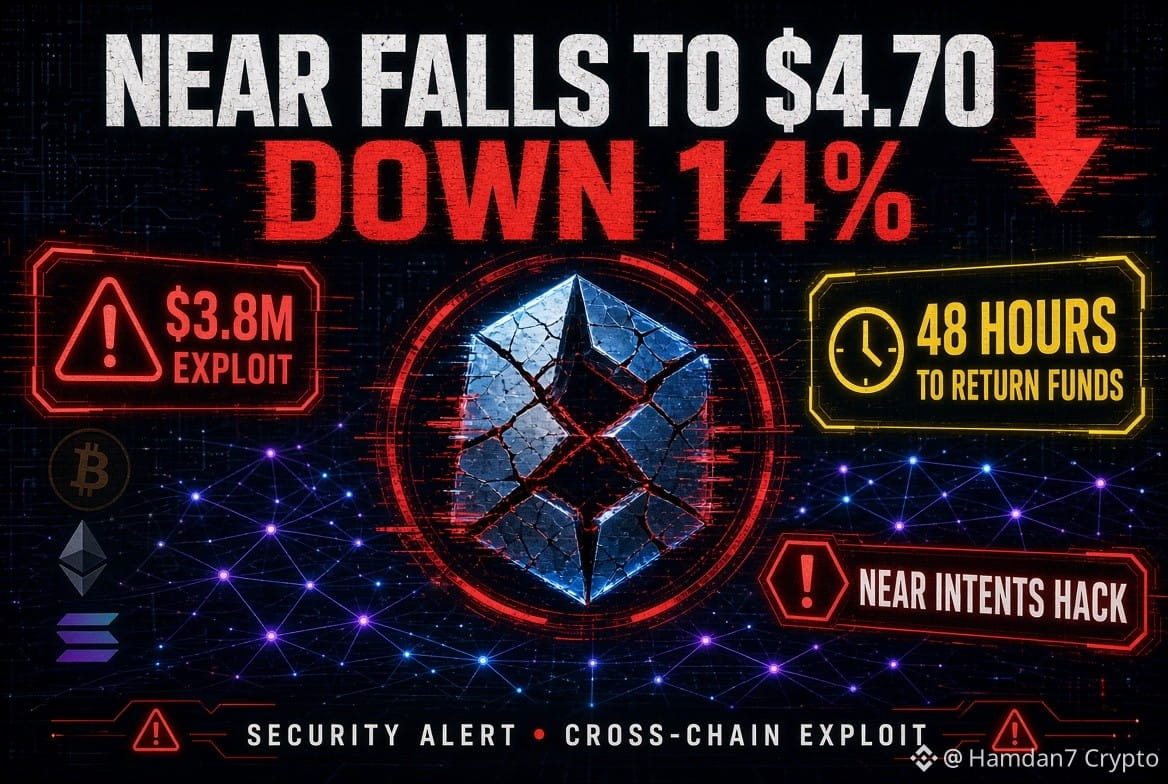
🚨$3.8M NEAR INTENTS EXPLOIT — 48 HOURS TO RETURN THE FUNDS
A major security incident has put $NEAR under pressure.
NEAR Intents suffered an exploit involving a bug in the interaction between its Omni deposit/withdrawal infrastructure and a NEAR Intents smart contract. The preliminary loss was reported at around $3.8 million.
Now comes the biggest development:
🚨 NEAR Intents GM Alex Shevchenko says the team has identified the person behind the exploit.
The suspected attacker has been given 48 hours to return the funds through a responsible-disclosure process.
“This is the last window to use it.”
The team has also published return addresses across Bitcoin, BNB/Ethereum and Solana. As of the latest reports, there was no confirmation that the stolen funds had been returned.
⚠️ WHY $NEAR IS UNDER PRESSURE
The exploit adds fresh security concerns around cross-chain infrastructure.
NEAR Intents has said the contract vulnerability was patched and that affected users would be fully compensated. The team also said it was working with security and blockchain-analysis partners to trace the funds.
Blockchain tracking has reportedly followed the majority of the stolen funds, with a significant portion moved into Bitcoin.
👀 NOW WATCH THESE 3 THINGS
1️⃣ Will the $3.8M be returned within 48 hours?
2️⃣ How much of the stolen crypto can actually be recovered?
3️⃣ Can $NEAR stabilize after the sharp sell-off?
This is no longer just a price story.
It is a security + recovery + confidence story for the NEAR ecosystem.
🔥 The next 48 hours could be critical for the recovery effort and market sentiment around $NEAR.
What do you think?
Will the attacker return the funds — or move them further? 👇
#NEAR #NEARProtocol #NEARIntents #CryptoHack #CryptoSecurity #DeFi #Altcoins #CryptoNews #Blockchain #Web3 #BTC #ETH #SOL #Trading #CryptoMarket