#bitgethotwalletbreachtiedtothirdpartysecurityflaw 🚨 Bitget Security Update: $388M Hot Wallet Breach Linked to Third-Party Flaw
A major crypto exchange confirmed a security incident, but with a crucial detail: user cold storage remains unaffected. Here is the factual breakdown.
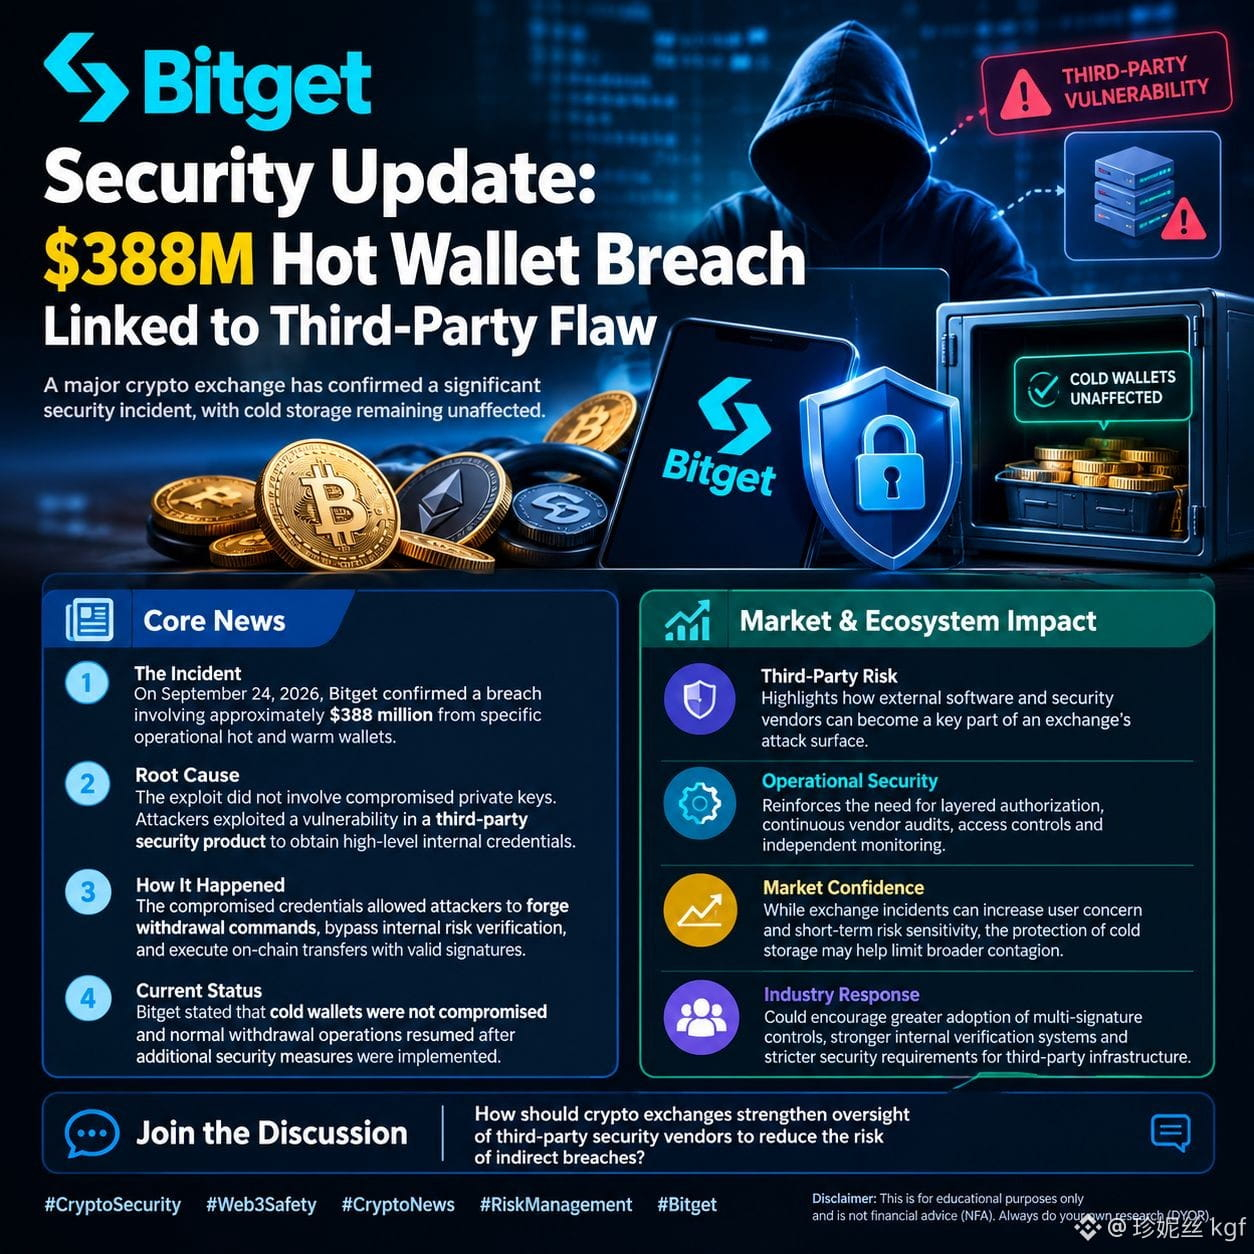
🔹 Incident On Sept 24, 2026, Bitget confirmed a breach of ~$388M from specific operational hot/warm wallets.
🔹 Root Cause**: The exploit did NOT involve compromised private keys. Attackers leveraged a vulnerability in a third-party security product to steal high-level internal credentials.
🔹 Mechanism These credentials allowed forged withdrawal commands, bypassing risk verification to execute on-chain transfers with valid signatures.
🔹 Status Bitget confirms cold wallets are safe. Normal operations have resumed following enhanced security protocols.
📊 Market Impact
• Vendor Risk Highlights a critical systemic risk in crypto: third-party software dependencies. Underscores the need for rigorous vendor audits industry-wide.
• Market Resilience Confirming cold storage is intact helps contain broader market contagion, despite potential short-term outflows.
• Industry Evolution Expect a renewed push for multi-signature operational frameworks and stricter compliance for centralized platforms.
💬 Join the Discussion
How should the crypto industry better audit third-party security vendors to prevent indirect breaches? Share your thoughts below! 👇
#CryptoSecurity #Web3Safety #CryptoNews #RiskManagement #Bitget
This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$MARSCOIN $HBAR $ZAMA