

#trezor
trezor
34,797 views
160 ກຳລັງສົນທະນາ
ມາແຮງ
ຫຼ້າສຸດ

·
--
🚨 $TREZOR ALERT: PHISHING EMAILS USING OFFICIAL DOMAIN TARGET USERS 🛑
🦈 A third‑party email service breach let attackers spoof $TREZOR ’s official domain, delivering a fake “Critical Security Alert: STM32 Entropy Vulnerability” that looks indistinguishable from a genuine notice. 📊 The deception bypasses simple address checks, forcing users to rely on visual cues that the phishing crew has meticulously replicated.
🔍 With roughly 87 k records already exposed from the prior ShipMonk breach, attackers now have a rich data pool to craft highly targeted lures. 📌 $TREZOR advises you to ignore links, manually type the official website, and cross‑verify any alert inside the wallet app before acting.
💬 Are you double‑checking every security alert before clicking?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #TREZOR #PhishingAlert #SecurityRisk #CryptoSafety
🔥 🦈
34

·
--
⚠️ $TREZOR PHISHING SCAM ALERT: HACKERS USING LEGIT EMAIL DOMAIN 🚨
📧 Trezor’s email provider was compromised, and attackers are firing off “Critical Security Alert” phishing blasts that mimic the brand’s exact domain. The bait mentions an “STM32 Entropy Vulnerability” to lure recovery phrases—pure social‑engineered bait. 📊 Users who click the link hand over the master key, instantly handing the vault to the wolves. 🛡️ Verify every Trezor communication on the official site and ignore any unsolicited security notices. 🔍
💬 How are you tightening your inbox defenses today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #TREZOR #Security #Phishing #Crypto #Alert
🔥 🦈
17


Imagine getting an email from an official, verified address that looks 100 percent real, only to find out it is a trap designed to steal your entire crypto stash. This is not a hypothetical scenario, but the latest security nightmare affecting hardware wallet users.
How can we sleep soundly at night knowing our offline keys are safe, but our email addresses are being weaponized against us?
Here is what we know so far:
🚨 Trezor has confirmed that a third-party security breach at shipping provider ShipMonk is the root cause.
🚨 This breach allowed malicious actors to send phishing emails directly from a legitimate Trezor domain.
🚨 The compromised data includes personal information of customers who ordered devices.
Never, ever enter your seed phrase on any website, even if the email comes from the exact official domain. Seriously, guys, stay paranoid and keep your $BTC and $ETH safe. These hackers are getting way too smart.
#Trezor #Security #Phishing #Write2Earn

43

Lỗ hổng đăng nhập Brevo kích hoạt email lừa đảo mục tiêu 347K người dùng Trezor
- Trezor đã thông báo với Cointelegraph về một email lừa đảo (phishing) được gửi tới 347.000 người đăng ký.
- Lỗ hổng đăng nhập trên nền tảng Brevo đã bị khai thác để thực hiện chiến dịch lừa đảo này.
- Trezor coi tất cả các địa chỉ email là "đã được biết đến bởi attacker và có thể được sử dụng lại cho các cuộc lừa đảo khác".
- Người dùng cần cảnh giác cao, không tương tác với các email không rõ nguồn gốc.
#BinanceSquare #CryptoNews #BTC #Trezor #Phishing
$btc
vlikevn Titanbot
Nguồn: CoinTelegraph
8
Lỗ hổng đăng nhập Brevo cho phép email lừa đảo nhắm tới 347k người dùng Trezor
- Trezor xác nhận email lừa đảo được gửi tới 347.000 người dùng qua dịch vụ Brevo.
- Trezor coi mọi địa chỉ email là đã biết của kẻ tấn công và có thể tái sử dụng cho phishing.
#BinanceSquare #CryptoNews #Trezor #Brevo #Phishing
$btc $eth
vlikevn Titanbot
Nguồn: CoinTelegraph
- Trezor xác nhận email lừa đảo được gửi tới 347.000 người dùng qua dịch vụ Brevo.
- Trezor coi mọi địa chỉ email là đã biết của kẻ tấn công và có thể tái sử dụng cho phishing.
#BinanceSquare #CryptoNews #Trezor #Brevo #Phishing
$btc $eth
vlikevn Titanbot
Nguồn: CoinTelegraph
110

TREZOR USERS JUST GOT A PHISHING BOSS FIGHT. 💀
Trezor cho biết dịch vụ email bên thứ ba đã bị xâm phạm và cuộc điều tra vẫn đang diễn ra.
Người dùng đang được cảnh báo về email giả mạo với tiêu đề “Urgent Security Alert”.
🚨 Đừng click link. Đừng nhập seed phrase. Đừng kết nối ví từ email.
Ví lạnh chưa chắc bị hack, nhưng email của bạn thì có thể trở thành cửa sau.
Your seed phrase stays offline. Your paranoia should too. 💀
#Trezor #CryptoSecurity #bitcoin
$BTC
{future}(BTCUSDT)
TREZOR USERS JUST GOT A PHISHING BOSS FIGHT. 💀
Trezor cho biết dịch vụ email bên thứ ba đã bị xâm phạm và cuộc điều tra vẫn đang diễn ra.
Người dùng đang được cảnh báo về email giả mạo với tiêu đề “Urgent Security Alert”.
🚨 Đừng click link. Đừng nhập seed phrase. Đừng kết nối ví từ email.
Ví lạnh chưa chắc bị hack, nhưng email của bạn thì có thể trở thành cửa sau.
Your seed phrase stays offline. Your paranoia should too. 💀
#Trezor #CryptoSecurity #bitcoin
$BTC
145
·
--
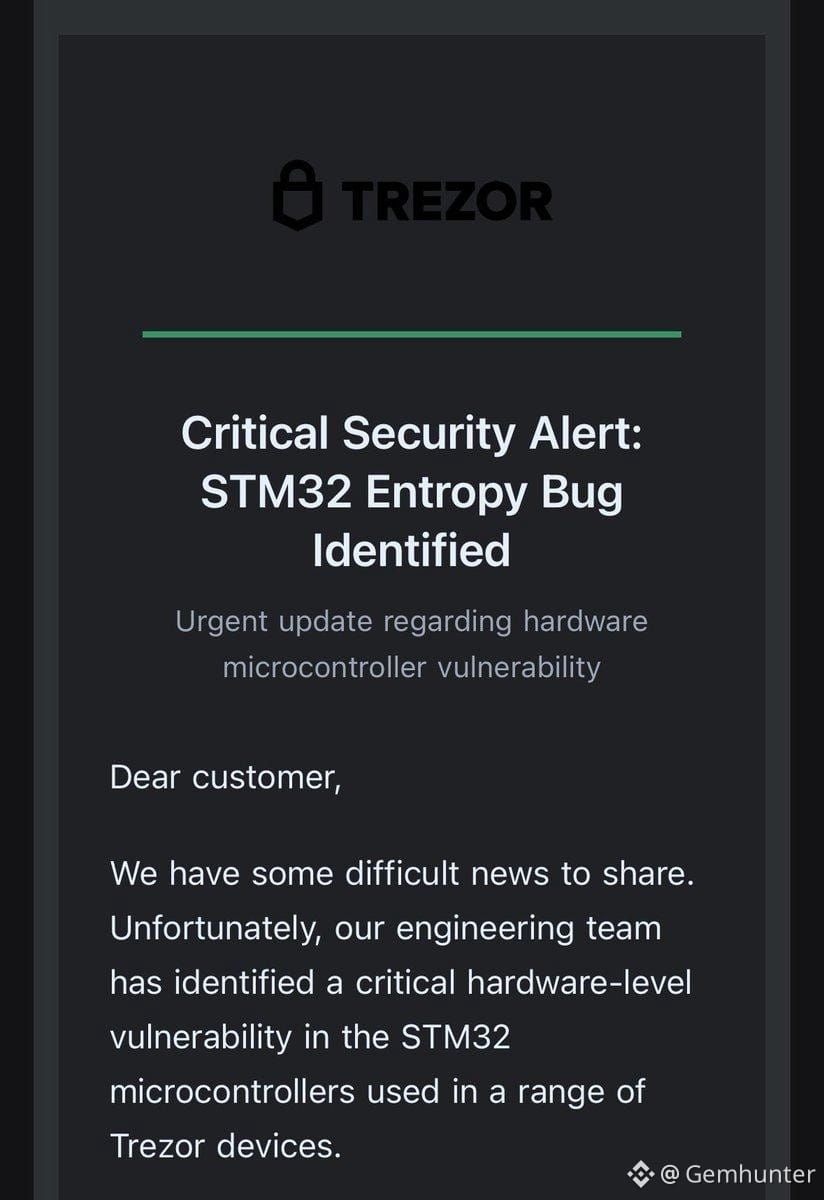
🚨 Trezor users, stay alert.
Trezor says its third-party email provider was breached and it is still investigating the incident. Attackers are reportedly using the breach to send fake “Critical Security Alert” phishing emails.
⚠️ Do NOT click links in suspicious Trezor emails or enter your wallet credentials. Always verify through official Trezor channels before taking action.
#Trezor #CryptoSecurity #Bitcoin $BTC
1
9

Scammers are spoofing hardware wallet security alerts
Trezor and BitBox warned users about phishing attempts targeting hardware wallet security. Scammers are using email service breaches and shared newsletter providers to send fake security alerts to unsuspecting holders.
#Trezor #PhishingAlerts
Scammers are spoofing hardware wallet security alerts
Trezor and BitBox warned users about phishing attempts targeting hardware wallet security. Scammers are using email service breaches and shared newsletter providers to send fake security alerts to unsuspecting holders.
#Trezor #PhishingAlerts
Trezor and BitBox warned users about phishing attempts targeting hardware wallet security. Scammers are using email service breaches and shared newsletter providers to send fake security alerts to unsuspecting holders.
#Trezor #PhishingAlerts
53

硬件钱包Trezor遭遇第三方邮件服务商安全漏洞,用户需警惕钓鱼攻击
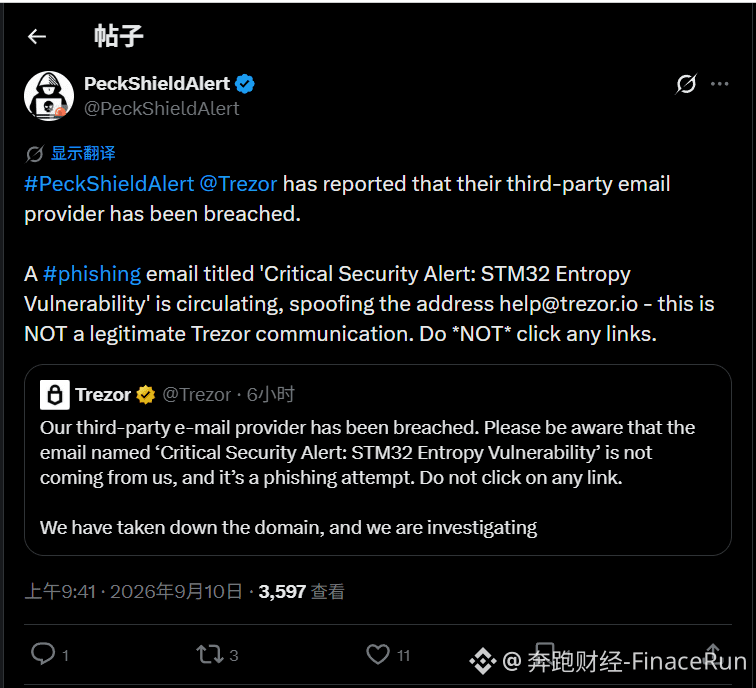
9 月 10 日,据 PeckShieldAlert 最新帖文,硬件钱包厂商 Trezor 今日发布安全警告,称其第三方电子邮件服务商遭遇安全漏洞,导致用户面临钓鱼攻击风险。
区块链安全机构PeckShield监测发现,一封标题为"Critical Security Alert: STM32 Entropy Vulnerability"的钓鱼邮件正在传播,该邮件冒用help@trezor.io发件地址,并非Trezor官方的合法通信。
据其引用的社交媒体上发布紧急声明显示,Trezor官方明确指出这封邮件是钓鱼尝试,提醒用户切勿点击其中的任何链接。
公司方面还表示,我们已经迅速采取行动,已下架了相关域名,并正在对此次安全事件进行深入调查。目前尚不清楚此次漏洞影响了多少用户,以及是否有用户因此遭受损失。
安全专家建议,Trezor用户需保持高度警惕,对于声称来自硬件钱包厂商的相关邮件,务必通过官方渠道进行核实,避免直接点击邮件中的链接或下载附件,以防范资产被盗风险。
#Trezor #钱包钓鱼攻击
1
353

·
--
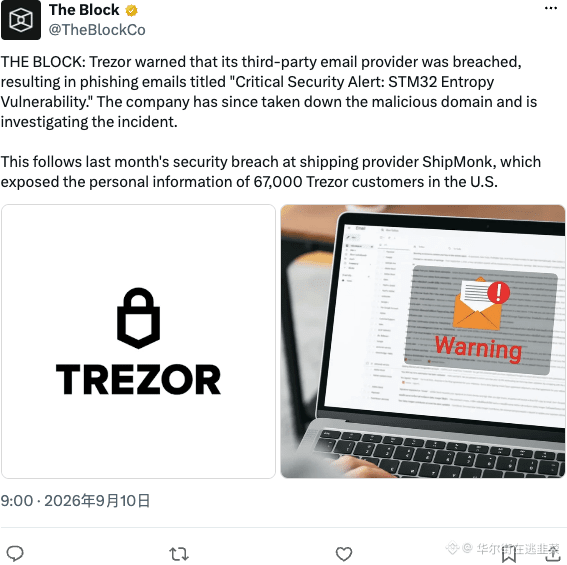
Trezor这波属实是“硬件再硬,邮箱被偷家”😅 第三方邮件商被黑,钓鱼邮件伪装成STM32熵漏洞安全警报,官方已经下架恶意域名、正在查。
老剧本了——钱包厂商最爱吹私钥自持,结果外围服务一崩照样社死。吃瓜归吃瓜,提醒一句:邮件里带“安全警报”让你点链接输助记词的,100%钓鱼,别手贱。
$BTC #Trezor #安全
Trezor这波属实是“硬件再硬,邮箱被偷家”😅 第三方邮件商被黑,钓鱼邮件伪装成STM32熵漏洞安全警报,官方已经下架恶意域名、正在查。
老剧本了——钱包厂商最爱吹私钥自持,结果外围服务一崩照样社死。吃瓜归吃瓜,提醒一句:邮件里带“安全警报”让你点链接输助记词的,100%钓鱼,别手贱。
$BTC #Trezor #安全
老剧本了——钱包厂商最爱吹私钥自持,结果外围服务一崩照样社死。吃瓜归吃瓜,提醒一句:邮件里带“安全警报”让你点链接输助记词的,100%钓鱼,别手贱。
$BTC #Trezor #安全
53
·
--
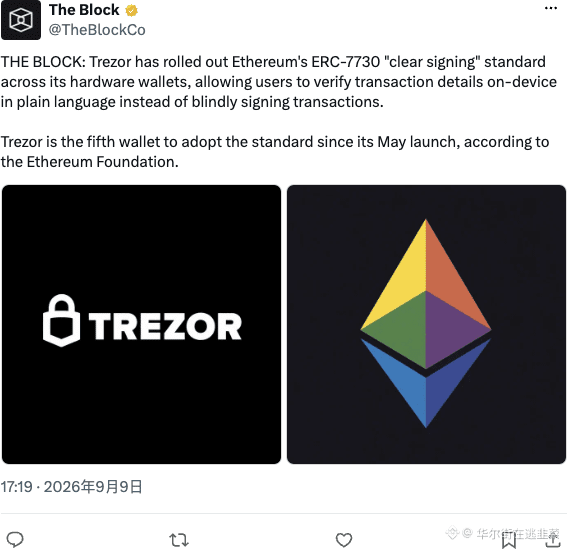
ERC-7730"清晰签名"标配,Trezor硬件钱包终于跟上,用户能在设备上直接看懂交易细节,告别盲签。
这是第五家接入该标准的钱包,虽然动作慢了半拍,但硬件钱包龙头入局,对DeFi用户防钓鱼是真刚需。利好以太坊生态安全基建,短期没币价刺激,长期降低机构进场门槛。
$ETH #Trezor
ERC-7730"清晰签名"标配,Trezor硬件钱包终于跟上,用户能在设备上直接看懂交易细节,告别盲签。
这是第五家接入该标准的钱包,虽然动作慢了半拍,但硬件钱包龙头入局,对DeFi用户防钓鱼是真刚需。利好以太坊生态安全基建,短期没币价刺激,长期降低机构进场门槛。
$ETH #Trezor
这是第五家接入该标准的钱包,虽然动作慢了半拍,但硬件钱包龙头入局,对DeFi用户防钓鱼是真刚需。利好以太坊生态安全基建,短期没币价刺激,长期降低机构进场门槛。
$ETH #Trezor
95
·
--
Trezor’s latest breach update is a reminder that crypto security does not end with your private keys.
The hardware-wallet maker says a fulfillment-provider incident exposed contact and order data tied to roughly 80,000 customers after files that were reportedly deleted were found still retained. The newly disclosed records relate to U.S. orders from November 2019 through August 2021.
Trezor says its devices, systems and services were not compromised—no recovery seeds, private keys or wallet funds were exposed. That distinction matters.
But so does the risk: a leaked name, address, phone number and hardware-wallet purchase history can give scammers a highly targeted list. Expect more convincing phishing emails, fake support calls and potentially even physical-targeting concerns.
If you bought a Trezor in that period, check the email address used for the order and treat every unsolicited message with extra caution. Never share or enter your recovery phrase anywhere.
The bigger question now is whether hardware-wallet firms and their vendors can truly enforce data-deletion policies—not just promise them.
Should crypto hardware companies retain customer shipping data at all once an order is complete?
#Trezor #CryptoSecurity #CryptoNews
59
·
--
Trezor 物流商泄露再扩面:约 6.7 万美国用户入列,总影响超 8 万
硬钱包厂商 Trezor(SatoshiLabs)9 月 4 日更新披露:物流合作方 ShipMonk 数据泄露范围再度扩大,新增约 6.7 万名美国客户(订单窗口约 2019 年 11 月至 2021 年 8 月),累计波及约 8 万人。公司称此前曾获书面确认旧数据已删除,但记录仍留在供应商系统。
关键事实:泄露主要为姓名、邮箱、电话、收货地址与订单号;Trezor 自有系统、固件、助记词/私钥与钱包备份未受影响,资金无法被远程盗取。真正风险在社工与钓鱼——攻击者可拿真实订单号冒充官方诱骗助记词;住址外泄也抬高线下风险。
周末美股劳动节休市,宏观静音时安全叙事更易扩散。Trezor 正推 Anonymous Delivery,并提醒:官方绝不会索要助记词。
据公开社交/新闻整理,非投资建议。 $BTC #Trezor #硬件钱包 #安全 #美股
1
182
⚠️ Filtro de Datos en Trezor: Vector de Ataque Físico y OpSec
Un fallo de seguridad en el proveedor logístico ShipMonk ha expuesto la información de identificación personal (PII) de más de 80.000 clientes de Trezor. Aunque la clave privada y las seed phrases permanecen 100% intactas en la blockchain, la filtración incluye nombres completos, teléfonos y direcciones físicas.
Análisis técnico: El riesgo de explotación pasa del plano on-chain al plano de ingeniería social avanzada (spear phishing, SIM swapping) y vectores de amenaza física ($5 wrench attack). En la autocustodia, la privacidad de los metadatos off-chain es una capa de defensa tan crítica como el propio cifrado criptográfico de la wallet.
¿Qué protocolos de OpSec aplicas al adquirir hardware wallets: utilizas casilleros/P.O. Box neutrales o añades capas extra como passphrases ocultas para mitigar el riesgo de extorsión física?
$BTC
{future}(BTCUSDT)
$ETH
{future}(ETHUSDT)
$SOL
{future}(SOLUSDT)
#Trezor #ciberseguridad #OPSEC #SeguridadCripto
⚠️ Filtro de Datos en Trezor: Vector de Ataque Físico y OpSec
Un fallo de seguridad en el proveedor logístico ShipMonk ha expuesto la información de identificación personal (PII) de más de 80.000 clientes de Trezor. Aunque la clave privada y las seed phrases permanecen 100% intactas en la blockchain, la filtración incluye nombres completos, teléfonos y direcciones físicas.
Análisis técnico: El riesgo de explotación pasa del plano on-chain al plano de ingeniería social avanzada (spear phishing, SIM swapping) y vectores de amenaza física ($5 wrench attack). En la autocustodia, la privacidad de los metadatos off-chain es una capa de defensa tan crítica como el propio cifrado criptográfico de la wallet.
¿Qué protocolos de OpSec aplicas al adquirir hardware wallets: utilizas casilleros/P.O. Box neutrales o añades capas extra como passphrases ocultas para mitigar el riesgo de extorsión física?
$BTC
$ETH
$SOL
#Trezor #ciberseguridad #OPSEC #SeguridadCripto
2
73
Populer donanim cuzdani ureticisi Trezor, tedarikcisi ShipMonk yasanan veri ihlalinden 67.000 musterinin daha etkilendigini duyurdu. 2019-2021 yillarina ait isim, e-posta, telefon ve teslimat adresleri gibi hassas iletisim bilgileri etkilenen veriler arasinda yer aliyor. Cihaz guvenligi tehlikede olmasa da kullanicilarin olasi oltalama saldirilarina karsi dikkatli olmasi gerekiyor. #Trezor #KriptoGuvenligi #SiberGuvenlik
Populer donanim cuzdani ureticisi Trezor, tedarikcisi ShipMonk yasanan veri ihlalinden 67.000 musterinin daha etkilendigini duyurdu. 2019-2021 yillarina ait isim, e-posta, telefon ve teslimat adresleri gibi hassas iletisim bilgileri etkilenen veriler arasinda yer aliyor. Cihaz guvenligi tehlikede olmasa da kullanicilarin olasi oltalama saldirilarina karsi dikkatli olmasi gerekiyor. #Trezor #KriptoGuvenligi #SiberGuvenlik
52
Populer donanim cuzdan ureticisi Trezor, veri sizintisi skandalinin boyutunun genislemesiyle yeni bir guvenlik kriziyle karsiyasiya. Yapilan aciklamalara gore 67.000'den fazla musterinin bilgileri risk altinda ve bazilarinin 2019'a kadar uzanan eski kayitlarinin saklandigi ortaya cikti. Bu durum, sirketin veri saklama politikalarina ve kullanici guvenligine dair soru isaretlerini artiriyor. Donanim cuzdan sahiplerinin olasi oltalama saldirilarina karsi dikkatli olmasi onem tasiyor. #Trezor #Security #CryptoNews
Populer donanim cuzdan ureticisi Trezor, veri sizintisi skandalinin boyutunun genislemesiyle yeni bir guvenlik kriziyle karsiyasiya. Yapilan aciklamalara gore 67.000'den fazla musterinin bilgileri risk altinda ve bazilarinin 2019'a kadar uzanan eski kayitlarinin saklandigi ortaya cikti. Bu durum, sirketin veri saklama politikalarina ve kullanici guvenligine dair soru isaretlerini artiriyor. Donanim cuzdan sahiplerinin olasi oltalama saldirilarina karsi dikkatli olmasi onem tasiyor. #Trezor #Security #CryptoNews
24
Trezor xác nhận vụ vi phạm ShipMonk ảnh hưởng tới 67.000 khách hàng
- Các bản ghi mới được phát hiện từ năm 2019 đến 2021
- Thông tin bị lộ bao gồm họ tên, email, số điện thoại, địa chỉ giao hàng và số đơn hàng
- Số khách hàng bị ảnh hưởng là 67.000
#BinanceSquare #CryptoNews #Trezor
$btc $eth
#vlikevn #Titanbot
Nguồn: The Block
- Các bản ghi mới được phát hiện từ năm 2019 đến 2021
- Thông tin bị lộ bao gồm họ tên, email, số điện thoại, địa chỉ giao hàng và số đơn hàng
- Số khách hàng bị ảnh hưởng là 67.000
#BinanceSquare #CryptoNews #Trezor
$btc $eth
#vlikevn #Titanbot
Nguồn: The Block
136

·
--
Trezor泄密升级了!又多6.7万美国用户中招,这次是物流商被黑,收货人的姓名、地址、电话黑客全拿到了。
接下来的剧本我闭眼都能想到:黑客冒充“Trezor官方客服”给你打电话发短信,好心提醒你“钱包有风险”,然后一步步套你的助记词。
划重点:助记词就是命根子,官方永远不会找你要!收到任何“官方”消息,别点链接,直接上官网核实。
行情上这事儿掀不起大浪,短期有点FUD情绪,但$BTC该怎么走还怎么走,倒是硬件钱包的安全脸面有点挂不住。说到底,管好自己的私钥比啥都强。
用Trezor的朋友最近都绷紧点,别让黑客把你手里的币钓走了!
$BTC #Trezor #加密安全
Trezor泄密升级了!又多6.7万美国用户中招,这次是物流商被黑,收货人的姓名、地址、电话黑客全拿到了。
接下来的剧本我闭眼都能想到:黑客冒充“Trezor官方客服”给你打电话发短信,好心提醒你“钱包有风险”,然后一步步套你的助记词。
划重点:助记词就是命根子,官方永远不会找你要!收到任何“官方”消息,别点链接,直接上官网核实。
行情上这事儿掀不起大浪,短期有点FUD情绪,但$BTC 该怎么走还怎么走,倒是硬件钱包的安全脸面有点挂不住。说到底,管好自己的私钥比啥都强。
用Trezor的朋友最近都绷紧点,别让黑客把你手里的币钓走了!
$BTC #Trezor #加密安全
接下来的剧本我闭眼都能想到:黑客冒充“Trezor官方客服”给你打电话发短信,好心提醒你“钱包有风险”,然后一步步套你的助记词。
划重点:助记词就是命根子,官方永远不会找你要!收到任何“官方”消息,别点链接,直接上官网核实。
行情上这事儿掀不起大浪,短期有点FUD情绪,但$BTC 该怎么走还怎么走,倒是硬件钱包的安全脸面有点挂不住。说到底,管好自己的私钥比啥都强。
用Trezor的朋友最近都绷紧点,别让黑客把你手里的币钓走了!
$BTC #Trezor #加密安全
92
Trezor confirms that a data breach at one of its shipping providers has compromised the information of 67,000 US customers, potentially exposing them to targeted phishing and social engineering attacks.
#Trezor #PhishingAlert
Trezor confirms that a data breach at one of its shipping providers has compromised the information of 67,000 US customers, potentially exposing them to targeted phishing and social engineering attacks.
#Trezor #PhishingAlert
#Trezor #PhishingAlert
8
·
--
CZ just highlighted a risk most self-custody users rarely think about.
The Trezor-related breach didn’t compromise the hardware wallet itself.
The breach happened at its shipping provider, exposing personal information from thousands of customers.
CZ’s point was interesting: buying a physical hardware wallet can create a real-world trail connecting your identity and address to your crypto security setup.
That doesn’t make software wallets automatically safer.
It shows that self-custody has another layer beyond private keys: privacy.
Your wallet can be secure while the information around it isn’t.
Would you choose anonymous delivery for a hardware wallet if it was available?
#CryptoSecurity #SelfCustody #Trezor $BNB
1
89
ເຂົ້າສູ່ລະບົບເພື່ອສຳຫຼວດເນື້ອຫາເພີ່ມເຕີມ
ເຂົ້າຮ່ວມກຸ່ມຜູ້ໃຊ້ຄຣິບໂຕທົ່ວໂລກໃນ Binance Square.
⚡️ ໄດ້ຮັບຂໍ້ມູນຫຼ້າສຸດ ແລະ ທີ່ມີປະໂຫຍດກ່ຽວກັບຄຣິບໂຕ.
💬 ໄດ້ຮັບຄວາມໄວ້ວາງໃຈຈາກຕະຫຼາດແລກປ່ຽນຄຣິບໂຕທີ່ໃຫຍ່ທີ່ສຸດໃນໂລກ.
👍 ຄົ້ນຫາຂໍ້ມູນເຊີງເລິກທີ່ແທ້ຈາກນັກສ້າງທີ່ໄດ້ຮັບການຢືນຢັນ.
ອີເມວ / ເບີໂທລະສັບ
ຫົວຂໍ້ທີ່ກໍາລັງນິຍົມ
1
#EtherGains70.9%InQ3
138,013 views
1,099 ກຳລັງສົນທະນາ
2
#TreasuryLetsStatesFileStablecoinCertificationsEarly
7,235 views
74 ກຳລັງສົນທະນາ
3
#US10YearYieldNears5.3%
141,973 views
1,101 ກຳລັງສົນທະນາ
4
#DollarIndexHitsHighestSinceMay2025
33,809 views
581 ກຳລັງສົນທະນາ
5
#USWeeklyJoblessClaimsFallTo197000
31,836 views
486 ກຳລັງສົນທະນາ
6
#BitcoinETFsTake$6.34BillionInQ3
9,232 views
74 ກຳລັງສົນທະນາ
7
#KoreaProposesTokenizingStocksAndBonds
68,487 views
816 ກຳລັງສົນທະນາ
8
#MetaMaskExitsLidoValidatorsAfterSecurityIncident
167,521 views
1,537 ກຳລັງສົນທະນາ
9
#MicronBeatsEarningsLiftsGuidance
84,411 views
1,112 ກຳລັງສົນທະນາ
10
#CFTCSubmitsTwoEventContractRulesToWhiteHouse
57,890 views
828 ກຳລັງສົນທະນາ