#keplradvisessocialloginuserstotransferassets
🚨 Security Incident Brief: Keplr Wallet & Web3Auth Infrastructure Vulnerability
📅 Issued: November 8, 2026 | ⚠️ Alert Level: High |
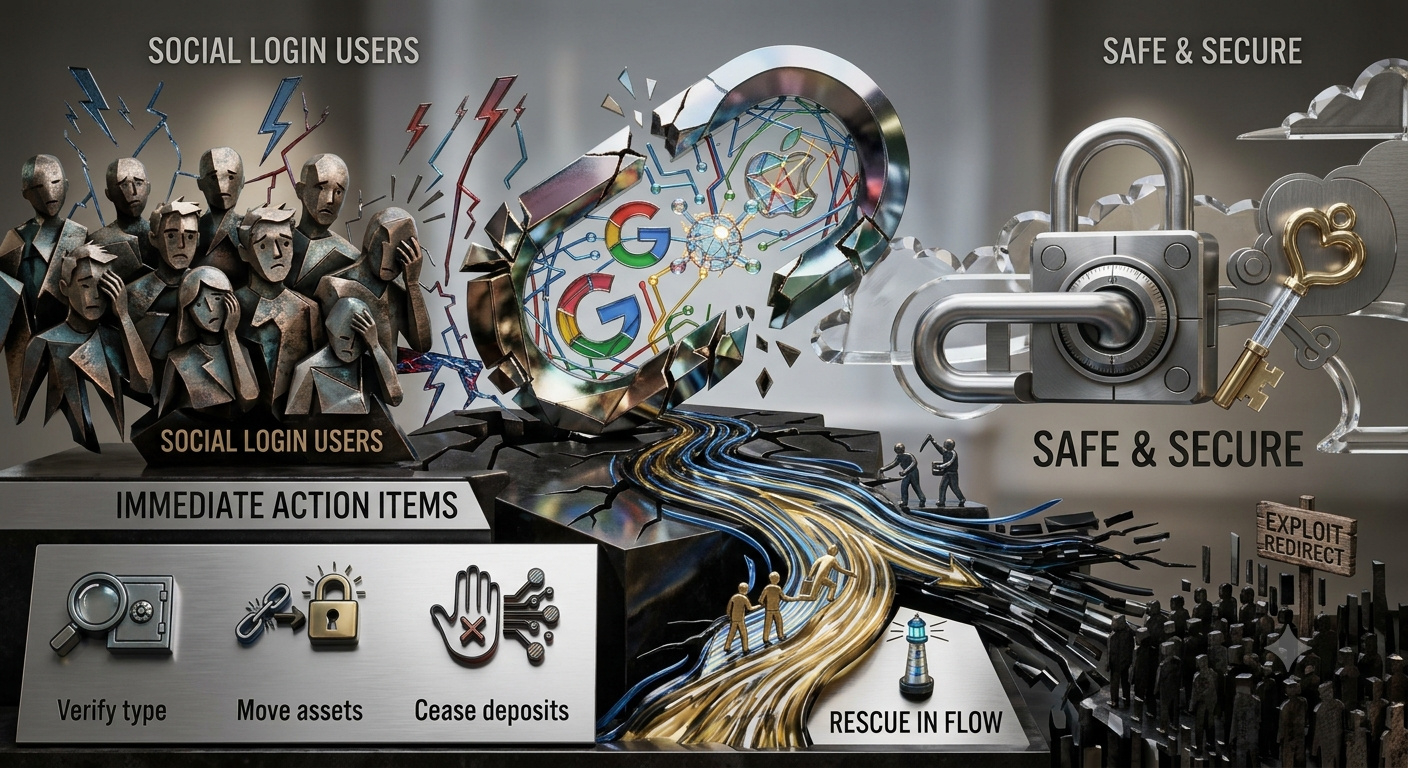
📌 Overview :- A critical upstream security vulnerability originating from Web3Auth—the third-party infrastructure provider powering social and embedded authentication—has impacted users utilizing Google and Apple ID logins on the Keplr ecosystem.
- 🔴 What Was Affected: Wallets generated through social/embedded sign-ins (Distributed Key Generation mechanism).
- 🟢 What Remained Safe: Traditional mnemonic seed-phrase wallets and hardware wallets (e.g., Ledger) are entirely unaffected. Keplr's core application code was not directly compromised.
📊 On-Chain Statistics & Impact Analysis
Comprehensive blockchain forensic data (via analytics providers such as Bitquery) highlights the scale of the exploit across the Cosmos ecosystem:
- 💰 Total Tracked Losses: ≥ $6.01 million in liquid assets across multiple Cosmos-based networks.
- 👛 Affected Scale: At least 44,041+ individual wallets suffered unauthorized balance sweeps.
- 🔒 Staked Asset Impact: Attackers extracted 1.96 million staked ATOM, bypassing traditional unbonding queues in certain vector sequences.
📉 Distribution of Losses:
- 88% of victims lost under $100, indicating a heavy impact on retail users.
- The median loss per wallet was low (~$1.34), meaning total losses are heavily concentrated within a few dozen higher-balance accounts (the single largest recorded individual drain reached $325K).
🌐 Multi-Chain Exposure: Because a single social login key manages cross-chain assets symmetrically, 46% of drained wallets were hit across two or more separate chains simultaneously.
⏱️ Behavioral Anomaly: Paradoxically, 86% of total funds were drained after initial public warnings went live, highlighting the propagation lag of security alerts among casual retail users.
🛡️ Important Note on "Disappearing" Balances
⚠️ Some affected wallets may show reduced or zero balances due to white-hat rescue transfers—assets proactively moved to safety by Keplr and Web3Auth—not theft.
- ✅ Check Web3Auth's verified rescue address list before concluding funds were stolen.
- ⏳ Staked and locked assets take longer to resolve due to processing complexity.
- 📌 The "86% drained after warnings" figure may be partially inflated by these rescue outflows.
✅ Immediate Action Items for Users
1. 🔍 Verify Your Login Type: If you access your assets strictly via seed phrase or hardware wallet, no action is required.
2. 💸 Move Remaining Assets: If you previously utilized Google/Apple sign-ins and still hold a liquid balance, urgently transfer remaining funds to a newly generated, self-custodied seed-phrase or hardware-backed wallet.
3. 🚫 Cease Deposits: Do not deposit any fresh liquidity into social-login associated accounts.
4. 🎣 Ignore Social Engineering: Beware of opportunistic threat actors circulating fake "recovery tools" or direct messages promising asset refunds. No legitimate entity will DM you first.
📡 What We're Monitoring
- Web3Auth's verified rescue address list publication
- Keplr's affected-account lookup tool launch
- Official corrections to total affected wallets and final loss figures
🔐 Stay safe, verify communication channels through official foundations, and prioritize cold storage hygiene. Self-custody with a seed phrase or hardware wallet remains the gold standard for high-value assets.
$GOOGLB $AAPLB $MSFTB
#Binance #Google #Apple #BinanceSquareTalks