🔐 A cyberattack on GitBook puts more than documentation at risk.
GitBook, a documentation platform used by crypto projects and other developers, disclosed a targeted intrusion involving AI agents on November 2.
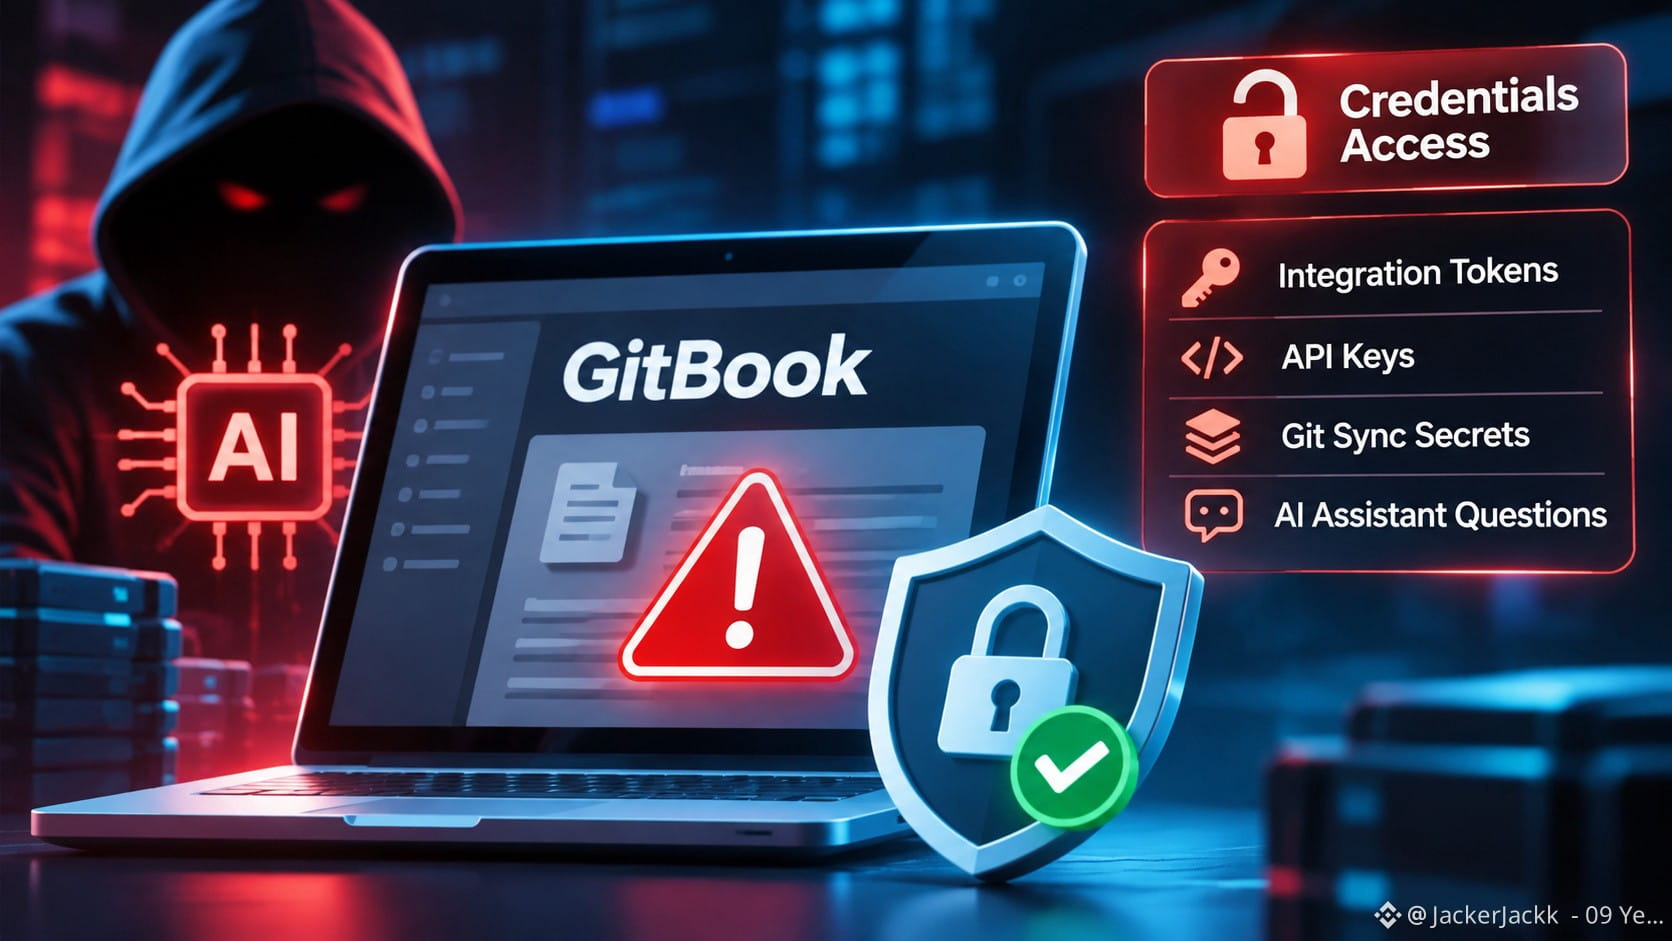
Attackers gained unauthorized access to some infrastructure credentials. GitBook says it detected and blocked the attack, but integration tokens, API keys, Git Sync secrets and questions submitted to its AI assistant may have been exposed.
The concern goes beyond leaked information. Credentials connected to other services could potentially give attackers access outside GitBook.
GitBook has replaced its infrastructure secrets, revoked customer API tokens and restored its main services. It reports no evidence that published content was modified.
For teams using GitBook, the priority is clear: GitBook advises customers to rotate connected third-party credentials and re-authenticate GitBook MCP connections.
The lesson extends beyond crypto: when services are connected, one security incident can create risks across several systems.
GitBook, a documentation platform used by crypto projects and other developers, disclosed a targeted intrusion involving AI agents on November 2.
Attackers gained unauthorized access to some infrastructure credentials. GitBook says it detected and blocked the attack, but integration tokens, API keys, Git Sync secrets and questions submitted to its AI assistant may have been exposed.
The concern goes beyond leaked information. Credentials connected to other services could potentially give attackers access outside GitBook.
GitBook has replaced its infrastructure secrets, revoked customer API tokens and restored its main services. It reports no evidence that published content was modified.
For teams using GitBook, the priority is clear: GitBook advises customers to rotate connected third-party credentials and re-authenticate GitBook MCP connections.
The lesson extends beyond crypto: when services are connected, one security incident can create risks across several systems.