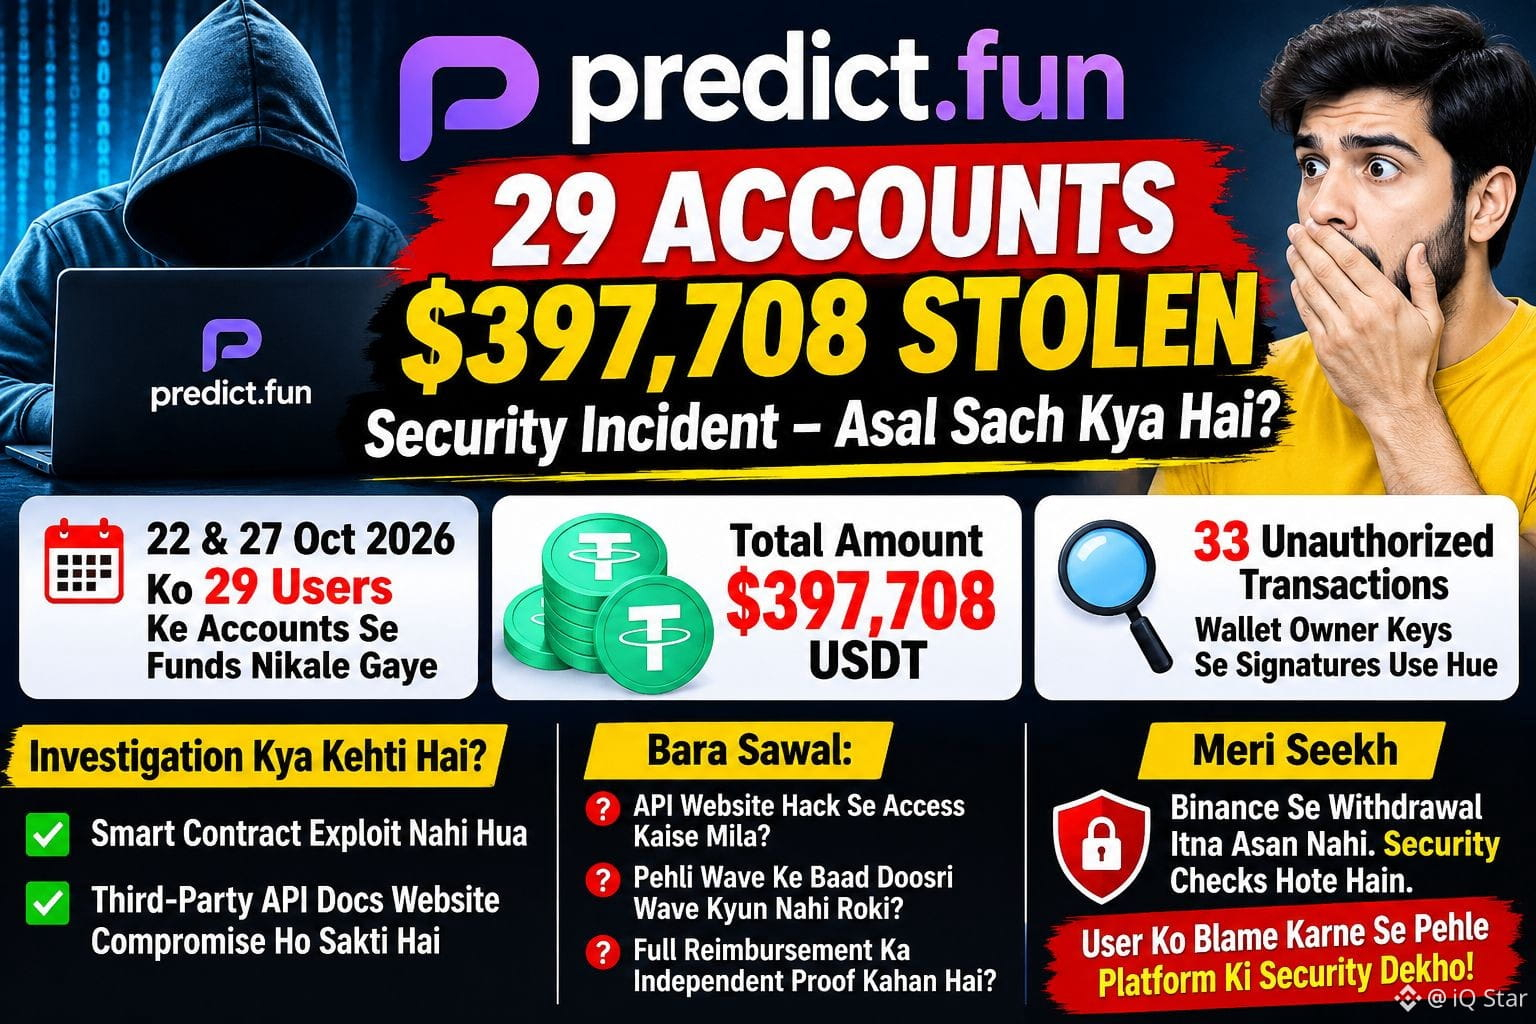

29 ACCOUNTS, $397,708 STOLEN – PREDICT.FUN INCIDENT SE ASAL SABAK KYA MILTA HAI?
Predict.fun par 22 aur 27 October 2026 ko do waves mein 29 users ke accounts se approximately 397,708 USDT nikal liye gaye.
Lekin is incident ki sab se important baat ye hai:
Blockchain investigation ke mutabiq 33 unauthorized transactions mein users ke wallet owner keys se signatures use hue. Predict.fun ke market smart contracts ko exploit nahi kiya gaya.
Platform ki preliminary explanation ke mutabiq uski third-party hosted API documentation website compromise hui ho sakti hai.
Ab sawal ye hai:
Agar kisi platform ki third-party service compromise ho jaye aur users ke wallet credentials expose ho jayein, to zimmedari kis ki hogi?
Meri baat samjhein:
Binance se kisi doosre trading platform par withdrawal karna sirf ek click ka mamla nahi. Security checks aur withdrawal reviews bhi hote hain. Isliye ye kehna ke AI ya kisi simple technical explanation se koi bhi kisi ka paisa nikal sakta hai, asal security failure ko samajhna nahi hai.
Teen sawal Predict.fun se jawab maangte hain:
API documentation website compromise hone se wallet owner keys tak access kaise mila?
Security monitoring ne pehli wave ke baad doosri wave ko kyun nahi roka?
Platform ne full reimbursement ka wada kiya hai, lekin payment complete hone ka independent confirmation kahan hai?
Meri nazar mein user ko blame karne se pehle platform ki security architecture, third-party dependencies aur access-control system ki investigation zaroori hai.
Asal security ka test tab hota hai jab users ka paisa risk mein ho, na ke tab jab platform apni security ka dawa kar raha ho.
Predict.fun par 22 aur 27 October 2026 ko do waves mein 29 users ke accounts se approximately 397,708 USDT nikal liye gaye.
Lekin is incident ki sab se important baat ye hai:
Blockchain investigation ke mutabiq 33 unauthorized transactions mein users ke wallet owner keys se signatures use hue. Predict.fun ke market smart contracts ko exploit nahi kiya gaya.
Platform ki preliminary explanation ke mutabiq uski third-party hosted API documentation website compromise hui ho sakti hai.
Ab sawal ye hai:
Agar kisi platform ki third-party service compromise ho jaye aur users ke wallet credentials expose ho jayein, to zimmedari kis ki hogi?
Meri baat samjhein:
Binance se kisi doosre trading platform par withdrawal karna sirf ek click ka mamla nahi. Security checks aur withdrawal reviews bhi hote hain. Isliye ye kehna ke AI ya kisi simple technical explanation se koi bhi kisi ka paisa nikal sakta hai, asal security failure ko samajhna nahi hai.
Teen sawal Predict.fun se jawab maangte hain:
API documentation website compromise hone se wallet owner keys tak access kaise mila?
Security monitoring ne pehli wave ke baad doosri wave ko kyun nahi roka?
Platform ne full reimbursement ka wada kiya hai, lekin payment complete hone ka independent confirmation kahan hai?
Meri nazar mein user ko blame karne se pehle platform ki security architecture, third-party dependencies aur access-control system ki investigation zaroori hai.
Asal security ka test tab hota hai jab users ka paisa risk mein ho, na ke tab jab platform apni security ka dawa kar raha ho.