

A shocking Binance security incident has raised serious questions about hot wallet security.
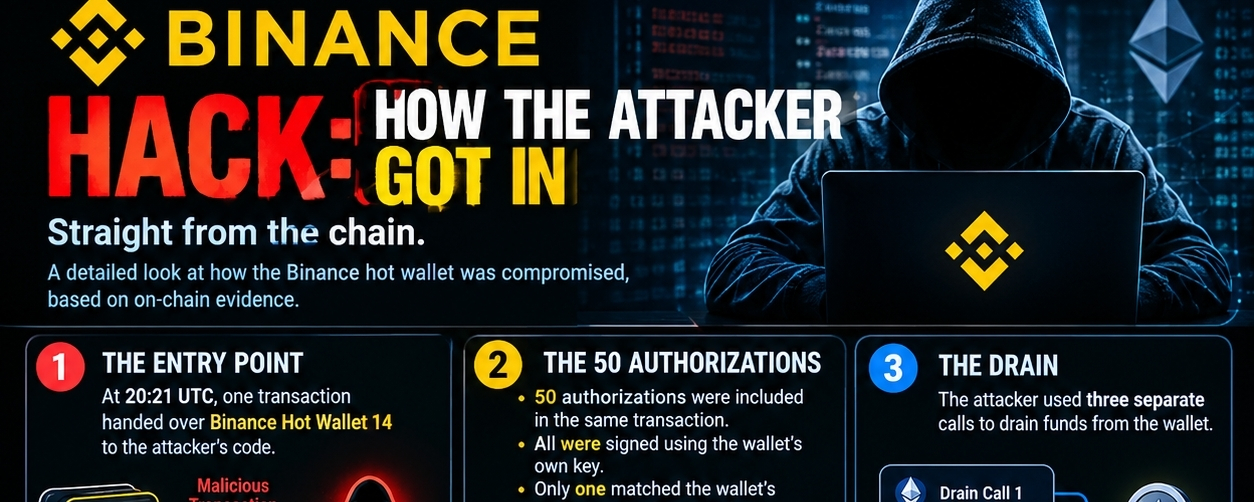
At 20:21 UTC, a transaction gave an attacker access to Binance Hot Wallet 14 through malicious code.
🔍 What happened?
- 50 authorizations were included in one transaction.
- All were signed using the wallet's own key.
- Only one authorization matched the wallet's next nonce and executed.
- The attacker used three separate calls to drain funds.
- The attacker's wallet received gas funding partly through Tornado Cash withdrawals.
- The first reported withdrawal happened on October 28, around 37 hours before the attack.
⚠️ The biggest concern: The attacker apparently had the ability to make Binance's wallet key authorize transactions.
💰 Around 94% of the Ethereum-denominated funds reportedly remain frozen, according to the provided incident details.
This incident highlights how dangerous compromised signing permissions can be, even when blockchain transactions remain fully transparent.
I will be watching the on-chain investigation closely. More updates may reveal how the attacker gained access.
Stay alert. Protect your assets. DYOR!
#Binance #CryptoSecurity #CRYPTOHYPER5 #Ethereum #blockchain $BTC
