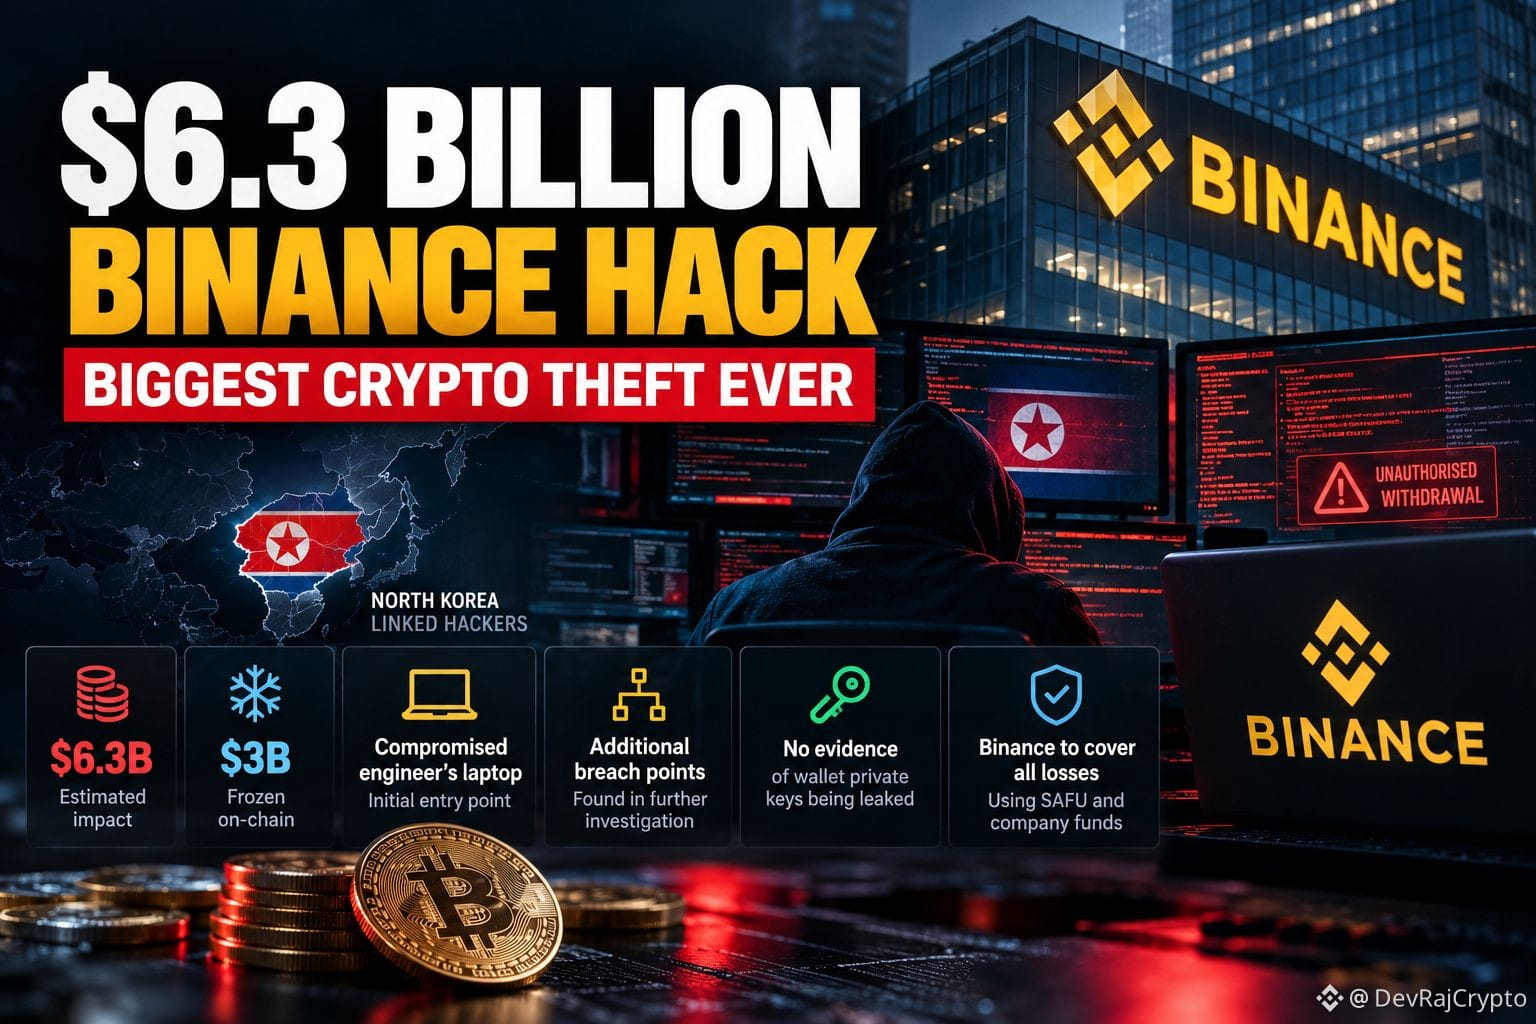
$6.3 BILLION.
The reported Binance security incident should make the entire crypto industry stop and think. But one detail deserves more attention than the headline: how did attackers gain access to the infrastructure that could authorise unauthorised withdrawals?
Here's what we know so far:
• Estimated financial impact: approximately $6.3 billion.
• Around $3 billion in affected assets frozen on-chain.
• Binance's initial investigation identified a potentially compromised DevOps engineer's laptop.
• Subsequent investigation uncovered additional points of breach.
• Binance says it found no evidence of wallet private keys being leaked.
• The company has committed to covering all losses using SAFU and company funds.
The technical details matter. Binance's initial explanation pointed to a compromised laptop that may have provided access to a service container. However, the company later clarified that this was a complex, multi-stage attack, not simply one engineer's permissions being exploited in a single action. A full technical post-mortem is still pending.
My biggest concern isn't just the amount involved. It's the security architecture that allowed unauthorised withdrawal transactions to happen. Crypto exchanges need more than secure wallets. They need strong internal access controls, transaction authorisation safeguards, continuous monitoring and independently verifiable security processes.
There's an important distinction here: freezing stolen assets is incident response. Covering financial losses is accountability. Preventing the next attack is security.
The industry needs all three.
Binance now needs to demonstrate transparency, provide independent verification and show measurable improvements to its security infrastructure. Its commitment to cover losses is important, but the full technical investigation and updated Proof of Reserves will matter just as much.
Trust isn't restored by a statement. It's rebuilt through evidence.
#Binance #CryptoSecurity #bitcoin