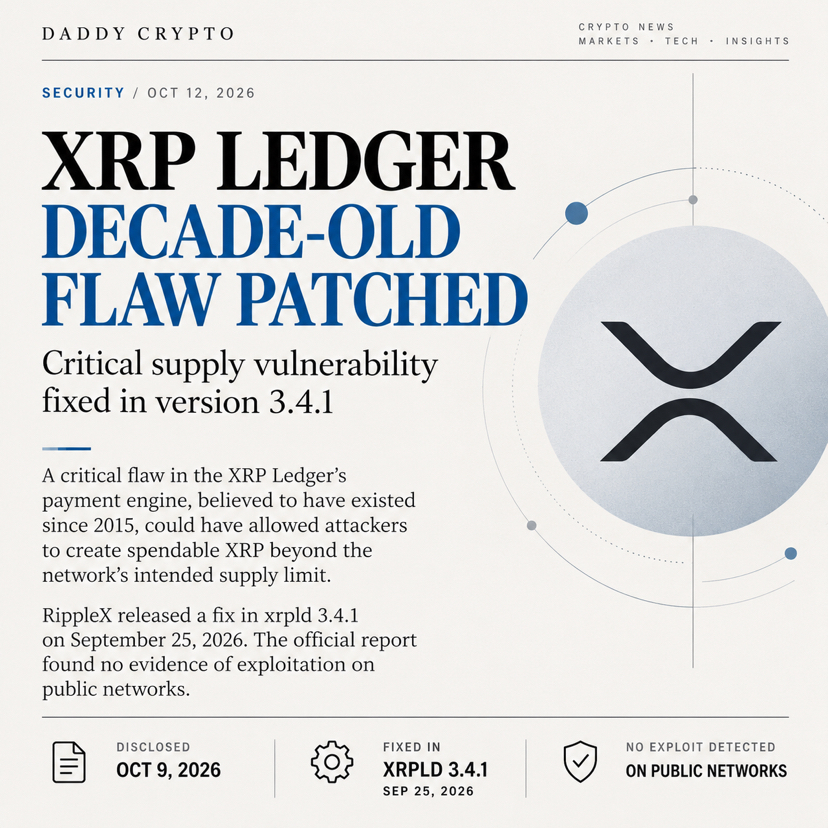
A critical $XRP Ledger flaw went undetected for roughly a decade.
Disclosed on October 9, the vulnerability could have allowed attackers to create spendable XRP beyond the network’s intended supply limit.
RippleX released a fix in xrpld 3.4.1 on September 25. The official report found no evidence of exploitation on public networks.
The takeaway? Fixed supply depends on secure code, not just protocol promises.