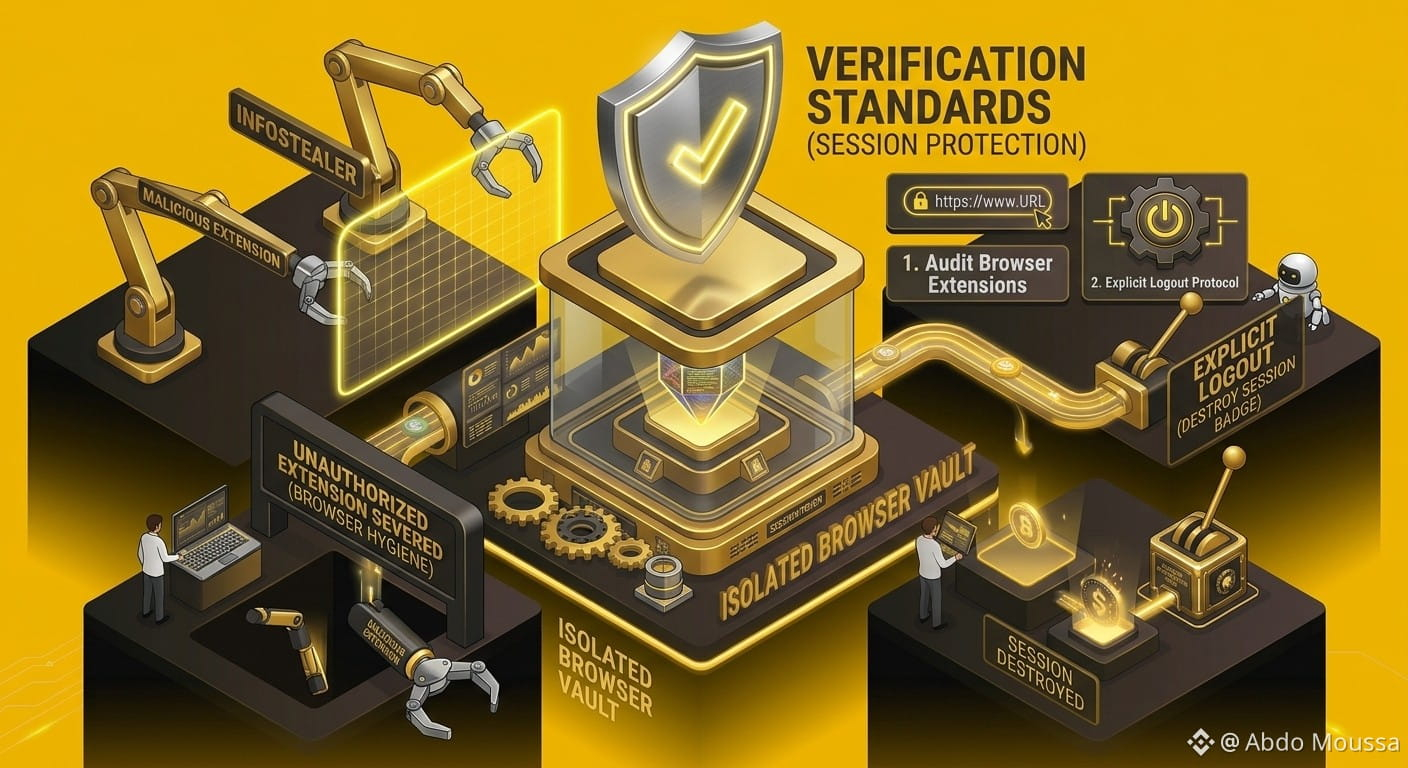
🍪 Browser Hygiene: Protecting Active Sessions from Cookie Theft
Relying solely on multi-factor authentication is insufficient if active browser sessions are left vulnerable to session-hijacking malware designed to steal access cookies and authorization tokens.
💡 Mitigating Session Hijacking & Token Theft
Understand Cookie Stealers: Specialized malware (InfoStealers) targets localized browser databases to export active session cookies, allowing attackers to clone an authenticated session on a remote machine.
Explicit Logouts: Always click the explicit Log Out button rather than simply closing the browser tab when concluding sensitive financial activities.
Audit Browser Extensions: Routinely inspect and remove unnecessary or unverified third-party browser extensions that possess broad web-reading permissions.
Isolate Trading Environments: Dedicate a clean, extension-free browser profile or isolated device exclusively for executing digital asset transactions.
⚠️ Security & Educational Disclaimer
Maintaining strict browser environment hygiene prevents unauthorized session cloning and credential harvesting, This publication is prepared strictly for educational and security awareness purposes.
https://www.binance.com/en/academy/articles/what-are-cookies
Clean your browser cache, log out of sensitive sessions, and always DYOR (Do Your Own Research) 💡
#Binance #Security #AccountSecurity #dyor