$387.5M drained from Bitget. Withdrawals finally reopen today.
Attackers didn't steal keys — they spoofed backend data and tricked Bitget's own approval flow. Cold wallets safe. User balances untouched. But withdrawals? Frozen since Sept 24.
CEO hints North Korea. No official confirmation yet.
Still with attacker:
63,000 $ETH ($183M)
102M $XRP ($157M)
Only $318K frozen
Bitget claims $464M+ protection fund covers it. We'll see.
Withdrawal rollout (08:00 UTC):
Sept 28: $BTC
Sept 29: $ETH
Sept 30: $USDT
Oct 2: Everything else
Real test starts today.
THORChain drama:
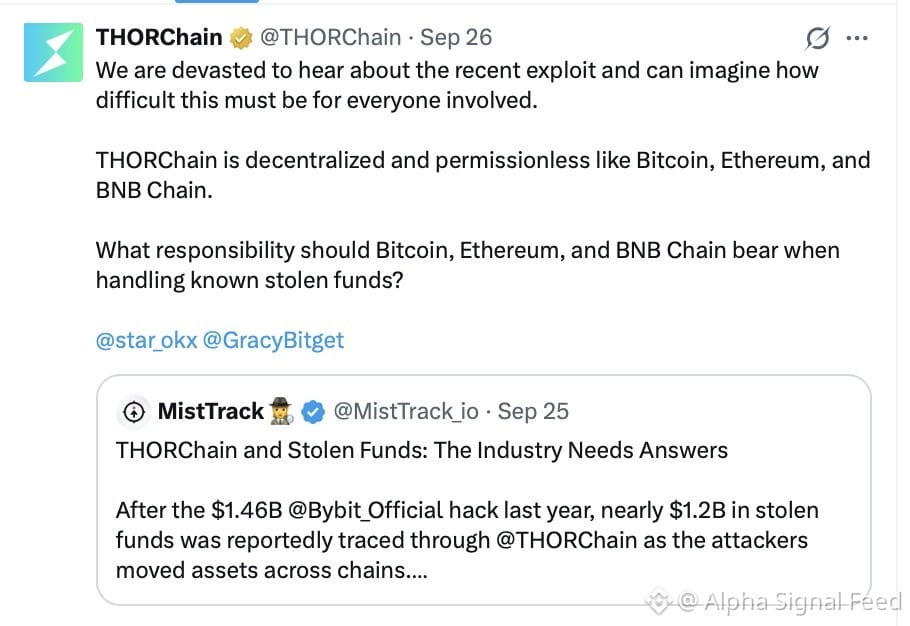
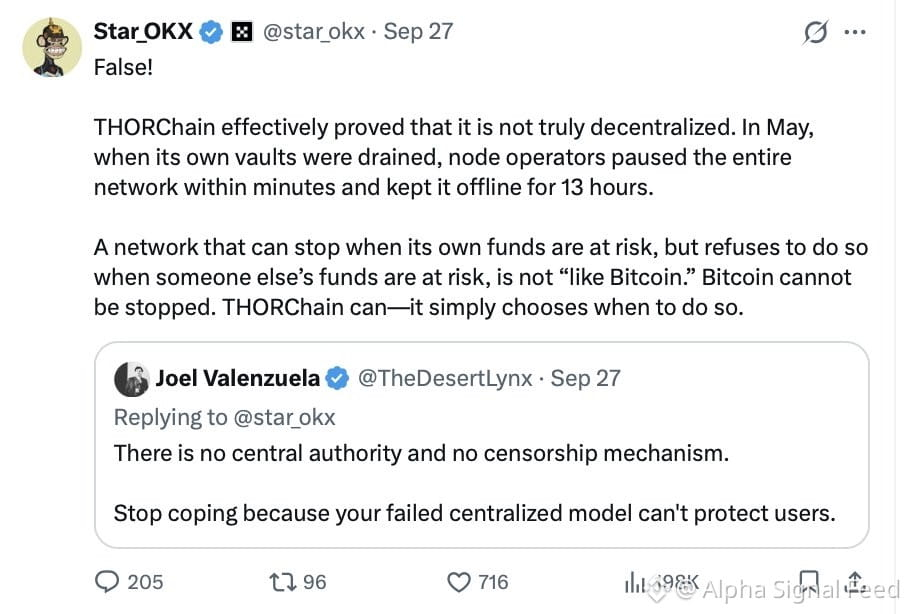
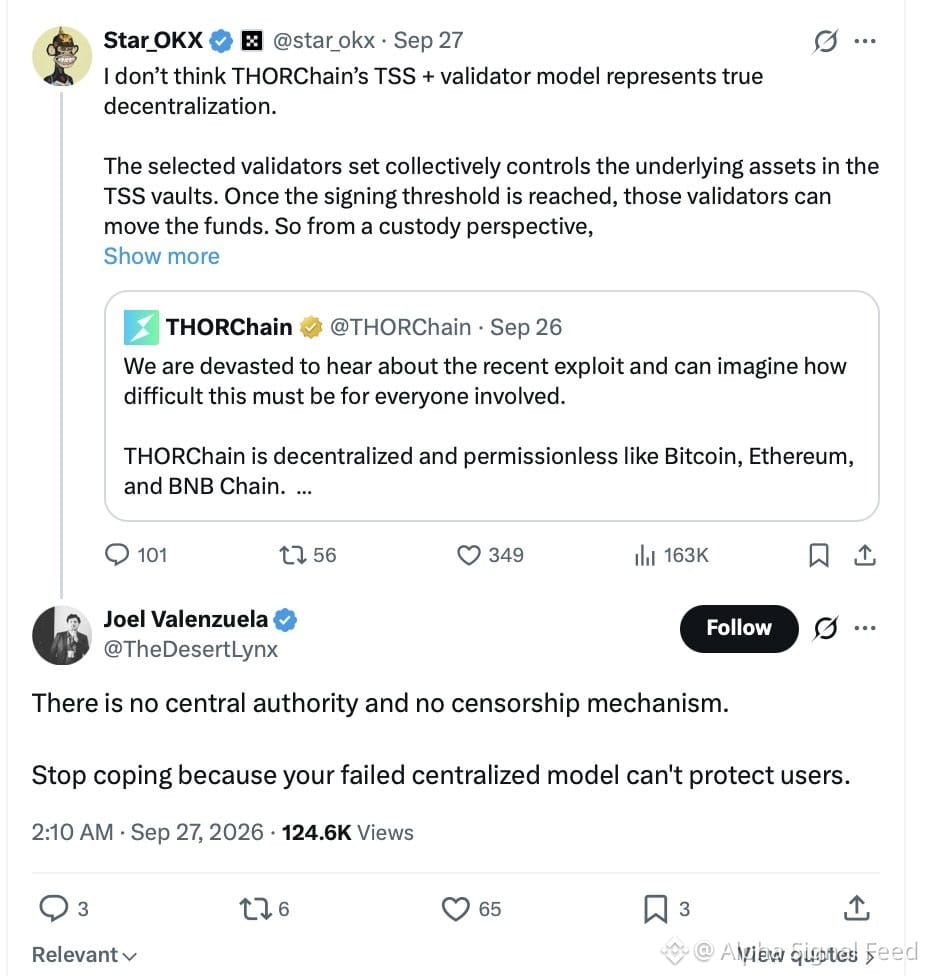
Stolen funds getting swapped to $BTC via THORChain. Same route as Bybit hack. Bitget asked them to block addresses. THORChain said no — "permissionless like Bitcoin."
But in May 2026, THORChain halted their entire network in hours after losing $10.7M of their own funds. Stayed offline 5+ weeks.
So the kill switch exists. They just choose when to use it.
$DOG delisting:
Bitget announced $DOG/USDT delisting for Sept 30 right after the hack. Holders trapped, price decoupled. They call it routine. Timing reeks.
Alpha:
Don't hold more on exchanges than you're actively trading
Judge Bitget by today's withdrawals, not PR
Watch $RUNE — pressure mounting on THORChain
Should THORChain block hacker addresses or stay "permissionless"?