You don’t have to be the target to become the victim.
If one centralized system holds a huge amount of information, one successful breach can turn into everyone’s problem.
That’s why I find Liberdus interesting.
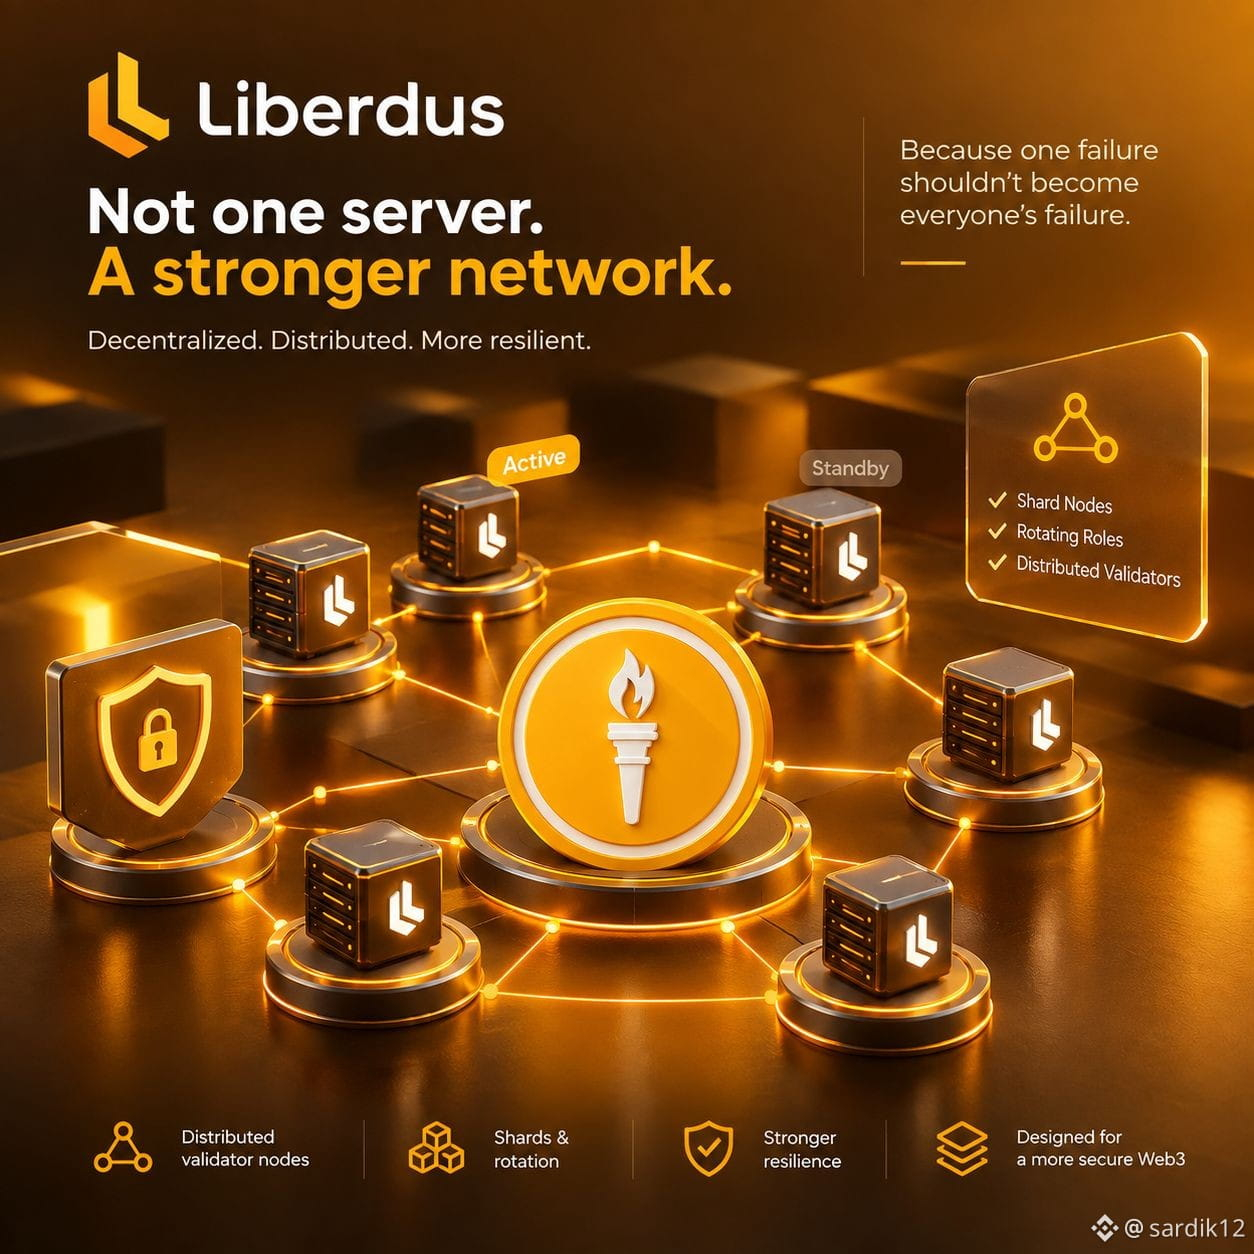
Its architecture isn’t built around one central server. Liberdus runs across distributed validator nodes using Shardus, with nodes organized into shards and rotated between active and standby roles.
The point isn’t:
“ #Liberdus can never be hacked.”
That would be a ridiculous security claim.
The more interesting question is:
If one part of the network is compromised, does that automatically compromise everything?
That’s the security model I find worth exploring.
Decentralization doesn’t remove risk.
It changes where the risk sits, how failures propagate, and how much one compromised component can affect the whole system.
There are still trade-offs. Nodes need protection. Code needs testing. Users still have responsibility for their devices.
But that’s exactly why I am paying attention to #Liberdus .
Not because it promises perfect security.
Because it is trying to design around the idea that one failure shouldn’t become everyone’s failure.
#Security $BTC #Privacy $ETH
If one centralized system holds a huge amount of information, one successful breach can turn into everyone’s problem.
That’s why I find Liberdus interesting.
Its architecture isn’t built around one central server. Liberdus runs across distributed validator nodes using Shardus, with nodes organized into shards and rotated between active and standby roles.
The point isn’t:
“ #Liberdus can never be hacked.”
That would be a ridiculous security claim.
The more interesting question is:
If one part of the network is compromised, does that automatically compromise everything?
That’s the security model I find worth exploring.
Decentralization doesn’t remove risk.
It changes where the risk sits, how failures propagate, and how much one compromised component can affect the whole system.
There are still trade-offs. Nodes need protection. Code needs testing. Users still have responsibility for their devices.
But that’s exactly why I am paying attention to #Liberdus .
Not because it promises perfect security.
Because it is trying to design around the idea that one failure shouldn’t become everyone’s failure.
#Security $BTC #Privacy $ETH