
Rahi__K
3.8k Posting
Rahi__K
Laporkan
Blokir Pengguna
"Security is not a one-time event, it's an ongoing process."
"Stay secure, stay safe."
"I invested in crypto. Only what you afford to lose, right?"
1.3K+ Mengikuti
1.1K+ Pengikut
162 Disukai
Posting
·
--
Artikel
Konten yang Dihasilkan AI vs Kreativitas Manusia: Membentuk Masa Depan Inovasi di Era Crypto$BTC $ETH $BNB
Pengantar
Kecerdasan Buatan bukan lagi konsep futuristik—itu dengan cepat menjadi batu penjuru ekonomi digital. Dari menghasilkan karya seni dan menulis artikel hingga membuat perangkat lunak dan menganalisis pasar keuangan, AI mengubah cara orang berkreasi, berkomunikasi, dan berinovasi.
Saat AI terus berkembang, sebuah pertanyaan yang memicu perdebatan sengit di berbagai industri tetap ada:
Bisakah kecerdasan buatan benar-benar menggantikan kreativitas manusia?
Jawabannya lebih kompleks daripada sekadar ya atau tidak.
Konten yang Dihasilkan AI vs Kreativitas Manusia: Membentuk Masa Depan Inovasi di Era Crypto
$BTC $ETH $BNB
Pengantar
Kecerdasan Buatan bukan lagi konsep futuristik—itu dengan cepat menjadi batu penjuru ekonomi digital. Dari menghasilkan karya seni dan menulis artikel hingga membuat perangkat lunak dan menganalisis pasar keuangan, AI mengubah cara orang berkreasi, berkomunikasi, dan berinovasi.
Saat AI terus berkembang, sebuah pertanyaan yang memicu perdebatan sengit di berbagai industri tetap ada:
Bisakah kecerdasan buatan benar-benar menggantikan kreativitas manusia?
Jawabannya lebih kompleks daripada sekadar ya atau tidak.
Pengantar
Kecerdasan Buatan bukan lagi konsep futuristik—itu dengan cepat menjadi batu penjuru ekonomi digital. Dari menghasilkan karya seni dan menulis artikel hingga membuat perangkat lunak dan menganalisis pasar keuangan, AI mengubah cara orang berkreasi, berkomunikasi, dan berinovasi.
Saat AI terus berkembang, sebuah pertanyaan yang memicu perdebatan sengit di berbagai industri tetap ada:
Bisakah kecerdasan buatan benar-benar menggantikan kreativitas manusia?
Jawabannya lebih kompleks daripada sekadar ya atau tidak.
1
50
·
--
Artikel
Perjalanan Saya di Binance: Cerita tentang Kembali dan Rasa SyukurSaya bergabung dengan Binance pada 10/09/2022, dan sekarang telah berjalan 1166 hari sejak perjalanan saya dimulai. Sejak awal, saya merasa senang bisa menjadi bagian dari platform yang terpercaya dan inovatif ini.
Selama perjalanan ini, ada suatu saat saya harus meninggalkan Binance karena alasan pribadi. Berpisah membantu saya merenung dan belajar, serta membuat saya menyadari nilai sejati dari platform ini. Setelah beberapa waktu, saya kembali ke Binance beberapa hari lalu dengan kepercayaan diri dan motivasi yang baru.
Kembali merasa seperti awal yang baru sambil tetap membawa pengalaman dari masa lalu. Binance terus menawarkan alat-alat yang kuat, peluang, dan komunitas global yang tangguh yang mendukung pertumbuhan dan pembelajaran.
Perjalanan Saya di Binance: Cerita tentang Kembali dan Rasa Syukur
Saya bergabung dengan Binance pada 10/09/2022, dan sekarang telah berjalan 1166 hari sejak perjalanan saya dimulai. Sejak awal, saya merasa senang bisa menjadi bagian dari platform yang terpercaya dan inovatif ini.
Selama perjalanan ini, ada suatu saat saya harus meninggalkan Binance karena alasan pribadi. Berpisah membantu saya merenung dan belajar, serta membuat saya menyadari nilai sejati dari platform ini. Setelah beberapa waktu, saya kembali ke Binance beberapa hari lalu dengan kepercayaan diri dan motivasi yang baru.
Kembali merasa seperti awal yang baru sambil tetap membawa pengalaman dari masa lalu. Binance terus menawarkan alat-alat yang kuat, peluang, dan komunitas global yang tangguh yang mendukung pertumbuhan dan pembelajaran.
Selama perjalanan ini, ada suatu saat saya harus meninggalkan Binance karena alasan pribadi. Berpisah membantu saya merenung dan belajar, serta membuat saya menyadari nilai sejati dari platform ini. Setelah beberapa waktu, saya kembali ke Binance beberapa hari lalu dengan kepercayaan diri dan motivasi yang baru.
Kembali merasa seperti awal yang baru sambil tetap membawa pengalaman dari masa lalu. Binance terus menawarkan alat-alat yang kuat, peluang, dan komunitas global yang tangguh yang mendukung pertumbuhan dan pembelajaran.
2
38
·
--
Lihat terjemahan
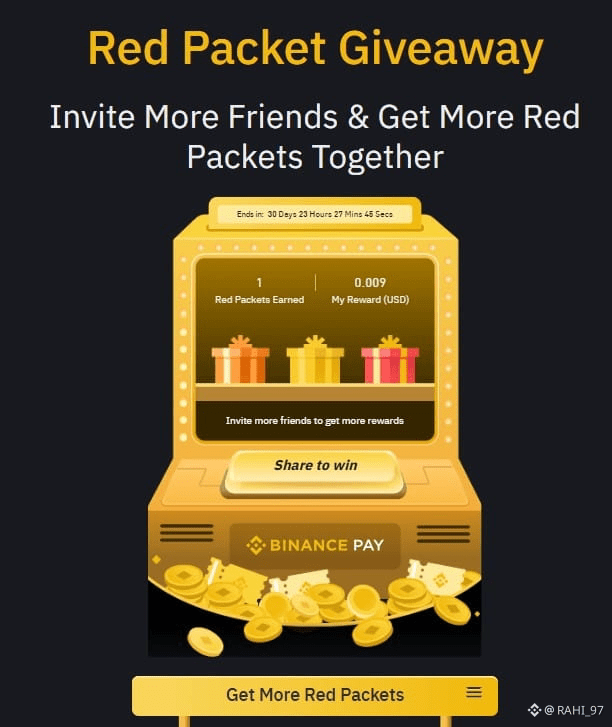
Welcome To The 2026 Let's Celebrate🎉 Happy New Year 2026,,,,, 💥🎁🎉With Free [Red Packet Giveaway.](https://app.binance.com/uni-qr/HwSMZeMR?utm_medium=web_share_copy)
Click [Claim](https://app.binance.com/uni-qr/HwSMZeMR?utm_medium=web_share_copy) Button to Claim Your Free Reward. & Share To Your Friend For Free Reward & Also More Extra Reward Waiting To You...... $DUSK ( $USDT )
{future}(DUSKUSDT)
Welcome To The 2026 Let's Celebrate🎉 Happy New Year 2026,,,,, 💥🎁🎉With Free Red Packet Giveaway.
Click Claim Button to Claim Your Free Reward. & Share To Your Friend For Free Reward & Also More Extra Reward Waiting To You...... $DUSK ( $USDT )
Click Claim Button to Claim Your Free Reward. & Share To Your Friend For Free Reward & Also More Extra Reward Waiting To You...... $DUSK ( $USDT )
2
12
12
·
--
Artikel
Lihat terjemahan
Binance Exchange Se Binance Web3 Wallet Me BNB Coin Kaise Transfer KareOpen Binance App (Log In ) GoTo ExchangeClick AssetsConvert Your $BNB In Spot (In Situation Your Fund In Other Wallet Then)Conform Your Assets In SpotGoto Home & Click Wallet (Uppar Side Show Exchange & Wallet)Check Are Your In Wallet Home. Then Click Receive Click Transfer From Binance ExchangeSelect BNBClick BNB Smart Chain (BEP20) (White Mark Show Then Choose)Click Continue Then Show Adress & Network Conform That.Enter Amount (How Much BNB)Click Transfer (Some Network Fees Cut In Your Amount & Other Amount Receive)Check All & Then Click ConformClick Verify Again (Use Your Passkey or Fingerprint Through Payment)Show In Display Withdrawal Processing & Also Showing Amount View History ? Goto Binance Wallet Click AnyOne Of That
or
GoTo Wallet Assets (Your Amount Showing There)
Binance Exchange Se Binance Web3 Wallet Me BNB Coin Kaise Transfer Kare
Open Binance App (Log In ) GoTo ExchangeClick AssetsConvert Your $BNB In Spot (In Situation Your Fund In Other Wallet Then)Conform Your Assets In SpotGoto Home & Click Wallet (Uppar Side Show Exchange & Wallet)Check Are Your In Wallet Home. Then Click Receive Click Transfer From Binance ExchangeSelect BNBClick BNB Smart Chain (BEP20) (White Mark Show Then Choose)Click Continue Then Show Adress & Network Conform That.Enter Amount (How Much BNB)Click Transfer (Some Network Fees Cut In Your Amount & Other Amount Receive)Check All & Then Click ConformClick Verify Again (Use Your Passkey or Fingerprint Through Payment)Show In Display Withdrawal Processing & Also Showing Amount View History ? Goto Binance Wallet Click AnyOne Of That
or
GoTo Wallet Assets (Your Amount Showing There)
or
GoTo Wallet Assets (Your Amount Showing There)
3
42
·
--
Artikel
Lihat terjemahan
New Offchain Computing Course with MarlinComplete the free course now on Binance Academy and share 2,000,000 POND in rewards.
1.How To Participate
2.Questions & Answers
3. Certificate
How To Participate Home => Notification ( Msg Inbox ) => [Marketing & Activities](https://www.binance.com/en/messages/v2/group/d14o5jb71n0jauledjq0) => Check Course related Topic Click There & Participate To [Learn & Earn](https://www.binance.com/en/academy/track/injective-the-layer-1-blockchain-built-for-finance).
Questions & Answers :-
1) What is the definition of "offchain computing"?
ANS :- Computation performed offchain, with results verified on-chain.
2) "Centralization concerns" and "Challenge periods" are "Cons" for which technology?
ANS :- Layer 2 scaling (rollups)
3) Which of the following is listed as a component of a coprocessor’s general architecture?
ANS :- Relay Contracts
4) How do we distinguish coprocessors from rollups?
ANS :- Rollups are described as sandboxed and "blockchain-esque," while coprocessors are compared to flexible VMs with attestations.
5) What "missing piece" in data protection does Confidential Computing address that Traditional Encryption leaves "Vulnerable"?
ANS :- Data "In Use"
6)What is the only primary "con" or disadvantage listed for TEE (Trusted Execution Environment) Coprocessors?
ANS :- Hardware vendor trust dependency
7) What is the primary goal of remote attestations?
ANS :- To verify that an attestation is valid, recent, and from a real enclave running a specific image.
8) Which TEE type is characterized by having "no persistent storage, external networking, or interactive access"?
ANS :- AWS Nitro Enclaves
9) According to the project overview, what is the primary reason for using Marlin's Oyster TEE coprocessors?
ANS :- To host verifiable AI (Llama 3.2) because blockchains cannot run AI and traditional APIs cannot be trusted.
10) What components are used to verify the TEE deployed AI's response onchain, as shown in the "Enclave Verification Data"?
ANS :- The "Oyster Signature" and the "Enclave Public Key".
11) According to the document, which computing model is characterized as "ephemeral," "stateless," and "event-driven"?
ANS :- Serverless Computing
12) Which of the following is listed as a "con" of using Confidential Virtual Machines (CVMs)?
ANS :- Upfront lease cost and longer cold start
13) What is the primary networking challenge associated with AWS Nitro Enclaves, and how does Oyster solve it?
ANS :- They only support vsock networking, so Oyster provides a simple IP interface to hide this complexity.
14)Which of the following is included in the checklist for verifying a decoded attestation document?
ANS :- Verify that the certificate chain's root is the AWS Nitro Enclaves Root certificate.
15)According to the document, what is the fundamental purpose of a Key Management System (KMS)?
ANS :- The lifecycle management of cryptographic keys, including their generation, storage, distribution, and rotation.
16) What is the core architectural difference between the Nautilus "Root Server" and "Derive Server"?
ANS :- The Root Server derives public keys (publicly), while the Derive Server derives private keys (inside the enclave).
17) Which of the following is listed as a key property of persistent storage in a TEE?
ANS :- Data persists across the enclave lifecycle and is cryptographically protected.
18) Which of the following is not a characteristic of "Contract-Based Persistent Storage"?
ANS :- It is a simple but rigid approach where the same code results in the same persistent keys.
19) What is the "Key Concept" of reproducible builds as defined in the document?
ANS :- Same source code + Same build environment = Identical binary output.
20) According to the document, what is the "gap" that Remote Attestation alone cannot solve, which reproducible builds address?
ANS :- Remote attestation verifies the binary (EIF) is running, but it doesn't prove what source code was used to create that binary.
21) What is the purpose of using npx pkg -t node18-alpine app.js in Step 2?
ANS :- To create a self-contained binary that runs without installing nodejs inside the enclave.
22) In Step 5, how is the deployed NodeJS server interacted with, and what is the expected response?
ANS :- By running curl <ip>:4000, expecting "Hello from Oyster Enclave!".
23) What is the primary security benefit of this decentralized frontend approach?
ANS :- It ensures that only enclaves running authorized images can request certificates for the domain, preventing tampering.
24) After fetching the subdomain, we have a waiting period of 4-5 minutes. What is happening during this time?
ANS :- The enclave is updating the DNS records.
25) In Step 3, what is the purpose of the --init-params ".env:1:1:file:./.env" flag in the oyster-cvm deploy command?
ANS :- To pass the environment variables file into the enclave during deployment.
26) How does a user interact with the deployed AI agent, according to Step 4?
ANS :- By running nc <Enclave_IP> 8080 and entering a prompt.
27) According to the "About the App" section, what is the primary role of the Marlin Oyster CVM enclave in this ZK-proof application?
ANS :- To secure the user's private inputs (age, BMI) so they cannot be leaked.
28) After deploying the server to a Marlin Oyster CVM, what command is used to perform a remote attestation to verify the enclave itself?
ANS :- oyster-cvm verify --enclave-ip <ip>
29) Where does the user go to deploy the minified JavaScript function for the Marlin Oyster Serverless service?
ANS :- They navigate to https://hub.marlin.org/oyster/serverless-sandbox/.
30) How is the deployed Marlin Oyster serverless function linked to the EthRate.sol smart contract before deployment?
ANS :- The "transaction hash" (codeHash) from the serverless deployment is added to the script/deploy/EthRate.ts file.
Certificate :-
New Offchain Computing Course with Marlin
Complete the free course now on Binance Academy and share 2,000,000 POND in rewards.
1.How To Participate
2.Questions & Answers
3. Certificate
How To Participate Home => Notification ( Msg Inbox ) => Marketing & Activities => Check Course related Topic Click There & Participate To Learn & Earn.
Questions & Answers :-
1) What is the definition of "offchain computing"?
ANS :- Computation performed offchain, with results verified on-chain.
2) "Centralization concerns" and "Challenge periods" are "Cons" for which technology?
ANS :- Layer 2 scaling (rollups)
3) Which of the following is listed as a component of a coprocessor’s general architecture?
ANS :- Relay Contracts
4) How do we distinguish coprocessors from rollups?
ANS :- Rollups are described as sandboxed and "blockchain-esque," while coprocessors are compared to flexible VMs with attestations.
5) What "missing piece" in data protection does Confidential Computing address that Traditional Encryption leaves "Vulnerable"?
ANS :- Data "In Use"
6)What is the only primary "con" or disadvantage listed for TEE (Trusted Execution Environment) Coprocessors?
ANS :- Hardware vendor trust dependency
7) What is the primary goal of remote attestations?
ANS :- To verify that an attestation is valid, recent, and from a real enclave running a specific image.
8) Which TEE type is characterized by having "no persistent storage, external networking, or interactive access"?
ANS :- AWS Nitro Enclaves
9) According to the project overview, what is the primary reason for using Marlin's Oyster TEE coprocessors?
ANS :- To host verifiable AI (Llama 3.2) because blockchains cannot run AI and traditional APIs cannot be trusted.
10) What components are used to verify the TEE deployed AI's response onchain, as shown in the "Enclave Verification Data"?
ANS :- The "Oyster Signature" and the "Enclave Public Key".
11) According to the document, which computing model is characterized as "ephemeral," "stateless," and "event-driven"?
ANS :- Serverless Computing
12) Which of the following is listed as a "con" of using Confidential Virtual Machines (CVMs)?
ANS :- Upfront lease cost and longer cold start
13) What is the primary networking challenge associated with AWS Nitro Enclaves, and how does Oyster solve it?
ANS :- They only support vsock networking, so Oyster provides a simple IP interface to hide this complexity.
14)Which of the following is included in the checklist for verifying a decoded attestation document?
ANS :- Verify that the certificate chain's root is the AWS Nitro Enclaves Root certificate.
15)According to the document, what is the fundamental purpose of a Key Management System (KMS)?
ANS :- The lifecycle management of cryptographic keys, including their generation, storage, distribution, and rotation.
16) What is the core architectural difference between the Nautilus "Root Server" and "Derive Server"?
ANS :- The Root Server derives public keys (publicly), while the Derive Server derives private keys (inside the enclave).
17) Which of the following is listed as a key property of persistent storage in a TEE?
ANS :- Data persists across the enclave lifecycle and is cryptographically protected.
18) Which of the following is not a characteristic of "Contract-Based Persistent Storage"?
ANS :- It is a simple but rigid approach where the same code results in the same persistent keys.
19) What is the "Key Concept" of reproducible builds as defined in the document?
ANS :- Same source code + Same build environment = Identical binary output.
20) According to the document, what is the "gap" that Remote Attestation alone cannot solve, which reproducible builds address?
ANS :- Remote attestation verifies the binary (EIF) is running, but it doesn't prove what source code was used to create that binary.
21) What is the purpose of using npx pkg -t node18-alpine app.js in Step 2?
ANS :- To create a self-contained binary that runs without installing nodejs inside the enclave.
22) In Step 5, how is the deployed NodeJS server interacted with, and what is the expected response?
ANS :- By running curl <ip>:4000, expecting "Hello from Oyster Enclave!".
23) What is the primary security benefit of this decentralized frontend approach?
ANS :- It ensures that only enclaves running authorized images can request certificates for the domain, preventing tampering.
24) After fetching the subdomain, we have a waiting period of 4-5 minutes. What is happening during this time?
ANS :- The enclave is updating the DNS records.
25) In Step 3, what is the purpose of the --init-params ".env:1:1:file:./.env" flag in the oyster-cvm deploy command?
ANS :- To pass the environment variables file into the enclave during deployment.
26) How does a user interact with the deployed AI agent, according to Step 4?
ANS :- By running nc <Enclave_IP> 8080 and entering a prompt.
27) According to the "About the App" section, what is the primary role of the Marlin Oyster CVM enclave in this ZK-proof application?
ANS :- To secure the user's private inputs (age, BMI) so they cannot be leaked.
28) After deploying the server to a Marlin Oyster CVM, what command is used to perform a remote attestation to verify the enclave itself?
ANS :- oyster-cvm verify --enclave-ip <ip>
29) Where does the user go to deploy the minified JavaScript function for the Marlin Oyster Serverless service?
ANS :- They navigate to https://hub.marlin.org/oyster/serverless-sandbox/.
30) How is the deployed Marlin Oyster serverless function linked to the EthRate.sol smart contract before deployment?
ANS :- The "transaction hash" (codeHash) from the serverless deployment is added to the script/deploy/EthRate.ts file.
Certificate :-
1.How To Participate
2.Questions & Answers
3. Certificate
How To Participate Home => Notification ( Msg Inbox ) => Marketing & Activities => Check Course related Topic Click There & Participate To Learn & Earn.
Questions & Answers :-
1) What is the definition of "offchain computing"?
ANS :- Computation performed offchain, with results verified on-chain.
2) "Centralization concerns" and "Challenge periods" are "Cons" for which technology?
ANS :- Layer 2 scaling (rollups)
3) Which of the following is listed as a component of a coprocessor’s general architecture?
ANS :- Relay Contracts
4) How do we distinguish coprocessors from rollups?
ANS :- Rollups are described as sandboxed and "blockchain-esque," while coprocessors are compared to flexible VMs with attestations.
5) What "missing piece" in data protection does Confidential Computing address that Traditional Encryption leaves "Vulnerable"?
ANS :- Data "In Use"
6)What is the only primary "con" or disadvantage listed for TEE (Trusted Execution Environment) Coprocessors?
ANS :- Hardware vendor trust dependency
7) What is the primary goal of remote attestations?
ANS :- To verify that an attestation is valid, recent, and from a real enclave running a specific image.
8) Which TEE type is characterized by having "no persistent storage, external networking, or interactive access"?
ANS :- AWS Nitro Enclaves
9) According to the project overview, what is the primary reason for using Marlin's Oyster TEE coprocessors?
ANS :- To host verifiable AI (Llama 3.2) because blockchains cannot run AI and traditional APIs cannot be trusted.
10) What components are used to verify the TEE deployed AI's response onchain, as shown in the "Enclave Verification Data"?
ANS :- The "Oyster Signature" and the "Enclave Public Key".
11) According to the document, which computing model is characterized as "ephemeral," "stateless," and "event-driven"?
ANS :- Serverless Computing
12) Which of the following is listed as a "con" of using Confidential Virtual Machines (CVMs)?
ANS :- Upfront lease cost and longer cold start
13) What is the primary networking challenge associated with AWS Nitro Enclaves, and how does Oyster solve it?
ANS :- They only support vsock networking, so Oyster provides a simple IP interface to hide this complexity.
14)Which of the following is included in the checklist for verifying a decoded attestation document?
ANS :- Verify that the certificate chain's root is the AWS Nitro Enclaves Root certificate.
15)According to the document, what is the fundamental purpose of a Key Management System (KMS)?
ANS :- The lifecycle management of cryptographic keys, including their generation, storage, distribution, and rotation.
16) What is the core architectural difference between the Nautilus "Root Server" and "Derive Server"?
ANS :- The Root Server derives public keys (publicly), while the Derive Server derives private keys (inside the enclave).
17) Which of the following is listed as a key property of persistent storage in a TEE?
ANS :- Data persists across the enclave lifecycle and is cryptographically protected.
18) Which of the following is not a characteristic of "Contract-Based Persistent Storage"?
ANS :- It is a simple but rigid approach where the same code results in the same persistent keys.
19) What is the "Key Concept" of reproducible builds as defined in the document?
ANS :- Same source code + Same build environment = Identical binary output.
20) According to the document, what is the "gap" that Remote Attestation alone cannot solve, which reproducible builds address?
ANS :- Remote attestation verifies the binary (EIF) is running, but it doesn't prove what source code was used to create that binary.
21) What is the purpose of using npx pkg -t node18-alpine app.js in Step 2?
ANS :- To create a self-contained binary that runs without installing nodejs inside the enclave.
22) In Step 5, how is the deployed NodeJS server interacted with, and what is the expected response?
ANS :- By running curl <ip>:4000, expecting "Hello from Oyster Enclave!".
23) What is the primary security benefit of this decentralized frontend approach?
ANS :- It ensures that only enclaves running authorized images can request certificates for the domain, preventing tampering.
24) After fetching the subdomain, we have a waiting period of 4-5 minutes. What is happening during this time?
ANS :- The enclave is updating the DNS records.
25) In Step 3, what is the purpose of the --init-params ".env:1:1:file:./.env" flag in the oyster-cvm deploy command?
ANS :- To pass the environment variables file into the enclave during deployment.
26) How does a user interact with the deployed AI agent, according to Step 4?
ANS :- By running nc <Enclave_IP> 8080 and entering a prompt.
27) According to the "About the App" section, what is the primary role of the Marlin Oyster CVM enclave in this ZK-proof application?
ANS :- To secure the user's private inputs (age, BMI) so they cannot be leaked.
28) After deploying the server to a Marlin Oyster CVM, what command is used to perform a remote attestation to verify the enclave itself?
ANS :- oyster-cvm verify --enclave-ip <ip>
29) Where does the user go to deploy the minified JavaScript function for the Marlin Oyster Serverless service?
ANS :- They navigate to https://hub.marlin.org/oyster/serverless-sandbox/.
30) How is the deployed Marlin Oyster serverless function linked to the EthRate.sol smart contract before deployment?
ANS :- The "transaction hash" (codeHash) from the serverless deployment is added to the script/deploy/EthRate.ts file.
Certificate :-
2
9
9
·
--
Artikel
Lihat terjemahan
Red Packet Giveaway[Free Red Packet](https://app.binance.com/uni-qr/RtAtCQwm?utm_medium=web_share_copy)
Click [Claim](https://app.binance.com/uni-qr/RtAtCQwm?utm_medium=web_share_copy) Button to Claim Your Free Reward. & Share To Your Friend For Free Reward & Also More Extra Reward Waiting To You......
Red Packet Giveaway
Free Red Packet
Click Claim Button to Claim Your Free Reward. & Share To Your Friend For Free Reward & Also More Extra Reward Waiting To You......
Click Claim Button to Claim Your Free Reward. & Share To Your Friend For Free Reward & Also More Extra Reward Waiting To You......
7
22
·
--
Artikel
Kursus Baru dengan Injective Belajar & DapatkanSelesaikan kursus gratis sekarang di Binance Academy dan dapatkan bagian Anda dari INJ selama minggu peluncuran.
Bergabunglah dengan Studi Kursus Pertama & Selesaikan Jawaban Kuis yang Diberikan & Klaim Sertifikat & Juga Beberapa Saham Dari Injective.
Klik kata Injective & Bergabung :- [Injective](https://www.binance.com/en/academy/track/injective-the-layer-1-blockchain-built-for-finance)
Bab 1. Jawaban
Bab 2. Jawaban
Kursus Baru dengan Injective Belajar & Dapatkan
Selesaikan kursus gratis sekarang di Binance Academy dan dapatkan bagian Anda dari INJ selama minggu peluncuran.
Bergabunglah dengan Studi Kursus Pertama & Selesaikan Jawaban Kuis yang Diberikan & Klaim Sertifikat & Juga Beberapa Saham Dari Injective.
Klik kata Injective & Bergabung :- Injective
Bab 1. Jawaban
Bab 2. Jawaban
Bergabunglah dengan Studi Kursus Pertama & Selesaikan Jawaban Kuis yang Diberikan & Klaim Sertifikat & Juga Beberapa Saham Dari Injective.
Klik kata Injective & Bergabung :- Injective
Bab 1. Jawaban
Bab 2. Jawaban
2
5
Masuk untuk menjelajahi konten lainnya
Bergabunglah dengan pengguna kripto global di Binance Square
⚡️ Dapatkan informasi terbaru dan berguna tentang kripto.
💬 Dipercayai oleh bursa kripto terbesar di dunia.
👍 Temukan wawasan nyata dari kreator terverifikasi.
Email/Nomor Ponsel
Topik Sedang Tren
FedRateWatch
1.5M penayangan
6,726 Berdiskusi
Bagikan & Menangkan Reward Traffic di Kampanye Hashtag Tren kami
✨Topik: FOMC September, Apa Langkah Berikutnya The Fed?
👉Cara Bergabung:
Publikasikan postingan atau artikel singkat dengan hashtag #FedRateWatch
Buat konten berdasarkan sudut pandang di bawah ini:
- CPI inti bulan Agustus naik 0,3% secara month-over-month, dan peluang kenaikan 25bp minggu ini kini mendekati 90%. Apakah Anda memperkirakan akan ada kenaikan suku bunga minggu ini? Apakah ini hanya satu kali, atau awal dari siklus kenaikan yang lebih panjang?
- Jika kenaikan itu terjadi, bagaimana dampaknya bagi BTC, saham teknologi, dan emas? Bullish atau bearish?
- Rencana Anda untuk trading berikutnya seperti apa? Bagikan trading/saham/holdings BTC, saham, atau emas Anda dengan widget berbagi trading kami.
⏰Periode Kampanye:
- 2026-09-15 11:00 - 2026-09-17 3:00 UTC
🎁Hadiah:
- Postingan yang memenuhi syarat sesuai pedoman di atas dan berisi lebih dari 100 kata akan ditinjau serta dapat menerima peningkatan traffic acak sebesar 500 hingga 3.000 views. Anda akan menerima notifikasi dari sekretaris feed jika postingan Anda dipilih.
- Dapatkan kesempatan agar artikel Anda ditampilkan di Binance Square Official
Butuh ide untuk postingan Anda? Kunjungi halaman topik #FedRateWatch atau Square Guide on How to Post for Better Reach.
Binance Square Official
·Disukai 648 Kali
·1.7M penayangan
ZcashRises6%
51,889 penayangan
653 Berdiskusi
XRPSinks10%
34,833 penayangan
428 Berdiskusi