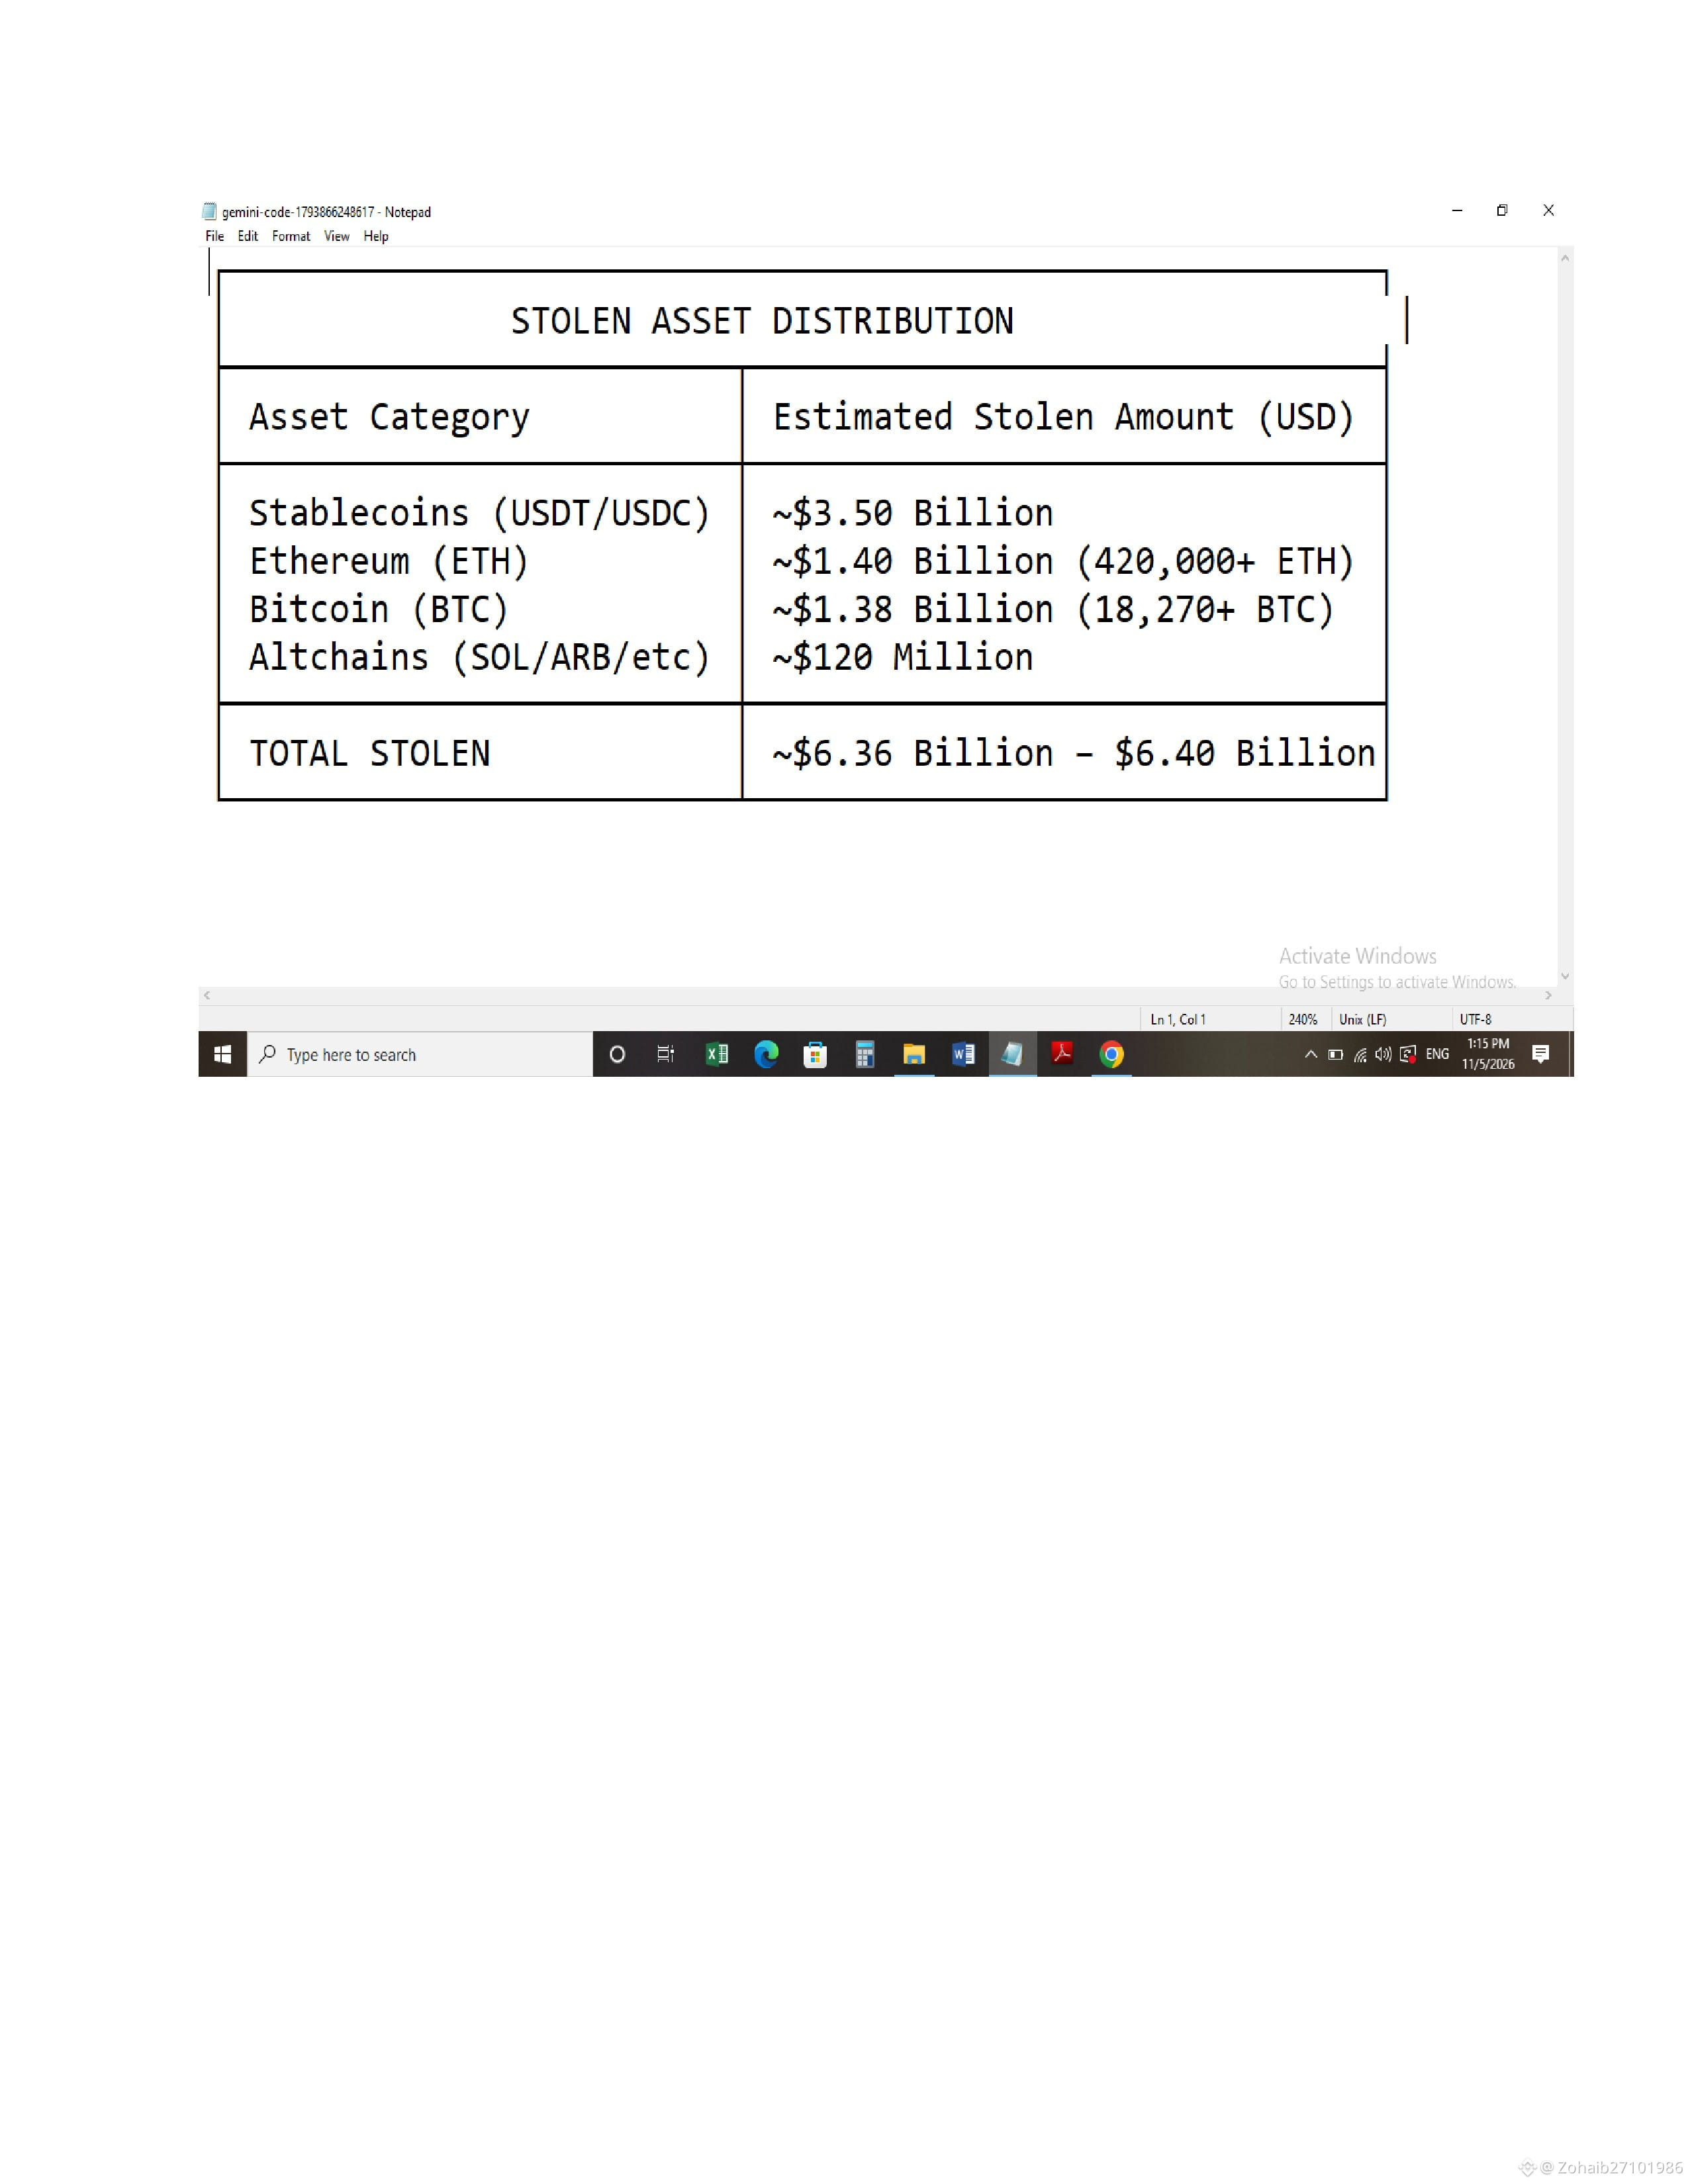
On October 29, 2026 (at ~20:05 UTC), Binance suffered the single largest security breach in cryptocurrency history. Attackers managed to drain approximately $6.36 Billion to $6.4 Billion worth of digital assets across 10 different blockchain networks in a high-speed, coordinated maneuver that took less than 20 minutes.
Chainalysis, TRM Labs, and the FBI attributed the attack with high confidence to TraderTraitor (a elite North Korean state-sponsored unit under the Lazarus umbrella).
⚙️ How Binance Was Hacked (Technical Breakdown)
The hack relied on a hybrid attack combining employee workstation intrusion, hot wallet infrastructure exploits, and advance-configured smart contract delegation.
Station Intrusion & Infrastructure Breach:
Attackers initially infiltrated a Binance engineer's workstation/laptop via malicious malware designed to wipe its own trace.
Subsequent investigations revealed additional intrusion vectors that compromised Binance's automated hot-wallet signing infrastructure (private keys themselves were not leaked directly).
The EIP-7702 Exploitation (Ethereum Sweeper):
On Ethereum, attackers used pre-signed EIP-7702 authorizations prepared weeks in advance.
They converted a main Binance hot wallet into a sweeper contract that only the attacker's master address could execute.
This instantly swept funds currently in the wallet and automatically redirected any incoming deposits in real-time.
Multi-Chain Rapid Siphon:
Concurrently across 9 other chains (Tron, Solana, Arbitrum, BSC, Optimism, Base, Polygon, Avalanche, etc.), automated signed transfers pulled assets out simultaneously.
Within 2 minutes, over $612 Million in USDT was moved off Tron alone.
#BitcoinETFs #CryptocurrencyWealth #USDT🔥🔥🔥
💰 Value Breakdown & What Was Stolen
Chainalysis, TRM Labs, and the FBI attributed the attack with high confidence to TraderTraitor (a elite North Korean state-sponsored unit under the Lazarus umbrella).
⚙️ How Binance Was Hacked (Technical Breakdown)
The hack relied on a hybrid attack combining employee workstation intrusion, hot wallet infrastructure exploits, and advance-configured smart contract delegation.
Station Intrusion & Infrastructure Breach:
Attackers initially infiltrated a Binance engineer's workstation/laptop via malicious malware designed to wipe its own trace.
Subsequent investigations revealed additional intrusion vectors that compromised Binance's automated hot-wallet signing infrastructure (private keys themselves were not leaked directly).
The EIP-7702 Exploitation (Ethereum Sweeper):
On Ethereum, attackers used pre-signed EIP-7702 authorizations prepared weeks in advance.
They converted a main Binance hot wallet into a sweeper contract that only the attacker's master address could execute.
This instantly swept funds currently in the wallet and automatically redirected any incoming deposits in real-time.
Multi-Chain Rapid Siphon:
Concurrently across 9 other chains (Tron, Solana, Arbitrum, BSC, Optimism, Base, Polygon, Avalanche, etc.), automated signed transfers pulled assets out simultaneously.
Within 2 minutes, over $612 Million in USDT was moved off Tron alone.
#BitcoinETFs #CryptocurrencyWealth #USDT🔥🔥🔥
💰 Value Breakdown & What Was Stolen