Imagine discovering that a blockchain’s payment system contained a flaw capable of creating new coins beyond its intended supply.
That’s what XRP Ledger developers disclosed on October 9.
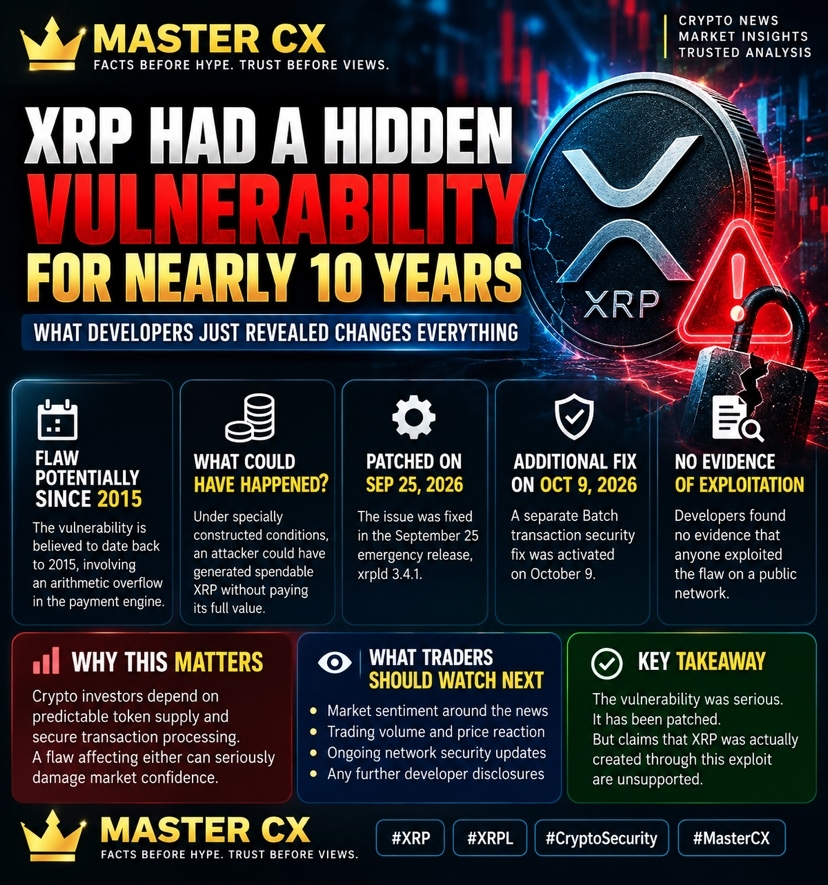
The vulnerability, believed to date back to 2015, involved an arithmetic overflow in the payment engine. Under specially constructed conditions, an attacker could have generated spendable XRP without paying its full value.
The important part: Developers found no evidence that anyone exploited the flaw on a public network.
The vulnerability was fixed in the September 25 emergency release, xrpld 3.4.1. A separate Batch transaction security fix activated on October 9.
Why does this matter?
Crypto investors depend on predictable token supply and secure transaction processing. A flaw affecting either can seriously damage market confidence.For XRP traders, the next thing to watch is whether the disclosure affects market sentiment, trading volume or confidence in network security.The patch is confirmed. The vulnerability was serious. But claims that XRP was actually created through this exploit are unsupported.
👑 MASTER CX | Facts Before Hype. Trust Before Views.