
#OPTIMJACKAttackInfectsAtLeast186Websites
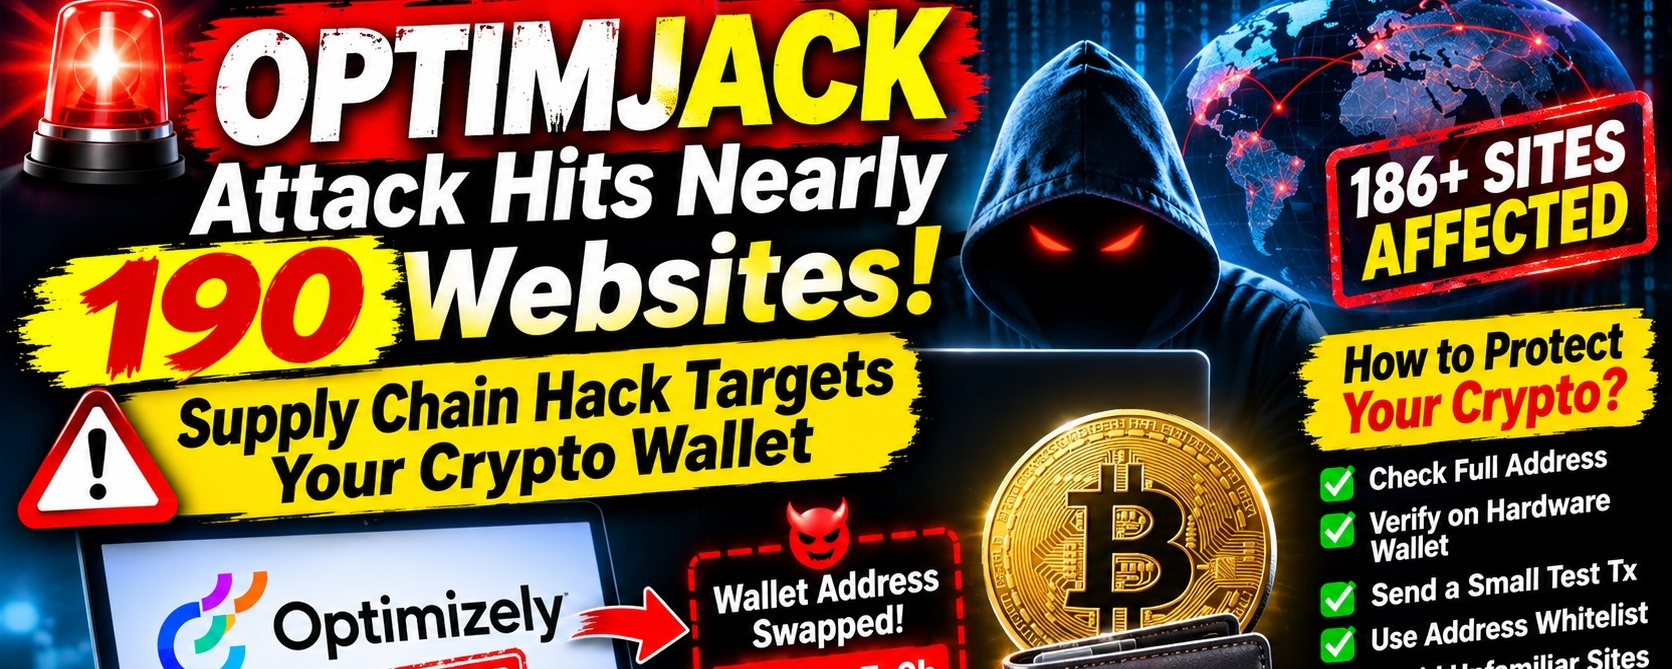
One of the biggest web security incidents of the year is still unfolding. 😱 A supply chain attack dubbed **OPTIMJACK** reportedly compromised **Optimizely**, an A/B testing platform used by many major websites. Attackers injected malicious JavaScript that can swap crypto wallet addresses and steal payment card data. 🧨 Here is what we know, what we don't, and how to protect yourself. 🛡️
## 🧩 What Happened?
According to reports, attackers injected malicious code into scripts served through Optimizely. 🌐 Security researcher Scott Helme reported **at least 186 infected websites** and warned the attack was still active. Other trackers cite slightly different counts, roughly **178 to 188 sites**, so treat the exact number as a moving target. 📊
- 🕓 The campaign reportedly began around **4:21 a.m. UTC on Monday, November 16, 2026**.
- 🏢 Affected sites reportedly include **CNN, Zoom, Fox News, BBC, Salesforce, GitLab, American Eagle and Hootsuite**. Finance and crypto-related sites such as Ledger, OANDA and IG were also named in some reports.
- 🕵️ The activity was named "OPTIMJACK" by independent researcher Amirul Iman.
## 💀 What Does the Malicious Code Do?
Researchers say the payload was built for theft. 🎯
1. 📋 **Crypto clipper:** When you copy a wallet address, the script can secretly replace it with the attacker's address. If you paste without checking, your funds go to a scammer. 💸
2. 💳 **Card skimming:** It can capture payment card details typed into website forms.
3. 🍪 **Data collection:** Some analysis mentions stolen screenshots and cookies.
4. 📱 **Mobile loaders:** One report says the code also included loaders aimed at Apple devices.
The code reportedly includes checks such as checksum and Luhn validation, which help it recognize real wallet addresses and card numbers. 🧠
## 🔎 How Could This Happen?
Many websites load scripts from third-party vendors for analytics, testing or ads. 🧱 Those scripts run with the same power as the site's own code. If a vendor's script is poisoned, every site that loads it may serve the malware to visitors. That is why it's called a **supply chain attack**. 🔗
Reports say the malicious JavaScript was inserted into Optimizely project files, and one report claims an unauthorized party exploited a weakness in the account signup flow. 🕳️ These details are still being investigated, so treat them as preliminary. 🔬
## 🧪 Why Many Sites Were Exposed
Security testing after the attack found that a strict **Content Security Policy (CSP)** can block this kind of payload. 🛑 But of 256 hosts tested, **68 had no CSP at all, 50 had one that still allowed the attack, and only 24 blocked it**. That shows how rarely this defense is set up correctly. ⚠️
## 🛡️ How to Protect Your Crypto
The viral post gives some good starting advice, but you can do more. 💪
1. 👀 **Check the whole address, not just the first and last characters.** Attackers often generate lookalike addresses that match the start and end. Compare every character, or use a copy of the address you saved safely beforehand.
2. 🔐 **Verify on your hardware wallet screen.** A hardware wallet protects you only if you confirm the destination address shown *on the device itself*, not on the website.
3. 🧪 **Send a small test transaction first** for large transfers. 💵
4. 📒 **Use an address book or whitelist** on exchanges and wallets for trusted addresses.
5. 🚫 **Avoid crypto transactions on unfamiliar sites** or browsers while the campaign is active.
6. 🌐 **Use a clean browser profile.** Disable unneeded extensions and consider a dedicated browser for crypto only.
7. 💳 **Watch your cards.** Review bank statements, and contact your bank if you entered card details on an affected site.
8. 🧹 **Clear cache and update your browser and operating system.**
## 🏢 Advice for Website Owners
- 🧱 Set up a **strict Content Security Policy** and test that it actually blocks unauthorized scripts.
- 🔏 Use **Subresource Integrity (SRI)** where possible.
- 📋 Audit every third-party script and remove ones you don't need.
- 🔑 Lock down vendor accounts with strong authentication and limit who can edit scripts.
- 🕵️ Monitor for unexpected changes in third-party code.
## 🌍 Why This Matters Beyond Crypto
OPTIMJACK is a reminder that **one compromised vendor can affect hundreds of trusted brands at once**. 🏗️ Even careful users can be exposed when a normal, well-known website serves a poisoned script. Crypto users are especially at risk, because blockchain transfers are **irreversible**. Once the money is sent to the wrong address, it is almost impossible to recover. ⛓️
## 🎯 Final Thoughts
The investigation is still ongoing, and numbers and technical details may change as researchers learn more. 🔄 Until the situation is clear, treat every copied wallet address with suspicion and verify it carefully before you send funds. A few extra seconds can save your entire balance. ⏱️💰 Stay alert, stay skeptical and keep your security habits sharp. 🧠🔐
*⚠️
**** #OPTIMJACK #CryptoSecurity #SupplyChainAttack #WalletSecurity #Web3Safety
#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal?