#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 Keystone Wallet Breach: Your Crypto May Be Safe, but Your Privacy Is at Risk
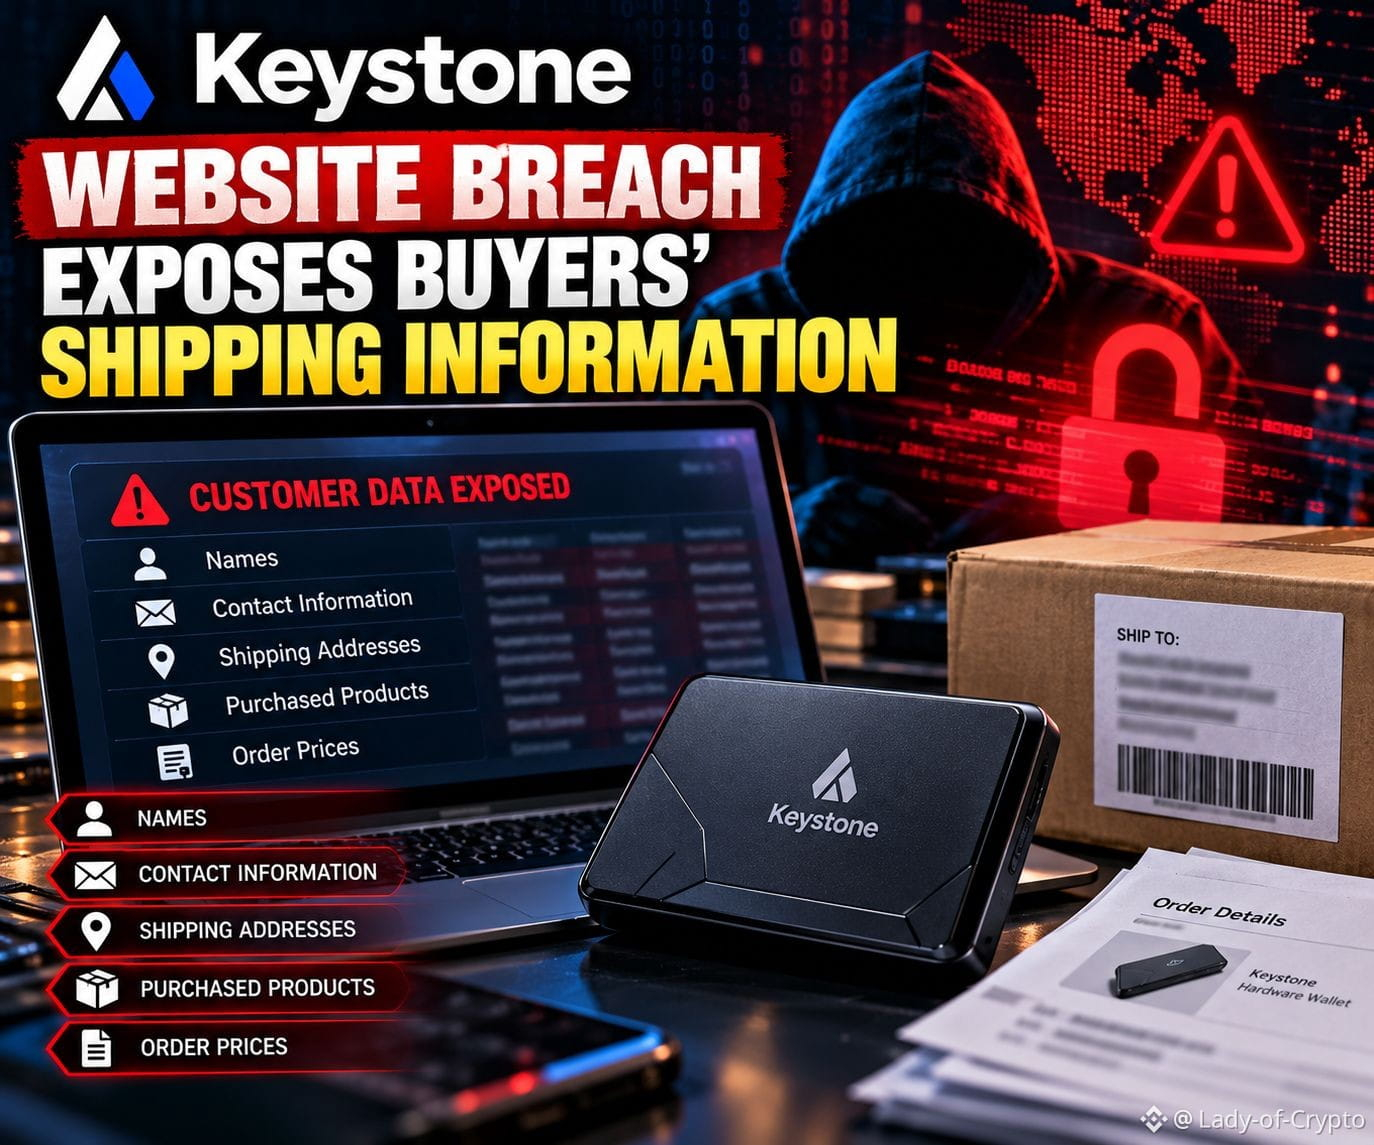
Keystone, a crypto hardware wallet manufacturer, has disclosed a website breach that exposed customer names, contact details, shipping addresses, and purchase records. The company confirmed unauthorized access on October 23, 2026, after investigating suspicious activity linked to its online store.
🔎 What Was Exposed?
• Customer names and contact information
• Shipping addresses
• Purchased products and order prices
Keystone says payment details, passwords, private keys, and recovery phrases were not exposed. The incident concerns customer records, not a confirmed compromise of users’ wallet keys.
⚠️ Why Should Crypto Holders Care?
A leaked address linked to a hardware wallet purchase can make someone a more attractive target for personalized phishing and impersonation scams. Attackers may pose as company support, offer fake replacement devices, or claim that funds need to be secured urgently.
The company says it has blocked unauthorized access, fixed the vulnerability, and begun notifying affected customers. The total number impacted has not yet been disclosed.
🛡️ What Users Should Do:
✅ Never share your recovery phrase or private keys.
✅ Ignore unsolicited recovery, refund, or replacement offers.
✅ Avoid suspicious links, even if messages include real order details.
✅ Verify communications through official channels.
The bigger lesson is that self-custody involves more than securing private keys. Protecting personal information matters too.
A hardware wallet can protect access to your assets, but it cannot prevent every scam targeting its owner.
💬 Should crypto companies be held to stricter data-retention and customer privacy standards?
#CryptoSecurity #KeystoneWallet #Bitcoin #CyberSecurity #BinanceSquare
$NIL $ENA $REZ