


Google latest quantum computing technique reportedly cuts relevant error rates by a factor of 40 and reaches 99.9% accuracy, advancing a field whose eventual capabilities could threaten Bitcoin cryptography. However, the result addresses quantum error, which Google’s method still needs to be demonstrated at a larger scale.
This leaves the immediate network threat unchanged, while making the longer-term Bitcoin quantum risk harder to dismiss as a purely theoretical engineering problem. The gap is narrowing, but it remains substantial.
 JUST IN: Google may bring Bitcoin’s Q-Day sooner than expected after its Willow chip cuts quantum errors 40x.
Google says a technique called “magic state cultivation” now works on its Willow chip, cutting errors about 40x with a record 99.99% accuracy.
Q-Day is the moment a… pic.twitter.com/6fquMJURPH
— Coin Bureau (@coinbureau) October 15, 2026
Google’s research targets magic states, a specialized resource used in quantum computation that the primary report says typically consumes about 95% of a quantum computer’s capacity. Improving the reliability and production of those states could ease a major bottleneck in building larger, more useful machines.
Quantum error correction is necessary for a sufficiently powerful fault-tolerant system, but the Bitcoin threat depends on many demanding capabilities working together. The milestone strengthens the case for long-term preparation.
Earn $50 and Enter $300K Prize Draw on EdgeXHow Far Away is Bitcoin Quantum Attack According to Google?
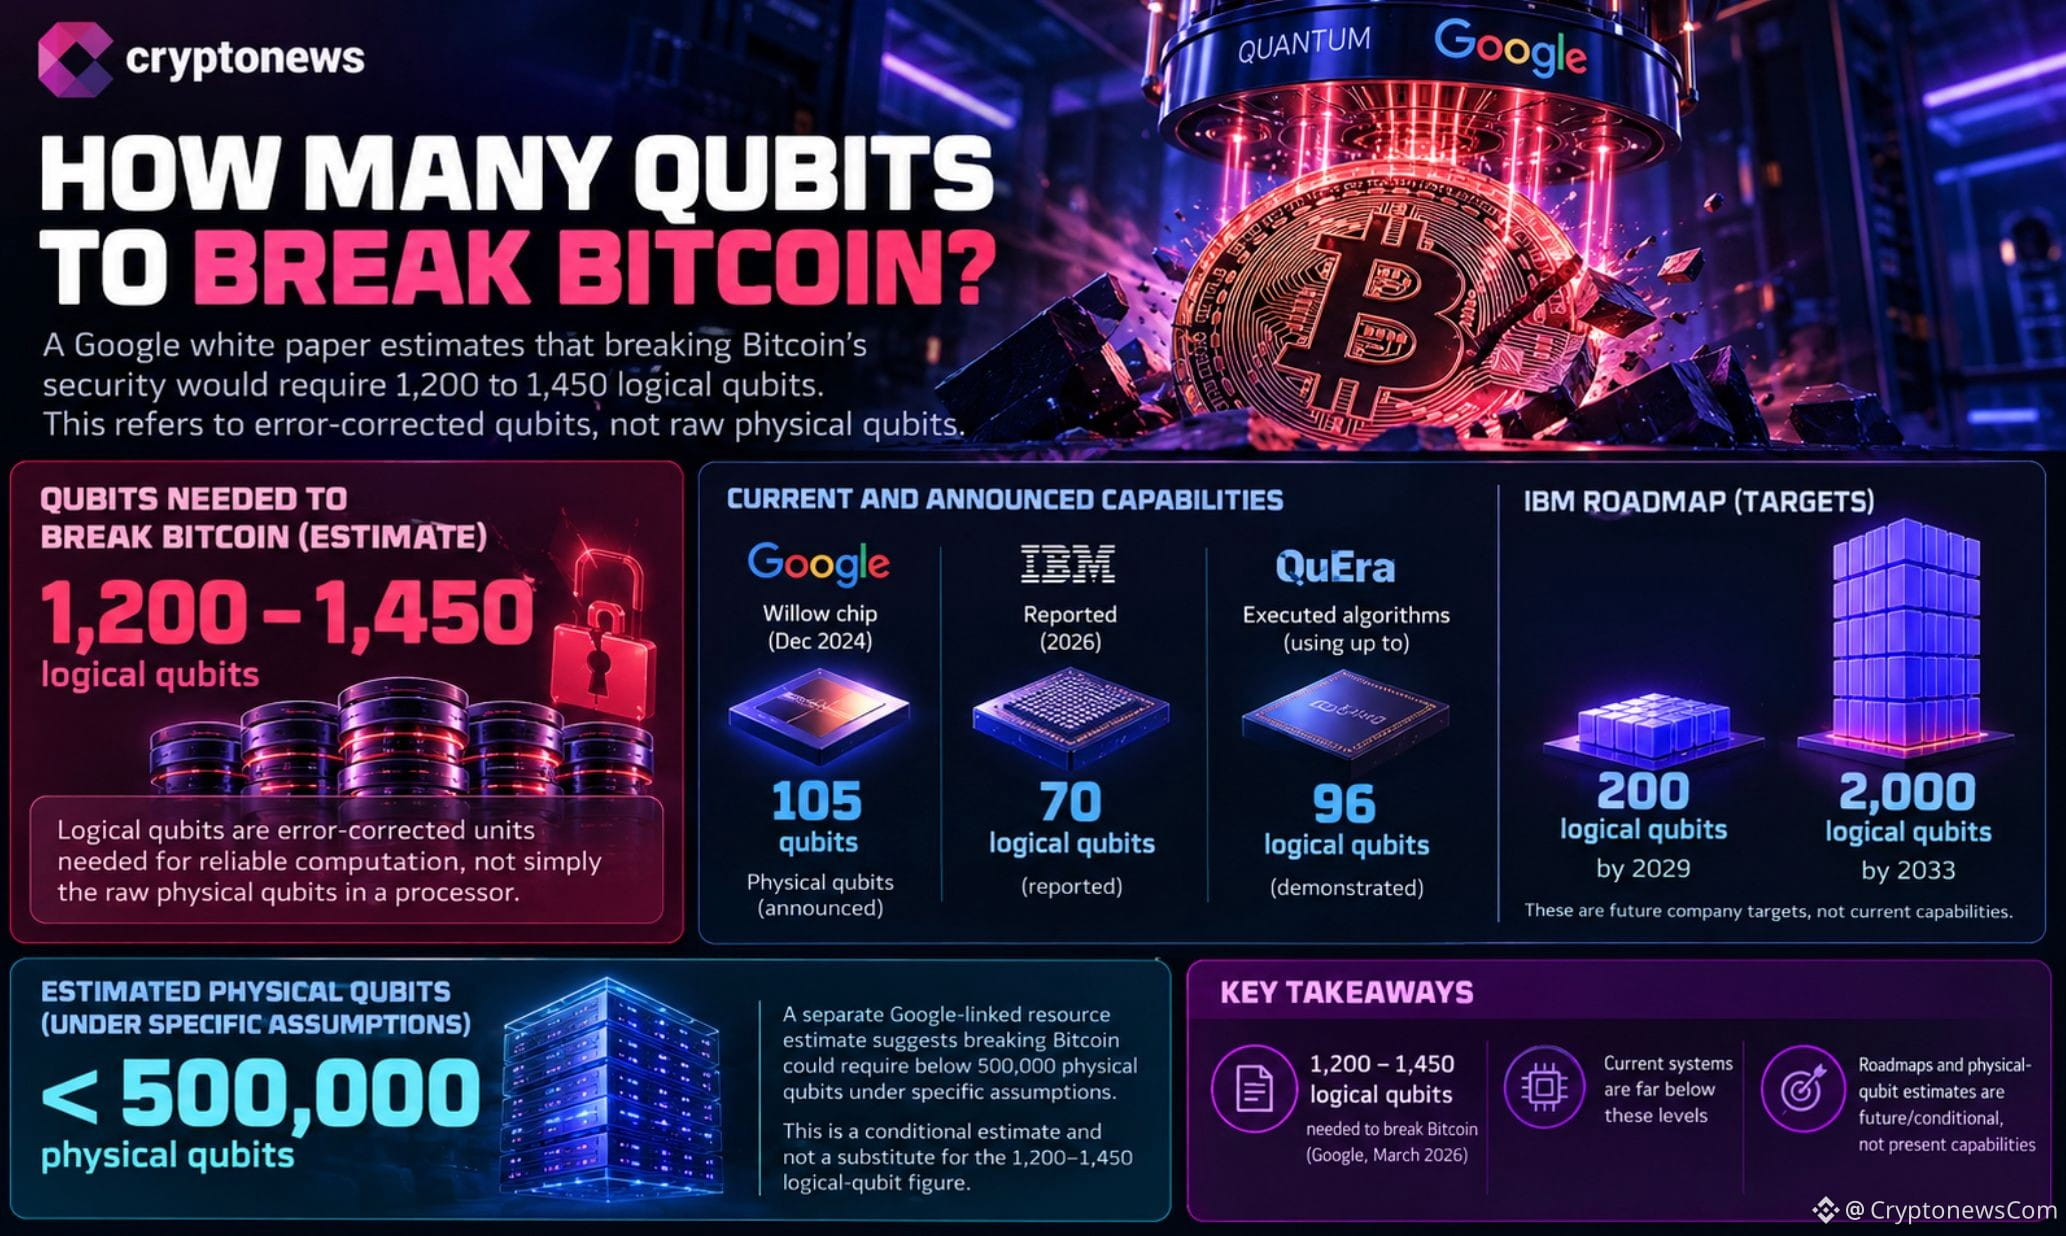
A Google white paper published in March estimated that breaking Bitcoin’s security would require 1,200 to 1,450 logical qubits. These are logical qubits, the error-corrected units needed for reliable computation, not simply the raw physical qubits installed in a processor.
Google’s Willow chip, announced in December 2024, has 105 qubits; IBM reported 70 logical qubits, while QuEra had executed algorithms using up to 96 logical qubits. IBM’s roadmap targeted 200 logical qubits by 2029 and 2,000 by 2033, making the roadmap a future company target rather than a present capability.
A separate Google-linked resource estimate discussed in other reporting puts the requirement below 500,000 physical qubits under specific assumptions. That conditional physical-qubit estimate is not a substitute for the 1,200–1,450 logical-qubit figure.
Likewise, a scenario in which an advanced machine could derive a private key from an exposed public key in nine minutes describes a hypothetical attack capability, not a machine that currently exists.
The practical exposure would also depend on whether a public key is revealed. A Google analysis of quantum vulnerabilities in cryptocurrency addresses the broader risk, while Bitcoin’s eventual response would require a technically sound migration path and coordination across users, developers and custodians.
Trade XRP on Bybit and Get a Chance to Win Our $1,000 USDT AirdropA Long-Horizon Security Issue
The primary report estimates that about 6.26 million BTC sits in quantum-vulnerable addresses. The risk is conditional on future machines becoming capable of deriving private keys from exposed public keys. Bitcoin’s long-term security debate concerns both the strength of future quantum hardware and the ability to move affected funds to safer arrangements.
Jameson Lopp, Casa’s co-founder and chief security officer, says that a machine powerful enough to decode a Bitcoin public key could be at least another decade away. Google’s error-correction progress reinforces why the issue deserves planning.
As of today, Polymarket assigned a 1% chance to the relevant possibility by year-end and 11% by the end of 2027, as reported in the source article. The more durable implication is that Bitcoin’s post-quantum migration challenge needs to be considered well before a credible attack-capable machine appears.
For BTC positioning, Google’s result does not establish an immediate security event or a standalone sell signal. It does add weight to the long-dated tail risk: error correction is advancing, but the leap from a laboratory milestone to a reliable Bitcoin-breaking system still requires scale, fault tolerance, and sustained computation that current machines have not demonstrated.
Discover: The Best Token Presales
The post Google Quantum 40x Breakthrough Rekindles Fears of Q-Day appeared first on Cryptonews.