
Harmony’s ONE token recently faced a major security incident.
On August 12, Harmony confirmed that attackers had exploited a vulnerability in its cross-shard receipt verification system, allowing previously processed receipts to be replayed and used to create unauthorized ONE tokens.
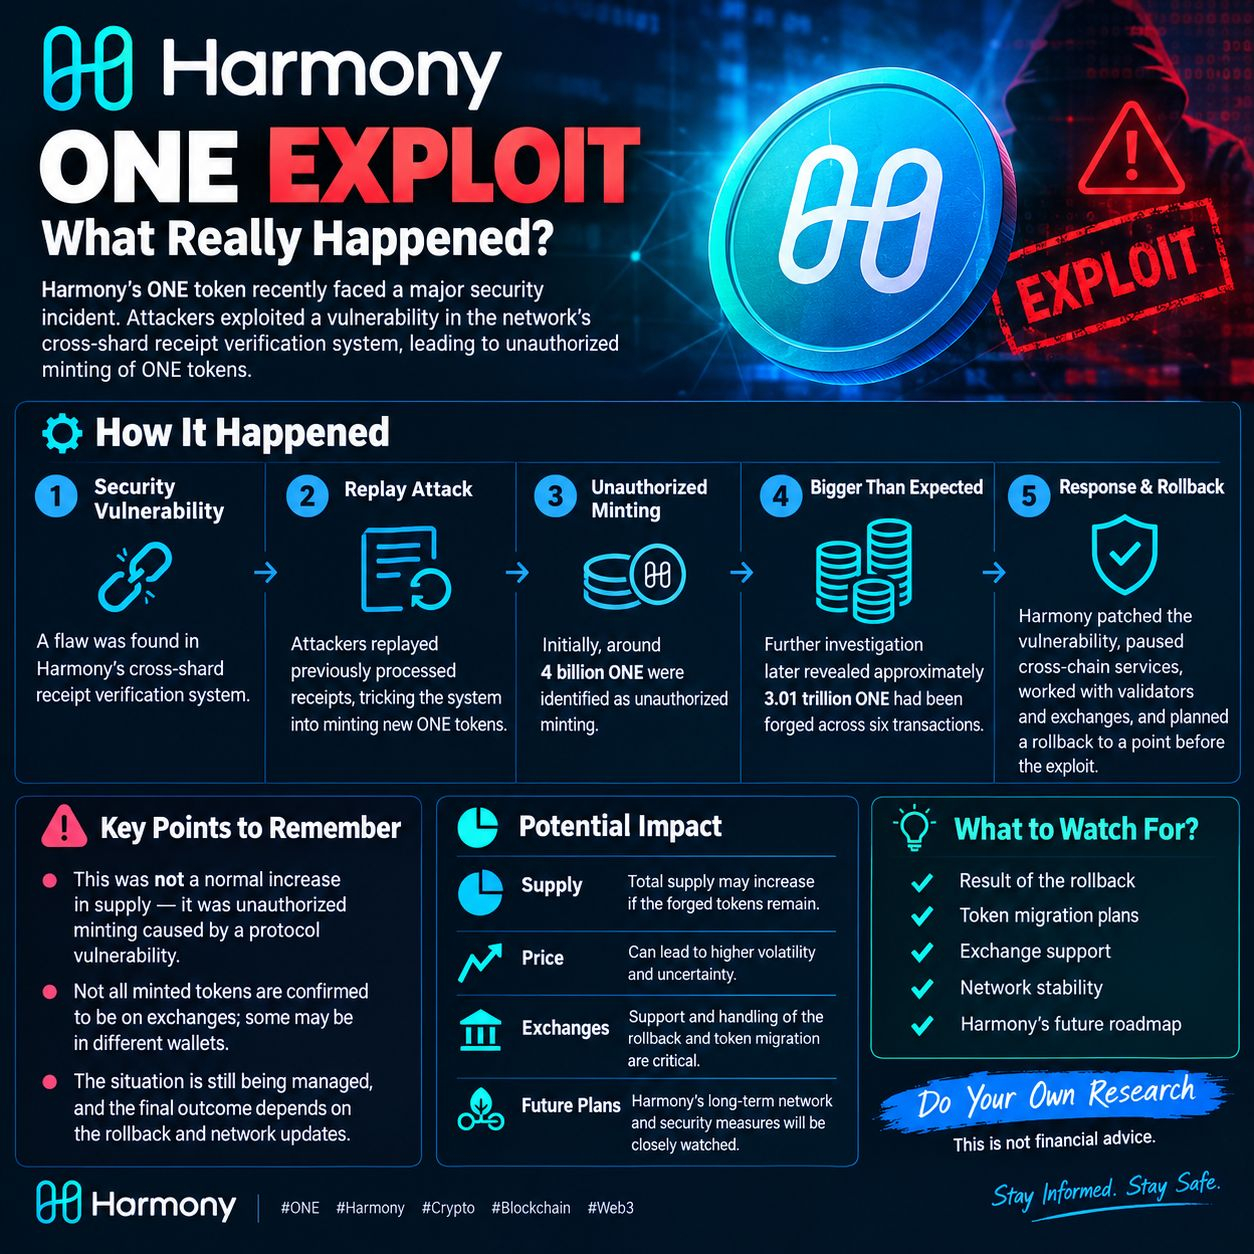 $
🔹 Initial discovery: Around 4 billion ONE were identified as unauthorized minting.
🔹 Later investigation: Harmony reconstructed the incident and found approximately 3.01 trillion ONE had been forged across six transactions.
🔹 Response: Harmony patched the vulnerability, paused cross-chain services and worked with validators and exchanges.
🔹 Rollback: Harmony subsequently planned a rollback to a point before the exploit to remove the forged state.
⚠️ Important: This was not simply a normal increase in supply. It was an unauthorized minting event caused by a protocol vulnerability.
For anyone following $ONE, the key things to watch are the rollback outcome, token migration plans, exchange support, and Harmony’s future network plans.
Do your own research. This is not financial advice.
#Harmony #ONE #ONEUSDT #Crypto #Blockchain #CryptoNews #Web3 #Security #Altcoins