🔌 API SECURITY: THE HIDDEN GATEWAY INTO MODERN APPLICATIONS 🛡️
Modern applications rarely work alone.
Behind websites, mobile apps, cloud platforms, and Web3 applications are APIs connecting different systems.
APIs can handle:
🔐 Authentication
👤 User data
💳 Payments
📦 Orders
☁️ Cloud services
🔗 Microservices
⛓️ Blockchain interactions
But this connectivity also creates another attack surface.
Attackers don't only target what users can see. They can target what applications can access.
⚠️ COMMON API SECURITY RISKS
🔴 Broken Authentication
Weak authentication can expose accounts and protected resources.
🔴 Broken Authorization
Being authenticated doesn't mean you should have access to everything.
🔴 Excessive Data Exposure
APIs may return sensitive information that the application doesn't actually need.
🔴 Rate Abuse
Uncontrolled requests can enable enumeration, credential attacks, and resource exhaustion.
🔴 Poor Input Validation
Never blindly trust incoming data. Treat API input as untrusted.
🔐 A STRONG API SECURITY STRATEGY
Authenticate → Authorize → Validate → Limit → Monitor → Protect → Test
Every layer matters.
🌐 APIs + Microservices = More Security Boundaries
Modern applications can look like:
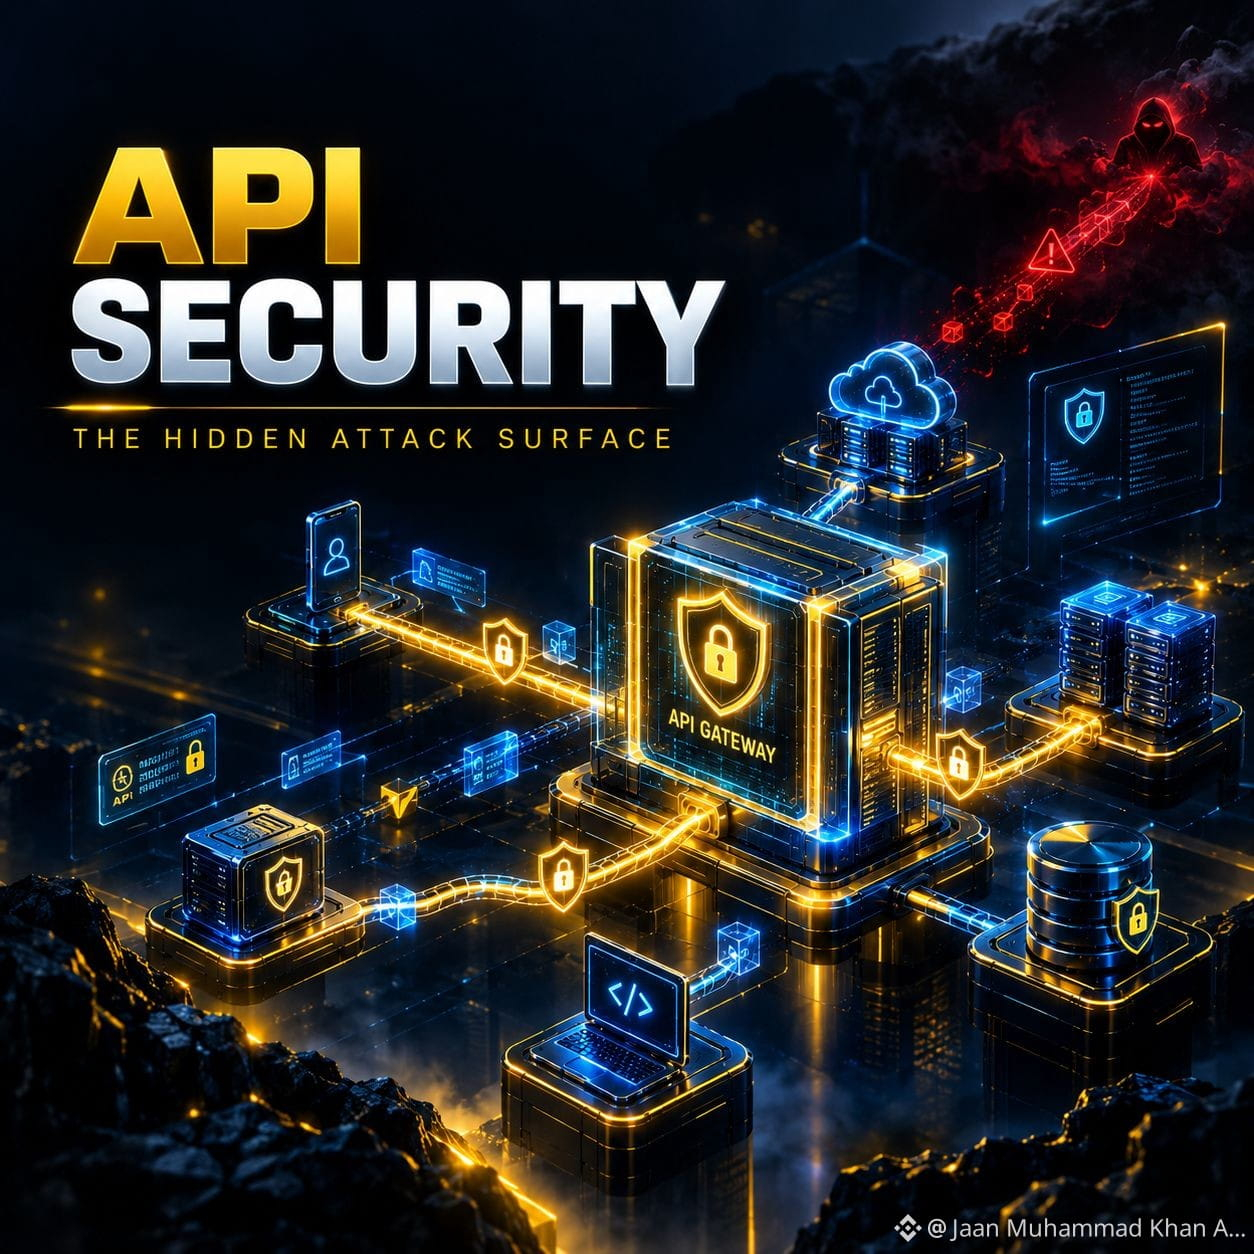
Frontend → API Gateway → Services → Database
Every connection creates another security boundary that needs protection.
🤖 AI APPLICATIONS ADD ANOTHER LAYER
AI systems increasingly connect models with databases, cloud services, search systems, APIs, and internal tools.
If an AI application has excessive permissions, those connections can become a security risk.
💡 MY TAKEAWAY
A beautiful frontend doesn't mean a secure application.
Secure the API.
Control authorization.
Validate inputs.
Monitor activity.
Test continuously.
Don't secure only what users can see.
Secure what the application can access. 🔐
Which API security area deserves more attention?
🔑 Authentication
👤 Authorization
📊 Monitoring
🧪 Testing
#API3
Modern applications rarely work alone.
Behind websites, mobile apps, cloud platforms, and Web3 applications are APIs connecting different systems.
APIs can handle:
🔐 Authentication
👤 User data
💳 Payments
📦 Orders
☁️ Cloud services
🔗 Microservices
⛓️ Blockchain interactions
But this connectivity also creates another attack surface.
Attackers don't only target what users can see. They can target what applications can access.
⚠️ COMMON API SECURITY RISKS
🔴 Broken Authentication
Weak authentication can expose accounts and protected resources.
🔴 Broken Authorization
Being authenticated doesn't mean you should have access to everything.
🔴 Excessive Data Exposure
APIs may return sensitive information that the application doesn't actually need.
🔴 Rate Abuse
Uncontrolled requests can enable enumeration, credential attacks, and resource exhaustion.
🔴 Poor Input Validation
Never blindly trust incoming data. Treat API input as untrusted.
🔐 A STRONG API SECURITY STRATEGY
Authenticate → Authorize → Validate → Limit → Monitor → Protect → Test
Every layer matters.
🌐 APIs + Microservices = More Security Boundaries
Modern applications can look like:
Frontend → API Gateway → Services → Database
Every connection creates another security boundary that needs protection.
🤖 AI APPLICATIONS ADD ANOTHER LAYER
AI systems increasingly connect models with databases, cloud services, search systems, APIs, and internal tools.
If an AI application has excessive permissions, those connections can become a security risk.
💡 MY TAKEAWAY
A beautiful frontend doesn't mean a secure application.
Secure the API.
Control authorization.
Validate inputs.
Monitor activity.
Test continuously.
Don't secure only what users can see.
Secure what the application can access. 🔐
Which API security area deserves more attention?
🔑 Authentication
👤 Authorization
📊 Monitoring
🧪 Testing
#API3