#termmax @TermMax
I’ve been looking at TermMax’s security a little differently.
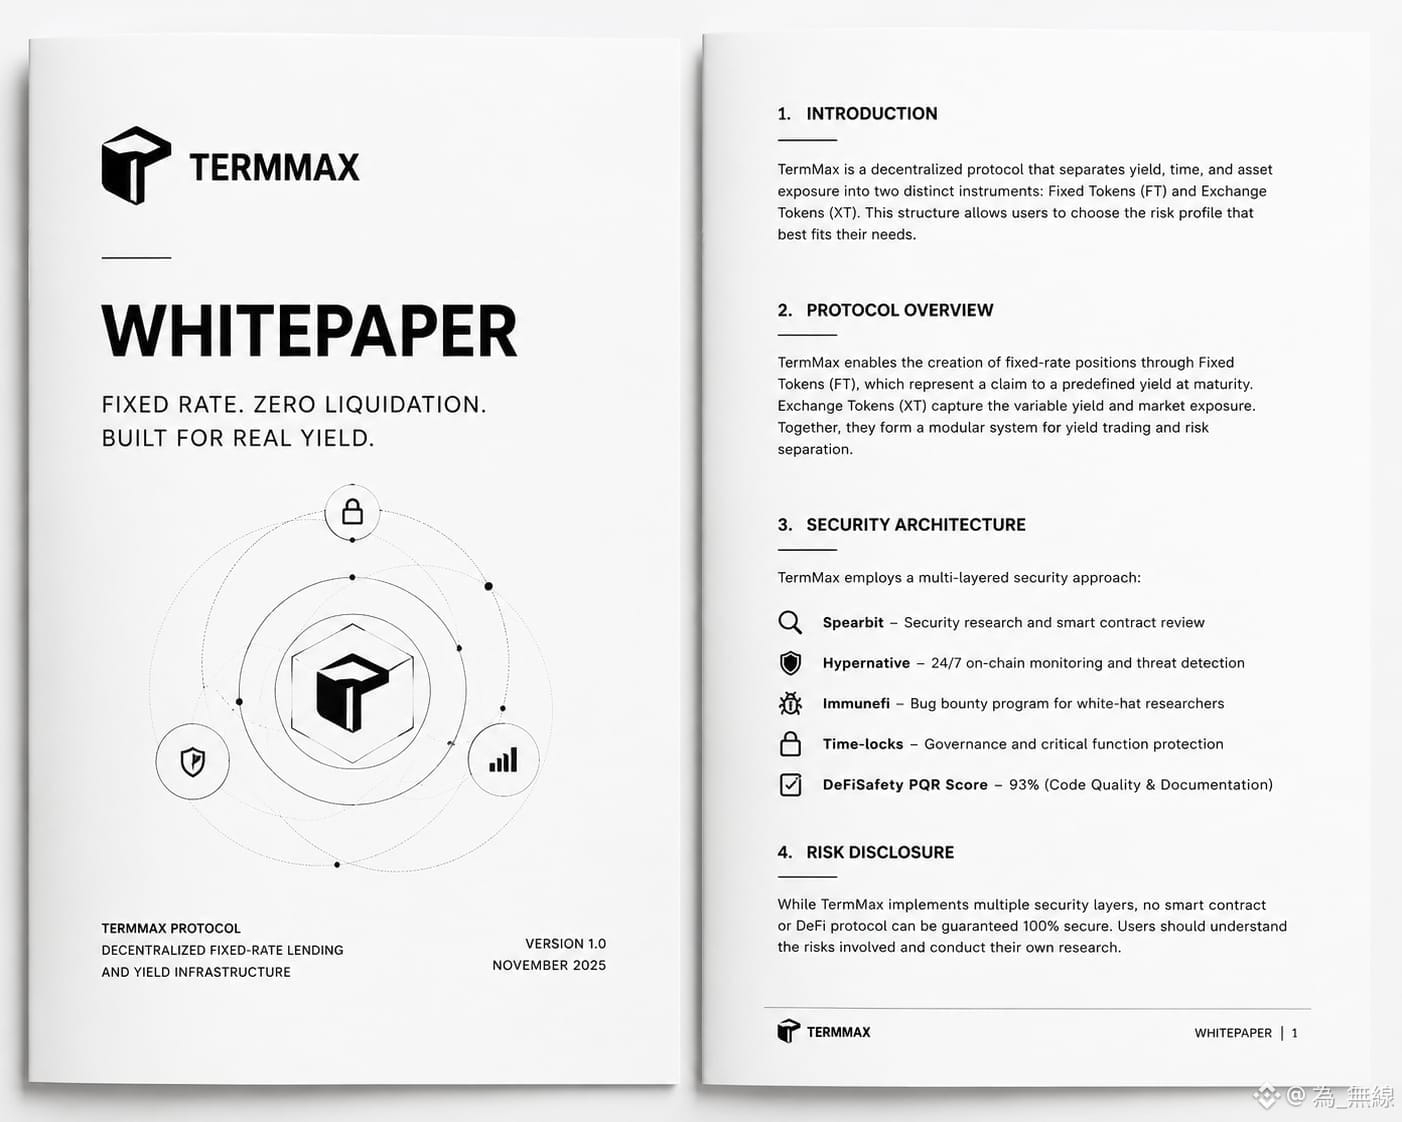
What stands out to me is that the approach isn’t based on just one audit. TermMax has mentioned security work involving Spearbit, real-time monitoring through Hypernative, an Immunefi bug bounty, time-lock protection, and a 93% DeFiSafety PQR score.
For me, that matters because an audit alone can’t guarantee that a DeFi protocol will never be exploited.
A good security setup needs more than a one-time review. Monitoring can help detect unusual activity, while bug bounties give independent researchers a reason to look for problems.
At the same time, I think it’s important to keep expectations realistic. I couldn’t verify a publicly available final Spearbit audit report for TermMax from the information I found, so I wouldn’t treat the partnership itself as proof that everything is fully secure.
The way I see it, TermMax is taking a multi-layer approach to security.
That’s a good starting point.
But in DeFi, the real test is always how those layers perform when the protocol is under actual stress.
$GIGGLE
$BTC
$ETH