#dusk $DUSK @Dusk
I’ve been going back through Dusk’s January incident notice and honestly the exploit itself is not even the part that keeps coming back to me.
It is the wording.
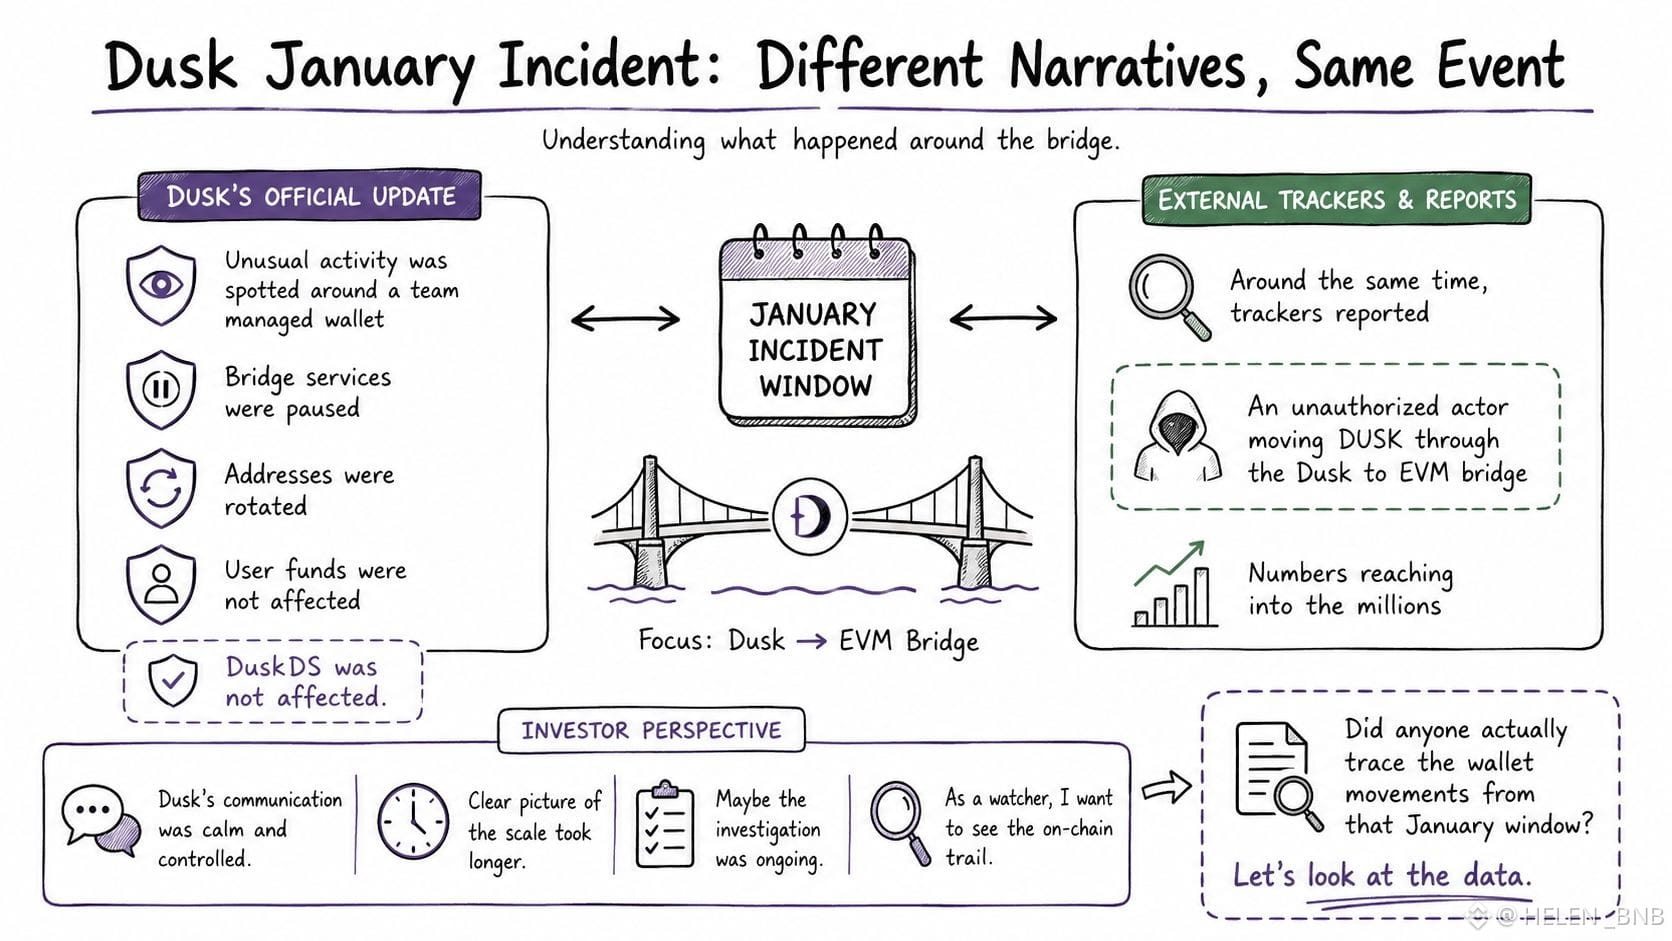
Dusk said unusual activity was spotted around a team managed wallet bridge services were paused addresses were rotated and user funds were not affected.
Very calm and controlled.
But around the same time other trackers were describing an unauthorized actor moving DUSK through the Dusk to EVM bridge with the numbers reaching into the millions.
Same incident. Very different picture.
That is what I find interesting.
I am not trying to call the incident huge or insignificant. I just want to understand what actually happened.
Dusk is building around privacy and compliance so when something happens around the bridge even if the core protocol is not affected, the way it is communicated matters too.
Dusk was quick to clarify that DuskDS was not affected.
What took longer was getting a clear picture of the actual scale.
Maybe that was simply because the investigation was still ongoing. Fair enough.
But as someone watching the project I still want to see the on chain trail and make my own judgment.
Did anyone actually trace the wallet movements from that January window…
I would genuinely like to see what the data says without relying on either sides framing.
I’ve been going back through Dusk’s January incident notice and honestly the exploit itself is not even the part that keeps coming back to me.
It is the wording.
Dusk said unusual activity was spotted around a team managed wallet bridge services were paused addresses were rotated and user funds were not affected.
Very calm and controlled.
But around the same time other trackers were describing an unauthorized actor moving DUSK through the Dusk to EVM bridge with the numbers reaching into the millions.
Same incident. Very different picture.
That is what I find interesting.
I am not trying to call the incident huge or insignificant. I just want to understand what actually happened.
Dusk is building around privacy and compliance so when something happens around the bridge even if the core protocol is not affected, the way it is communicated matters too.
Dusk was quick to clarify that DuskDS was not affected.
What took longer was getting a clear picture of the actual scale.
Maybe that was simply because the investigation was still ongoing. Fair enough.
But as someone watching the project I still want to see the on chain trail and make my own judgment.
Did anyone actually trace the wallet movements from that January window…
I would genuinely like to see what the data says without relying on either sides framing.