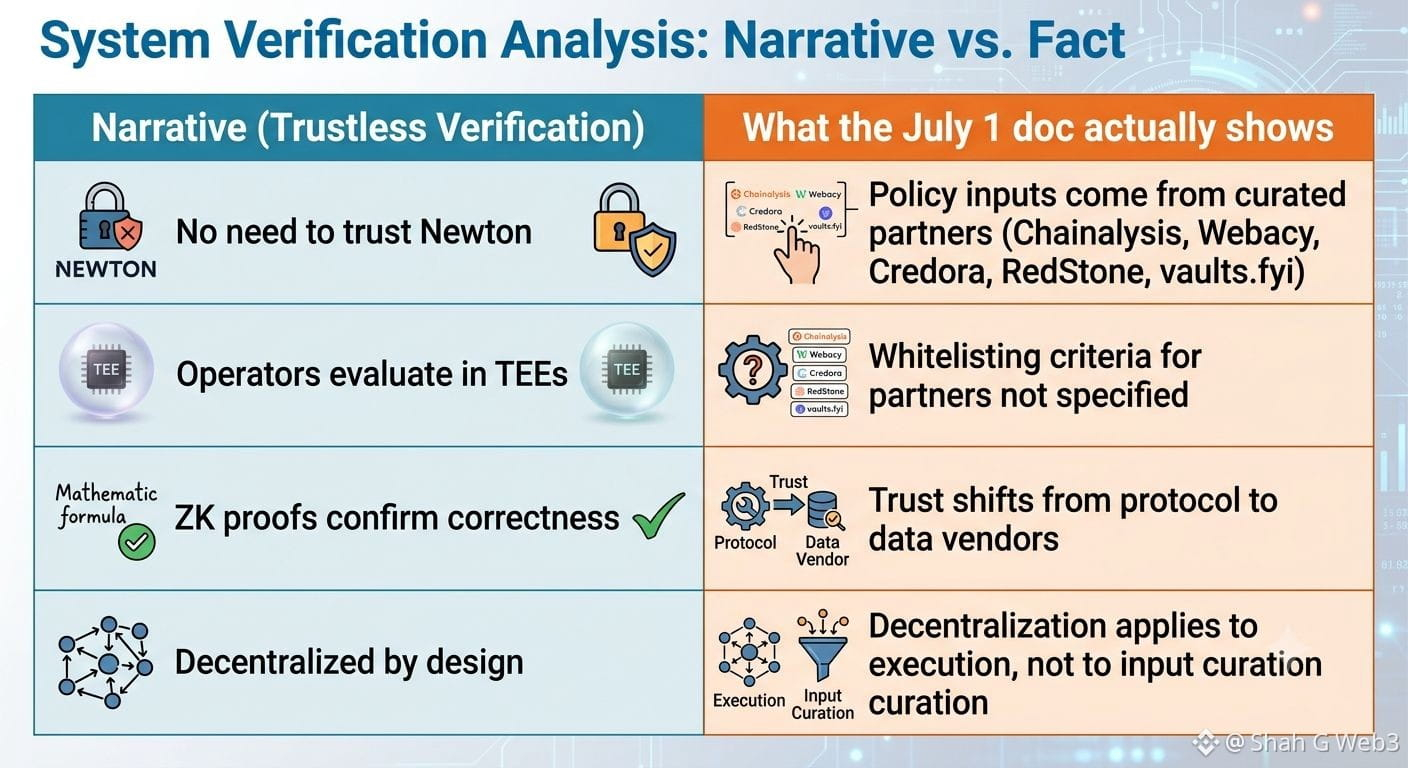
Newton Protocol just dropped their July 1 writeup on how the Authorization Layer actually works — the piece walking through what happens before settlement, not after. Been staring at that page for an hour. $NEWT @NewtonProtocol
Here's what got me — the whole pitch is "trustless" and "cryptographically verifiable," and technically it is, operators run in TEEs, ZK proofs attest to correct evaluation. But the actual policy inputs — the stuff that decides pass or fail — come from a short list of onboarded partners. Chainalysis for sanctions. Webacy for wallet reputation. Credora for risk ratings. RedStone for price feeds. That's not nothing, it's just… a different kind of trust. You're not trusting Newton, sure. You're trusting whoever curated that partner list.
Had my own small "wait" moment reading it — I kept expecting the doc to address who decides which oracle gets whitelisted into a policy, and it just doesn't go there. Maybe that's a governance question for later, maybe it's already answered somewhere I haven't found yet.
So when they say "safer AI agents," is the safety coming from the crypto, or from picking good data vendors? Feels like those are two very different claims wearing the same word.
#Newt