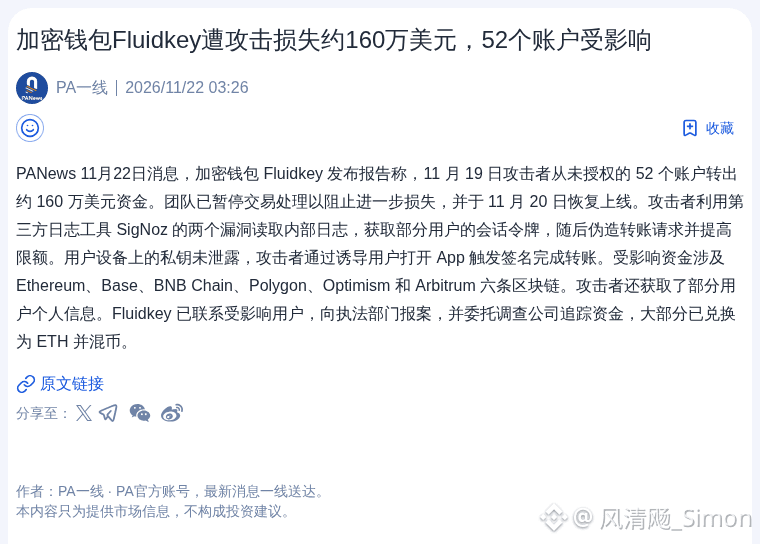
Fluidkey really got hit hard this time: 52 accounts were drained of $1.6 million.
Apparently, attackers exploited a vulnerability in SigNoz to obtain session tokens, then forged transfer requests. The craziest part is that users’ private keys weren’t compromised—instead, they tricked users into opening the app and signing transactions to transfer the funds.
Their security defenses are seriously pathetic. Hackers even got hold of users’ personal information. I really feel for the users who got caught up in this mess.
$ETH
$BNB
$ARB
#Ethereum
#BNBChain
Apparently, attackers exploited a vulnerability in SigNoz to obtain session tokens, then forged transfer requests. The craziest part is that users’ private keys weren’t compromised—instead, they tricked users into opening the app and signing transactions to transfer the funds.
Their security defenses are seriously pathetic. Hackers even got hold of users’ personal information. I really feel for the users who got caught up in this mess.
$ETH
$BNB
$ARB
#Ethereum
#BNBChain