In 2018, an emergency fix for $BTC first publicly warned that “nodes could crash,” and only later fully disclosed the inflation risk. Looking back at CVE-2018-17144 today leaves a difficult question: does explaining everything sooner always make users safer?
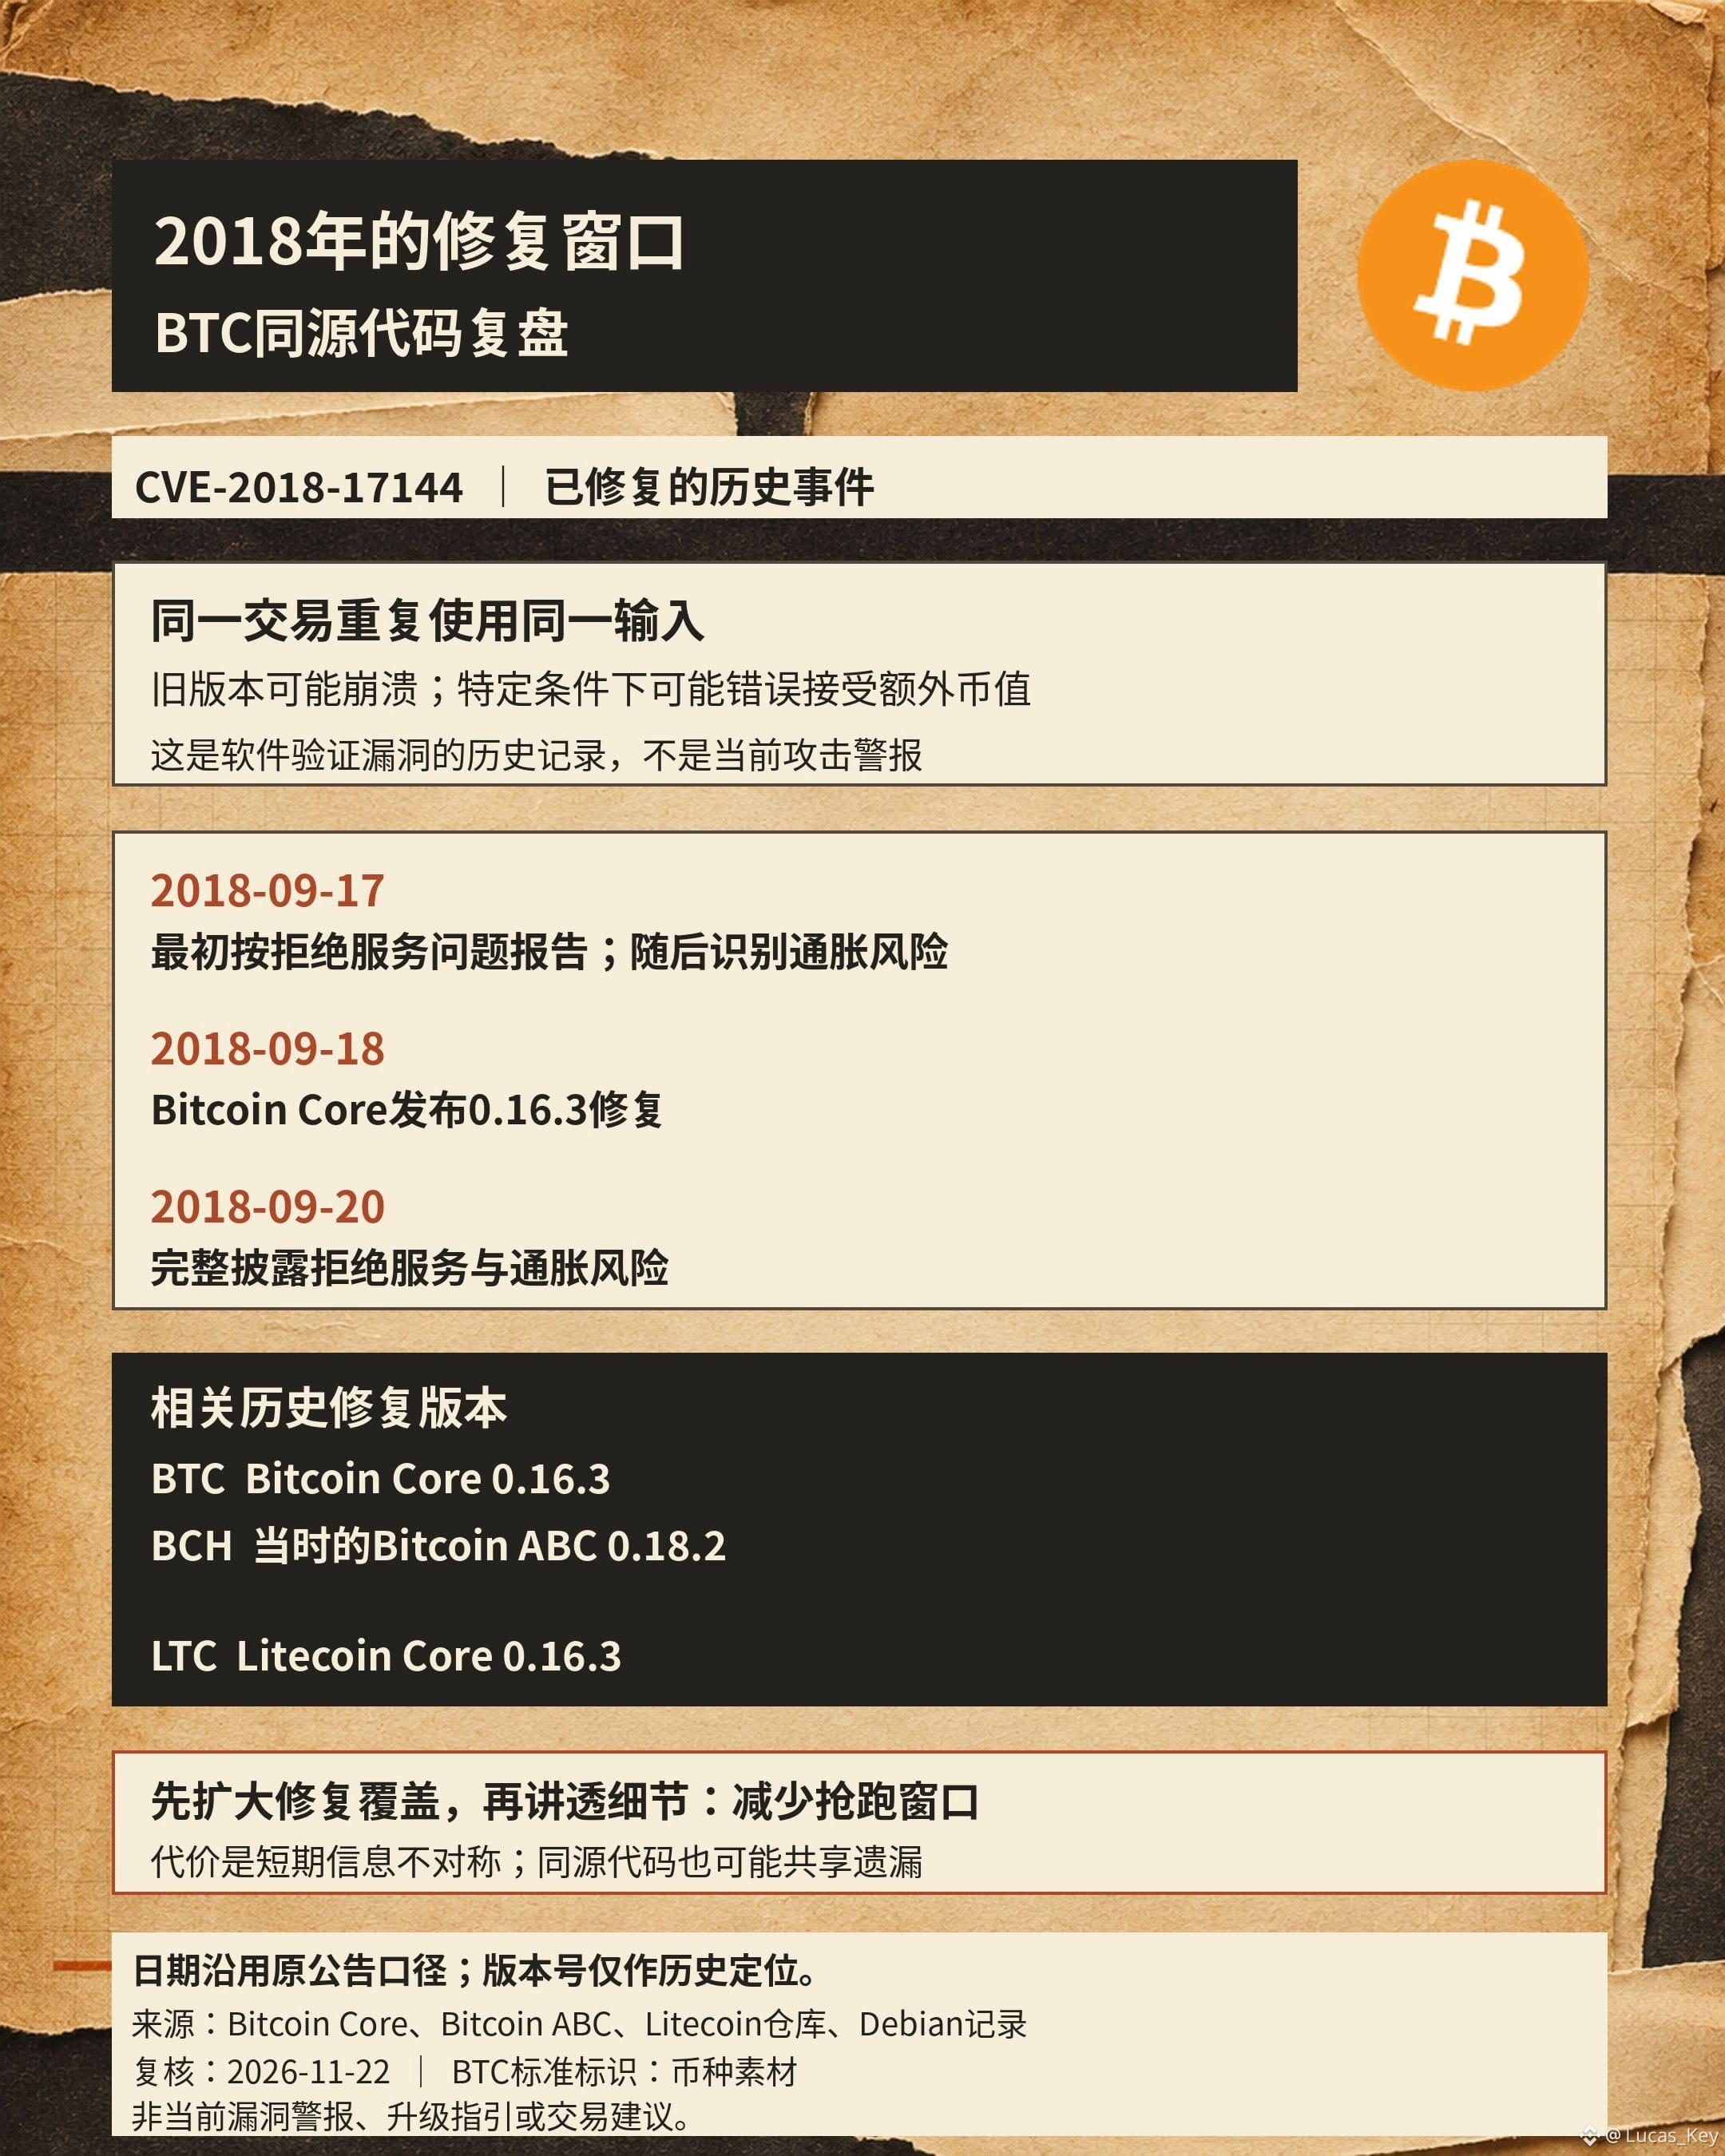
Bitcoin Core’s official records show that on September 17, it received a vulnerability report initially categorized as a denial-of-service issue. Developers later identified an inflation risk with the same root cause. A fix, version 0.16.3, was released on September 18, and the issue was fully disclosed on September 20. The issue involved reusing the same input in a transaction: certain older versions could crash during block validation, while in other cases they could incorrectly accept extra coins. This is a historical software vulnerability, not something to describe as a current attack.
There were clear reasons for choosing staged disclosure: give miners, businesses, and nodes time to upgrade, reducing the window in which an attacker could exploit the issue first. But this also created an information asymmetry—operators who did not yet know the full severity had to rely on maintainers’ judgment about how urgently to upgrade. Transparency and patch coverage should be considered together.
The risk also spread through shared code. At the time, Bitcoin ABC, which supported $BCH , released a 0.18.2 fix; subsequent reports said the vulnerability had not been exploited on the mainnet. $LTC ’s 0.16.3 also fixed a crash issue related to duplicate inputs. The three chains had different rules, yet could inherit the same validation logic. Diversifying holdings by coin name does not automatically diversify this kind of code risk.
I’m more interested in whether subsequent reviews can reconstruct the sequence of discovery, fixing, release, and notification; whether the scope of affected versions was explained; and whether the fix included regression tests. These points remain useful when assessing projects with shared code today: shared code can mean shared review benefits, but also shared oversights. What needs to be verified is the version and patch path, not just the project’s age.
Dates follow the original announcements. Sources: Bitcoin Core announcements of September 18 and 20, 2018; Bitcoin ABC incident report; Litecoin code and security records. Reviewed on 2026-11-22. This historical issue has been fixed and is not a current vulnerability alert or trading advice. This post may receive platform creator rewards.
Bitcoin Core’s official records show that on September 17, it received a vulnerability report initially categorized as a denial-of-service issue. Developers later identified an inflation risk with the same root cause. A fix, version 0.16.3, was released on September 18, and the issue was fully disclosed on September 20. The issue involved reusing the same input in a transaction: certain older versions could crash during block validation, while in other cases they could incorrectly accept extra coins. This is a historical software vulnerability, not something to describe as a current attack.
There were clear reasons for choosing staged disclosure: give miners, businesses, and nodes time to upgrade, reducing the window in which an attacker could exploit the issue first. But this also created an information asymmetry—operators who did not yet know the full severity had to rely on maintainers’ judgment about how urgently to upgrade. Transparency and patch coverage should be considered together.
The risk also spread through shared code. At the time, Bitcoin ABC, which supported $BCH , released a 0.18.2 fix; subsequent reports said the vulnerability had not been exploited on the mainnet. $LTC ’s 0.16.3 also fixed a crash issue related to duplicate inputs. The three chains had different rules, yet could inherit the same validation logic. Diversifying holdings by coin name does not automatically diversify this kind of code risk.
I’m more interested in whether subsequent reviews can reconstruct the sequence of discovery, fixing, release, and notification; whether the scope of affected versions was explained; and whether the fix included regression tests. These points remain useful when assessing projects with shared code today: shared code can mean shared review benefits, but also shared oversights. What needs to be verified is the version and patch path, not just the project’s age.
Dates follow the original announcements. Sources: Bitcoin Core announcements of September 18 and 20, 2018; Bitcoin ABC incident report; Litecoin code and security records. Reviewed on 2026-11-22. This historical issue has been fixed and is not a current vulnerability alert or trading advice. This post may receive platform creator rewards.