If the people who robbed the vault had the real key, does that still count as a hack?
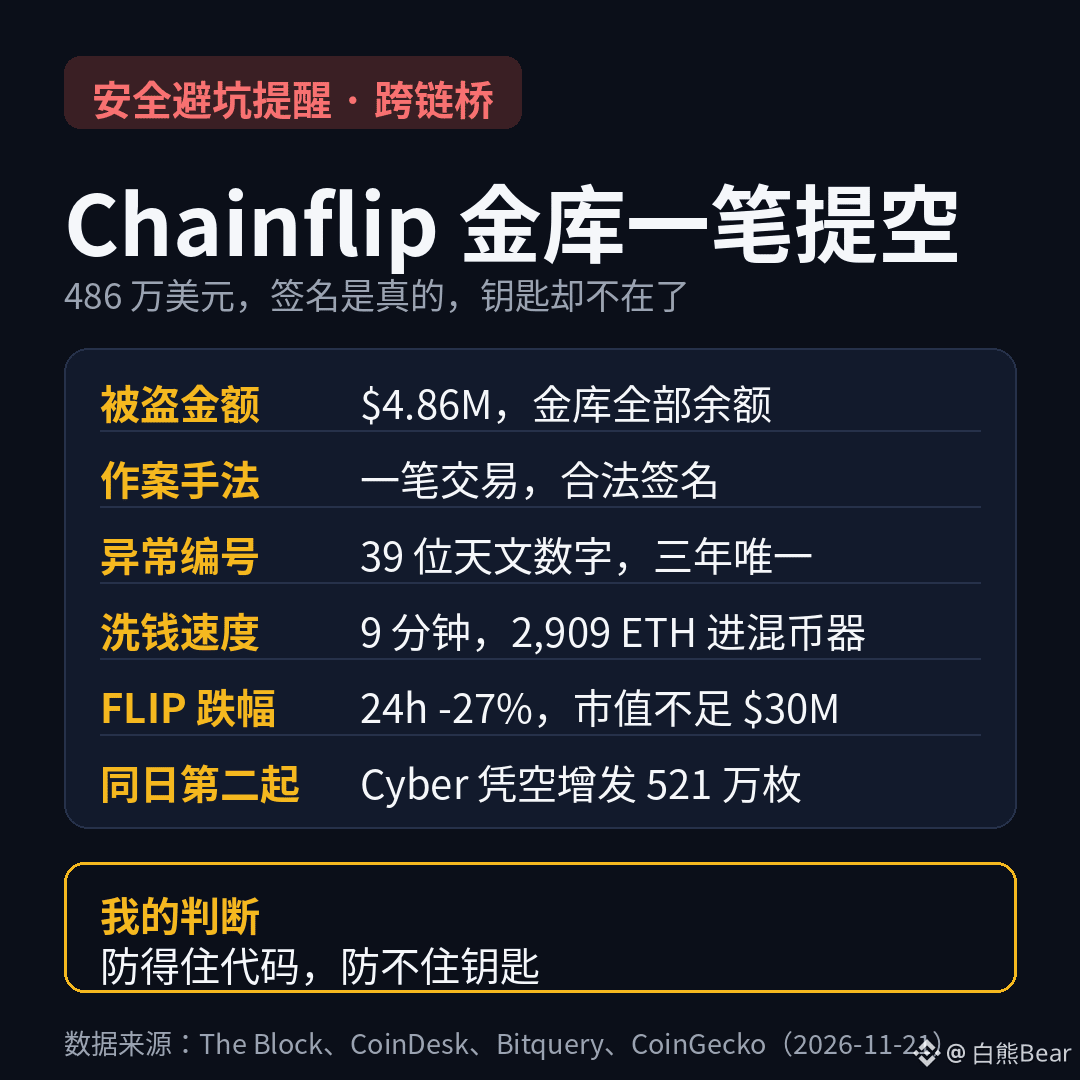
That’s exactly how Chainflip’s Ethereum vault was drained. In a single transaction, 520 ETH, 3.25 million USDC, and 758,000 USDT were taken—a total of $4.86 million. They took everything in the vault, down to the last cent.
The strange part is that the withdrawal signature was genuine. Chainflip’s rules put 150 validators in control of a shared key, and at least 100 must participate in signing to move funds from the vault. Once the signature is verified, the money goes out. Bitquery went through all 299,677 signatures from the vault’s three-year history and found just one that didn’t add up: its ID was an astronomical 39-digit number, while a normal ID should be around 315,000. The signature itself was valid, but it hadn’t been generated through the normal system. The key had most likely fallen into the wrong hands.
The attacker wasted no time: in nine minutes, they converted all the stablecoins into ETH, then sent 2,909 ETH into Tornado Cash in 38 transactions over 48 seconds. The attack wallet received its first funds just one minute before the attack—and those funds had come from a mixer. Chainflip then shut down its entire platform: deposits, withdrawals, swaps, and quotes were all disabled, and even LPs couldn’t withdraw their funds. FLIP fell more than 27% in a day, with its market cap shrinking from $41.6 million to under $30 million. Something happened on Tron in September, too, and validators voted to compensate LPs then. Whether they’ll do so this time is still unclear.
Cyber was hit the same day: 5.213 million CYBER tokens were minted out of thin air on Solana, and the same amount was withdrawn from the Ethereum bridge’s locked reserves. The tokens were sold for about $970,000 worth of ETH, and Upbit and Bithumb immediately froze CYBER deposits and withdrawals. The two incidents used different methods, but exposed the same weakness: the security of cross-chain bridges and vaults doesn’t depend on whether the code has vulnerabilities—it depends on whether the people and processes controlling the keys have been compromised.
In my view, this week’s cluster of security incidents is no coincidence: sBOLD on the 18th, Fluidkey on the 19th, XMR1 on the 20th, and Chainflip plus Cyber on the 21st—five incidents in one week, with losses ranging from $1 million to $13.5 million. The market had just climbed back above $60,000 after hitting a low of $55,300, and the security incidents started coming one after another. The weaker the market, the more active the attackers become. Everyone’s busy trying to recover their losses, and no one is watching risk controls. What’s even more concerning is a case like Chainflip’s: no contract vulnerability, a genuine signature, and an audit that couldn’t stop it. Having 150 validators share control of a key sounds decentralized, but if there’s even one gap in the signing process, the whole design effectively leaves the front door open to attackers.
Here’s what to watch next: Will Chainflip compensate LPs? It did so after the September incident; if it doesn’t this time, FLIP and its LPs could be finished. What will happen to Cyber’s 5.21 million unbacked CYBER tokens—will they be burned, or will the issuance become a fait accompli? And what’s happening to the 2,909 ETH in Tornado Cash? Will the same people go after other bridges?
Would you still dare to leave your money in a cross-chain bridge vault long-term, or would you only use it when needed and swap out right away?
$BTC $FLIP $CYBER
#跨链桥 #DeFi Security
That’s exactly how Chainflip’s Ethereum vault was drained. In a single transaction, 520 ETH, 3.25 million USDC, and 758,000 USDT were taken—a total of $4.86 million. They took everything in the vault, down to the last cent.
The strange part is that the withdrawal signature was genuine. Chainflip’s rules put 150 validators in control of a shared key, and at least 100 must participate in signing to move funds from the vault. Once the signature is verified, the money goes out. Bitquery went through all 299,677 signatures from the vault’s three-year history and found just one that didn’t add up: its ID was an astronomical 39-digit number, while a normal ID should be around 315,000. The signature itself was valid, but it hadn’t been generated through the normal system. The key had most likely fallen into the wrong hands.
The attacker wasted no time: in nine minutes, they converted all the stablecoins into ETH, then sent 2,909 ETH into Tornado Cash in 38 transactions over 48 seconds. The attack wallet received its first funds just one minute before the attack—and those funds had come from a mixer. Chainflip then shut down its entire platform: deposits, withdrawals, swaps, and quotes were all disabled, and even LPs couldn’t withdraw their funds. FLIP fell more than 27% in a day, with its market cap shrinking from $41.6 million to under $30 million. Something happened on Tron in September, too, and validators voted to compensate LPs then. Whether they’ll do so this time is still unclear.
Cyber was hit the same day: 5.213 million CYBER tokens were minted out of thin air on Solana, and the same amount was withdrawn from the Ethereum bridge’s locked reserves. The tokens were sold for about $970,000 worth of ETH, and Upbit and Bithumb immediately froze CYBER deposits and withdrawals. The two incidents used different methods, but exposed the same weakness: the security of cross-chain bridges and vaults doesn’t depend on whether the code has vulnerabilities—it depends on whether the people and processes controlling the keys have been compromised.
In my view, this week’s cluster of security incidents is no coincidence: sBOLD on the 18th, Fluidkey on the 19th, XMR1 on the 20th, and Chainflip plus Cyber on the 21st—five incidents in one week, with losses ranging from $1 million to $13.5 million. The market had just climbed back above $60,000 after hitting a low of $55,300, and the security incidents started coming one after another. The weaker the market, the more active the attackers become. Everyone’s busy trying to recover their losses, and no one is watching risk controls. What’s even more concerning is a case like Chainflip’s: no contract vulnerability, a genuine signature, and an audit that couldn’t stop it. Having 150 validators share control of a key sounds decentralized, but if there’s even one gap in the signing process, the whole design effectively leaves the front door open to attackers.
Here’s what to watch next: Will Chainflip compensate LPs? It did so after the September incident; if it doesn’t this time, FLIP and its LPs could be finished. What will happen to Cyber’s 5.21 million unbacked CYBER tokens—will they be burned, or will the issuance become a fait accompli? And what’s happening to the 2,909 ETH in Tornado Cash? Will the same people go after other bridges?
Would you still dare to leave your money in a cross-chain bridge vault long-term, or would you only use it when needed and swap out right away?
$BTC $FLIP $CYBER
#跨链桥 #DeFi Security