The biggest risk for a cross-chain bridge isn’t a contract vulnerability—it’s compromised signing keys.
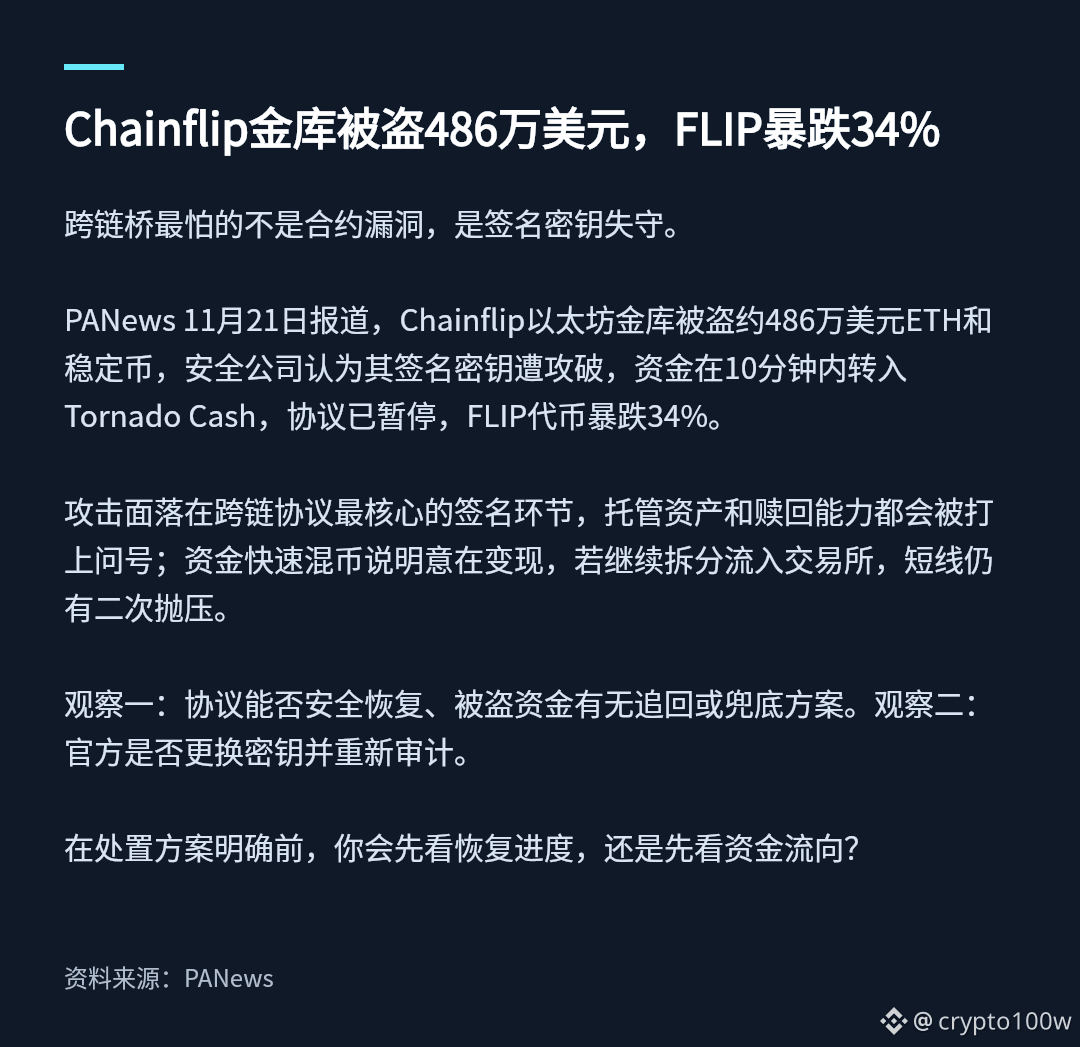
PANews reported on November 21 that approximately $4.86 million worth of ETH and stablecoins was stolen from Chainflip’s Ethereum vault. Security firms believe the signing keys were compromised. The funds were transferred to Tornado Cash within 10 minutes. The protocol has been paused, and the FLIP token plunged 34%.
The attack targeted the signing process at the heart of the cross-chain protocol, raising questions about both the custody of assets and the ability to process withdrawals. The rapid mixing of funds suggests an intent to cash out. If the funds continue to be split up and sent to exchanges, further short-term selling pressure may follow.
What to watch, part one: Can the protocol be safely restored, and is there a plan to recover the stolen funds or compensate users? Part two: Will the team replace the keys and conduct a new audit?
Before the response plan is clear, would you focus first on recovery progress or on where the funds are flowing?
Image 1: $4.86 million stolen from Chainflip’s vault; FLIP plunges 34% · News highlights
Image source: https://www.panewslab.com/zh/articles/01a1febe-4ef4-7135-b580-bfd626115d34
PANews reported on November 21 that approximately $4.86 million worth of ETH and stablecoins was stolen from Chainflip’s Ethereum vault. Security firms believe the signing keys were compromised. The funds were transferred to Tornado Cash within 10 minutes. The protocol has been paused, and the FLIP token plunged 34%.
The attack targeted the signing process at the heart of the cross-chain protocol, raising questions about both the custody of assets and the ability to process withdrawals. The rapid mixing of funds suggests an intent to cash out. If the funds continue to be split up and sent to exchanges, further short-term selling pressure may follow.
What to watch, part one: Can the protocol be safely restored, and is there a plan to recover the stolen funds or compensate users? Part two: Will the team replace the keys and conduct a new audit?
Before the response plan is clear, would you focus first on recovery progress or on where the funds are flowing?
Image 1: $4.86 million stolen from Chainflip’s vault; FLIP plunges 34% · News highlights
Image source: https://www.panewslab.com/zh/articles/01a1febe-4ef4-7135-b580-bfd626115d34