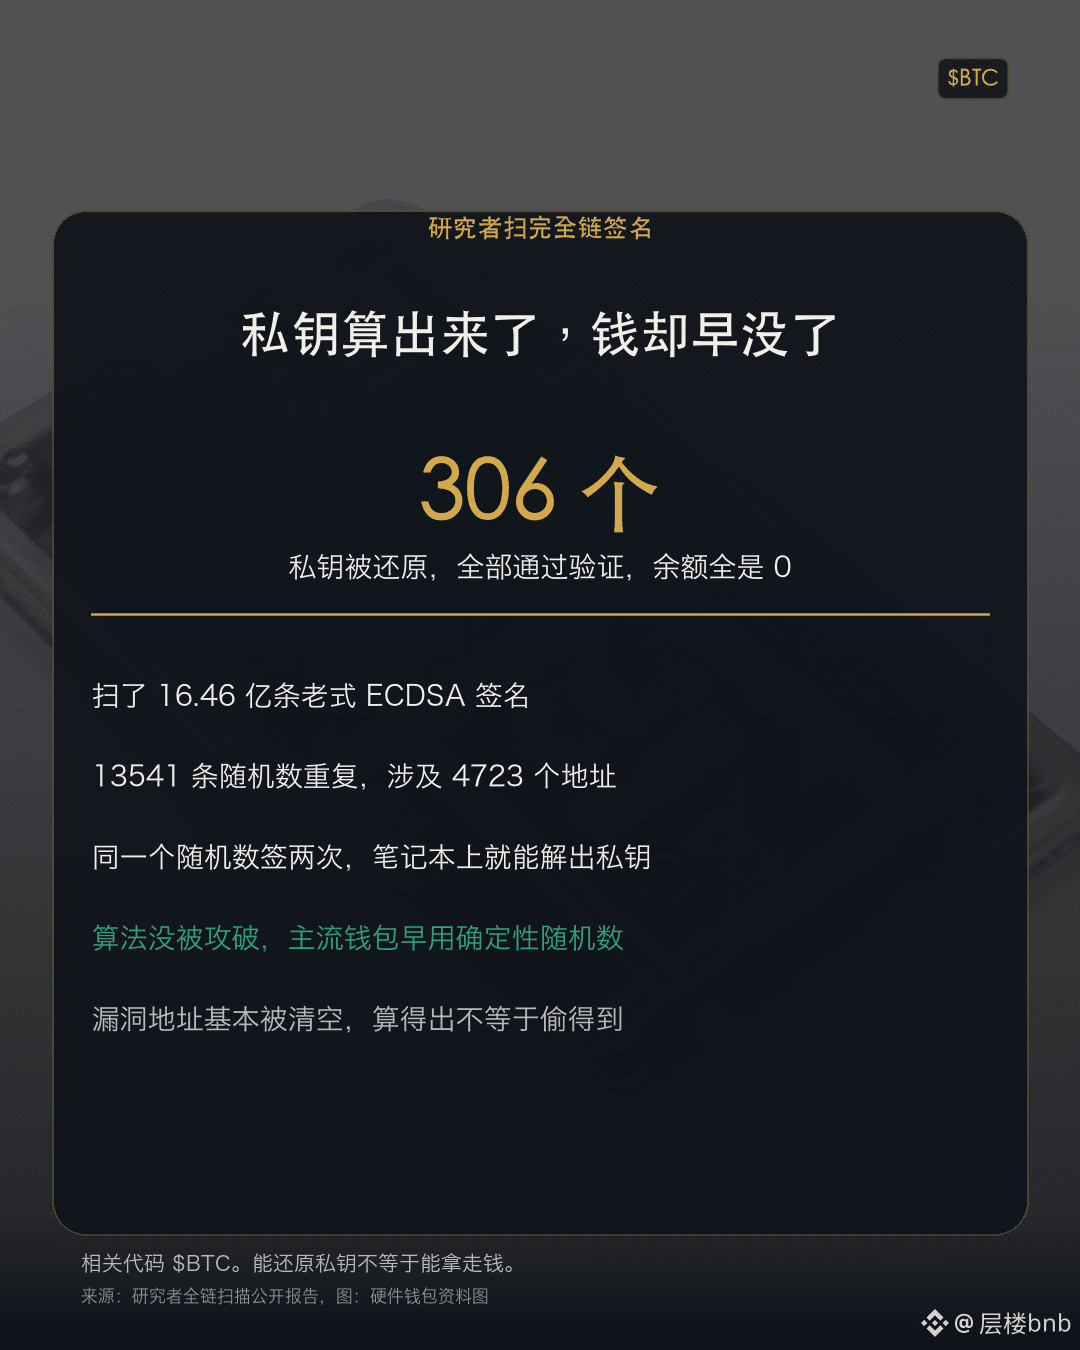
The Bitcoin signature vulnerability was being portrayed as something that could be cracked in seconds, but the reality is much less alarming. A researcher scanned all 1.646 billion legacy signatures in Bitcoin’s history and found 13,541 signatures with reused nonces, involving 4,723 addresses. Once a nonce is reused, someone can use two signatures on a laptop to calculate the private key. The researcher actually recovered all 306 private keys in question; all 306 passed verification, with not a single error. Then they discovered that not one of those 306 addresses held any bitcoin. The vulnerability is real, but these old addresses had long since been emptied. The signature algorithm itself has not been broken, and mainstream wallets have used deterministic nonces since 2016, preventing reuse. Being able to calculate a private key doesn’t mean you can get the money.
Related code: $BTC
#比特币签名漏洞可被秒级利用
Related code: $BTC
#比特币签名漏洞可被秒级利用