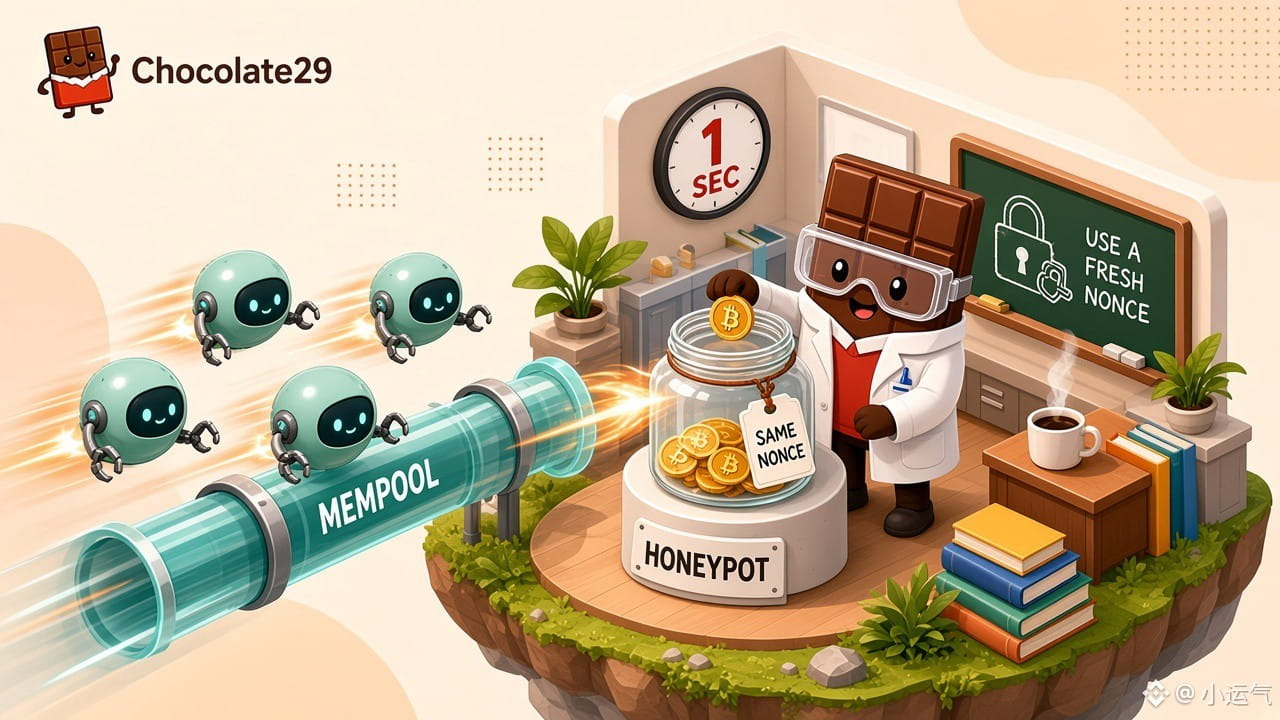
Two university researchers left a few dollars in deliberately flawed bitcoin wallets, and automated bots tried to grab the coins within seconds.
As reported by CoinDesk on November 20, 2026, Vincent Jacquot and Benoît Donnet of Belgium's University of Liège reused a signing "nonce" on purpose. Every ECDSA signature needs a fresh random number; if one key reuses it, anyone watching can work out the private key. On $BTC, rival transactions raced for the bait "a second or a few seconds" after it was set up.
Their scan of six blockchains through June 30, 2024 recovered 3,620 private keys, 3,278 of them on Bitcoin. Peak balances of the exposed addresses add up to about $106 million at November 2024 prices, though the team did not establish how much was actually taken. The weak spot is faulty wallet software, not the Bitcoin protocol, so stick to well-maintained, updated wallets.
#Bitcoin #WalletSecurity #CryptoResearch
DYOR. Not financial advice.
As reported by CoinDesk on November 20, 2026, Vincent Jacquot and Benoît Donnet of Belgium's University of Liège reused a signing "nonce" on purpose. Every ECDSA signature needs a fresh random number; if one key reuses it, anyone watching can work out the private key. On $BTC, rival transactions raced for the bait "a second or a few seconds" after it was set up.
Their scan of six blockchains through June 30, 2024 recovered 3,620 private keys, 3,278 of them on Bitcoin. Peak balances of the exposed addresses add up to about $106 million at November 2024 prices, though the team did not establish how much was actually taken. The weak spot is faulty wallet software, not the Bitcoin protocol, so stick to well-maintained, updated wallets.
#Bitcoin #WalletSecurity #CryptoResearch
DYOR. Not financial advice.