
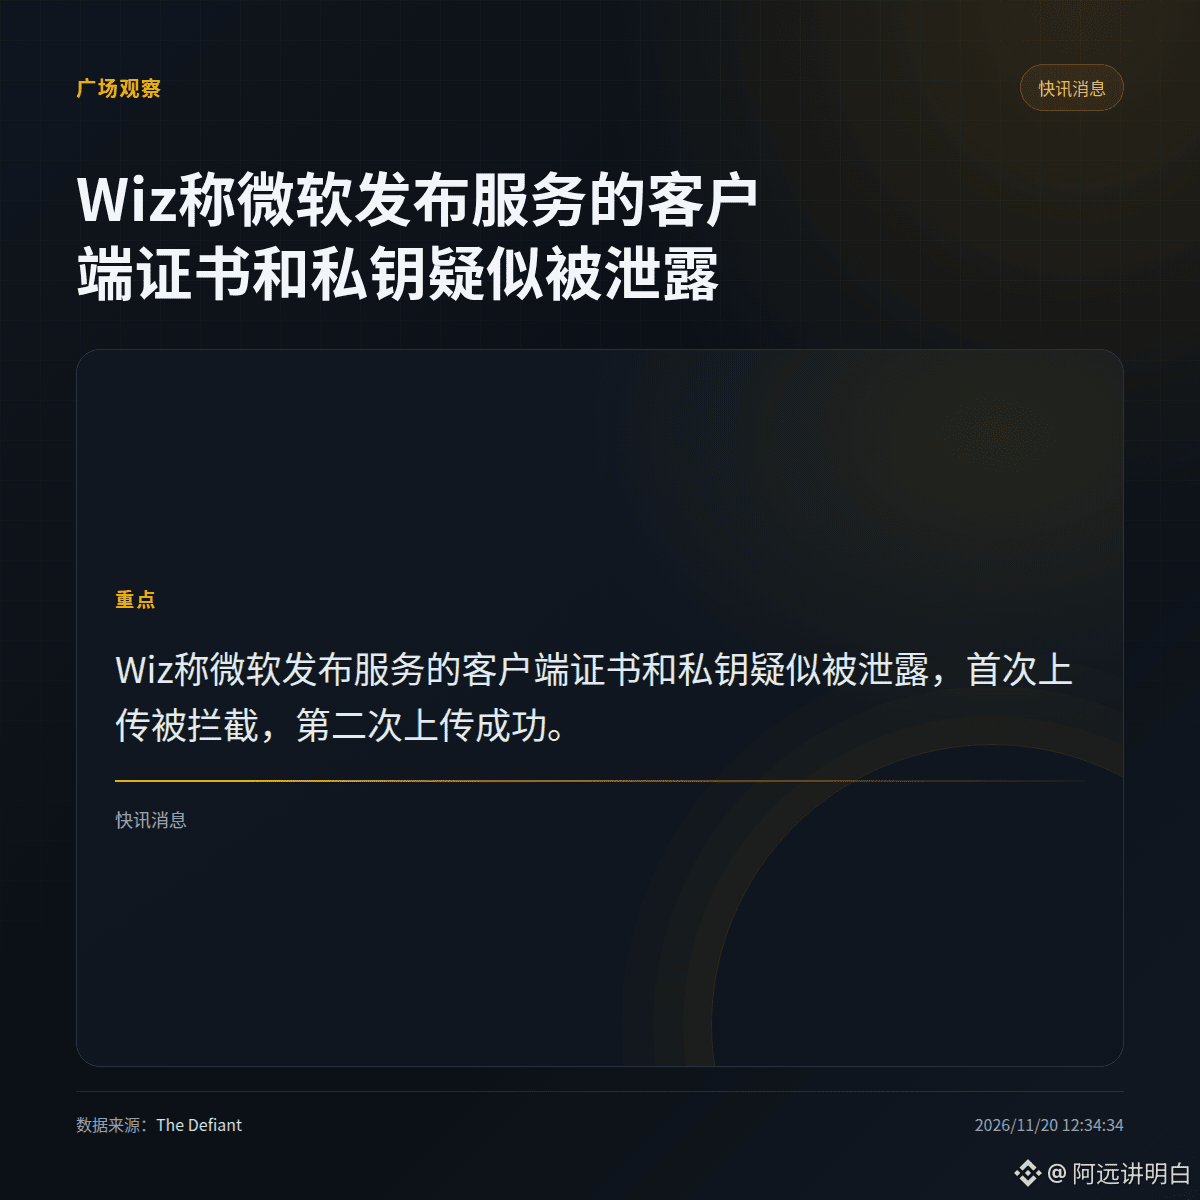
The core of the Microsoft AI package incident is the credentials: Wiz says the client certificate and private key for Microsoft’s publishing service may have been exposed. The first upload attempt was blocked, but the second succeeded. The fact that the safeguard failed the second time suggests the threat wasn’t just about a single certificate—the defenses in the publishing process were bypassed once. The information available doesn’t say what the second upload ultimately published or which packages were affected, so don’t extrapolate the scope of the impact. What we can confirm is the change from “blocked the first time” to “succeeded the second time.” Next, we’ll need to see whether Microsoft confirms the status of the credentials and whether it makes any changes to the publishing process. For now, keep watching the range and volume; there’s no need to draw conclusions before anything is confirmed.
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number