Hackers are practically picking up free money every day—52.42 ETH in the bag!
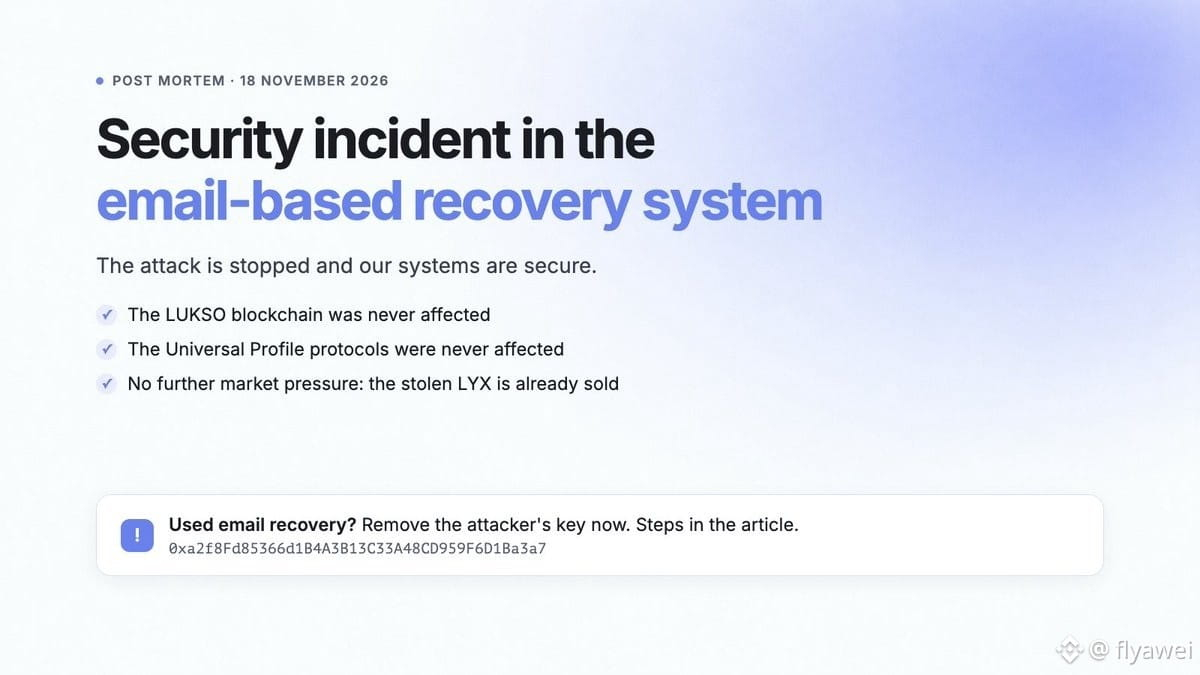
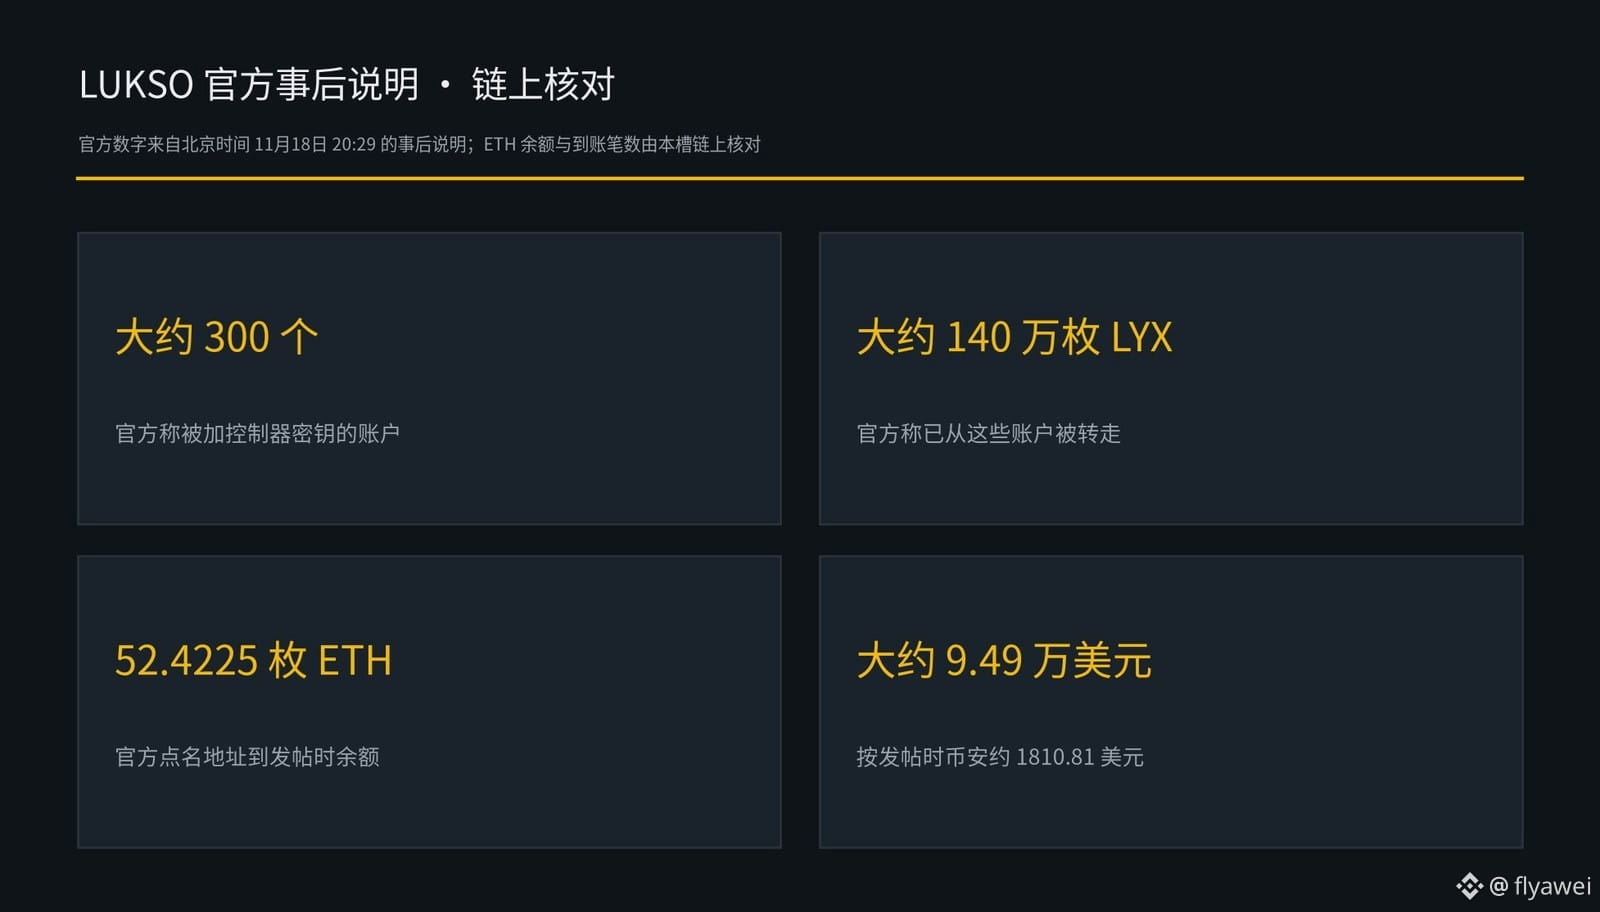
LUKSO officially posted a post-incident statement at 20:29 Beijing time on November 18, saying that from the night of November 17 through November 18, a vulnerability in the backend of its email recovery system allowed attackers to add controller keys to around 300 Universal Profile accounts. About 1.4 million LYX was stolen from these accounts in total.
The official statement said that all of the roughly 1.4 million LYX had been bridged to Ethereum, traded for ether on decentralized exchanges, and eventually converted into about 50 ETH, worth approximately $95,000.
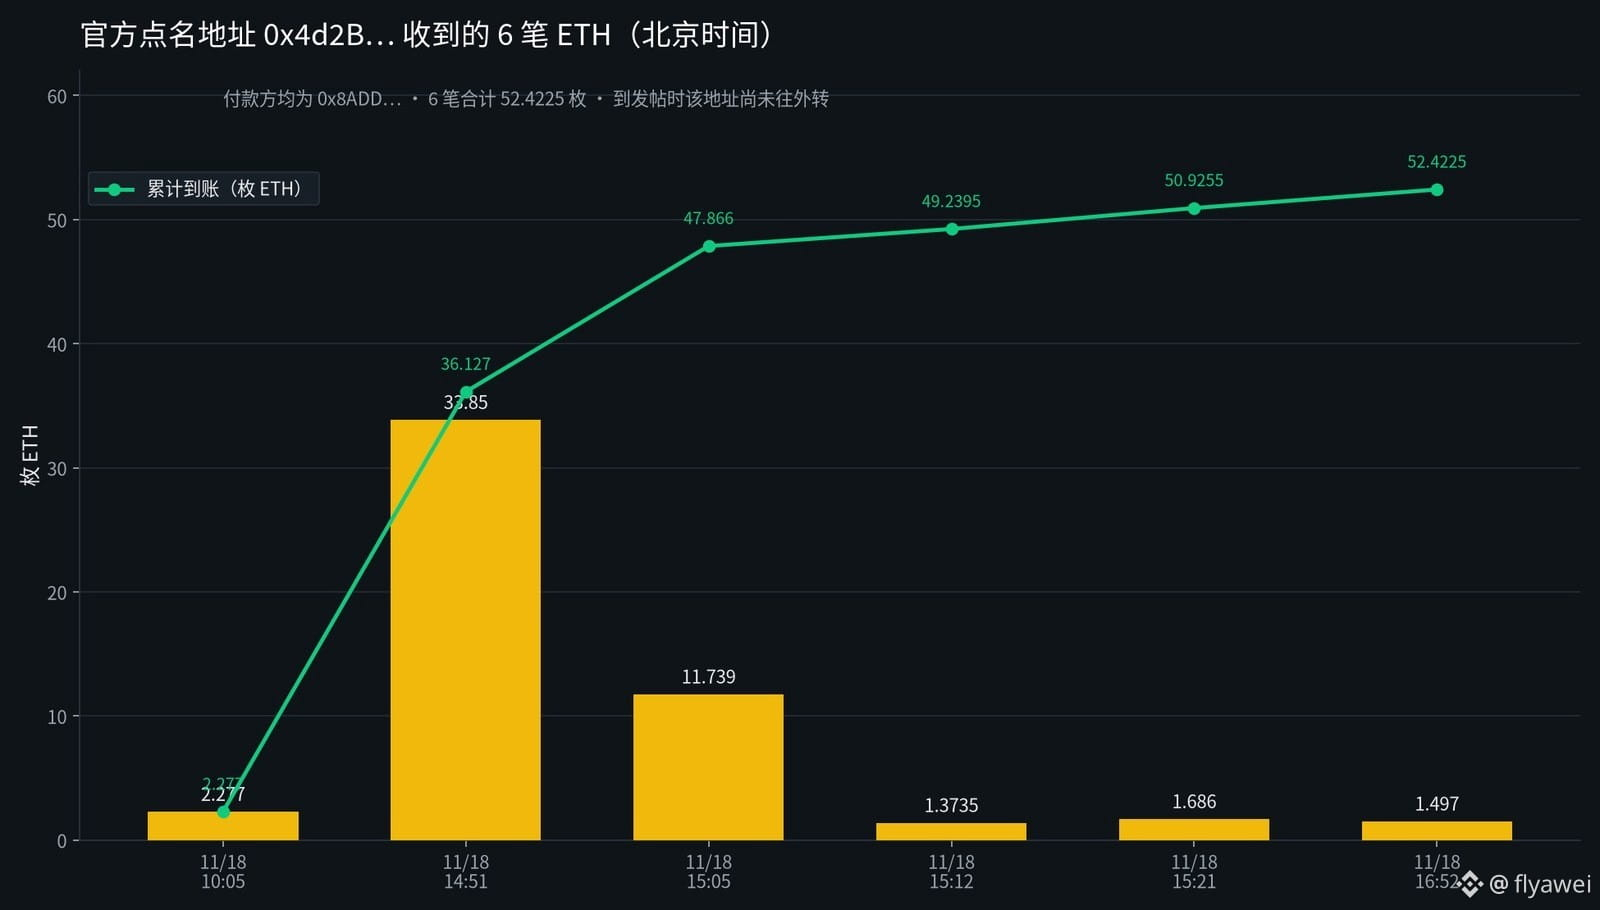
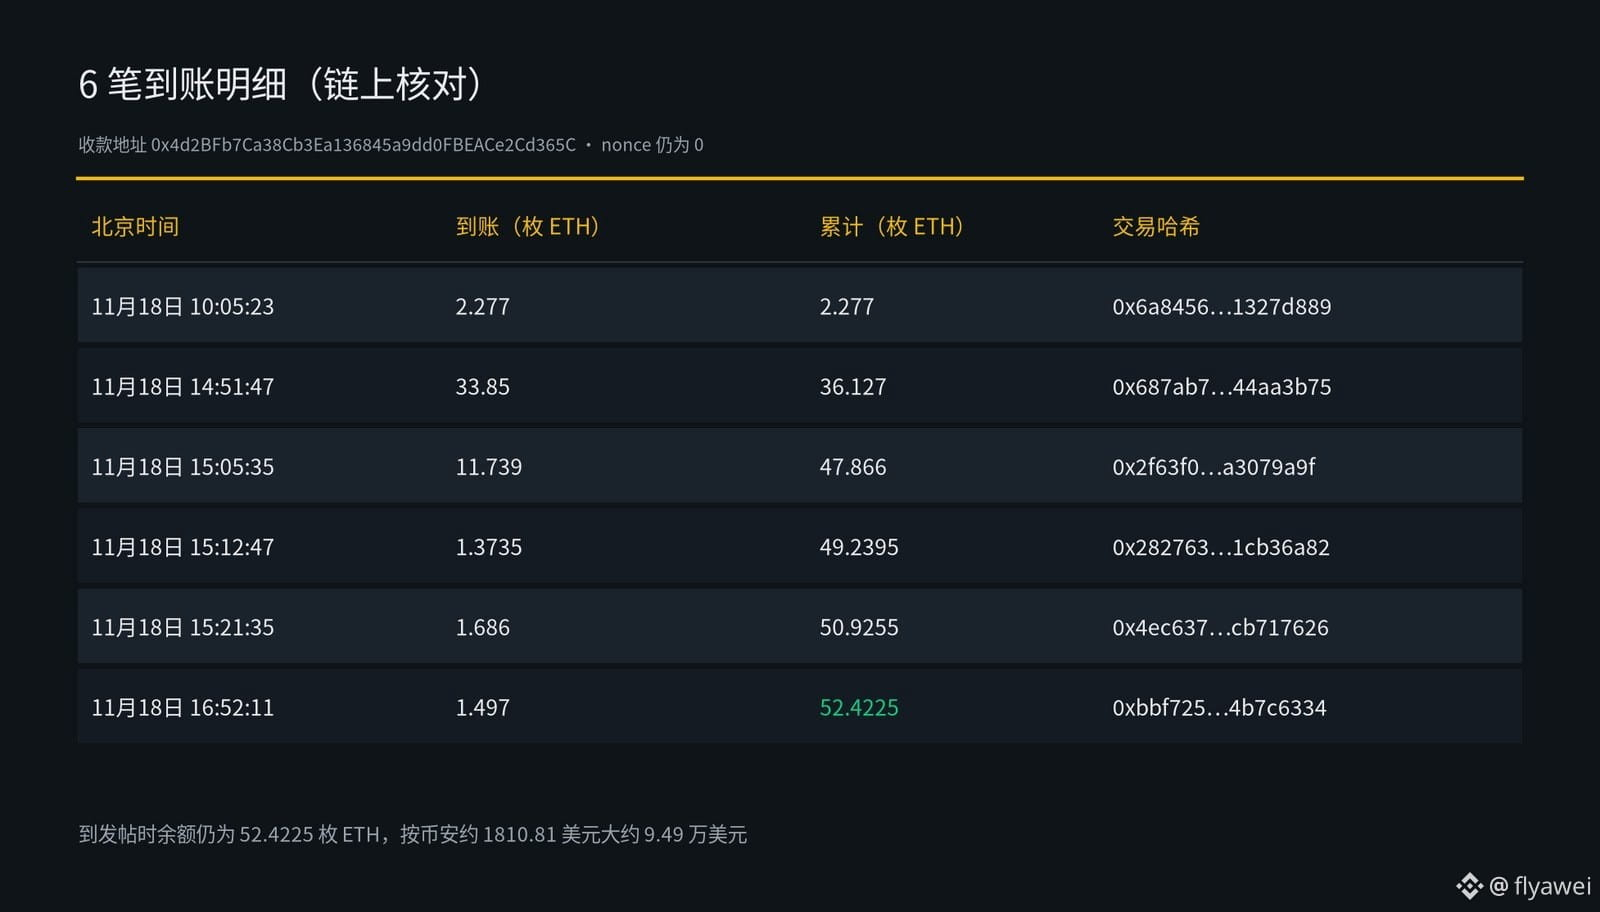
I checked the address named in the official statement (0x4d2B…). From 10:05 to 16:52 Beijing time on November 18, another address (0x8ADD…) sent it a total of 52.4225 ETH in six transactions. At the time of posting, this address had not sent any funds out; its balance was still 52.4225 ETH, worth about $94,900 at Binance’s price of approximately $1,810.81 per ETH.
The official statement also said that the email recovery system had been disabled, and that the public blockchain and the Universal Profile contracts themselves were unaffected. A compensation plan will be announced in the coming weeks, but no details have been given yet about how much will be paid or when.
At 20:40 Beijing time on November 19, the official account issued another reminder: the attack had been stopped, but some profiles still need to completely remove the attacker’s key and the malicious recovery controller.
My take: the funds have already been converted into ether and are sitting at this address. The compensation plan hasn’t been finalized yet, and profiles that had keys added still need to remove them first.
Beginners should watch more and trade less. If you buy crypto, only buy $BTC
LUKSO officially posted a post-incident statement at 20:29 Beijing time on November 18, saying that from the night of November 17 through November 18, a vulnerability in the backend of its email recovery system allowed attackers to add controller keys to around 300 Universal Profile accounts. About 1.4 million LYX was stolen from these accounts in total.
The official statement said that all of the roughly 1.4 million LYX had been bridged to Ethereum, traded for ether on decentralized exchanges, and eventually converted into about 50 ETH, worth approximately $95,000.
I checked the address named in the official statement (0x4d2B…). From 10:05 to 16:52 Beijing time on November 18, another address (0x8ADD…) sent it a total of 52.4225 ETH in six transactions. At the time of posting, this address had not sent any funds out; its balance was still 52.4225 ETH, worth about $94,900 at Binance’s price of approximately $1,810.81 per ETH.
The official statement also said that the email recovery system had been disabled, and that the public blockchain and the Universal Profile contracts themselves were unaffected. A compensation plan will be announced in the coming weeks, but no details have been given yet about how much will be paid or when.
At 20:40 Beijing time on November 19, the official account issued another reminder: the attack had been stopped, but some profiles still need to completely remove the attacker’s key and the malicious recovery controller.
My take: the funds have already been converted into ether and are sitting at this address. The compensation plan hasn’t been finalized yet, and profiles that had keys added still need to remove them first.
Beginners should watch more and trade less. If you buy crypto, only buy $BTC