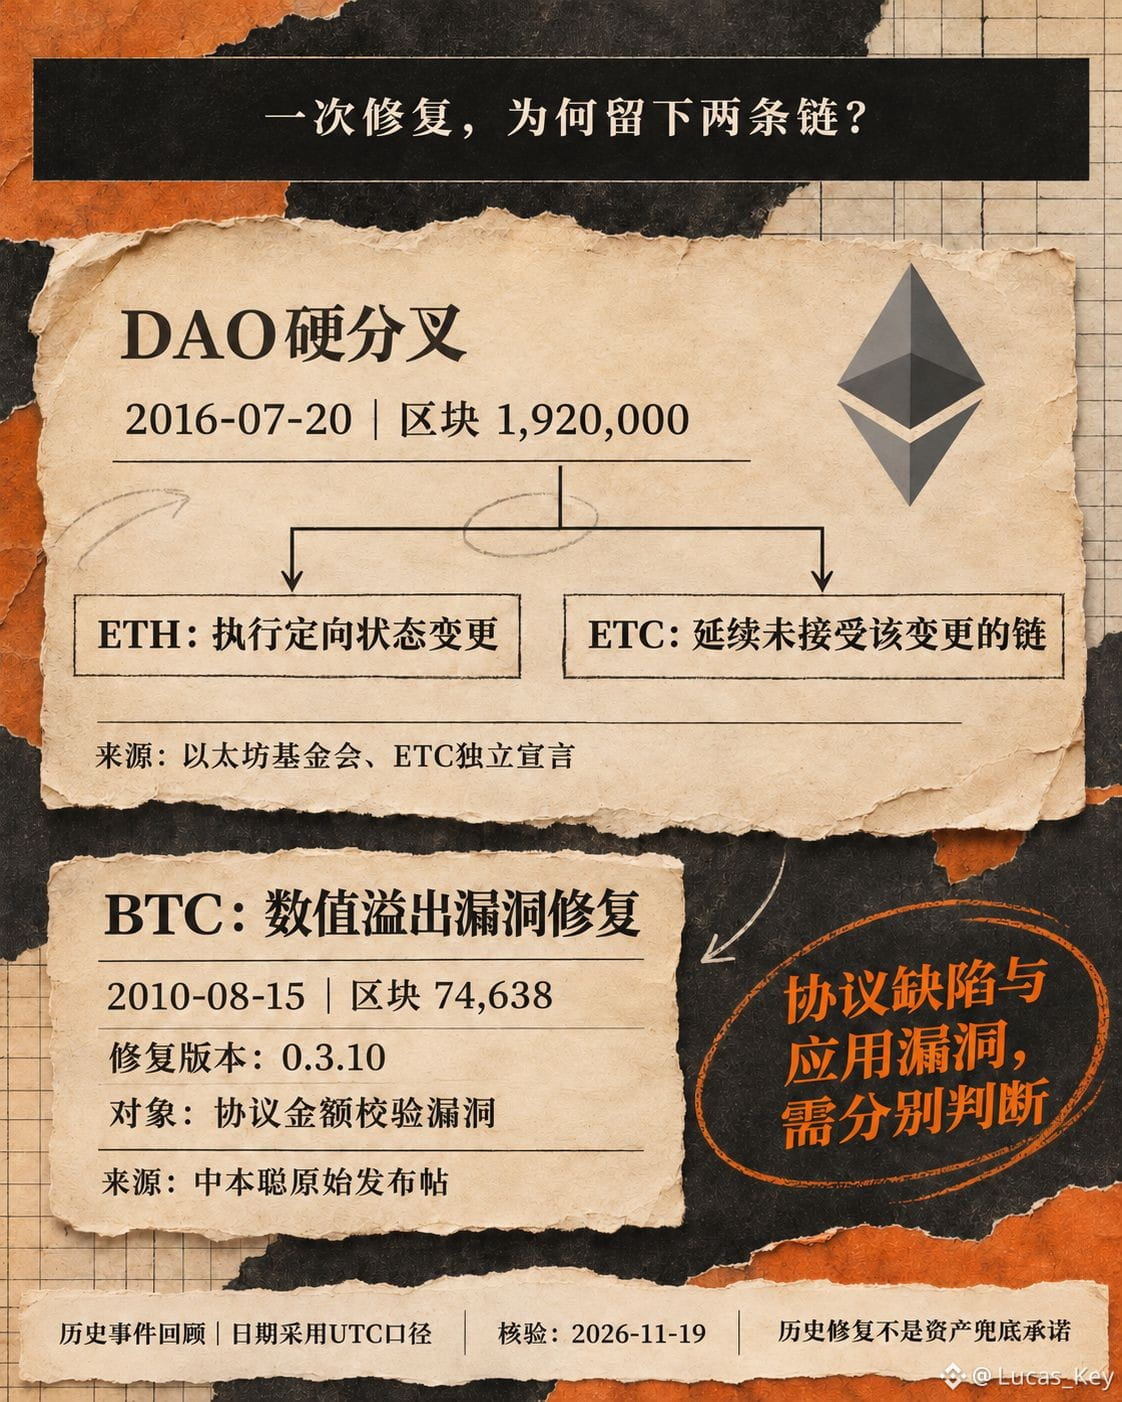
On July 20, 2016, $ETH carried out the DAO hard fork at block 1,920,000, making a targeted state change to the balances of specific contracts and moving the associated funds to a recovery contract. The chain that did not accept this change continued to operate and later became known as $ETC . This history can still help assess security incidents today: when a fix for a vulnerability is promised, which layer is actually being changed?
Those who supported intervention hoped to mitigate losses caused by an application vulnerability; those who opposed it worried that changing asset balances in response to a specific incident would undermine confidence in the principle that “the rules don’t change for anyone.” The Ethereum Foundation’s announcement of the fork’s completion and the ETC Declaration of Independence document this genuine disagreement. Neither side should be reduced to simply wanting a bailout, nor should the other be portrayed as endorsing the attack.
Consider $BTC : on August 15, 2010, an integer overflow issue arose at block 74,638, and Satoshi Nakamoto released patch 0.3.10 to fix it. This addressed a flaw in amount validation in the protocol implementation; the DAO dispute, by contrast, centered on whether chain-level rules should be used to target and change balances after an application contract was exploited. Both cases required network participants to adopt the corresponding software, but the technical issues and value trade-offs were not the same.
The boundary I care about is whether a proposed fix can clearly explain which expected rule was violated, which states will be affected, who needs to adopt the new version, and whether those who disagree can continue validating another chain. The histories of ETH, ETC, and BTC offer different contexts; they cannot automatically endorse any project today, much less support the conclusion that “someone will always restore your assets after a theft.” Sources: the Ethereum Foundation’s July 2016 announcement, the ETC Declaration of Independence, and Satoshi Nakamoto’s 0.3.10 release post; verified on November 19. Risk warning: historical fixes do not guarantee asset recovery; protocol and contract risks must still be assessed separately.
Those who supported intervention hoped to mitigate losses caused by an application vulnerability; those who opposed it worried that changing asset balances in response to a specific incident would undermine confidence in the principle that “the rules don’t change for anyone.” The Ethereum Foundation’s announcement of the fork’s completion and the ETC Declaration of Independence document this genuine disagreement. Neither side should be reduced to simply wanting a bailout, nor should the other be portrayed as endorsing the attack.
Consider $BTC : on August 15, 2010, an integer overflow issue arose at block 74,638, and Satoshi Nakamoto released patch 0.3.10 to fix it. This addressed a flaw in amount validation in the protocol implementation; the DAO dispute, by contrast, centered on whether chain-level rules should be used to target and change balances after an application contract was exploited. Both cases required network participants to adopt the corresponding software, but the technical issues and value trade-offs were not the same.
The boundary I care about is whether a proposed fix can clearly explain which expected rule was violated, which states will be affected, who needs to adopt the new version, and whether those who disagree can continue validating another chain. The histories of ETH, ETC, and BTC offer different contexts; they cannot automatically endorse any project today, much less support the conclusion that “someone will always restore your assets after a theft.” Sources: the Ethereum Foundation’s July 2016 announcement, the ETC Declaration of Independence, and Satoshi Nakamoto’s 0.3.10 release post; verified on November 19. Risk warning: historical fixes do not guarantee asset recovery; protocol and contract risks must still be assessed separately.