279 profiles had a key added, but it doesn’t show up in the list
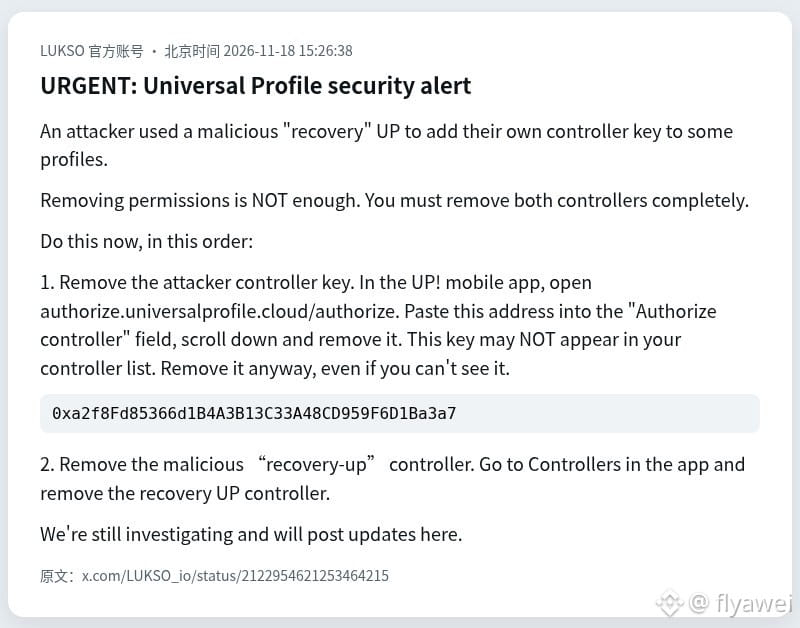
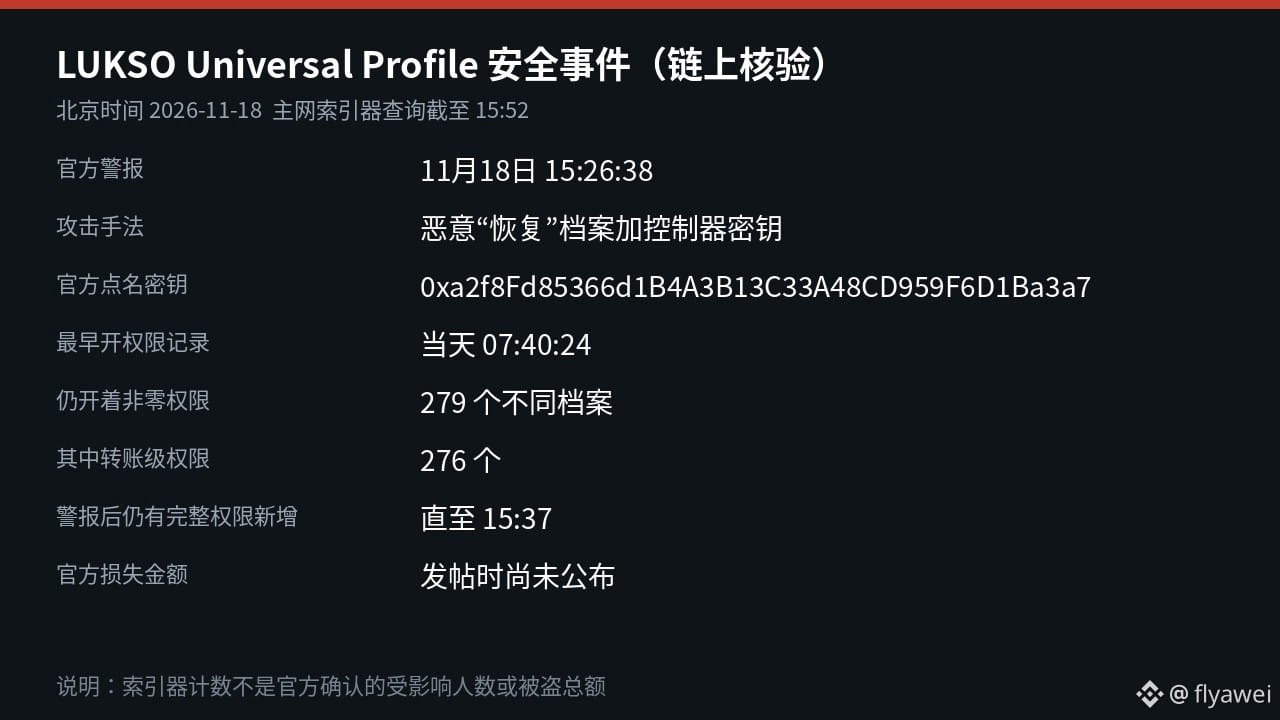
At 15:26 Beijing time on November 18, the public blockchain LUKSO issued an urgent security alert saying that someone had used a malicious “recovery” profile to add their own controller key to some Universal Profile accounts. I then checked the mainnet indexer. By 15:52, 279 different profiles still had nonzero permissions enabled for this key.
The address the official alert specifically said to remove is 0xa2f8…a3a7. It also warned that this key might not even be visible in the controller list. Simply disabling its permissions isn’t enough: the attacker’s key and the malicious recovery-up controller must be removed entirely.
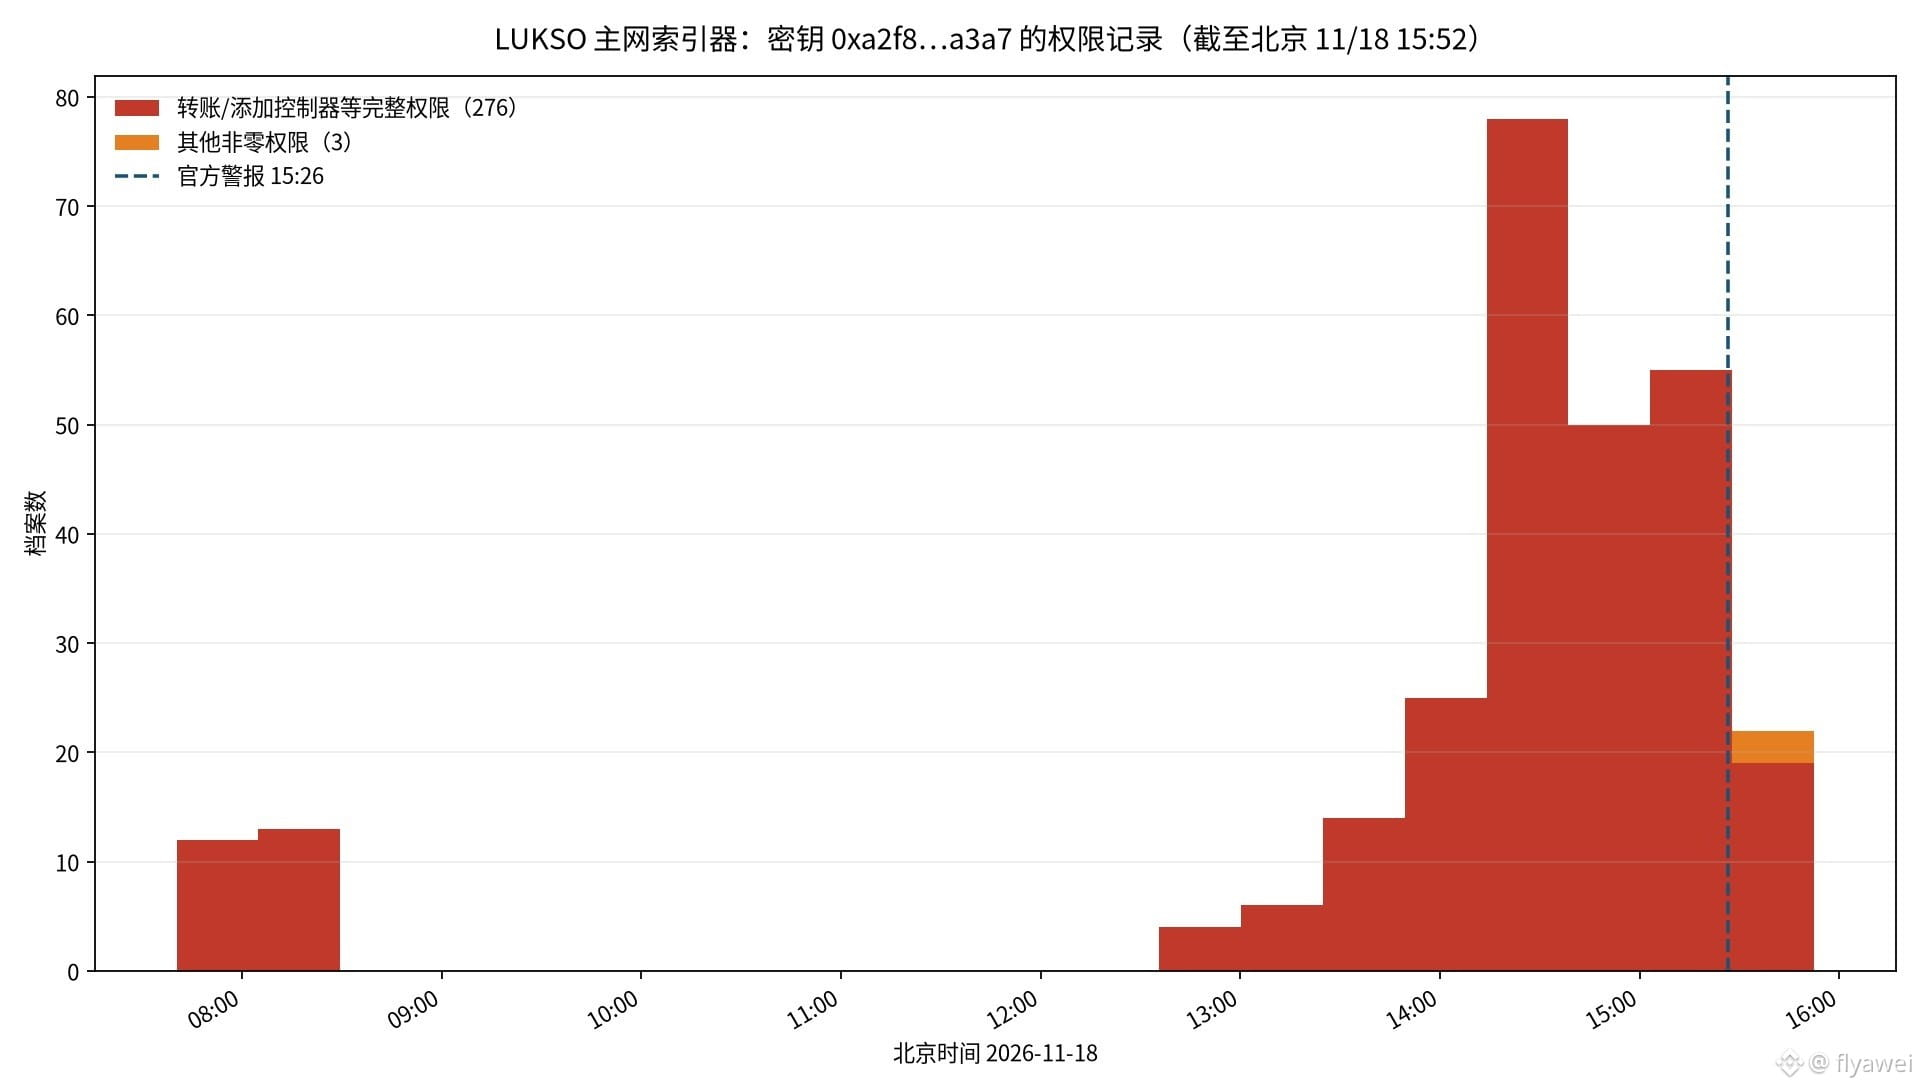
According to the indexer, the earliest record of permissions being enabled appeared at 7:40 that day. Of the 279 profiles, 276 had enabled permissions such as transferring funds and adding controllers. Even after the official alert was issued, new records granting transfer permissions continued to appear, as late as 15:37.
A Universal Profile is an on-chain smart contract account. With the appropriate permissions, a controller can edit profile information and transfer LYX, tokens, and NFTs. Officials said they were still investigating and had not disclosed the amount stolen or the number of people affected at the time of posting. Some people have already commented under the official post that their profiles were drained, but this has not yet been confirmed by officials.
First, follow the official instructions and remove this key, then delete the malicious recovery controller. Don’t click recovery links from unknown sources.
Beginners are advised to observe more and do less. If you’re buying crypto, stick to $BTC .
At 15:26 Beijing time on November 18, the public blockchain LUKSO issued an urgent security alert saying that someone had used a malicious “recovery” profile to add their own controller key to some Universal Profile accounts. I then checked the mainnet indexer. By 15:52, 279 different profiles still had nonzero permissions enabled for this key.
The address the official alert specifically said to remove is 0xa2f8…a3a7. It also warned that this key might not even be visible in the controller list. Simply disabling its permissions isn’t enough: the attacker’s key and the malicious recovery-up controller must be removed entirely.
According to the indexer, the earliest record of permissions being enabled appeared at 7:40 that day. Of the 279 profiles, 276 had enabled permissions such as transferring funds and adding controllers. Even after the official alert was issued, new records granting transfer permissions continued to appear, as late as 15:37.
A Universal Profile is an on-chain smart contract account. With the appropriate permissions, a controller can edit profile information and transfer LYX, tokens, and NFTs. Officials said they were still investigating and had not disclosed the amount stolen or the number of people affected at the time of posting. Some people have already commented under the official post that their profiles were drained, but this has not yet been confirmed by officials.
First, follow the official instructions and remove this key, then delete the malicious recovery controller. Don’t click recovery links from unknown sources.
Beginners are advised to observe more and do less. If you’re buying crypto, stick to $BTC .