The original photos in your album may be getting scanned for seed phrases.
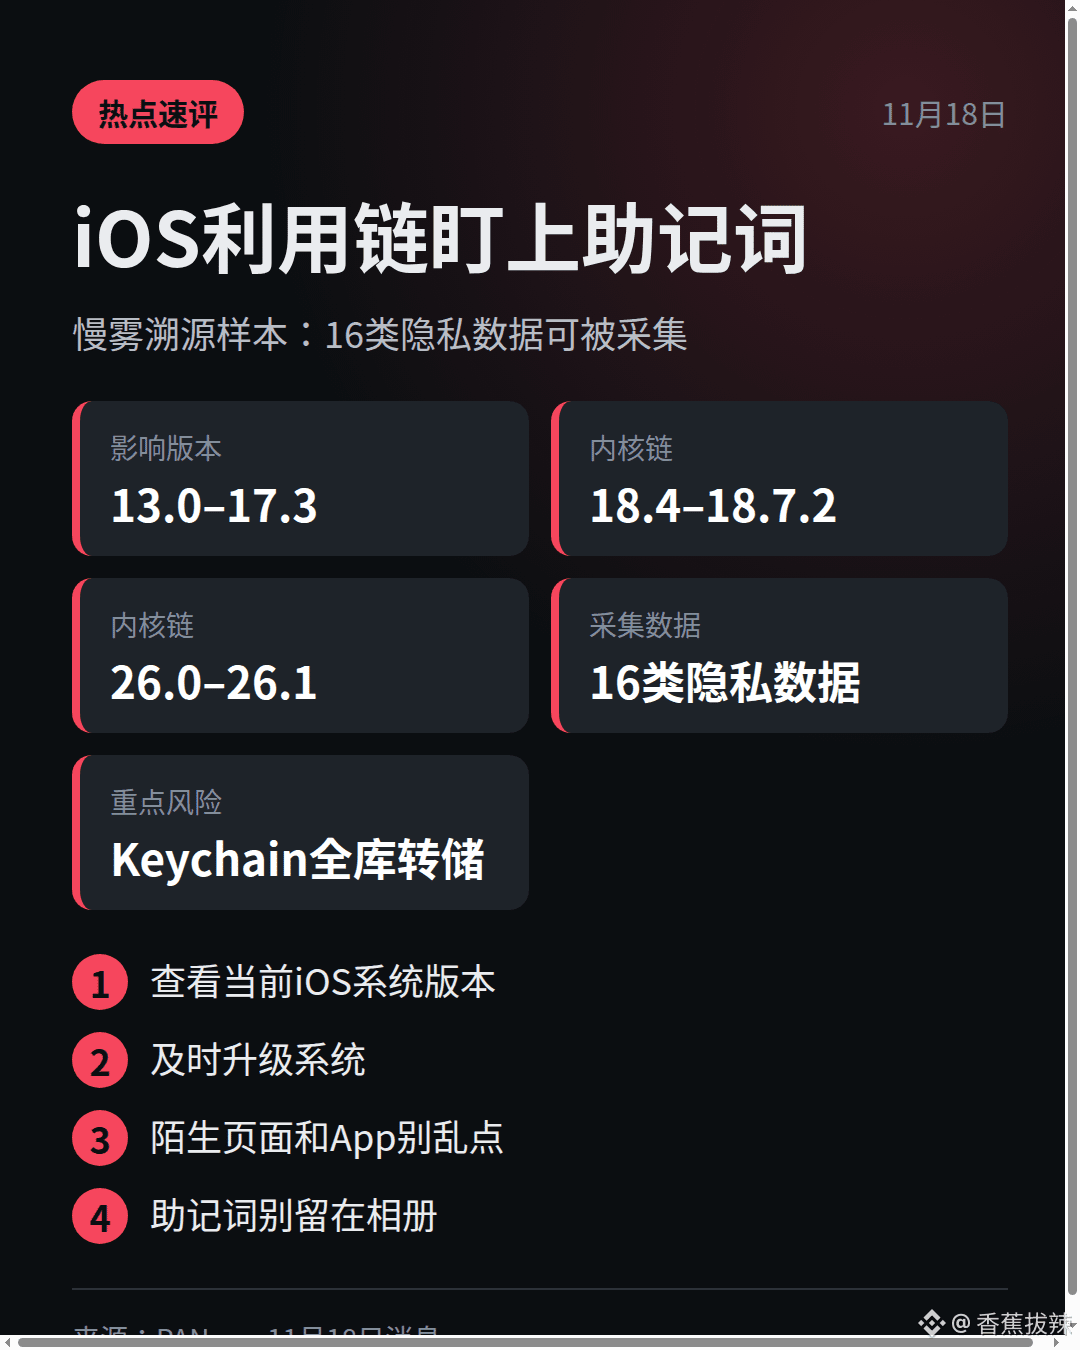
Cosine of SlowMist said that after tracing the samples, the team found multiple attack chains on the attackers’ backend: iOS 13.0–17.3 uses a Hook chain, while iOS 18.4–18.7.2 and iOS 26.0–26.1 use a kernel chain.
These chains can collect 16 types of private data. For crypto users, the most immediate risks are OCR scanning of original photos for seed phrases, password vaults being cracked, and local encrypted files containing wallet private keys and seed phrases being stolen. They can even automatically launder funds across multiple chains.
The 18.4–18.7.2 chain can also dump the entire Keychain and inject into SpringBoard. Once triggered, data from your Keychain, Notes, and Photos could all be collected.
The attack is triggered through Safari or an app, so don’t tap unfamiliar pages. 1️⃣ Check your system version first to see whether it falls within the affected range; 2️⃣ Update your system promptly—that’s SlowMist’s recommendation; 3️⃣ Don’t leave screenshots of your seed phrase in your photo album.
Guys, what system version are you running now? Is it in the 18.4–18.7.2 range? #iOS
Cosine of SlowMist said that after tracing the samples, the team found multiple attack chains on the attackers’ backend: iOS 13.0–17.3 uses a Hook chain, while iOS 18.4–18.7.2 and iOS 26.0–26.1 use a kernel chain.
These chains can collect 16 types of private data. For crypto users, the most immediate risks are OCR scanning of original photos for seed phrases, password vaults being cracked, and local encrypted files containing wallet private keys and seed phrases being stolen. They can even automatically launder funds across multiple chains.
The 18.4–18.7.2 chain can also dump the entire Keychain and inject into SpringBoard. Once triggered, data from your Keychain, Notes, and Photos could all be collected.
The attack is triggered through Safari or an app, so don’t tap unfamiliar pages. 1️⃣ Check your system version first to see whether it falls within the affected range; 2️⃣ Update your system promptly—that’s SlowMist’s recommendation; 3️⃣ Don’t leave screenshots of your seed phrase in your photo album.
Guys, what system version are you running now? Is it in the 18.4–18.7.2 range? #iOS