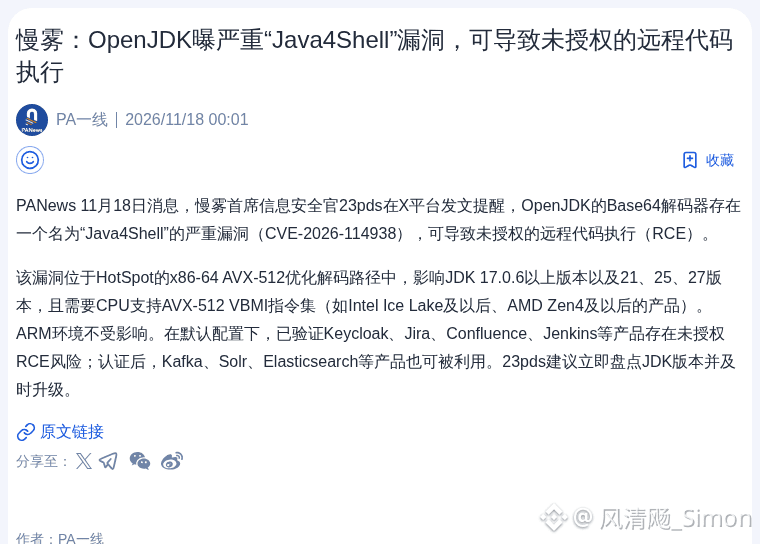
SlowMist just posted that OpenJDK has a serious vulnerability called “Java4Shell.” It can lead to unauthorized remote code execution, which sounds pretty scary.
The vulnerability is in HotSpot’s optimized decoding path and affects versions JDK 17.0.6 and later. ARM environments are unaffected, but x86-64 systems—mainly those using Intel Ice Lake or AMD Zen 4 and later—are at risk.
If you work in development or operations, check your environment right away. Don’t wait until you’ve been hacked to find out.
$BTC
$ETH
#SecurityIncident
The vulnerability is in HotSpot’s optimized decoding path and affects versions JDK 17.0.6 and later. ARM environments are unaffected, but x86-64 systems—mainly those using Intel Ice Lake or AMD Zen 4 and later—are at risk.
If you work in development or operations, check your environment right away. Don’t wait until you’ve been hacked to find out.
$BTC
$ETH
#SecurityIncident