The signature credential wasn’t verified, turning the pool into an ATM.
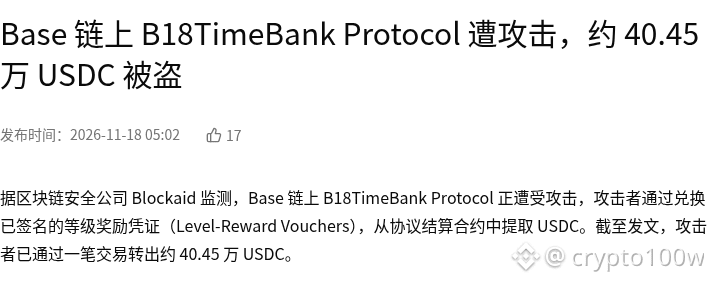
Blockchain security firm Blockaid reported that B18TimeBank Protocol on Base is under attack. The attacker redeemed signed Level-Reward Vouchers to withdraw USDC from the protocol’s settlement contract. As of publication, approximately 404,500 USDC had been transferred out in a single transaction. Source: Wu Says.
This is a typical way to bypass contract validation logic: if signed credentials lack replay protection or amount checks, the same reward may be redeemed repeatedly. There is no direct impact on major assets such as BTC or ETH; the impact is mainly on the B18TimeBank token and sentiment toward DeFi in the Base ecosystem.
Scenario to watch 1: If the protocol urgently pauses the contract and announces a compensation or buyback plan, holders will have a clear short-term reference point. Scenario to watch 2: If the stolen funds are traced or enter a mixing service, the audit coverage and permission settings of new protocols on Base will come under renewed scrutiny.
Which matters more to you: whether the protocol pauses the contract, or whether the stolen funds are tracked?
Image 1: B18TimeBank on Base attacked, 404,500 USDC stolen · Screenshot of source page
Image source: https://www.wublock123.com/news/base-b18timebank-protocol-exploit-405k-usdc-72156
Blockchain security firm Blockaid reported that B18TimeBank Protocol on Base is under attack. The attacker redeemed signed Level-Reward Vouchers to withdraw USDC from the protocol’s settlement contract. As of publication, approximately 404,500 USDC had been transferred out in a single transaction. Source: Wu Says.
This is a typical way to bypass contract validation logic: if signed credentials lack replay protection or amount checks, the same reward may be redeemed repeatedly. There is no direct impact on major assets such as BTC or ETH; the impact is mainly on the B18TimeBank token and sentiment toward DeFi in the Base ecosystem.
Scenario to watch 1: If the protocol urgently pauses the contract and announces a compensation or buyback plan, holders will have a clear short-term reference point. Scenario to watch 2: If the stolen funds are traced or enter a mixing service, the audit coverage and permission settings of new protocols on Base will come under renewed scrutiny.
Which matters more to you: whether the protocol pauses the contract, or whether the stolen funds are tracked?
Image 1: B18TimeBank on Base attacked, 404,500 USDC stolen · Screenshot of source page
Image source: https://www.wublock123.com/news/base-b18timebank-protocol-exploit-405k-usdc-72156