🚨 FLASH SECURITY TELEMETRY: OPTIMJACK Supply-Chain Attack Infiltrated 178 Enterprise Sites — Ledger Hardware Keys Completely Unaffected
A sophisticated software supply-chain breach targeting web experimentation platform Optimizely was actively detected and neutralized on November 16, 2026.
Key Telemetry & Incident Forensics:
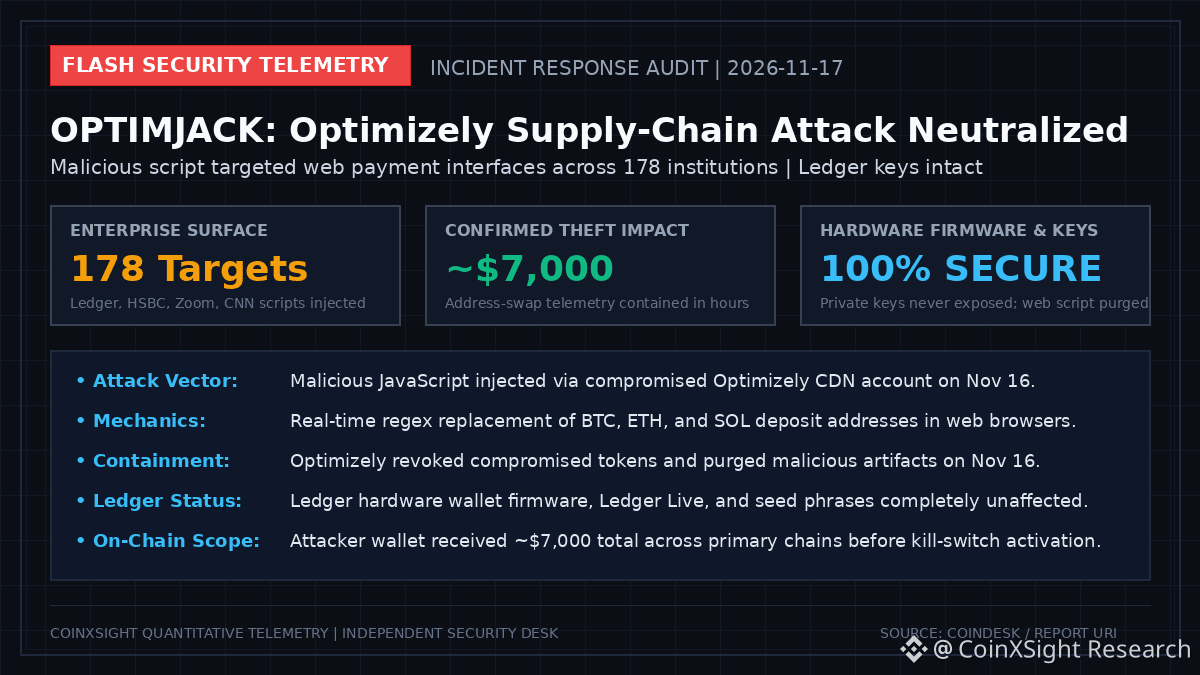
• Attack Vector: Malicious JavaScript injected via compromised Optimizely CDN account, targeting web interfaces across 178 global institutions including Ledger, HSBC, Zoom, and CNN.
• Mechanics: Automated regex replacement attempting to swap browser-rendered cryptocurrency deposit addresses (Bitcoin, Ethereum, Solana).
• Containment & Kill-Switch: Optimizely revoked compromised access tokens and purged all malicious web scripts within hours of discovery on Nov 16.
• On-Chain Impact: Attacker wallet intercepted approximately ~,000 total across chains before containment.
• Hardware Security Status: Ledger confirmed zero compromise to hardware devices, firmware, Ledger Live application, or private seed phrases.
Institutional takeaway: Client-side web script hijacking remains an enterprise vulnerability, reinforcing the necessity of offline hardware validation for high-value crypto transfers.
#BTC #BinanceSquare
(Disclaimer: Quantitative market and security telemetry published strictly for informational purposes. Not financial advice.)
A sophisticated software supply-chain breach targeting web experimentation platform Optimizely was actively detected and neutralized on November 16, 2026.
Key Telemetry & Incident Forensics:
• Attack Vector: Malicious JavaScript injected via compromised Optimizely CDN account, targeting web interfaces across 178 global institutions including Ledger, HSBC, Zoom, and CNN.
• Mechanics: Automated regex replacement attempting to swap browser-rendered cryptocurrency deposit addresses (Bitcoin, Ethereum, Solana).
• Containment & Kill-Switch: Optimizely revoked compromised access tokens and purged all malicious web scripts within hours of discovery on Nov 16.
• On-Chain Impact: Attacker wallet intercepted approximately ~,000 total across chains before containment.
• Hardware Security Status: Ledger confirmed zero compromise to hardware devices, firmware, Ledger Live application, or private seed phrases.
Institutional takeaway: Client-side web script hijacking remains an enterprise vulnerability, reinforcing the necessity of offline hardware validation for high-value crypto transfers.
#BTC #BinanceSquare
(Disclaimer: Quantitative market and security telemetry published strictly for informational purposes. Not financial advice.)