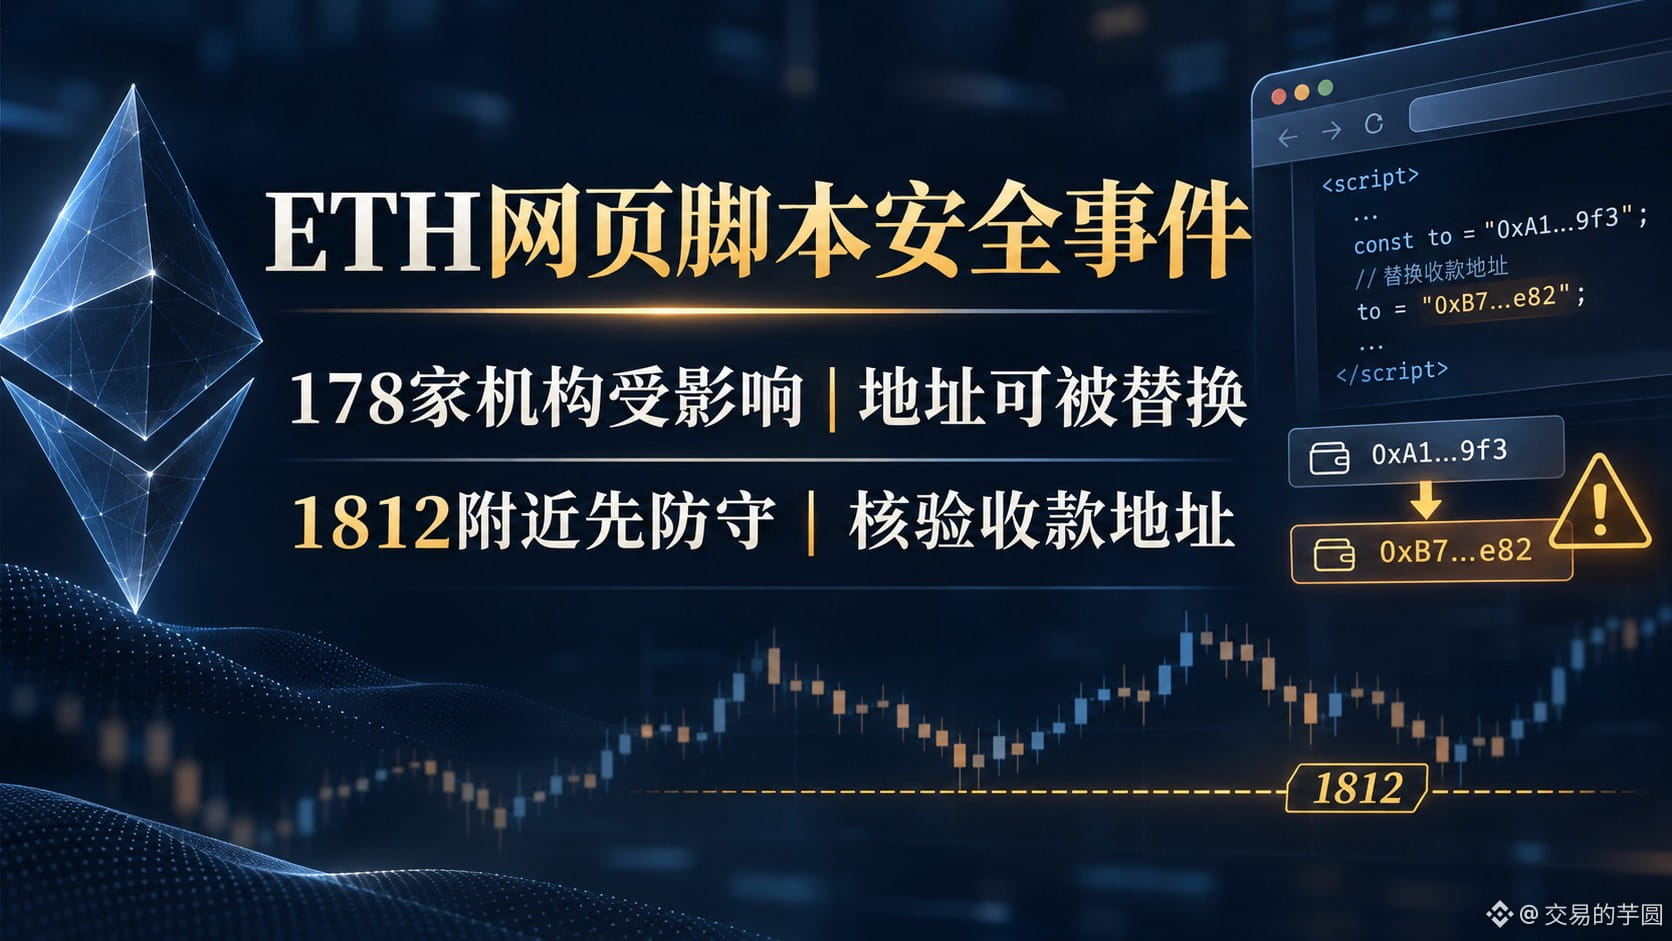
ETH security incident escalates|Third-party scripts can replace payment addresses|Defend first around 1812
My view: This news is primarily about risks in the transfer process, not evidence that the Ethereum blockchain itself has been breached. For now, I won't short ETH just because of security news, but I also won't treat an intraday rebound as proof that the risk has passed. Binance Square is discussing #OPTIMJACKAttackInfectsAtLeast186Websites, a topic title that uses an earlier tally. StepSecurity, a security research firm, updated its findings: on November 16, malicious code appeared in 188 Optimizely web experiment scripts used by 178 organizations. The two figures refer to organizations and scripts respectively; they should not be conflated as “188 websites.”
More importantly, Optimizely’s status page confirms that someone exploited a Web Experimentation vulnerability to add malicious JavaScript to some customer projects. The company says the vulnerability has been fixed, the injected code removed, and the affected accounts secured; the status is currently being monitored. StepSecurity’s independent analysis found that the code could replace valid payment addresses for ETH and other chains with attackers’ addresses while webpages were displayed, copied, or some forms submitted. It could also steal payment card information. StepSecurity listed Ledger and other affected organizations, but “visited these websites” does not mean every user lost funds; actual losses and the number of victims cannot be estimated from webpage exposure figures alone.
The incident affects the crypto market through trust and operational costs: even when copying an address from a seemingly legitimate website, users should verify it character by character on their wallet or hardware device’s confirmation screen. The entry point was the web supply chain, which does not justify inferring that the ETH protocol, mainnet, or all wallets have been compromised. If the relevant service providers disclose more victimized transactions in the short term, industry risk appetite may come under pressure; conversely, confirmation of the fix and no further evidence of victims would lessen the impact. Price-wise, ETH/USDT was around $1,812 at the time of observation, still up about 0.7% over the rolling 24 hours, with a range of 1,787 to 1,867. It has pulled back about $55 from the range high, but this entire move cannot be attributed to this incident. 1,787 is this swing’s low, and 1,800 is a psychological level; to the upside, watch 1,835 first, then 1,867.
If I were trading this myself: I’d stay out for now. The only direction I’d consider is a small spot long; I would absolutely not open a high-leverage short because of a security headline. I’d enter only if ETH regains 1,835 and then holds on a retest, with no further spread of the security incident. I’d use at most 3% of my total capital to open a position; the first target is 1,867, where I’d take half off, then watch whether the remaining position can hold above 1,870. I’d place a stop-loss below 1,815 after entry. If ETH breaks below 1,787 outright or an official update expands the reported scope of affected users, I’d cancel any unfilled order and immediately close any open position. If it merely rebounds to 1,835 and gets pushed back down, I’d remain on the sidelines. First verify the address, then think about position size.
#OPTIMJACKAttackInfectsAtLeast186Websites #ETH
The above is only my personal market observation and does not constitute investment advice.
My view: This news is primarily about risks in the transfer process, not evidence that the Ethereum blockchain itself has been breached. For now, I won't short ETH just because of security news, but I also won't treat an intraday rebound as proof that the risk has passed. Binance Square is discussing #OPTIMJACKAttackInfectsAtLeast186Websites, a topic title that uses an earlier tally. StepSecurity, a security research firm, updated its findings: on November 16, malicious code appeared in 188 Optimizely web experiment scripts used by 178 organizations. The two figures refer to organizations and scripts respectively; they should not be conflated as “188 websites.”
More importantly, Optimizely’s status page confirms that someone exploited a Web Experimentation vulnerability to add malicious JavaScript to some customer projects. The company says the vulnerability has been fixed, the injected code removed, and the affected accounts secured; the status is currently being monitored. StepSecurity’s independent analysis found that the code could replace valid payment addresses for ETH and other chains with attackers’ addresses while webpages were displayed, copied, or some forms submitted. It could also steal payment card information. StepSecurity listed Ledger and other affected organizations, but “visited these websites” does not mean every user lost funds; actual losses and the number of victims cannot be estimated from webpage exposure figures alone.
The incident affects the crypto market through trust and operational costs: even when copying an address from a seemingly legitimate website, users should verify it character by character on their wallet or hardware device’s confirmation screen. The entry point was the web supply chain, which does not justify inferring that the ETH protocol, mainnet, or all wallets have been compromised. If the relevant service providers disclose more victimized transactions in the short term, industry risk appetite may come under pressure; conversely, confirmation of the fix and no further evidence of victims would lessen the impact. Price-wise, ETH/USDT was around $1,812 at the time of observation, still up about 0.7% over the rolling 24 hours, with a range of 1,787 to 1,867. It has pulled back about $55 from the range high, but this entire move cannot be attributed to this incident. 1,787 is this swing’s low, and 1,800 is a psychological level; to the upside, watch 1,835 first, then 1,867.
If I were trading this myself: I’d stay out for now. The only direction I’d consider is a small spot long; I would absolutely not open a high-leverage short because of a security headline. I’d enter only if ETH regains 1,835 and then holds on a retest, with no further spread of the security incident. I’d use at most 3% of my total capital to open a position; the first target is 1,867, where I’d take half off, then watch whether the remaining position can hold above 1,870. I’d place a stop-loss below 1,815 after entry. If ETH breaks below 1,787 outright or an official update expands the reported scope of affected users, I’d cancel any unfilled order and immediately close any open position. If it merely rebounds to 1,835 and gets pushed back down, I’d remain on the sidelines. First verify the address, then think about position size.
#OPTIMJACKAttackInfectsAtLeast186Websites #ETH
The above is only my personal market observation and does not constitute investment advice.