The shipping labels for hardware wallets leaked before the wallets themselves: information on around 27,000 Trezor orders was compromised
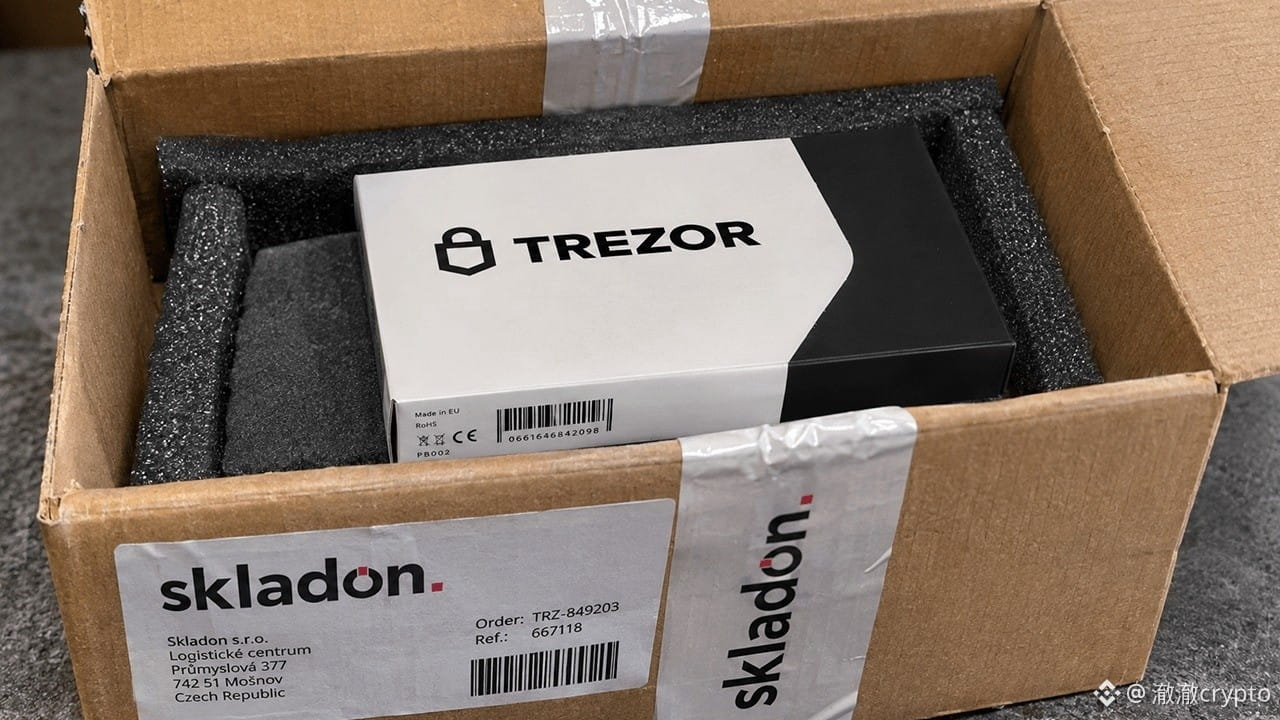
Trezor announced on November 16 that its logistics provider, Skladon, was breached on November 7 and only notified Trezor on November 15.
Information on around 27,000 orders placed between August 9 and November 7 was exported, including names, phone numbers, home addresses, email addresses, models, and prices. U.S. users were not affected.
Some users have already received scam calls from people posing as customer support. The scammers can start by quoting your real order details.
The devices, recovery phrases, and PINs are all safe, so your funds can’t be stolen. But with your address exposed, spotting scam calls just got a whole lot harder.
This is also Trezor’s third third-party data leak this year: around 14,000 orders at ShipMonk in August, and 347,000 contacts at email provider Brevo in September.
If you placed an order between August 9 and November 7, treat any call, text, or email about your order as a scam. Contact customer support only through the official website.
There’s only one reason to think otherwise: Trezor would have to walk back its statement and say the data wasn’t leaked. Otherwise, assume it was.
Do you think hardware wallet companies should be held responsible for leaks at their logistics providers, or is the blame entirely on the contractors?
$BTC $ETH $SOL
#硬件钱包 #Trezor
Trezor announced on November 16 that its logistics provider, Skladon, was breached on November 7 and only notified Trezor on November 15.
Information on around 27,000 orders placed between August 9 and November 7 was exported, including names, phone numbers, home addresses, email addresses, models, and prices. U.S. users were not affected.
Some users have already received scam calls from people posing as customer support. The scammers can start by quoting your real order details.
The devices, recovery phrases, and PINs are all safe, so your funds can’t be stolen. But with your address exposed, spotting scam calls just got a whole lot harder.
This is also Trezor’s third third-party data leak this year: around 14,000 orders at ShipMonk in August, and 347,000 contacts at email provider Brevo in September.
If you placed an order between August 9 and November 7, treat any call, text, or email about your order as a scam. Contact customer support only through the official website.
There’s only one reason to think otherwise: Trezor would have to walk back its statement and say the data wasn’t leaked. Otherwise, assume it was.
Do you think hardware wallet companies should be held responsible for leaks at their logistics providers, or is the blame entirely on the contractors?
$BTC $ETH $SOL
#硬件钱包 #Trezor